Hashtag

#privacy

1,544 posts tagged with this hashtag.

@thenewoil@mastodon.thenewoil.org
@r_alb@mastodon.social

I wonder whether the @EUCommission and the European Parliament have heard about the AdFection attack vector by now.

For years, they have done too little to rein in the online marketing industry. Now the monster they let grow and prosper exposes them to espionage.

Politicians, this should be your wake-up call. Ditch the Digital Omnibus. Give us strong privacy laws and enforce them properly. Protect us - and yourselves!

Further reading:
citizenlab.ca/research/exposin
--

citizenlab.ca

Exposing AdFection Executive Summary - The Citizen Lab

This is an executive summary for our report "Exposing AdFection: How Discover-Tech Turned Targeted Ads Into a Pipeline for Zero-Click Mercenary Spyware."

@privacyguides@neat.computer

🚨 This Week in Privacy #75 will be live in 30 minutes! Ledger has confirmed that hardware implants were found in cold-storage devices sold through reseller networks, silently recording seed phrases and draining user wallets via LTE!

We'll also be talking about the latest & news!

👋 Come watch and join the Q&A! youtube.com/@privacyguides/live

youtube.com

The Ledger Wallet Hack is Not Just a Crypto Problem

Ledger devices distributed through a reseller, were compromised with a hardware implant that drained users' crypto wallets, Google is silently linking your p...

@thenewoil@mastodon.thenewoil.org
@noybeu@mastodon.social

🇪🇺 The is currently changing its core privacy law, the . Members of the European Parliament have made more than 1000 amendments - we have analyzed them all. 🔍 Want to know who is playing into the hands of by undermining protections, and who is actually trying to defend your ?

👉 Visit gdpr-omnibus.eu and look up your MEP by country and political group.

If the European Commission and the EU Member States get their way, the 
“Digital Omnibus” will result in a fundamental change to EU privacy laws.

What about the European Parliament? 

To find out more, noyb has analysed more than 1,000 amendments that Members of Parliament (MEPs) have tabled. This analysis shows that many MEPs are in favour of stripping people of their privacy rights – while others still push back.
ALT text

If the European Commission and the EU Member States get their way, the “Digital Omnibus” will result in a fundamental change to EU privacy laws. What about the European Parliament? To find out more, noyb has analysed more than 1,000 amendments that Members of Parliament (MEPs) have tabled. This analysis shows that many MEPs are in favour of stripping people of their privacy rights – while others still push back.

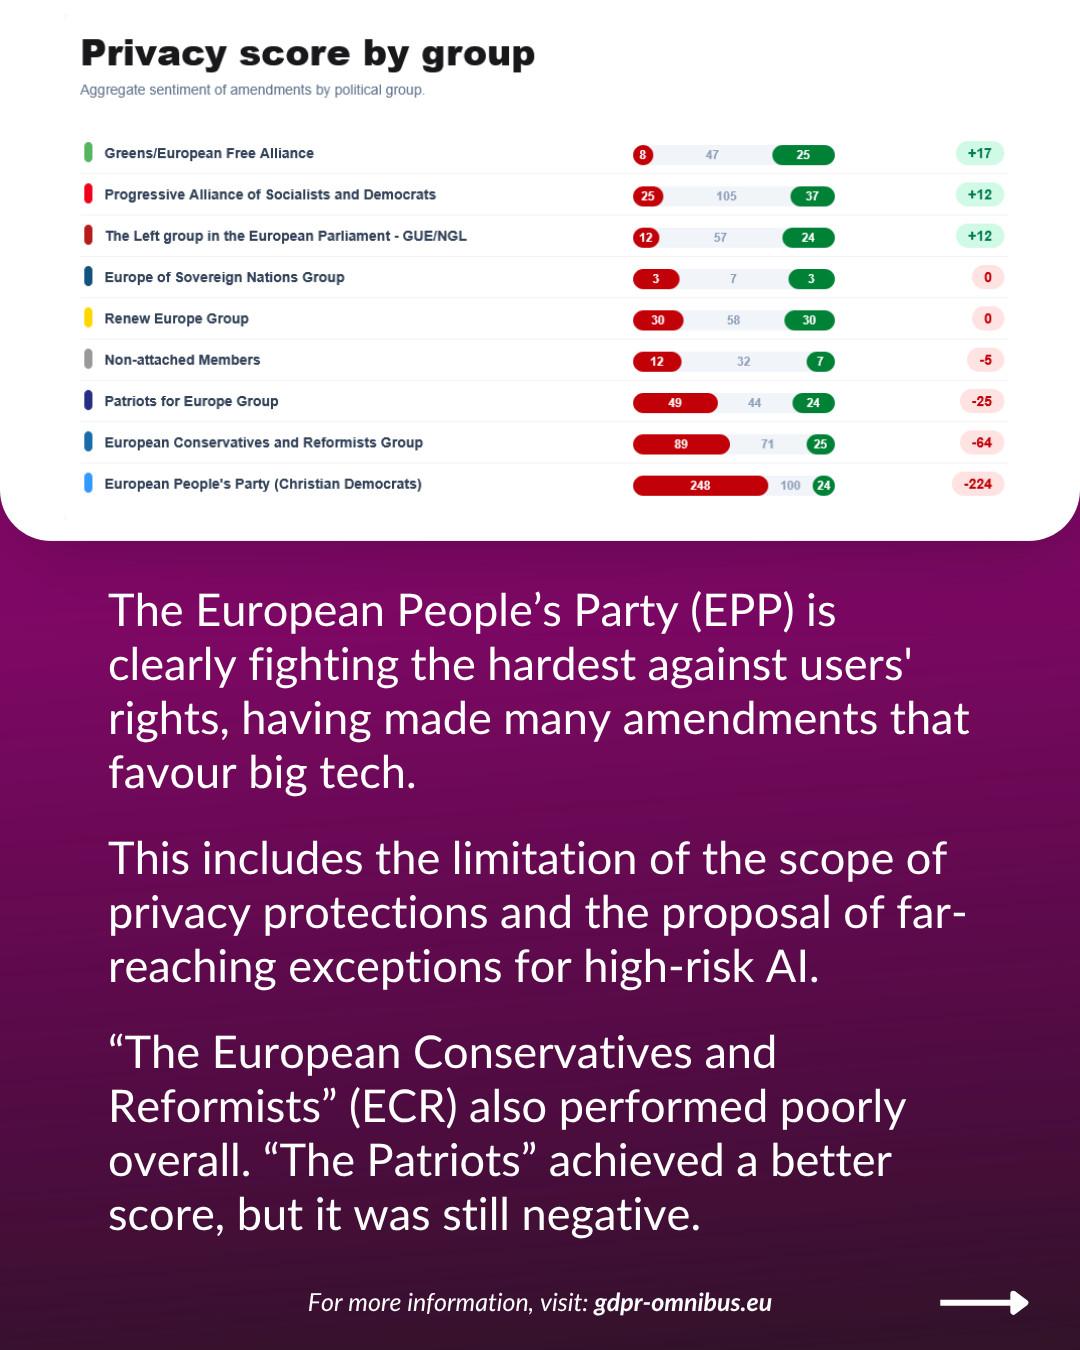
The European People’s Party (EPP) is clearly fighting the hardest against users' rights, having made many amendments that favour big tech.

This includes the limitation of the scope of privacy protections and the proposal of far-reaching exceptions for high-risk AI.

“The European Conservatives and Reformists” (ECR) also performed poorly overall. “The Patriots” achieved a better score, but it was still negative.
ALT text

The European People’s Party (EPP) is clearly fighting the hardest against users' rights, having made many amendments that favour big tech. This includes the limitation of the scope of privacy protections and the proposal of far-reaching exceptions for high-risk AI. “The European Conservatives and Reformists” (ECR) also performed poorly overall. “The Patriots” achieved a better score, but it was still negative.

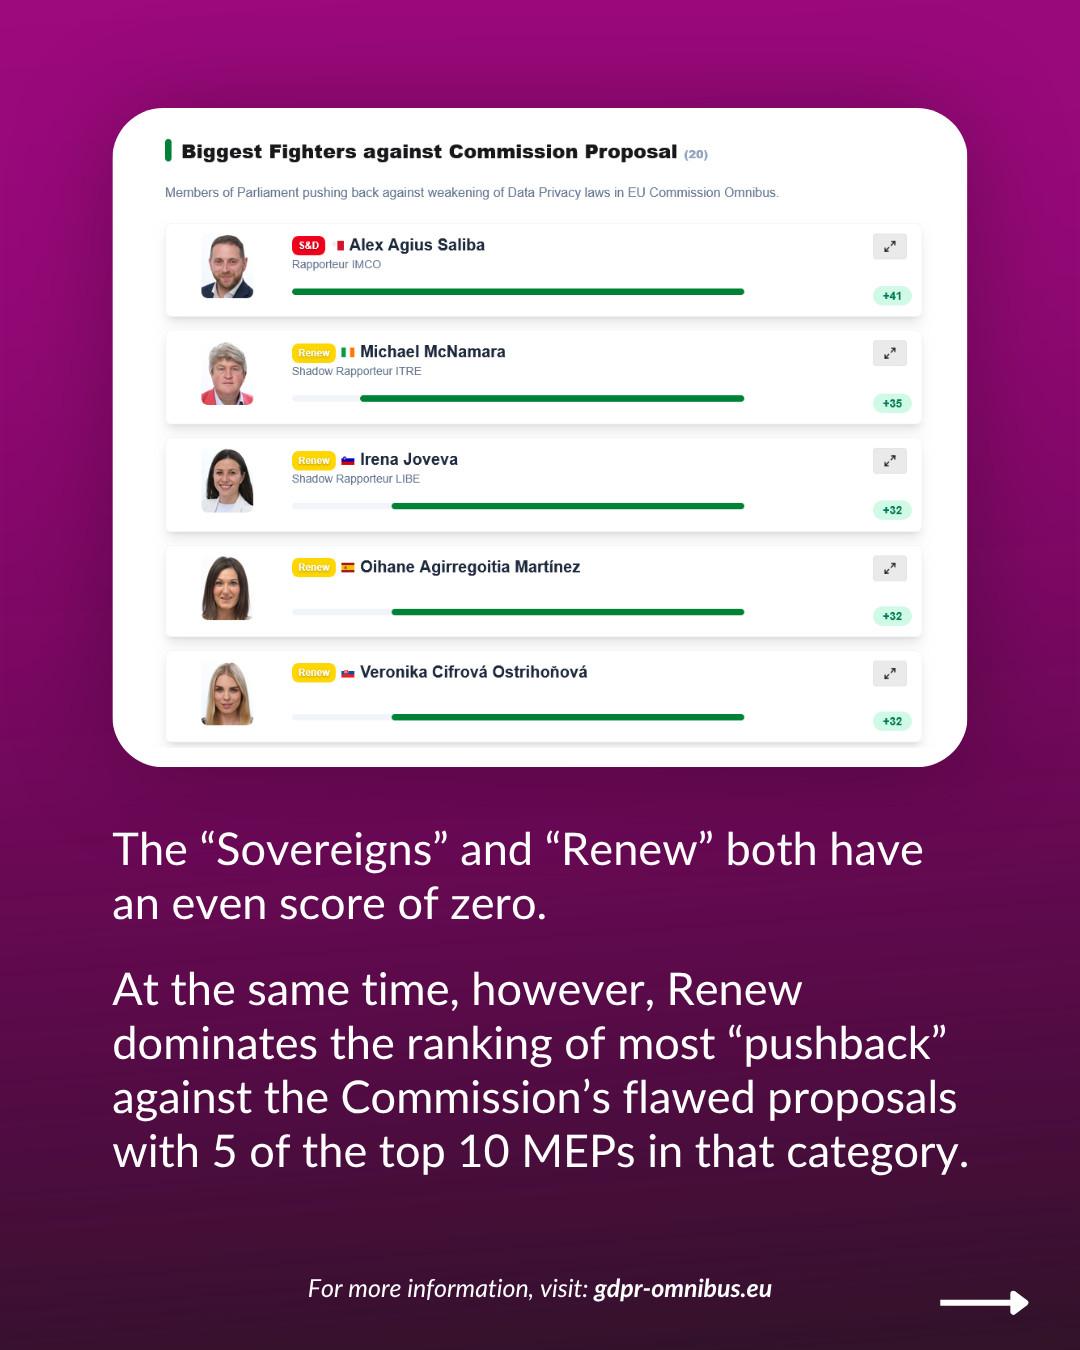
The “Sovereigns” and “Renew” both have an even score of zero.

At the same time, however, Renew dominates the ranking of most “pushback” against the Commission’s flawed proposals with 5 of the top 10 MEPs in that category.
ALT text

The “Sovereigns” and “Renew” both have an even score of zero. At the same time, however, Renew dominates the ranking of most “pushback” against the Commission’s flawed proposals with 5 of the top 10 MEPs in that category.

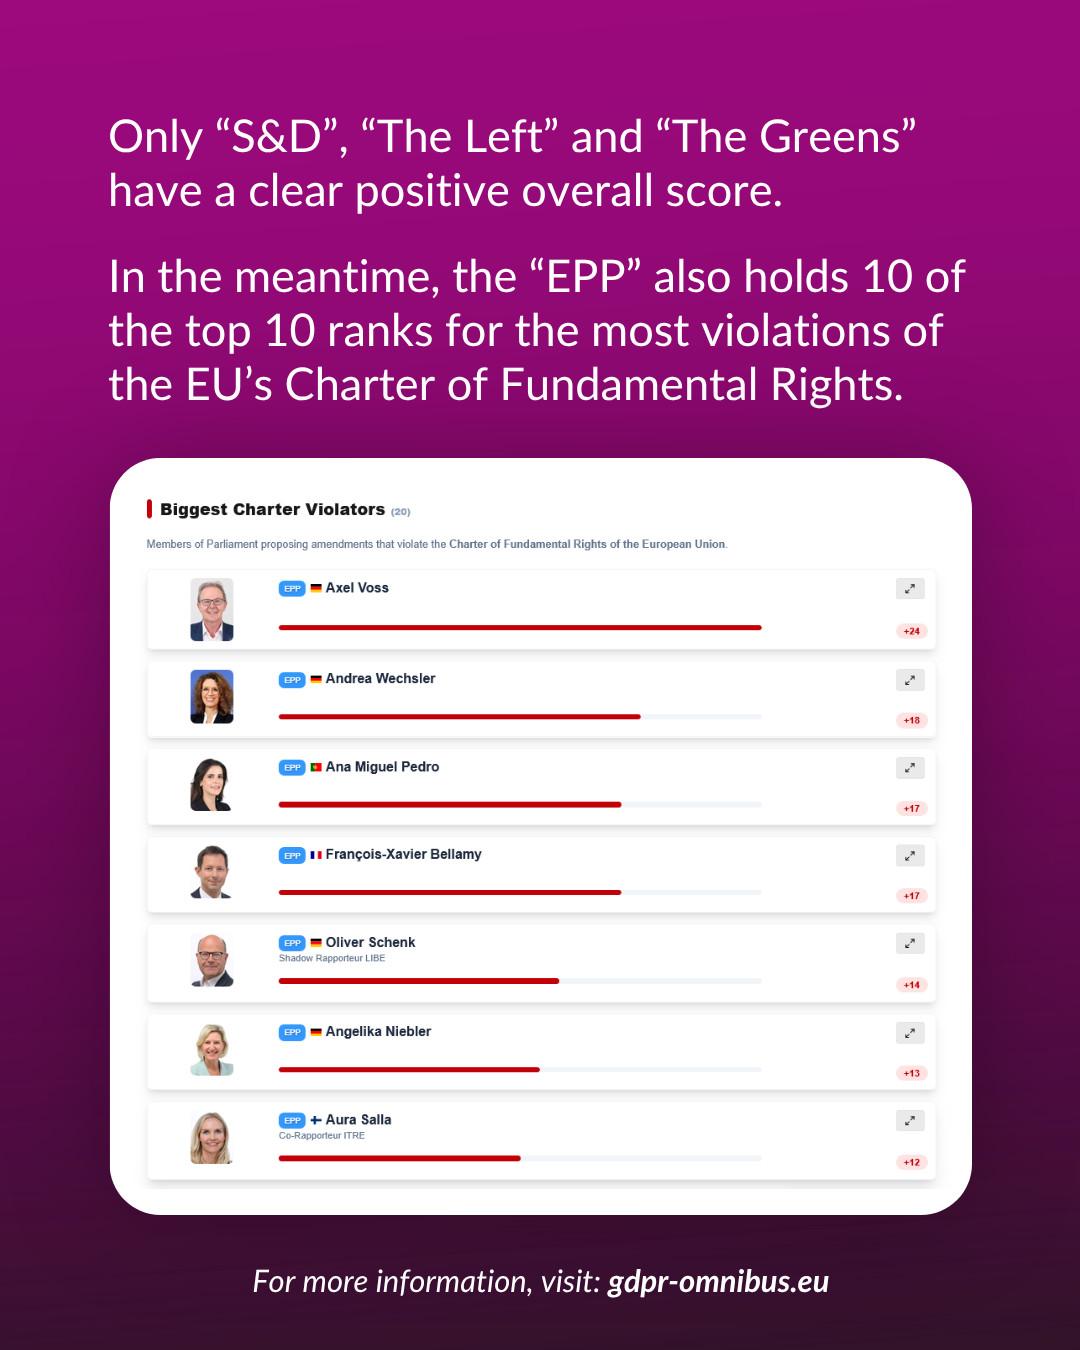
Only “S&D”, “The Left” and “The Greens” have a clear positive overall score.

In the meantime, the “EPP” also holds 10 of the top 10 ranks for the most violations of the EU’s Charter of Fundamental Rights.
ALT text

Only “S&D”, “The Left” and “The Greens” have a clear positive overall score. In the meantime, the “EPP” also holds 10 of the top 10 ranks for the most violations of the EU’s Charter of Fundamental Rights.

@thenewoil@mastodon.thenewoil.org
@ggus@mastodon.social

In Amsterdam next week: Join @torproject and Internet Archive Europe for a conversation about threats to the open internet and how Onion Services can help keep the web open.

"Avoiding the Internet Achilles' heel: Locking the web open with Onion Services"

📅 October 8, 5:30 - 7:30 PM
📍 Oudeschans 16, 1011 KZ Amsterdam

Evening Program:
* Presentation
* Talk with slides
* Q&A
* Informal happy hour & conversation

To join the event, please register below.

luma.com/s64zolbc

luma.com

Avoiding the Internet Achilles' heel: locking the web open with Onion Services · Luma

Join the Internet Archive Europe and members of the Tor Project to discuss the current threats to internet access, focusing on the recent events revealing the…

@thenewoil@mastodon.thenewoil.org
@noybeu@mastodon.social

🇪🇺 The is currently changing its core privacy law, the . Members of the European Parliament have made more than 1000 amendments - we have analyzed them all. 🔍 Want to know who is playing into the hands of by undermining protections, and who is actually trying to defend your ?

👉 Visit gdpr-omnibus.eu and look up your MEP by country and political group.

If the European Commission and the EU Member States get their way, the 
“Digital Omnibus” will result in a fundamental change to EU privacy laws.

What about the European Parliament? 

To find out more, noyb has analysed more than 1,000 amendments that Members of Parliament (MEPs) have tabled. This analysis shows that many MEPs are in favour of stripping people of their privacy rights – while others still push back.
ALT text

If the European Commission and the EU Member States get their way, the “Digital Omnibus” will result in a fundamental change to EU privacy laws. What about the European Parliament? To find out more, noyb has analysed more than 1,000 amendments that Members of Parliament (MEPs) have tabled. This analysis shows that many MEPs are in favour of stripping people of their privacy rights – while others still push back.

The European People’s Party (EPP) is clearly fighting the hardest against users' rights, having made many amendments that favour big tech.

This includes the limitation of the scope of privacy protections and the proposal of far-reaching exceptions for high-risk AI.

“The European Conservatives and Reformists” (ECR) also performed poorly overall. “The Patriots” achieved a better score, but it was still negative.
ALT text

The European People’s Party (EPP) is clearly fighting the hardest against users' rights, having made many amendments that favour big tech. This includes the limitation of the scope of privacy protections and the proposal of far-reaching exceptions for high-risk AI. “The European Conservatives and Reformists” (ECR) also performed poorly overall. “The Patriots” achieved a better score, but it was still negative.

The “Sovereigns” and “Renew” both have an even score of zero.

At the same time, however, Renew dominates the ranking of most “pushback” against the Commission’s flawed proposals with 5 of the top 10 MEPs in that category.
ALT text

The “Sovereigns” and “Renew” both have an even score of zero. At the same time, however, Renew dominates the ranking of most “pushback” against the Commission’s flawed proposals with 5 of the top 10 MEPs in that category.

Only “S&D”, “The Left” and “The Greens” have a clear positive overall score.

In the meantime, the “EPP” also holds 10 of the top 10 ranks for the most violations of the EU’s Charter of Fundamental Rights.
ALT text

Only “S&D”, “The Left” and “The Greens” have a clear positive overall score. In the meantime, the “EPP” also holds 10 of the top 10 ranks for the most violations of the EU’s Charter of Fundamental Rights.

@thenewoil@mastodon.thenewoil.org
@yawnbox@disobey.net
@privacyguides@neat.computer

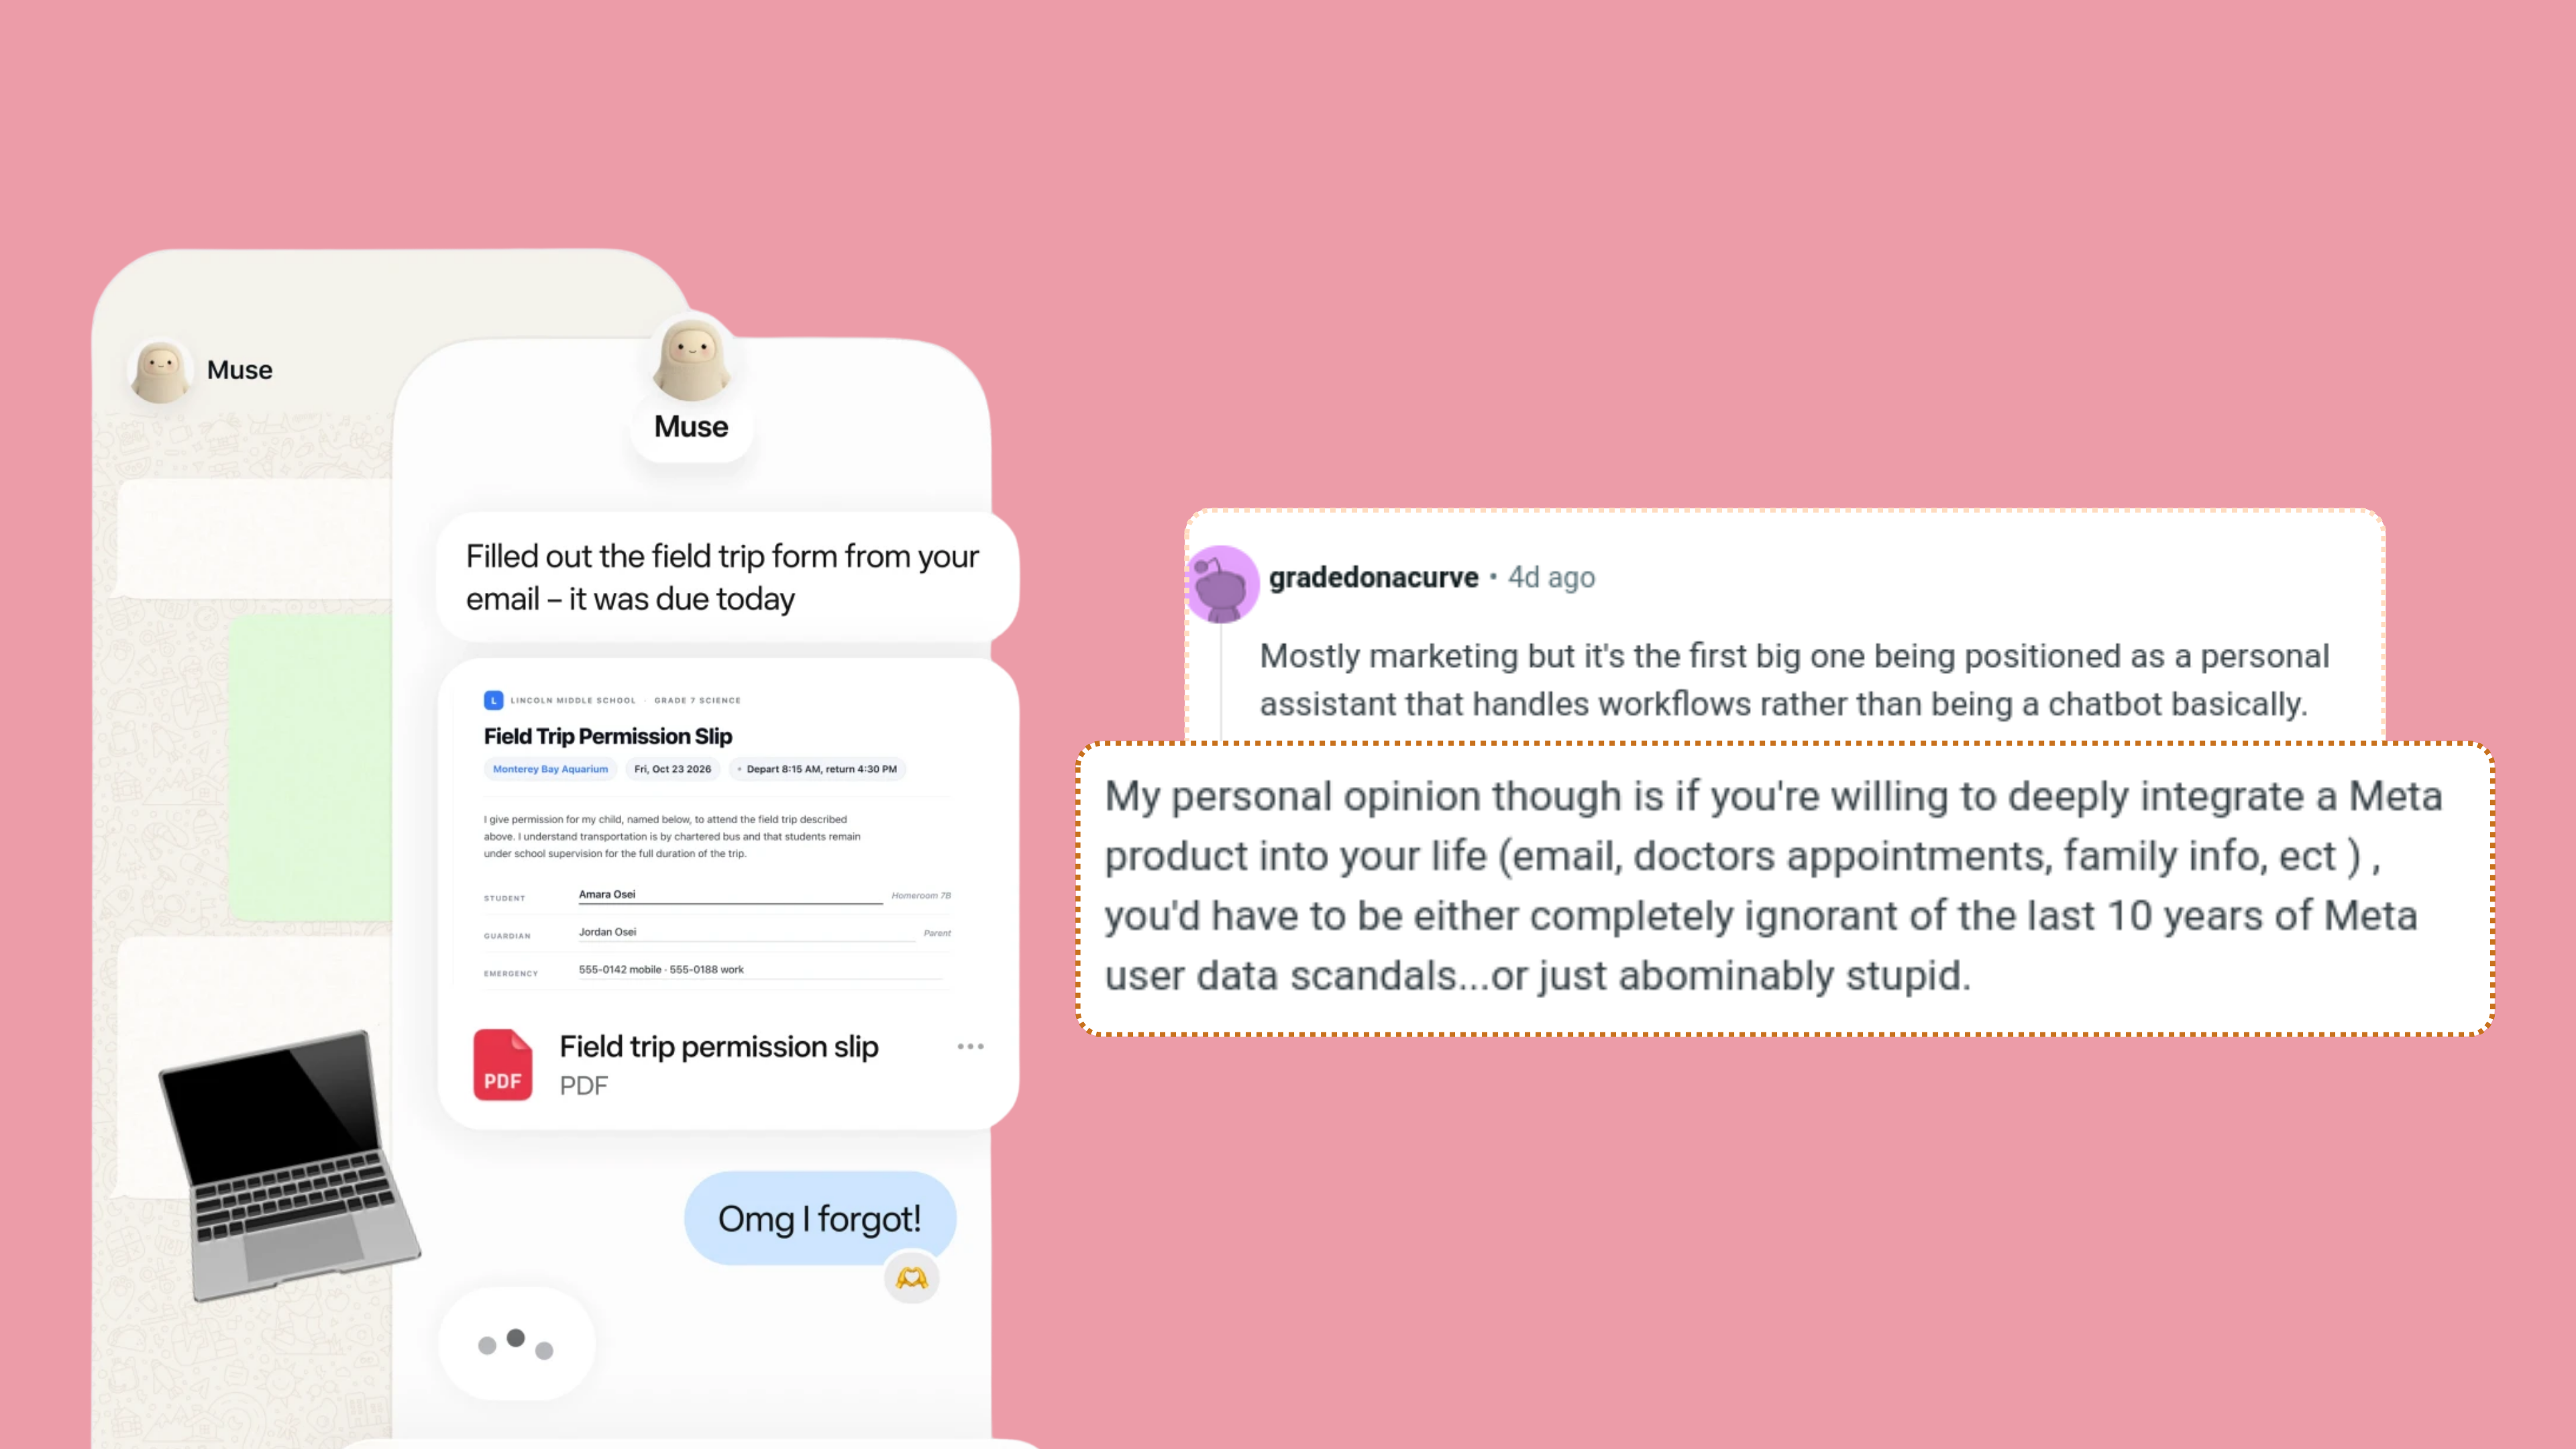
🚨 This Week in Privacy #74 will be live in 30 minutes! Leaked internal documents show that Meta's Muse AI agent is building dossiers on your friends, family and you, even if you've never used it before!

We'll also be talking about the latest & news!

👋 Come watch and join the Q&A!

youtube.com/@privacyguides/live

youtube.com

Muse is Collecting YOUR Data (Even if You Don't Use It)

Leaked internal documents show that Meta's Muse AI agent is building dossiers on your friends, family and you, even if you've never used it before, Kagi is e...

@thenewoil@mastodon.thenewoil.org
@xabd@mastodon.social

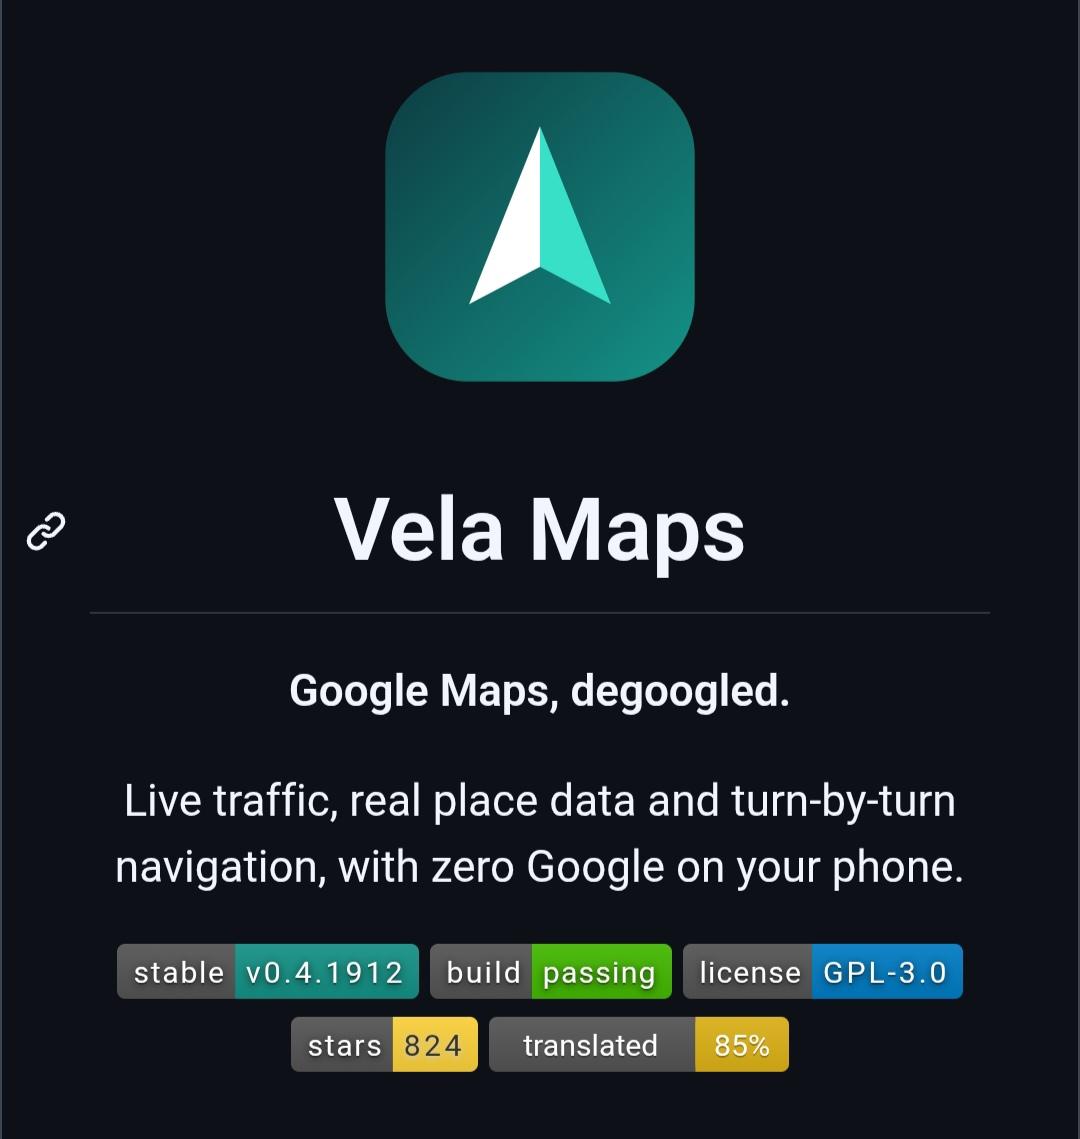
🗺️ Looking for a de-Googled alternative to Google Maps?

Vela Maps is an open-source Android maps app built around OpenStreetMap and other open data.

It supports offline maps, turn-by-turn navigation, public transit, and live traffic without Google Play Services or a Google account.

It can even run with Google completely disabled for a fully de-Googled experience.

More details & alternatives: digitalescapetools.com/tools/v

Vela Maps logo and app page showing the tagline “Google Maps, degoogled,” with live traffic, place data, turn-by-turn navigation, and badges for version, build status, GPL-3.0 license, stars, and translation progress.
ALT text

Vela Maps logo and app page showing the tagline “Google Maps, degoogled,” with live traffic, place data, turn-by-turn navigation, and badges for version, build status, GPL-3.0 license, stars, and translation progress.

@thenewoil@mastodon.thenewoil.org
@frontenddogma@mas.to
@ggus@mastodon.social

In Amsterdam next week: Join @torproject and Internet Archive Europe for a conversation about threats to the open internet and how Onion Services can help keep the web open.

"Avoiding the Internet Achilles' heel: Locking the web open with Onion Services"

📅 October 8, 5:30 - 7:30 PM
📍 Oudeschans 16, 1011 KZ Amsterdam

Evening Program:
* Presentation
* Talk with slides
* Q&A
* Informal happy hour & conversation

To join the event, please register below.

luma.com/s64zolbc

luma.com

Avoiding the Internet Achilles' heel: locking the web open with Onion Services · Luma

Join the Internet Archive Europe and members of the Tor Project to discuss the current threats to internet access, focusing on the recent events revealing the…

@thenewoil@mastodon.thenewoil.org
@harald@hub.volse.no
The inclusion of Autistici/Inventati on the US Specially Designated Global Terrorist list is a kick in the guts for all of us hosting services for others, whether it's fediverse instances, blogs, mailing lists or anything else. While most of us will hopefully never be on the receiving end of such a designation, the US regime has demonstrated how easily they can ruin our lives by throwing a politically motivated terror designation our way.

You may think that you're safe. You're not doing anything illegal after all. Just providing some infrastructure, a services or a place for people to come together and communicate. Privately. In confidence. Anonymously.

That was also what Autistici/Inventati was doing.

We're all targets now. And if we don't stand up against it, we let the fascists win!

In Autistici/Inventati's own words:
Let us have a thousand servers, a thousand networks. Let us flood them with possibilities until they run out of time and money to pursue and persecute us.


#antifa #activism #digitalsovereignity #privacy

hub.volse.no

Volse Hubzilla

@thenewoil@mastodon.thenewoil.org
@GalacticGoddess@ieji.de

Europeans/EU Citizens!

Update on the EU Kids Act:

The EU Commission has opened up the submission form for feedback on the bill. Let them know how much you don't want this! Let them know how much harm this bill will do to civil rights and economic stability! It's better to try and fail then to roll over and take it!

ec.europa.eu/info/law/better-r

P.S. And as always, mail/call your MEPs and other relevant government officials!

@maxim@chaos.social
chatcontrol 1.0

In a few minutes, parliament will vote on chatcontrol. There are a few other votes first. You can see the list of amendments to be voted on here: europarl.europa.eu/sedcms/voti

The actual text for the amendments is here:
europarl.europa.eu/plenary/en/

Livestream: europarl.europa.eu/streaming/?

The votes about chatcontrol are only the 4th item in the list of things to be voted on, but you'll likely have to wait a bit: europarl.europa.eu/sedcms/docu

@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer

🚨 This Week in Privacy #73 is live! We’re covering Reddit’s latest moves to limit anonymous access, including requiring users to log in to view old.reddit.com, discontinuing RSS feeds, and ending public API access.

We'll also be talking about the latest & news!

👋 Come watch and join the Q&A!

streamyard.com/watch/4CSyzqGkQ

streamyard.com

Is This The End of Anonymous Reddit?

Reddit is forcing users to login to view old.reddit.com, discontinuing it's RSS feeds and ending public API access killing privacy preserving third party clients. We'll be covering the latest in privacy & security news, so join us for This Week In Privacy #73!

@thenewoil@mastodon.thenewoil.org
@helloyanis@furries.club

I added Twitter to my extension to bypass age verification!

Hi! If you don't know me, I made an for to skip age verification screens on many platforms!

Recently, (yes, I'm not calling it X!) sent a cease and deceist letter to that allowed you to browse privately. I think this sucks, so now if you want to see an age restricted post you can use my extension to show it! (Still needs to be logged in to an account however, otherwise twitter won't return the tweet data)

🧩 Extension : addons.mozilla.org/addon/age-v

💻 Source : github.com/helloyanis/age-veri

Basically, it works by taking all the data from age restricted posts and re-arranging it in the way that regular posts do!

If you're still on twitter (why!) feel free to give it a try, and give me some feedback! Thanks!! 🦊🧡

@privacy@programming.dev @privacy@lemmy.ml

github.com

GitHub - helloyanis/age-verification-bypass: Extension to bypass age verification on some websites

Extension to bypass age verification on some websites - helloyanis/age-verification-bypass

@thenewoil@mastodon.thenewoil.org
@royaards@newsie.social

Post-privacy society. Cartoon for Dutch newspaper Trouw.

Cartoon depicting a surveillance-heavy urban scene. A storefront labeled 'Meta Glasses' displays a blue infinity logo and a giant pair of smart glasses mounted above. Multiple security cameras, drones, and AI monitoring devices beam spotlights downward at pedestrians below. Signs read 'FREE AI'," and 'FREE DOWNLOAD'. People are walking down the street; where they are hit by one of the spotlights they become naked. People wearing smart glasses also shoot out beams to other people, making them appear naked. One person is looking up at a traffic sign that reads 'No privacy'.
ALT text

Cartoon depicting a surveillance-heavy urban scene. A storefront labeled 'Meta Glasses' displays a blue infinity logo and a giant pair of smart glasses mounted above. Multiple security cameras, drones, and AI monitoring devices beam spotlights downward at pedestrians below. Signs read 'FREE AI'," and 'FREE DOWNLOAD'. People are walking down the street; where they are hit by one of the spotlights they become naked. People wearing smart glasses also shoot out beams to other people, making them appear naked. One person is looking up at a traffic sign that reads 'No privacy'.

@thenewoil@mastodon.thenewoil.org
@w_b@mastodon.world

Hey Fediverse!

First anyone have recommendations for a VPN service that will let me appear to be in my home area to stream football games while I'm vacation?

Bonus feature would be to also appear to be in Canada to stream CBC Gem content.

Privacy would be great too.


@ggus@mastodon.social

In Amsterdam next week: Join @torproject and Internet Archive Europe for a conversation about threats to the open internet and how Onion Services can help keep the web open.

"Avoiding the Internet Achilles' heel: Locking the web open with Onion Services"

📅 October 8, 5:30 - 7:30 PM
📍 Oudeschans 16, 1011 KZ Amsterdam

Evening Program:
* Presentation
* Talk with slides
* Q&A
* Informal happy hour & conversation

To join the event, please register below.

luma.com/s64zolbc

luma.com

Avoiding the Internet Achilles' heel: locking the web open with Onion Services · Luma

Join the Internet Archive Europe and members of the Tor Project to discuss the current threats to internet access, focusing on the recent events revealing the…

@thenewoil@mastodon.thenewoil.org
@ggus@mastodon.social

In Amsterdam next week: Join @torproject and Internet Archive Europe for a conversation about threats to the open internet and how Onion Services can help keep the web open.

"Avoiding the Internet Achilles' heel: Locking the web open with Onion Services"

📅 October 8, 5:30 - 7:30 PM
📍 Oudeschans 16, 1011 KZ Amsterdam

Evening Program:
* Presentation
* Talk with slides
* Q&A
* Informal happy hour & conversation

To join the event, please register below.

luma.com/s64zolbc

luma.com

Avoiding the Internet Achilles' heel: locking the web open with Onion Services · Luma

Join the Internet Archive Europe and members of the Tor Project to discuss the current threats to internet access, focusing on the recent events revealing the…

@zerionchat@mastodon.social

🔐 Your private conversations don’t need a phone number, account or central messaging server.

Meet Zerion private messaging over Tor with post-quantum encryption on every message.

No ads. No tracking. Open source.

Download Zerion on Google Play and try it with your friends and family.

play.google.com/store/apps/det

play.google.com

Zerion Chat - Apps on Google Play

Private messaging over Tor. No phone number, account or central server.

@Tutanota@mastodon.social

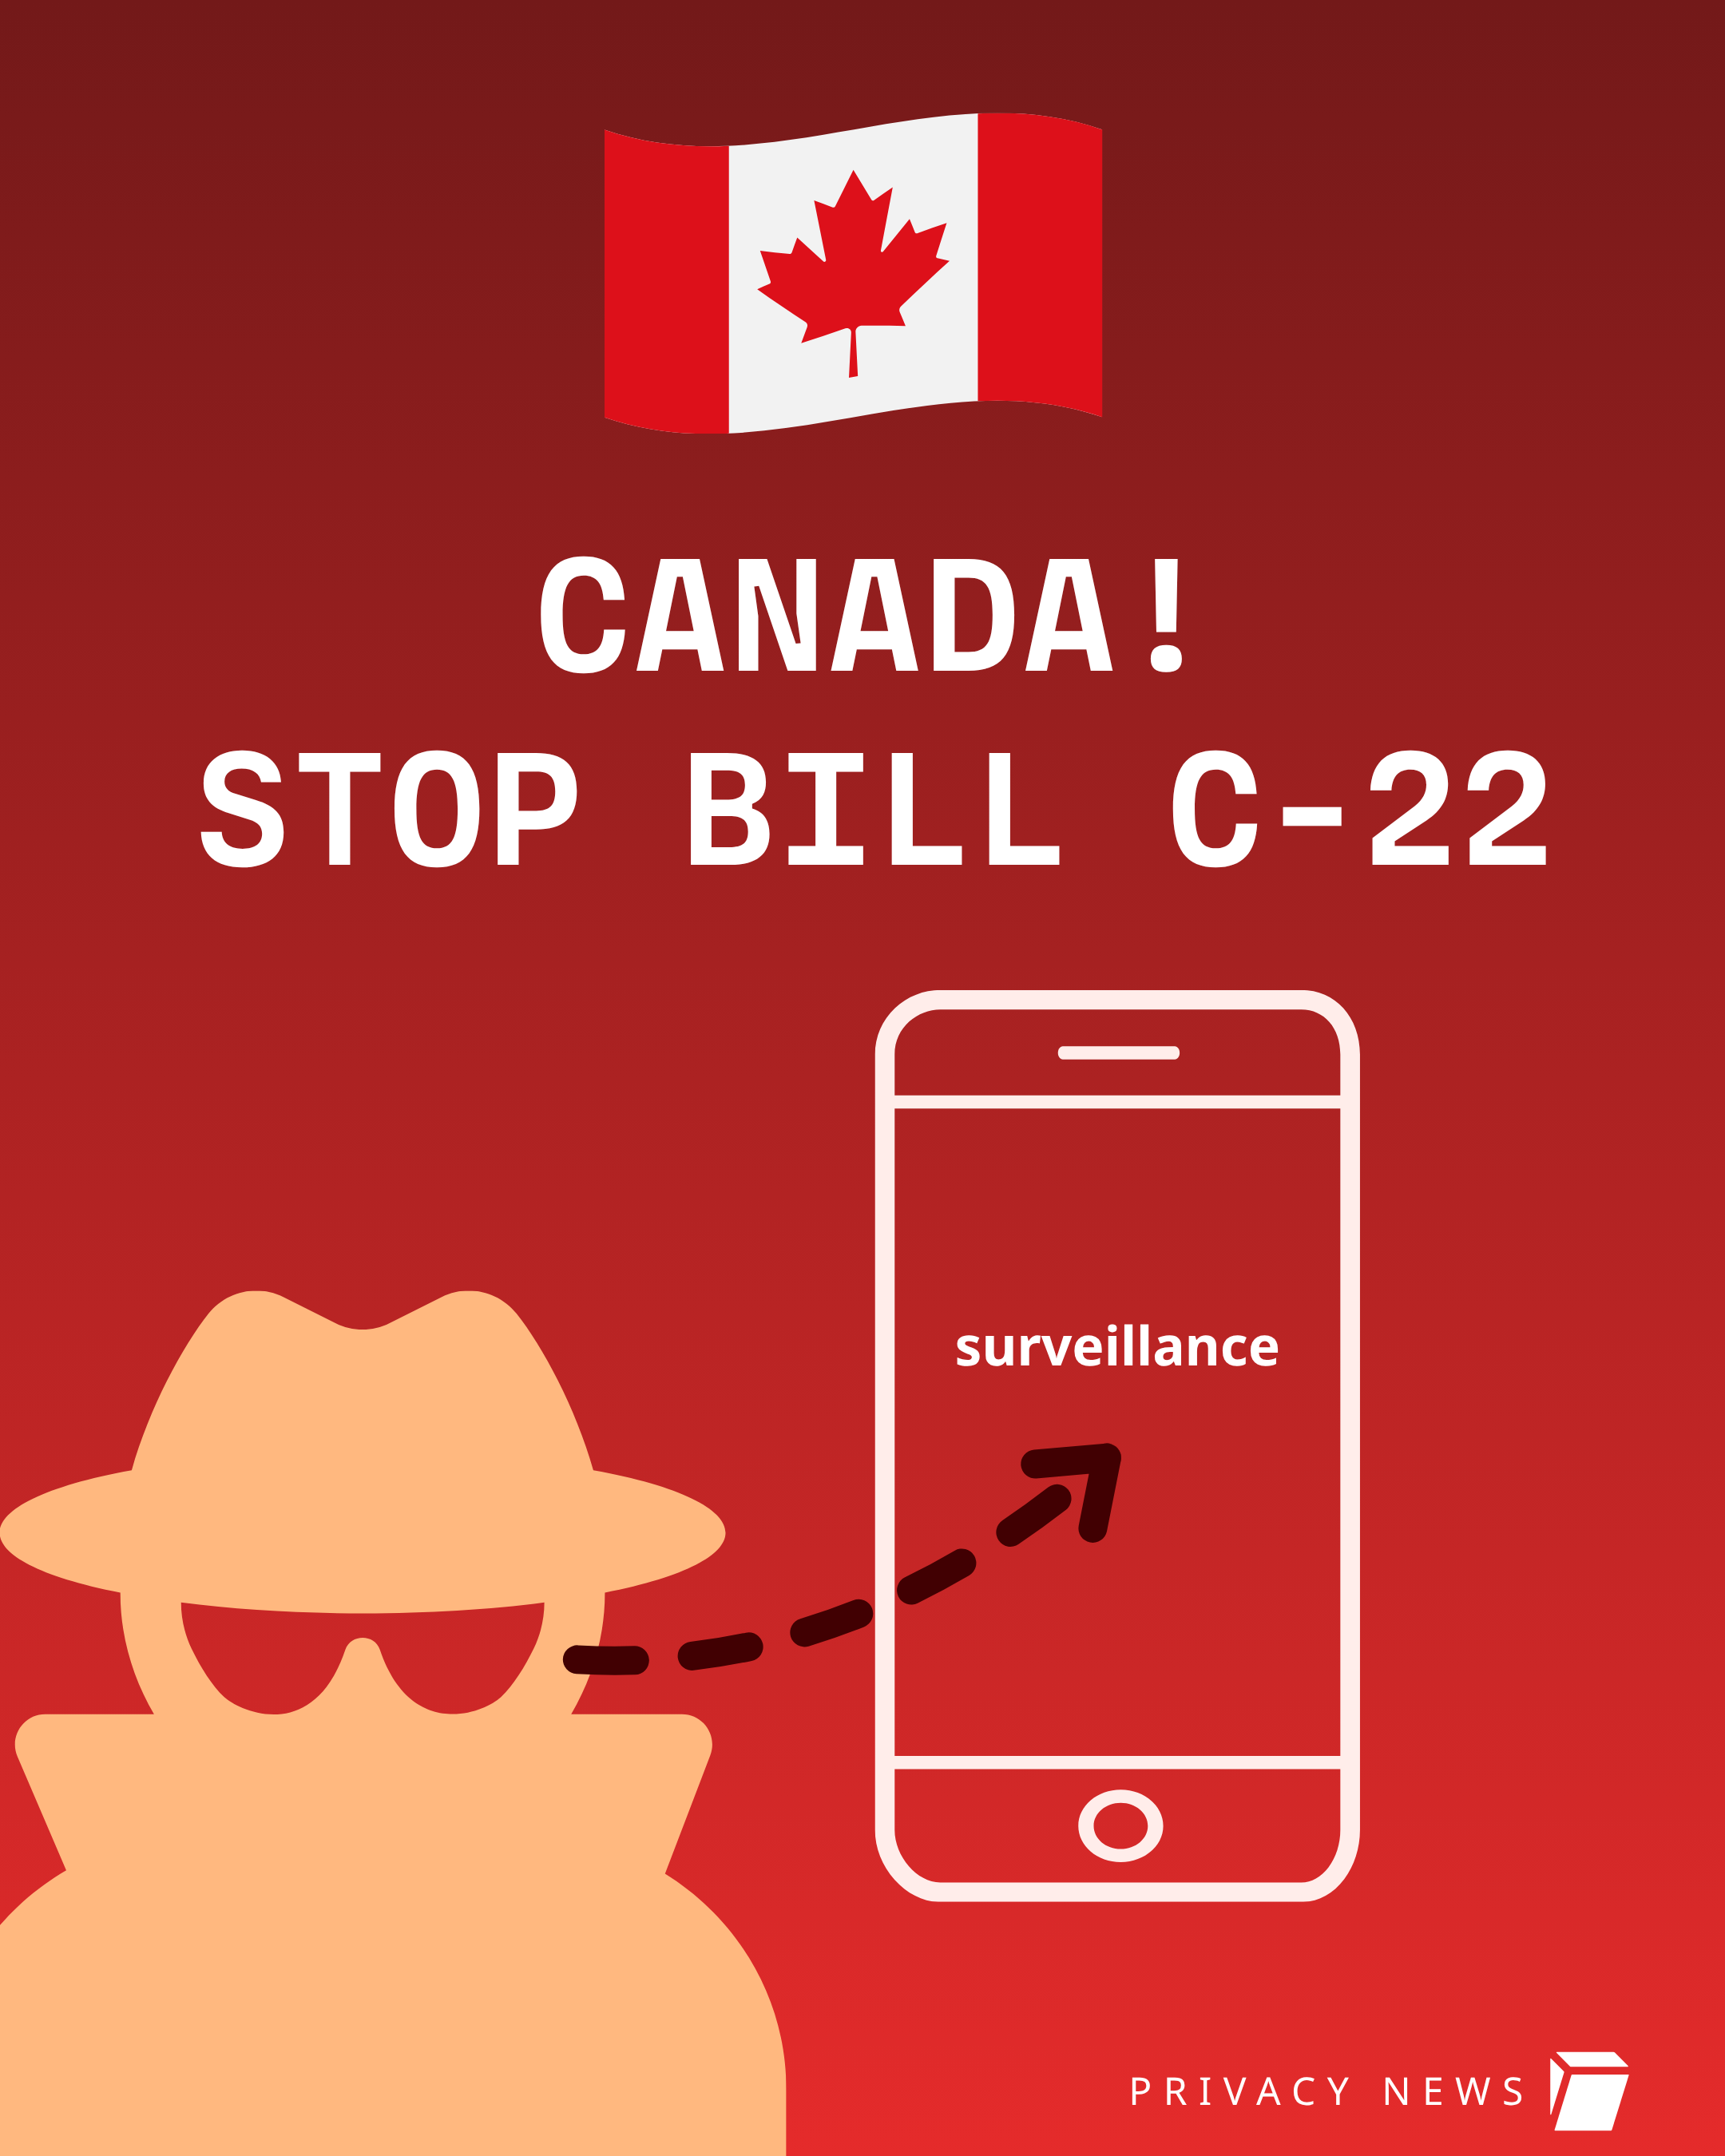
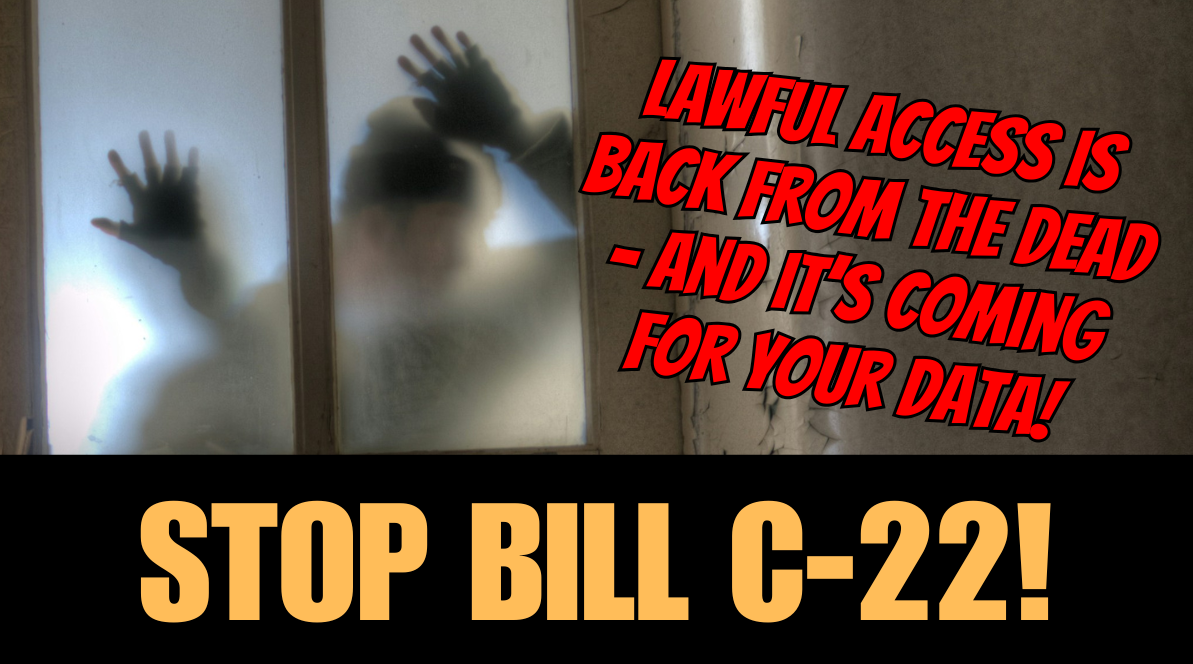
🚨Canada is about to destroy with Bill C-22 — one of the worst surveillance laws.

We stopped Bill C-2 just last year (details: tuta.com/blog/canada-bill-c2-s)

Let's do it again! We say 💪

Because there's no such thing as "lawful access" for the good guys only.

We've signed an open letter against Bill C-22, please join the fight!

👉 theccf.ca/stop-government-spyi

👉 Open Letter: fixc22.ca

Canada stop Bill C-22
ALT text

Canada stop Bill C-22

@freddy@social.lol
@freddy@social.lol
@xabd@mastodon.social

Looking for a self-hosted alternative to Jira or Linear?

Plane is an open-source project management platform for tracking issues, planning cycles, managing projects, and building product roadmaps.

It includes Pages, analytics, custom views, and modules to help teams organize work and track progress.

Self-host it on your own infrastructure with Docker or Kubernetes for more control over your project data.

More details & alternatives:
digitalescapetools.com/tools/p

Screenshot of the Plane project page showing its logo and tagline, “Modern project management for all teams.” It describes Plane as an open-source tool for tracking issues, running sprints and cycles, and managing product roadmaps.
ALT text

Screenshot of the Plane project page showing its logo and tagline, “Modern project management for all teams.” It describes Plane as an open-source tool for tracking issues, running sprints and cycles, and managing product roadmaps.

@jonsnow@mastodon.online
@linuxeasy@mastodon.uno
@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer
@thenewoil@mastodon.thenewoil.org
@mahryekuh@hachyderm.io

An interesting conflict between a Dutch media creator Roel Maalderink (together with Bits of Freedom) and Meta regarding Meta glasses.

The guy made a video wearing the glasses outside the Meta office in Amsterdam.

The video showed several Meta employees reacting negatively to the glasses, and even asking multiple times if he was filming (showing that even they couldn’t see if the glasses are active.)

Instagram took the video offline, which is the first time this creator had a takedown of one of his videos.

I hope this goes viral beyond The Netherlands.

Edit: Added a Fedi post by Roel himself.

mastodon.social/@Roelmaalderin

mastodon.social

Roelmaalderink (@Roelmaalderink@mastodon.social)

Attached: 1 video Meta doesn’t want you to watch this video

@sgbv@infosec.exchange

F-Droid 2.0 is finally out. The biggest update in a decade, and the first one that actually does not look like it was designed in a shed.

The whole app is a Kotlin Compose rewrite now. Navigation is down to three tabs: Discover, Search, My Apps. Updates are automatic in the background by default, and the new session installer finally makes the install flow on par with the Play Store (thanks, EU DMA).

The trade-offs?
- No more Privileged Extension support
- Tor auto-detection is gone, you now need a Tor VPN for that
- The panic wipe feature and the fake calculator disguise are also dead
- Android 6 support has been dropped

This a massive step forward for FOSS Android. But do read the release notes before updating if you relied on those privacy tools.

lwn.net/Articles/1096444/

lwn.net

F-Droid 2.0: A new chapter for Android freedom

The F-Droid project has announced the release of F-Droid 2.0, which is a complete redesign of t [...]

@nils@hollo.weisensee.me

"The Instagram removal underscores the extraordinary power of the company: Meta can both promote products and censor criticism when it suits them. When a privacy-respecting satirical video shows that even Meta employees find these glasses objectionable, Meta censors their message."

https://www.bitsoffreedom.nl/en/2026/09/24/meta-removes-critical-widely-viewed-video-about-metas-pervert-glasses/

bitsoffreedom.nl

Meta removes critical, widely viewed video about Meta’s “Pervert Glasses” – Bits of Freedom

@vmcall@infosec.exchange · Reply to SNeela

On , watching the root directory (`C:\`) reports the full path of every file touched anywhere on the system, regardless of permissions, even across users 🙂. Microsoft considers this an ✨ undocumented feature ✨. The most severe case we found is leaking which websites another user visits in real time, a huge issue that , once again, said was an undocumented feature. Our findings got Microsoft nominated for the lamest vendor response category at the [Pwnies Award 2026](youtube.com/live/8Eo4ZDQTAFs?t).

Here's a demo of it visiting @arstechnica

A cross-user watcher mounted on C:\ reports events on all files, even if the user can’t read them. In this video, an attacker filters for “http,” while another user visits arstechnica.com in Firefox.
ALT text

A cross-user watcher mounted on C:\ reports events on all files, even if the user can’t read them. In this video, an attacker filters for “http,” while another user visits arstechnica.com in Firefox.

@thenewoil@mastodon.thenewoil.org
@nils@hollo.weisensee.me

"The Instagram removal underscores the extraordinary power of the company: Meta can both promote products and censor criticism when it suits them. When a privacy-respecting satirical video shows that even Meta employees find these glasses objectionable, Meta censors their message."

https://www.bitsoffreedom.nl/en/2026/09/24/meta-removes-critical-widely-viewed-video-about-metas-pervert-glasses/

bitsoffreedom.nl

Meta removes critical, widely viewed video about Meta’s “Pervert Glasses” – Bits of Freedom

@mahryekuh@hachyderm.io

An interesting conflict between a Dutch media creator Roel Maalderink (together with Bits of Freedom) and Meta regarding Meta glasses.

The guy made a video wearing the glasses outside the Meta office in Amsterdam.

The video showed several Meta employees reacting negatively to the glasses, and even asking multiple times if he was filming (showing that even they couldn’t see if the glasses are active.)

Instagram took the video offline, which is the first time this creator had a takedown of one of his videos.

I hope this goes viral beyond The Netherlands.

Edit: Added a Fedi post by Roel himself.

mastodon.social/@Roelmaalderin

mastodon.social

Roelmaalderink (@Roelmaalderink@mastodon.social)

Attached: 1 video Meta doesn’t want you to watch this video

@nils@hollo.weisensee.me

"The Instagram removal underscores the extraordinary power of the company: Meta can both promote products and censor criticism when it suits them. When a privacy-respecting satirical video shows that even Meta employees find these glasses objectionable, Meta censors their message."

https://www.bitsoffreedom.nl/en/2026/09/24/meta-removes-critical-widely-viewed-video-about-metas-pervert-glasses/

bitsoffreedom.nl

Meta removes critical, widely viewed video about Meta’s “Pervert Glasses” – Bits of Freedom

@Tutanota@mastodon.social

🚨Canada is about to destroy with Bill C-22 — one of the worst surveillance laws.

We stopped Bill C-2 just last year (details: tuta.com/blog/canada-bill-c2-s)

Let's do it again! We say 💪

Because there's no such thing as "lawful access" for the good guys only.

We've signed an open letter against Bill C-22, please join the fight!

👉 theccf.ca/stop-government-spyi

👉 Open Letter: fixc22.ca

Canada stop Bill C-22
ALT text

Canada stop Bill C-22

@oatmeal@kolektiva.social

is possibly the first app to block notetakers in meetings. It's in closed beta, Apple Silicon only right now. Developers claim AI fails to transcribe 2 out of 3 words when Kalypata is activated.

[…] Kalypta runs on your device while you are in a meeting and interrupts AI transcription of your voice. The people on the call hear you exactly as before — transcribers and note-takers listening in do not get usable text.

deveillance.com/kalypta

@i_ngli@assemblag.es

Yesterday’s win in :

~6m of building, I now have my own chat interface, on top of a local gateway to remote .

Nice here: sensitive terms get redacted locally, their semantic role is preserved for the model, and the originals are restored only on my side when the reply comes back.

The sensitive terms never leave my computer

This is exactly the kind of tiny geeky I wanted to exist.

If this sort of thing speaks to your own tinkering, say hi.

@thenewoil@mastodon.thenewoil.org
@parismarx@mastodon.online

John Ternus kicked off his tenure as Apple CEO by announcing the long-awaited folding iPhone.

But behind the scenes, it looks like products and services are going to get more expensive to please shareholders and he’s ready to sacrifice privacy on the altar of AI.

disconnect.blog/red-flags-at-t

disconnect.blog

Red flags at the start of Apple’s John Ternus era

Under the new CEO, products are more expensive and AI comes with more surveillance

@noybeu@mastodon.social

🔓 LEAKED DOCUMENT 🇮🇪 Shown below is an excerpt from the leaked proposal by the Irish Presidency. The Member States are expected to give their opinions by end of week. 🇪🇺

@maxschrems: “Under these proposals, the profits of companies would trump Europeans' fundamental right to ."

👉 Read more on our website 🔗 noyb.eu/en/ai-eu-member-states

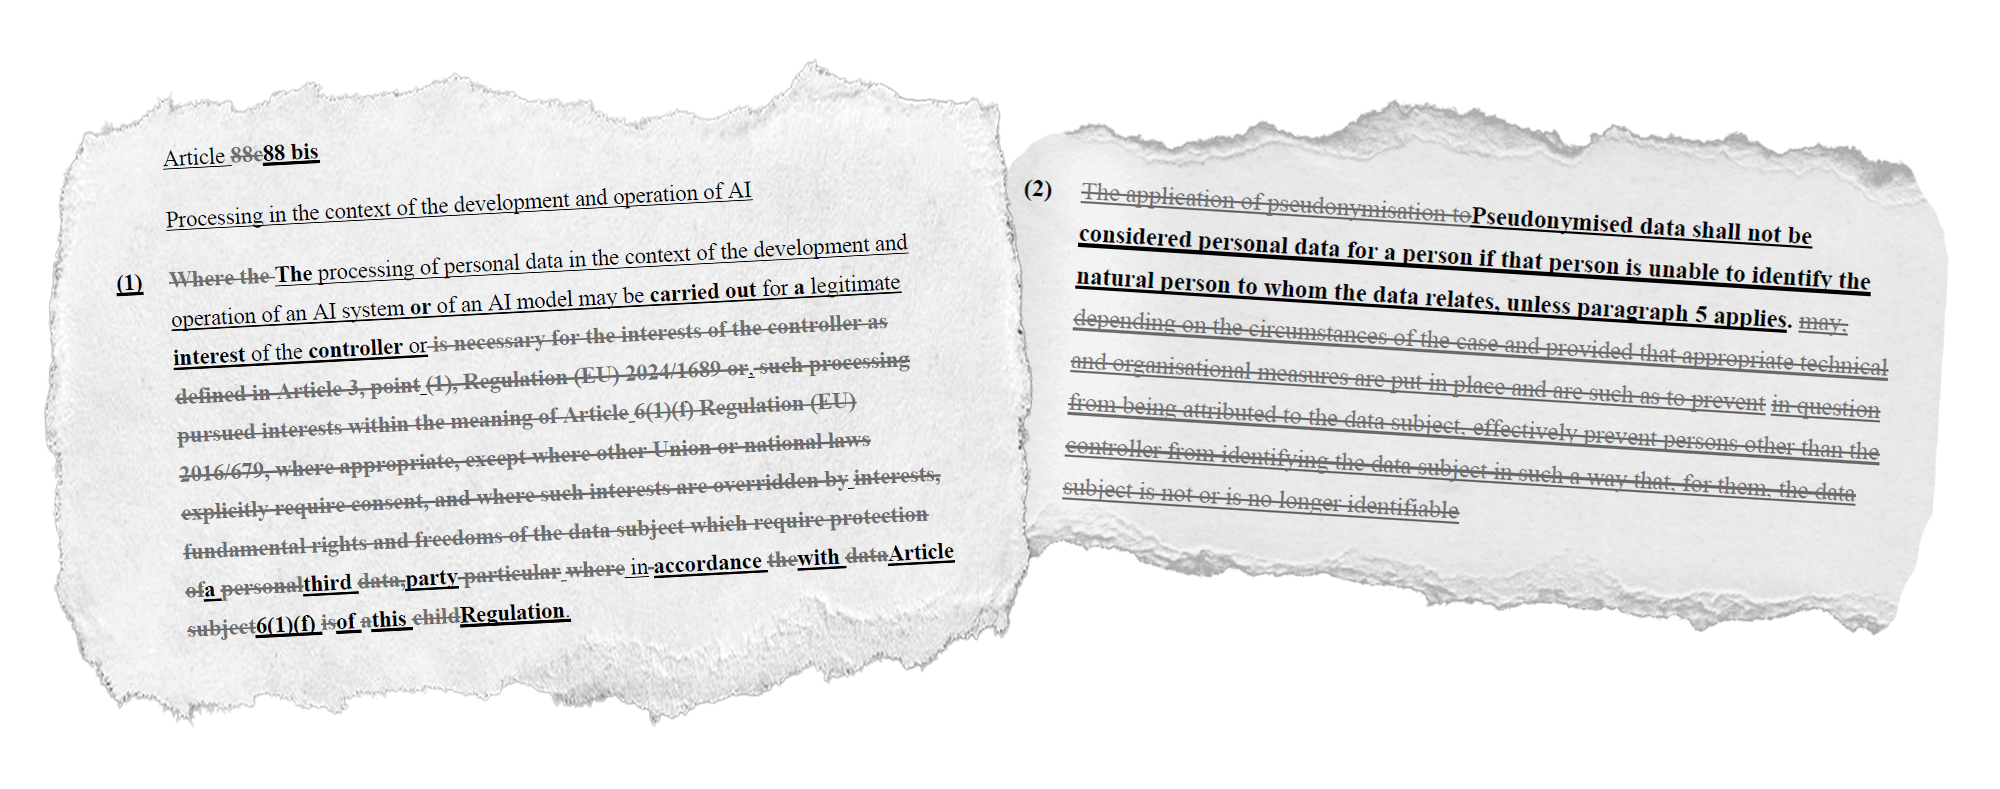
The image attached to this post shows part of the leaked text. It reads: "Article 88 bis: Processing in the context of the development and operation of AI: (1) The processing of personal data in the context of the development and operation of an AI system or of an AI model may be carried out for a legitimate interest of the controller or a third party in accordance with Article6(1)(f) of this Regulation. (2) Pseudonymised data shall not be considered personal data for a person if that person is unable to identify the natural person to whom the data relates, unless paragraph 5 applies."
ALT text

The image attached to this post shows part of the leaked text. It reads: "Article 88 bis: Processing in the context of the development and operation of AI: (1) The processing of personal data in the context of the development and operation of an AI system or of an AI model may be carried out for a legitimate interest of the controller or a third party in accordance with Article6(1)(f) of this Regulation. (2) Pseudonymised data shall not be considered personal data for a person if that person is unable to identify the natural person to whom the data relates, unless paragraph 5 applies."

@DailyCyberSecurity@infosec.exchange
@thenewoil@mastodon.thenewoil.org
@noybeu@mastodon.social

🔓 LEAKED DOCUMENT 🇮🇪 Shown below is an excerpt from the leaked proposal by the Irish Presidency. The Member States are expected to give their opinions by end of week. 🇪🇺

@maxschrems: “Under these proposals, the profits of companies would trump Europeans' fundamental right to ."

👉 Read more on our website 🔗 noyb.eu/en/ai-eu-member-states

The image attached to this post shows part of the leaked text. It reads: "Article 88 bis: Processing in the context of the development and operation of AI: (1) The processing of personal data in the context of the development and operation of an AI system or of an AI model may be carried out for a legitimate interest of the controller or a third party in accordance with Article6(1)(f) of this Regulation. (2) Pseudonymised data shall not be considered personal data for a person if that person is unable to identify the natural person to whom the data relates, unless paragraph 5 applies."
ALT text

The image attached to this post shows part of the leaked text. It reads: "Article 88 bis: Processing in the context of the development and operation of AI: (1) The processing of personal data in the context of the development and operation of an AI system or of an AI model may be carried out for a legitimate interest of the controller or a third party in accordance with Article6(1)(f) of this Regulation. (2) Pseudonymised data shall not be considered personal data for a person if that person is unable to identify the natural person to whom the data relates, unless paragraph 5 applies."

@d@greennuclear.online · Reply to Tjeerd Royaards

@royaards @Heidentweet @JigmeDatse @GLaDTheresCake @romli The is just nice revamped version Chatcontrol 😡same mass surveillance, different packaging.

Monitoring all EU citizens under the guise of "protecting children." The bureaucrats dream of a panopticon dream.

But we've won this fight before.
The EU Kids Act can still be stopped. Sign the citizen initiative: citizens-initiative.europa.eu/

citizens-initiative.europa.eu

Initiative detail | European Citizens' Initiative

@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer
@thenewoil@mastodon.thenewoil.org
@Em0nM4stodon@infosec.exchange

I hate that I can recycle my posts about Chat Control every 6 months and they are still relevant.

Please don't give up, and keep fighting against authoritarian policies destroying our privacy rights ✊

We have a responsibility to fight for a better future for all, not only for ourselves but also for the next generations 💚🔒

@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer
@thenewoil@mastodon.thenewoil.org
@frontenddogma@mas.to
@thenewoil@mastodon.thenewoil.org
@bjmendelson@mastodon.social
@thenewoil@mastodon.thenewoil.org
@nemobis@mamot.fr · Reply to Jan Penfrat

@ilumium If the Commission actually cared about kids or evidence, you might expect the quadrennial Commission report ex GDPR art. 97 (eur-lex.europa.eu/eli/reg/2016) to say some words on the impact of past legislative efforts in this area. Yet there was nothing.
eur-lex.europa.eu/legal-conten

How did @je5perl call it? "Policy-driven evidence-making"?

 Children require specific protection when their personal data are processed ( 109 ). The GDPR is part of a comprehensive legal framework that ensures that children are protected offline as well as online ( 110 ). Given the increased presence of children online, a number of actions at EU and national level have been taken in recent years to support the protection of children online. Data protection authorities have imposed significant fines on social media companies for violation of the GDPR when processing children’s data. They also cooperate with other authorities to call for more protection of children in the area of advertising. In the 2020 report, the Commission invited the Board to adopt guidelines on the processing of children’s data and this work is currently under way ( 111 ). The Digital Services Act includes specific provisions to ensure a high level of privacy, safety and security of children using online platforms.

Some stakeholders report challenges with the exercise of data subject rights, when the data subjects are children. In particular, they report that children do not fully understand their rights, lack digital literacy skills and may be subject to undue influence ( 112 ). The Commission has funded several initiatives at national level on the protection of children’s data and on promoting data protection awareness among children ( 113 ). Under the Better Internet for Kids (BIK+) strategy, the Commission is providing awareness-raising resources and trainings to children on their digital rights, including data protection (e.g. digital consent) ( 114 ). There is increasing focus on the need for effective and privacy-friendly age verification tools. In early 2024, the Commission set up a taskforce on age verification with Member States, the Board and the European Regulators Group for Audiovisual Media Services, with the aim of discussing and supporting the development of a EU-wide approach to age verification. This work will now continue under the Digital Services Act Board, in the Protection of Minors Working Group. In the context of the EU Digital Identity Regulation ( 115 ), which entered into force in May 2024, the Commission is working to ensure that the European Digital Identity Wallet is offered to all EU citizens and residents in 2026, including for age verification. Meanwhile, before the Wallet ecosystem is fully operational, a short-term solution for age verification will be developed and become available across the EU.
ALT text

Children require specific protection when their personal data are processed ( 109 ). The GDPR is part of a comprehensive legal framework that ensures that children are protected offline as well as online ( 110 ). Given the increased presence of children online, a number of actions at EU and national level have been taken in recent years to support the protection of children online. Data protection authorities have imposed significant fines on social media companies for violation of the GDPR when processing children’s data. They also cooperate with other authorities to call for more protection of children in the area of advertising. In the 2020 report, the Commission invited the Board to adopt guidelines on the processing of children’s data and this work is currently under way ( 111 ). The Digital Services Act includes specific provisions to ensure a high level of privacy, safety and security of children using online platforms. Some stakeholders report challenges with the exercise of data subject rights, when the data subjects are children. In particular, they report that children do not fully understand their rights, lack digital literacy skills and may be subject to undue influence ( 112 ). The Commission has funded several initiatives at national level on the protection of children’s data and on promoting data protection awareness among children ( 113 ). Under the Better Internet for Kids (BIK+) strategy, the Commission is providing awareness-raising resources and trainings to children on their digital rights, including data protection (e.g. digital consent) ( 114 ). There is increasing focus on the need for effective and privacy-friendly age verification tools. In early 2024, the Commission set up a taskforce on age verification with Member States, the Board and the European Regulators Group for Audiovisual Media Services, with the aim of discussing and supporting the development of a EU-wide approach to age verification. This work will now continue under the Digital Services Act Board, in the Protection of Minors Working Group. In the context of the EU Digital Identity Regulation ( 115 ), which entered into force in May 2024, the Commission is working to ensure that the European Digital Identity Wallet is offered to all EU citizens and residents in 2026, including for age verification. Meanwhile, before the Wallet ecosystem is fully operational, a short-term solution for age verification will be developed and become available across the EU.

@thenewoil@mastodon.thenewoil.org
@ai6yr@m.ai6yr.org

👀

"...Hackers ripped down a Flock camera above a roadway, made a near-complete copy of the data stored inside it, and shared the files with 404 Media and WIRED, revealing in new detail how exactly Flock Safety’s cameras track the movements of both vehicles and people. The hackers say they are also publishing details on how they managed to obtain the software, in the hopes that other people may copy them.

The breach provides an unprecedented look inside a system that Flock has described as protected by on-device encryption. The hackers were able to copy the camera’s storage and recover an encryption key stored on the device, which unlocked videos of thousands of vehicle detections..."

404media.co/hackers-stole-floc

404media.co

Hackers Stole Flock’s Camera Software, Revealing How the Company Tracks Cars and People

While people around the U.S. are tearing down Flock cameras, one group of hackers went a step further: extracting the camera's software too.

@thenewoil@mastodon.thenewoil.org
@remixtures@tldr.nettime.org

"As it turns out, Apple realistically needs customer data to make Siri AI work well. So, starting with iOS 27, it is asking users to opt-in to training on your data.

A new section in the iOS 27 privacy policy shows that Apple has reversed its stance on using customers' data to train its AI models. Previously, the company assured customers that it had no need for customer data, and would figure out how to make Siri AI work well without it.

Apple maintains that it "takes steps to ensure that personal data is not stored or used by Apple." But as Heise points out, and Apple has said in the terms of service for a few years now, the audio material may be listened to by Apple employees after anonymization.

Currently, new feature is opt-in only. When iOS 27 rolls out on Monday, September 14, users will see a prompt that asks users to help improve the chatbot, with an agree or "not now" button.

It also admits that data collected may be reviewed by "review personnel." It is unclear if "review personnel" are Apple employees or a third-party company contracted to read conversation transcripts, as it has historically been.

The change is a big deal."

appleinsider.com/articles/26/0

appleinsider.com

Apple has altered course on using customer data to train its AI

As it turns out, Apple realistically needs customer data to make Siri AI work well. So, starting with iOS 27, it is asking users to opt-in to training on your data.

@thenewoil@mastodon.thenewoil.org
@_elena@mastodon.social

Does anyone have any insights / scoops about the upcoming , set to be introduced this Thursday to "age gate" access to social media platforms across the EU? (Thus forcing every citizen to upload their government ID to establish their age)

I'm super worried about the impact on the and the Fediverse in particular.

🔗 : politico.eu/article/eu-to-prop

I wish they would share a clear description of the platforms affected by this legislation.

politico.eu

EU to limit access to social media before age of 15

New “EU KIDS Act” would require TikTok and Instagram to create safer accounts for younger users.

@thenewoil@mastodon.thenewoil.org
@mysk@mastodon.social

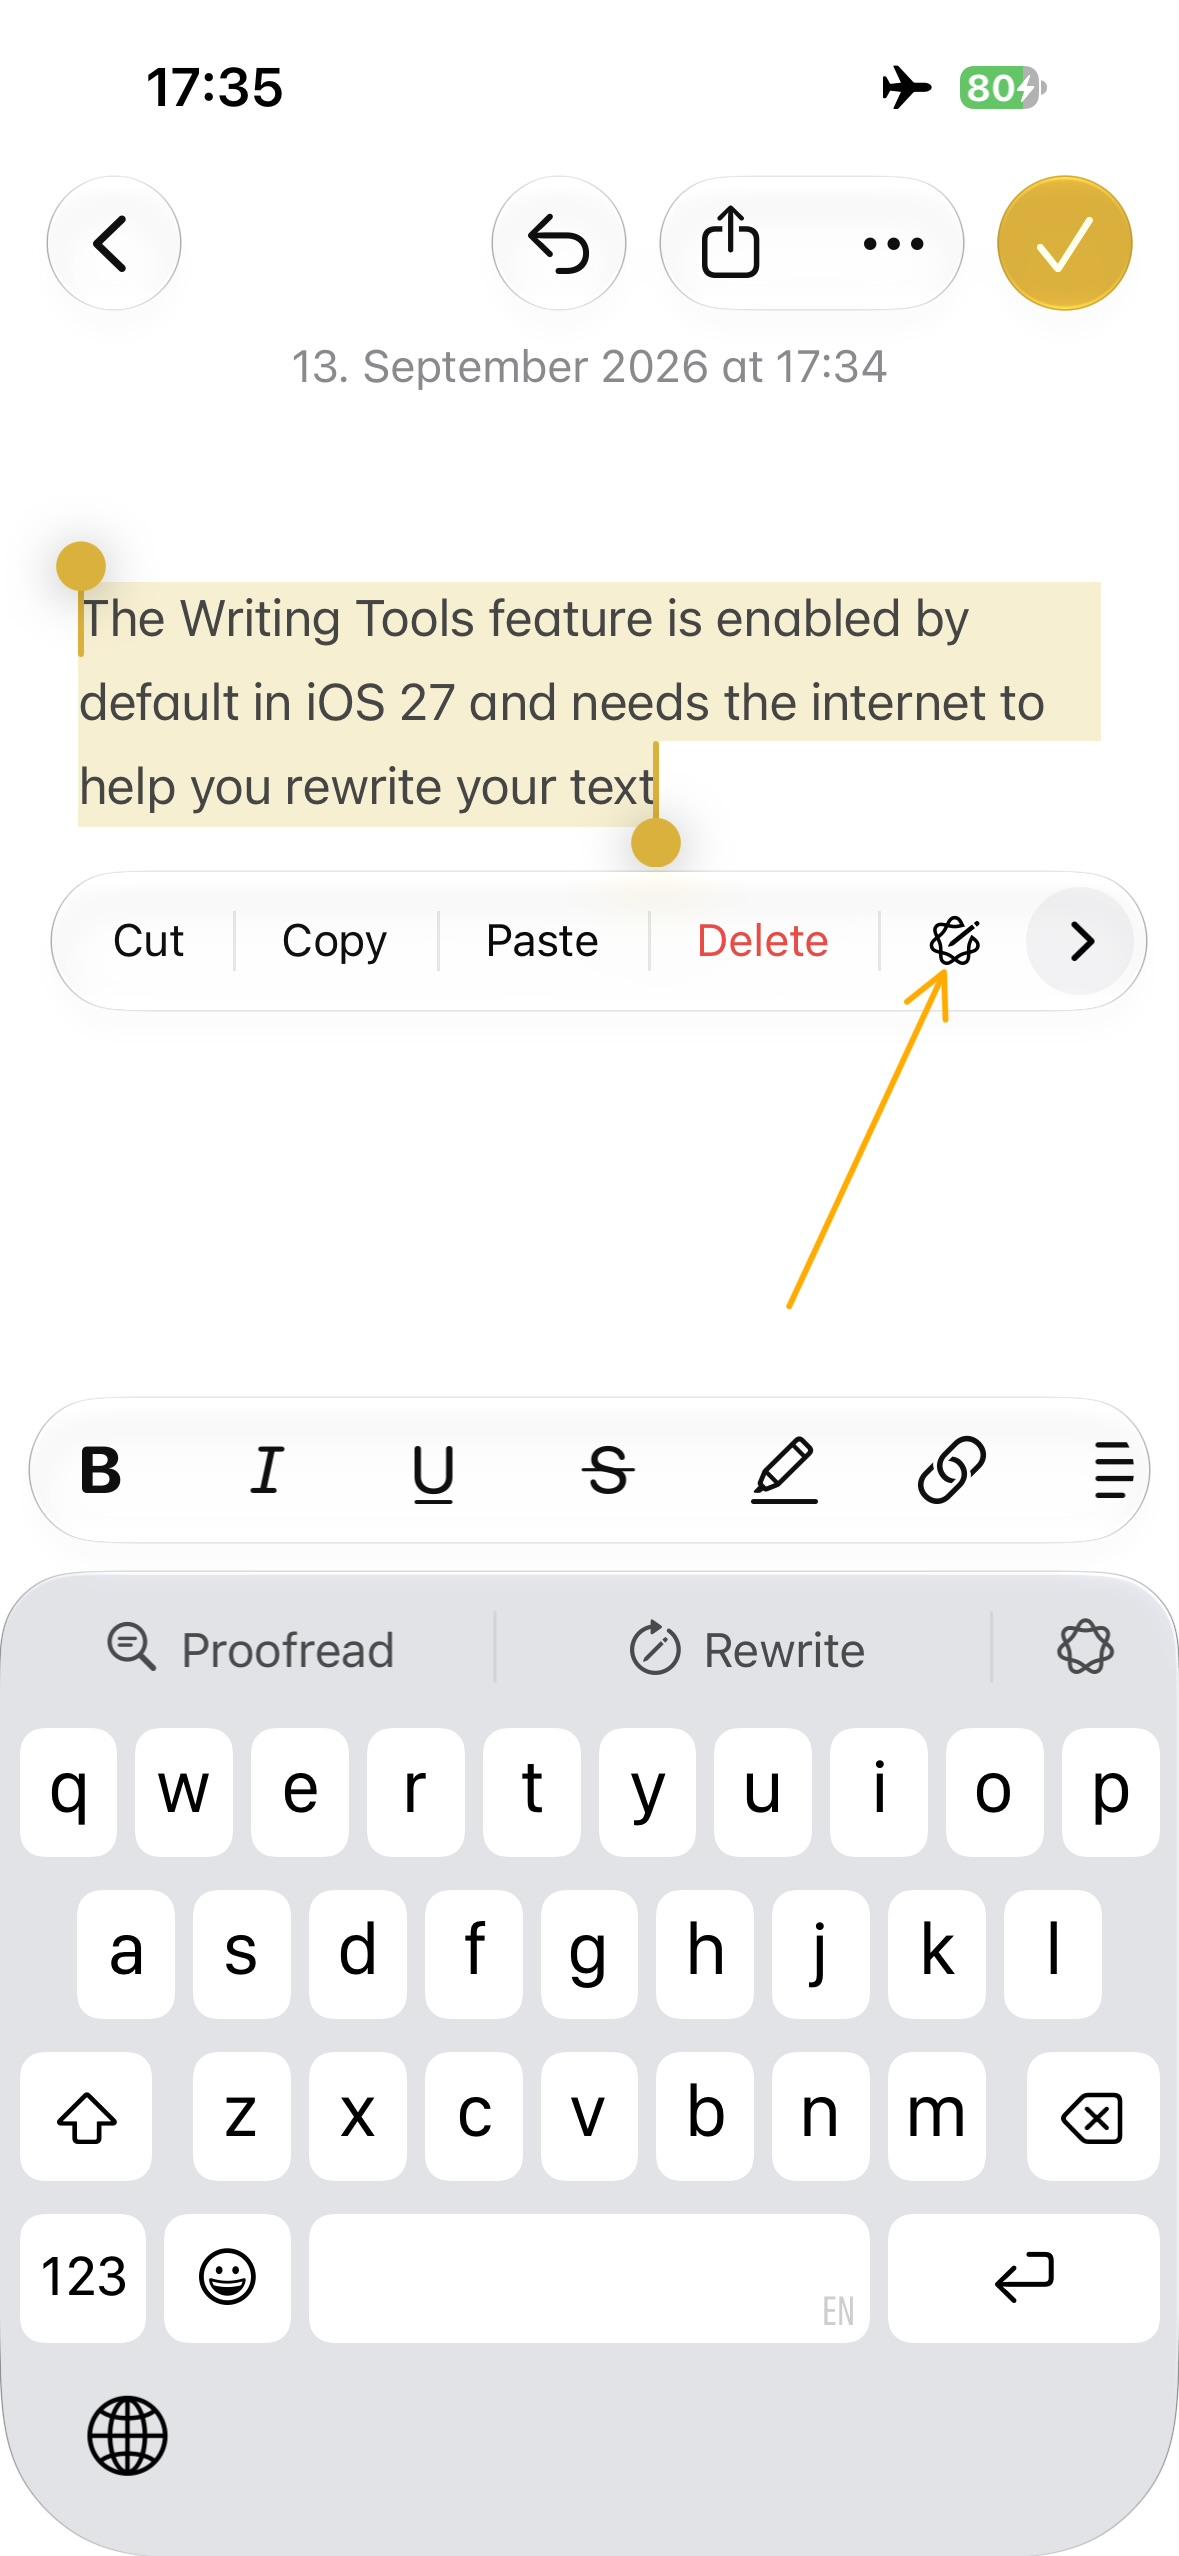
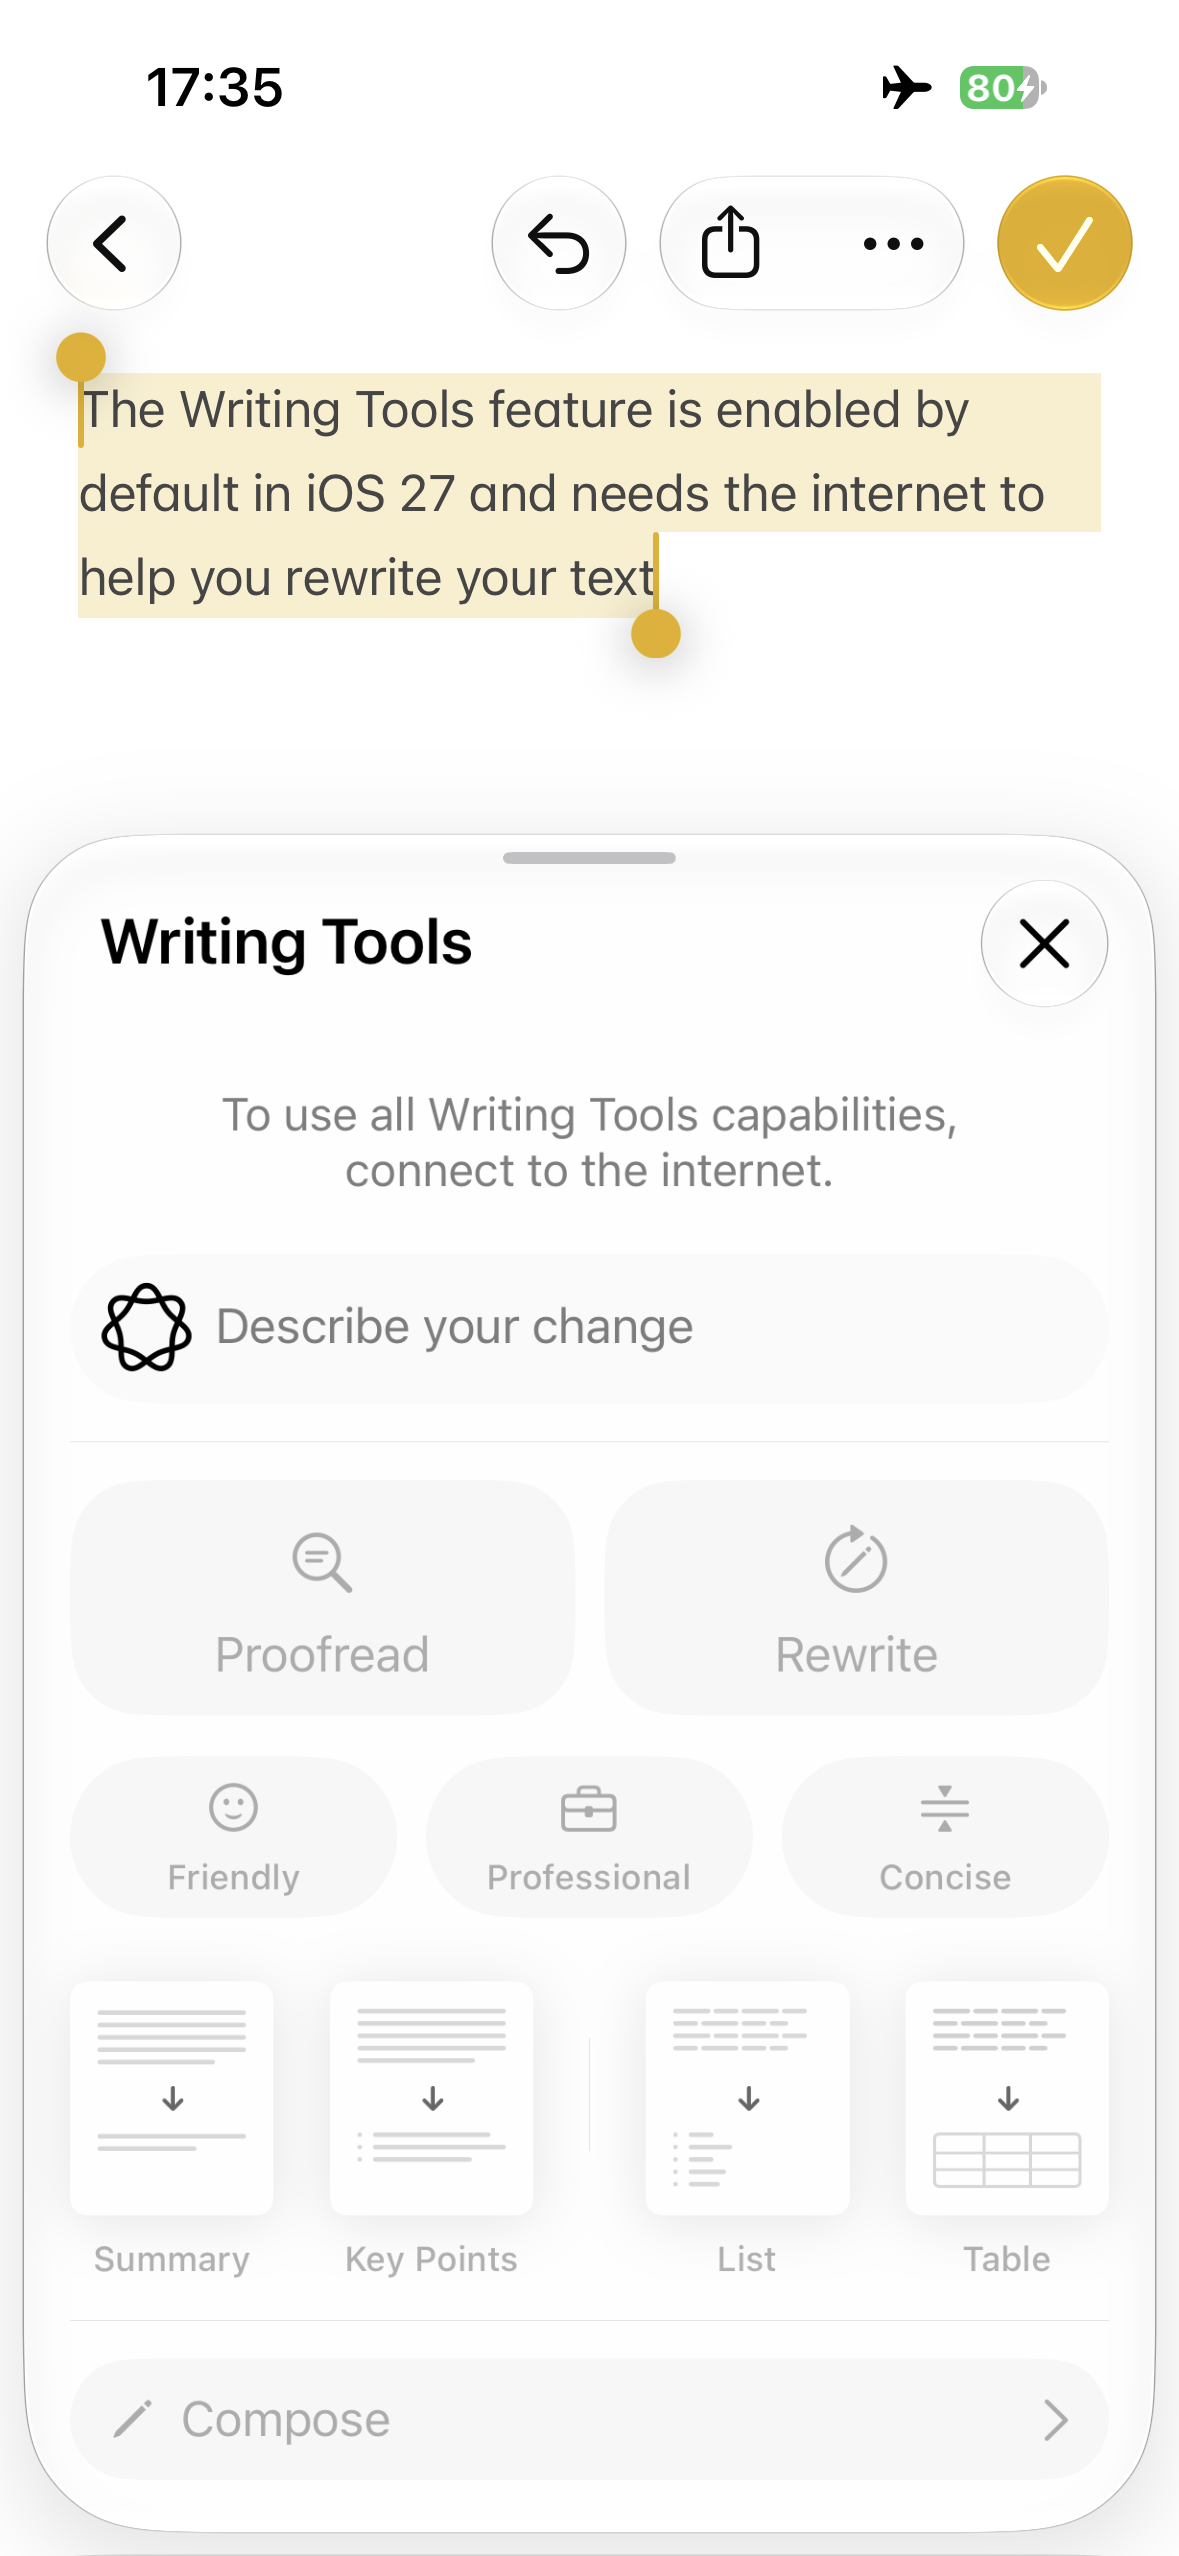
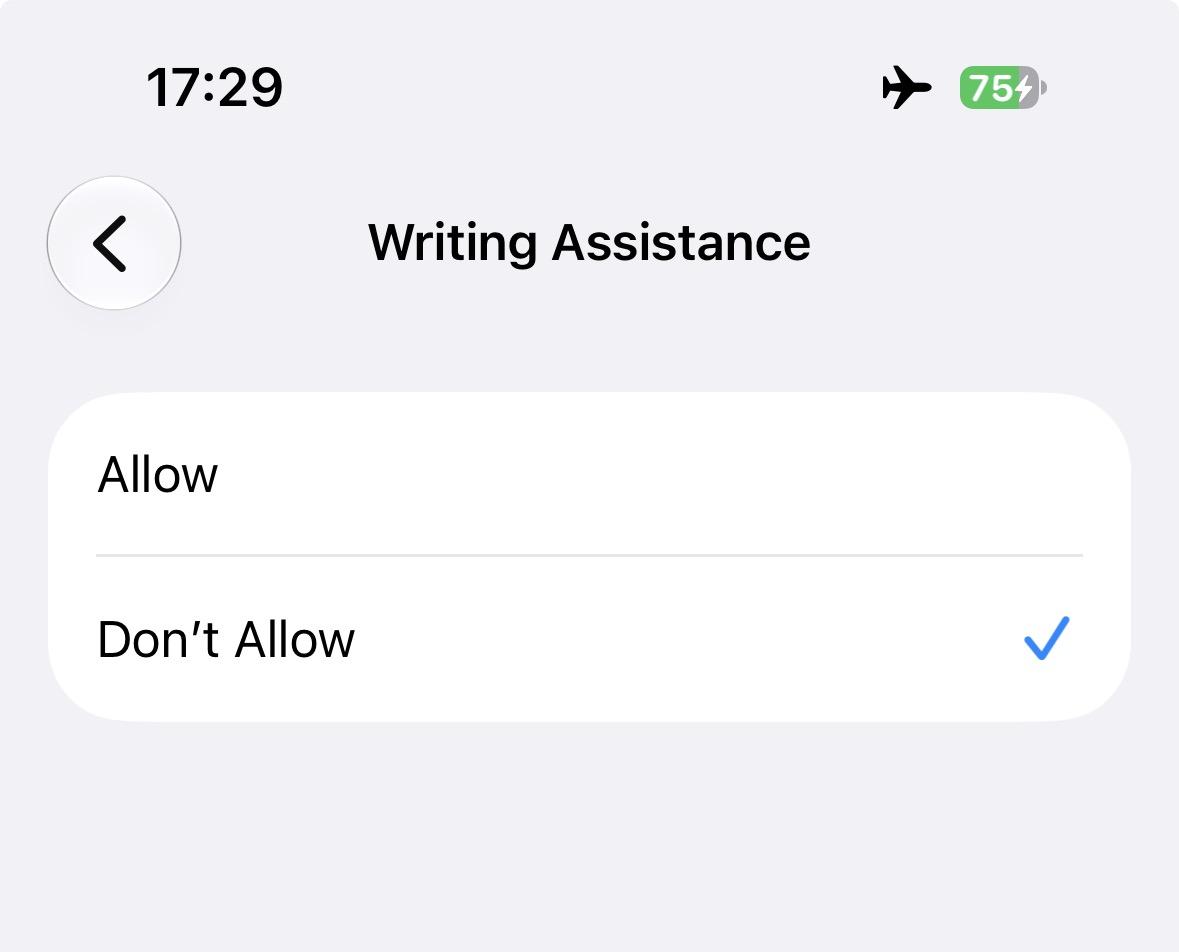
In iOS 27, there’s no longer simple toggle to disable Apple Intelligence entirely. Some features like Writing Tools can also send data off-device for processing through Private Cloud Compute

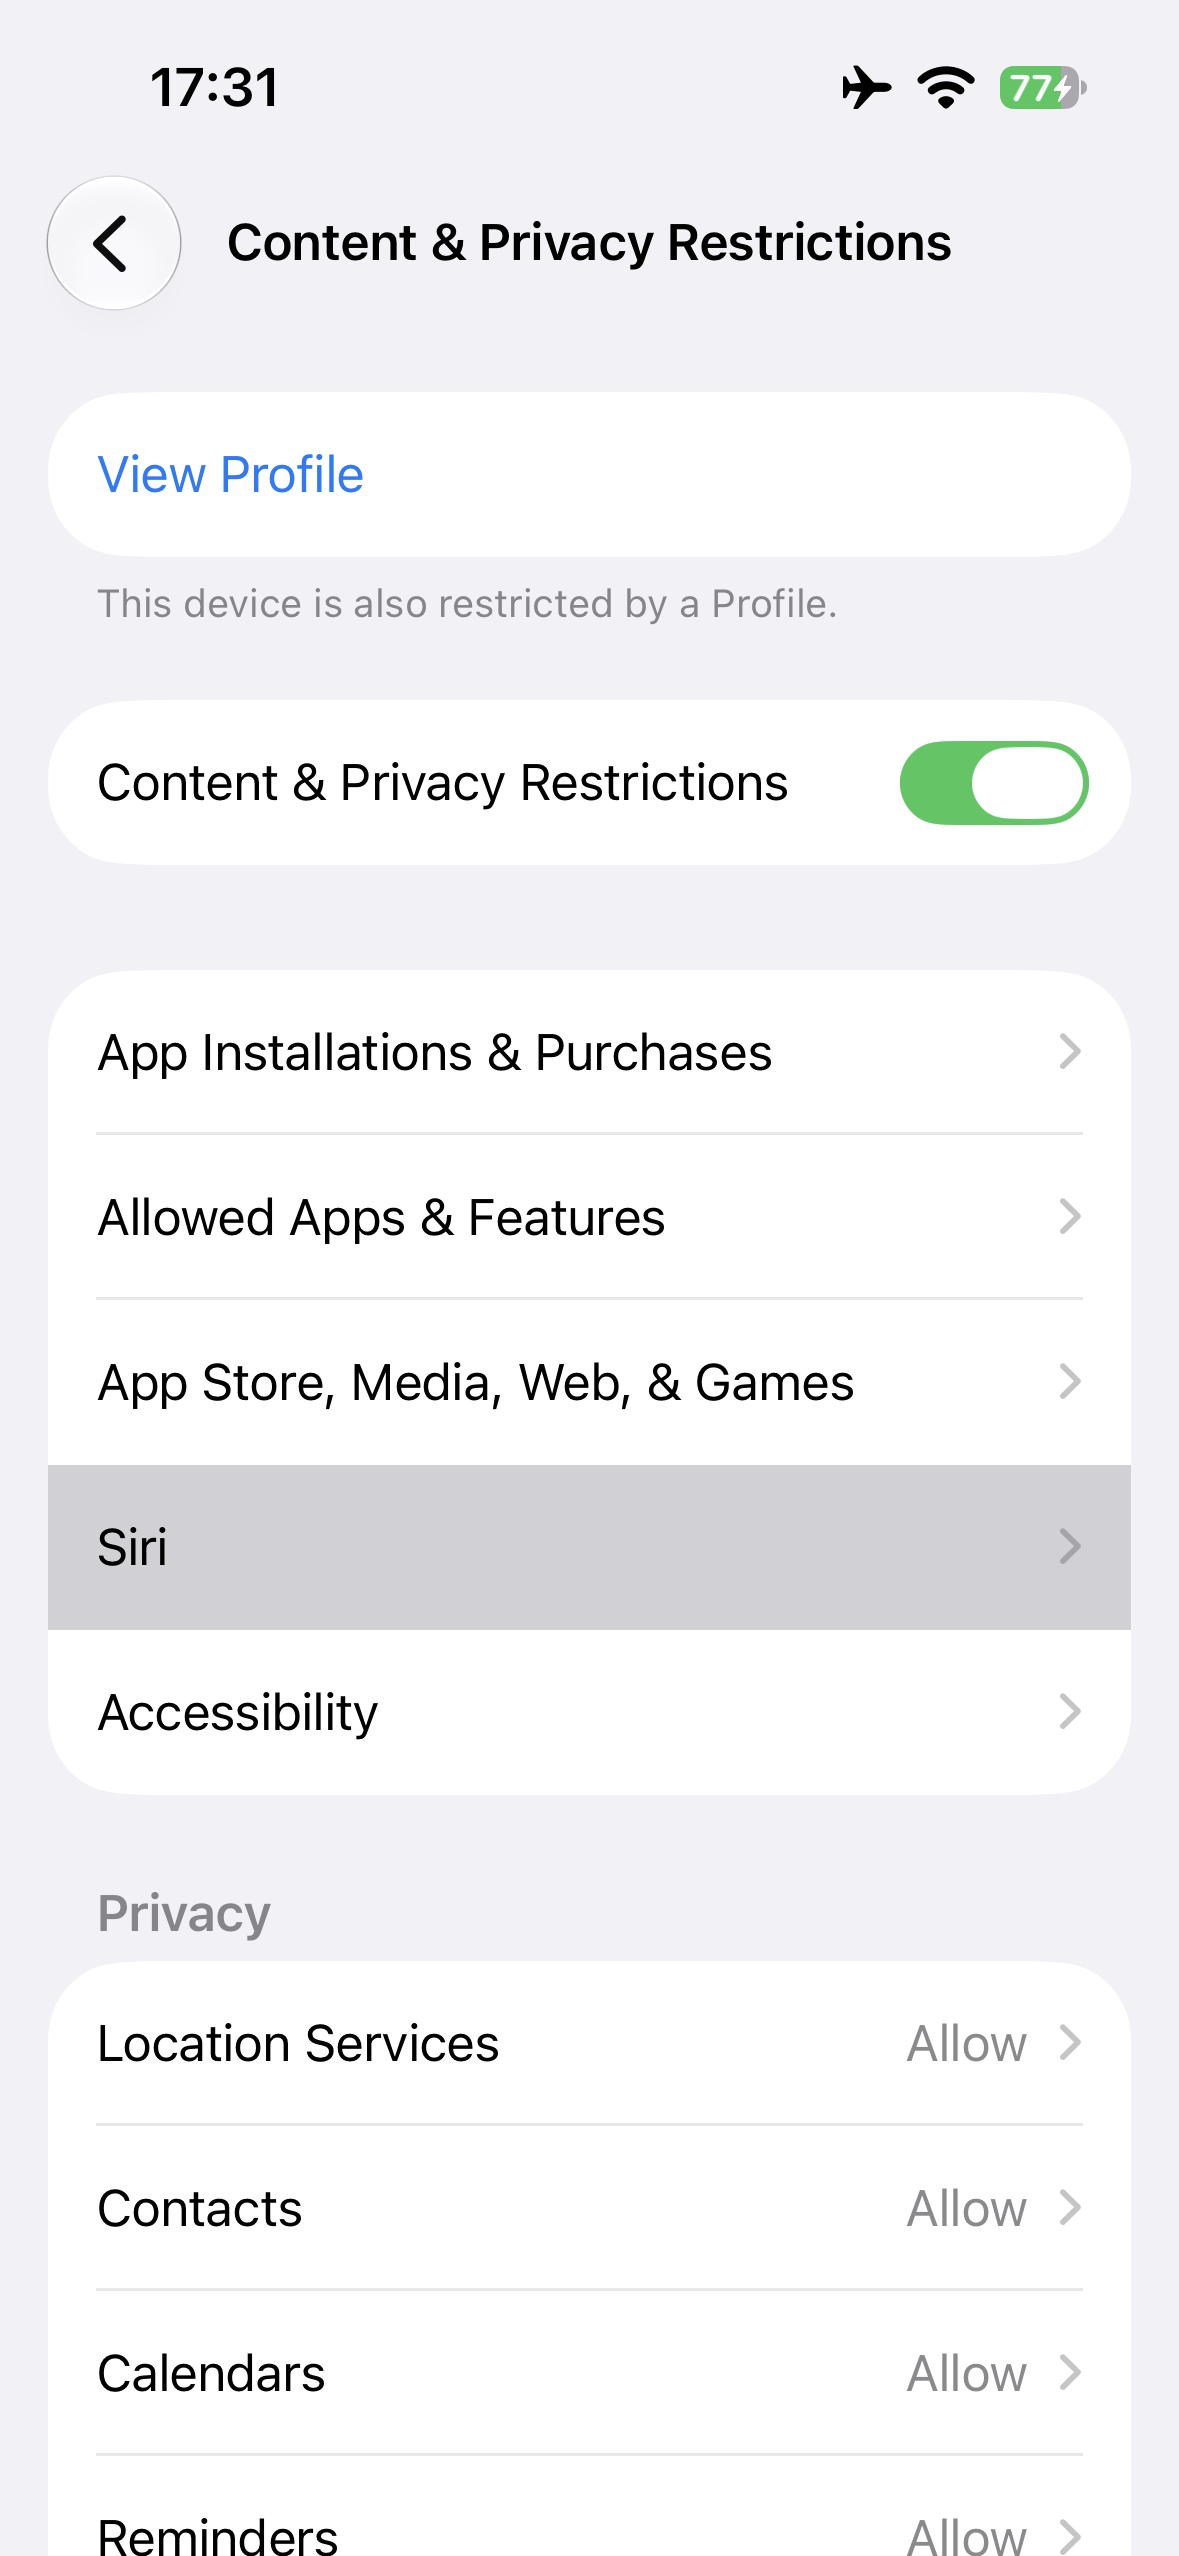
After some digging, here’s how to disable Writing Tools:

1️⃣ Settings → Screen Time
2️⃣ Content & Privacy Restrictions → turn it on
3️⃣ Siri → Writing Assistance → Don’t Allow

@bearsong@ravenation.club
@mysk@mastodon.social

In iOS 27, there’s no longer simple toggle to disable Apple Intelligence entirely. Some features like Writing Tools can also send data off-device for processing through Private Cloud Compute

After some digging, here’s how to disable Writing Tools:

1️⃣ Settings → Screen Time
2️⃣ Content & Privacy Restrictions → turn it on
3️⃣ Siri → Writing Assistance → Don’t Allow

@thenewoil@mastodon.thenewoil.org
@Voline@kolektiva.social

Right so, Facebook is all sad because people are calling their "AI" surveillance specs "Pervert Glasses" and it's killing them. It's also establishing the social norm that you don't go around with video recording glasses on your face, you'll be shunned.

So we need to start calling the Apple Watch the "Creep Watch" for humanity's sake.

infosec.exchange/@Em0nM4stodon

infosec.exchange

Em :official_verified: (@Em0nM4stodon@infosec.exchange)

Today @zackwhittaker@mastodon.social brings up a very important topic about the launch of the new Apple Watch this week: How a large company like Apple can play an important role in normalizing intrusive surveillance. "Apple is opening the door to a world where other companies, device makers, and app developers try to recreate or rival Apple's technology and do a far shoddier job, all the while creating a worse surveillance monster and introducing new security and privacy risks along the way." We don't talk enough about how privacy is also a culture, part of cultural norms that can go in one direction or another. Products like this, produced and sold at a massive scale, weakens our culture of consent and privacy, and pushes society towards the increasing normalization of always-on surveillance. I highly recommend reading Zack's article: https://this.weekinsecurity.com/watch-what-you-say-apple-opens-the-door-to-a-nightmare-world-of-always-listening-tech/ #Privacy #Security #Apple #MassSurveillance

@Em0nM4stodon@infosec.exchange

Imagine you're having a remote appointment with your doctor for a very personal health issue.

Your doctor is a tech enthusiast, and is proudly wearing the new Apple Watch with all the recording features enabled.

You don't see the "Audible and visible signals for Live Rewind", because you don't see your doctor's wrist on videochat or on speakerphone.

The "Omitted content" safeguard fails to detect the sensitive conversation, because none of the pre-selected keywords are detected.

"What about all the privacy laws protecting me?", you claim in distress.

Sadly, your doctor is unaware and thinks "surely Apple respects all the laws by default?"

The medical clinic isn't informed about privacy risks related to new technologies, and hasn't implemented any training or policies about it yet.

Your sensitive health data is collected by Apple's new features, stored on their servers, blissfully unaware of the infringements to your consent, your privacy, and all the laws supposed to protect you.

This is only one scenario of the many surveillance nightmares we might hear about in the coming months and years.

Brace yourself.

@thenewoil@mastodon.thenewoil.org
@Em0nM4stodon@infosec.exchange

Imagine you're having a remote appointment with your doctor for a very personal health issue.

Your doctor is a tech enthusiast, and is proudly wearing the new Apple Watch with all the recording features enabled.

You don't see the "Audible and visible signals for Live Rewind", because you don't see your doctor's wrist on videochat or on speakerphone.

The "Omitted content" safeguard fails to detect the sensitive conversation, because none of the pre-selected keywords are detected.

"What about all the privacy laws protecting me?", you claim in distress.

Sadly, your doctor is unaware and thinks "surely Apple respects all the laws by default?"

The medical clinic isn't informed about privacy risks related to new technologies, and hasn't implemented any training or policies about it yet.

Your sensitive health data is collected by Apple's new features, stored on their servers, blissfully unaware of the infringements to your consent, your privacy, and all the laws supposed to protect you.

This is only one scenario of the many surveillance nightmares we might hear about in the coming months and years.

Brace yourself.

@Em0nM4stodon@infosec.exchange

Today @zackwhittaker brings up a very important topic about the launch of the new Apple Watch this week:

How a large company like Apple can play an important role in normalizing intrusive surveillance.

"Apple is opening the door to a world where other companies, device makers, and app developers try to recreate or rival Apple's technology and do a far shoddier job, all the while creating a worse surveillance monster and introducing new security and privacy risks along the way."

We don't talk enough about how privacy is also a culture, part of cultural norms that can go in one direction or another.

Products like this, produced and sold at a massive scale, weakens our culture of consent and privacy, and pushes society towards the increasing normalization of always-on surveillance.

I highly recommend reading Zack's article: this.weekinsecurity.com/watch-

this.weekinsecurity.com

Watch what you say: Apple opens the door to a nightmare world of always-listening tech

Apple's new upcoming ambient audio recording features set a risky precedent in normalizing intrusive surveillance. Privacy experts weigh in.

@thenewoil@mastodon.thenewoil.org
@Xavier@infosec.exchange

This is some next level shit right here.

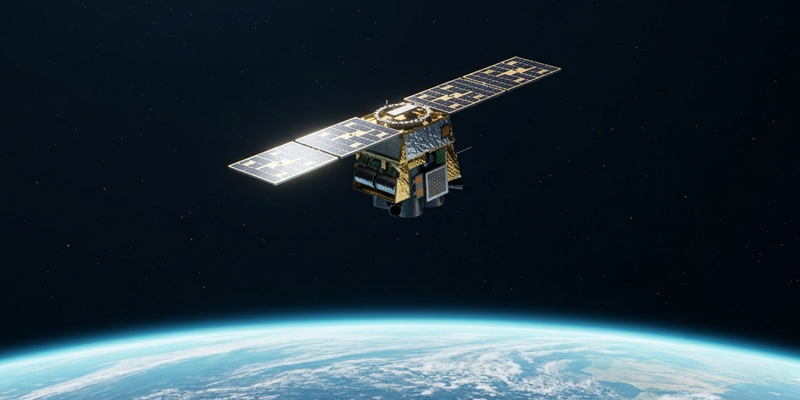
"Merlin combines daily global coverage with one-meter spatial resolution, a capability that Satellogic believes is not available in Earth observation systems today. This combination is expected to enable entirely new intelligence applications by allowing organizations to monitor activity continuously and cost-effectively on a planetary scale."

satellogic.com/news/press-rele

satellogic.com

Satellogic Introduces Merlin Constellation

Satellogic Introduces Merlin Constellation for Daily Global Monitoring at One-Meter Resolution

@thenewoil@mastodon.thenewoil.org
@scottwilson@infosec.exchange

announces new Apple Watch model in partnership with !

PRESS RELEASE SEPTEMBER 11, 2026. CUPERTINO, CALIFORNIA Apple today introduced Apple Watch Flock Edition (tm) — the ultimate surveillance and adventure watch — now including new, always-on video recording and AI-enhanced processing. Note: longer battery life may be affected by the requirement to have a 4K stream always connected to our primary data center in Hell.

Apple Watch Flock Edition (tm)
ALT text

Apple Watch Flock Edition (tm)

@GrapheneOS@grapheneos.social
@scottwilson@infosec.exchange

announces new Apple Watch model in partnership with !

PRESS RELEASE SEPTEMBER 11, 2026. CUPERTINO, CALIFORNIA Apple today introduced Apple Watch Flock Edition (tm) — the ultimate surveillance and adventure watch — now including new, always-on video recording and AI-enhanced processing. Note: longer battery life may be affected by the requirement to have a 4K stream always connected to our primary data center in Hell.

Apple Watch Flock Edition (tm)
ALT text

Apple Watch Flock Edition (tm)

@thenewoil@mastodon.thenewoil.org
@openrightsgroup@social.openrightsgroup.org

Cover your bits, the UK government wants to put scanning tech on your phone.

The aim? To prevent kids receiving and sending nudes. But it'll be there as default for everyone, unless you go through age verification to disable it.

It's a disproportionate move that'll compromise privacy and security.

Read our blog ⬇️

openrightsgroup.org/blog/nudit

openrightsgroup.org

Nudity scanning tech will leave us more exposed

The Government’s proposals to prevent under 18s from creating or sharing nude images aim to address serious issues such as sextortion, grooming, and abuse.

@thenewoil@mastodon.thenewoil.org
@frontenddogma@mas.to
@thenewoil@mastodon.thenewoil.org
@openrightsgroup@social.openrightsgroup.org · Reply to Open Rights Group

Nudity blocking works by scanning ALL your content.

The privacy implications are huge.

And the same goes for the alternative: having to submit your sensitive data in the form of ID uploads or biometric scans to verify you're over 18.

Meanwhile, the age verification industry remains unregulated.

@thenewoil@mastodon.thenewoil.org
@openrightsgroup@social.openrightsgroup.org · Reply to Open Rights Group

Don't believe the hype, we've just had a warning about supposedly ‘safe by design’ tech.

The HMD Fuse child-safety phone was taken off sale after serious security vulnerabilities were discovered.

This includes flaws which could expose a child’s live location and allow protections to be disabled.

ft.com/content/670b2b1d-7e4c-4

@openrightsgroup@social.openrightsgroup.org

Cover your bits, the UK government wants to put scanning tech on your phone.

The aim? To prevent kids receiving and sending nudes. But it'll be there as default for everyone, unless you go through age verification to disable it.

It's a disproportionate move that'll compromise privacy and security.

Read our blog ⬇️

openrightsgroup.org/blog/nudit

openrightsgroup.org

Nudity scanning tech will leave us more exposed

The Government’s proposals to prevent under 18s from creating or sharing nude images aim to address serious issues such as sextortion, grooming, and abuse.

@thenewoil@mastodon.thenewoil.org
@frontenddogma@mas.to
@bupu@lgbtqia.space

I have a hypothesis that Metro (Canadian grocery store company) is using those IoT sensors that Wal-Mart uses that track the location of phones throughout the store to track foot traffic because I've gone two times recently and stood in front of a product and thought about getting it but didn't then got an ad for it the next day.

I remember seeing on YouTube a user use an app or something to scan for devices connected to WiFi nearby to identify if a store is using these sensors but I can't find it now.

Does anyone know what you can use on your phone to check for them (and what are they usually identified as)?

@ai6yr@m.ai6yr.org

IMPORTANT PASSWORD SECURITY/PRIVACY ISSUE
----

For everyone:

If you are using the same password for Mastodon that you use anywhere else, CHANGE YOUR PASSWORD NOW.

A hacker is stealing accounts on Mastodon using something called “credential stuffing.” This means they use email/password combinations stolen from other sites.

This is a common hacking technique. But right now someone is targeting Mastodon accounts.

This is not a security flaw with Mastodon. Someone is just using it across Mastodon.

You can check if your email is in a data breach elsewhere:

haveibeenpwned.com

Create a new strong password:

1. 12+ characters
2. Capital/lowercase letters
3. At least one special character

For admins:

The hacker is using the same unique user agent.

Go-http-client/1.1

We’re seeing a pattern of IPs, but they’re from varying ISPs. They’re also not changing the account emails.

haveibeenpwned.com

Have I Been Pwned: Check if your email address has been exposed in a data breach

Search tens of billions of breached records, monitor corporate domains via API, and get alerted when credentials are exposed. Trusted by security teams, MSSPs, and government agencies worldwide.

@thenewoil@mastodon.thenewoil.org
@ai6yr@m.ai6yr.org
@harald@hub.volse.no
The inclusion of Autistici/Inventati on the US Specially Designated Global Terrorist list is a kick in the guts for all of us hosting services for others, whether it's fediverse instances, blogs, mailing lists or anything else. While most of us will hopefully never be on the receiving end of such a designation, the US regime has demonstrated how easily they can ruin our lives by throwing a politically motivated terror designation our way.

You may think that you're safe. You're not doing anything illegal after all. Just providing some infrastructure, a services or a place for people to come together and communicate. Privately. In confidence. Anonymously.

That was also what Autistici/Inventati was doing.

We're all targets now. And if we don't stand up against it, we let the fascists win!

In Autistici/Inventati's own words:
Let us have a thousand servers, a thousand networks. Let us flood them with possibilities until they run out of time and money to pursue and persecute us.


#antifa #activism #digitalsovereignity #privacy

hub.volse.no

Volse Hubzilla

@thenewoil@mastodon.thenewoil.org
@generalx@freeradical.zone

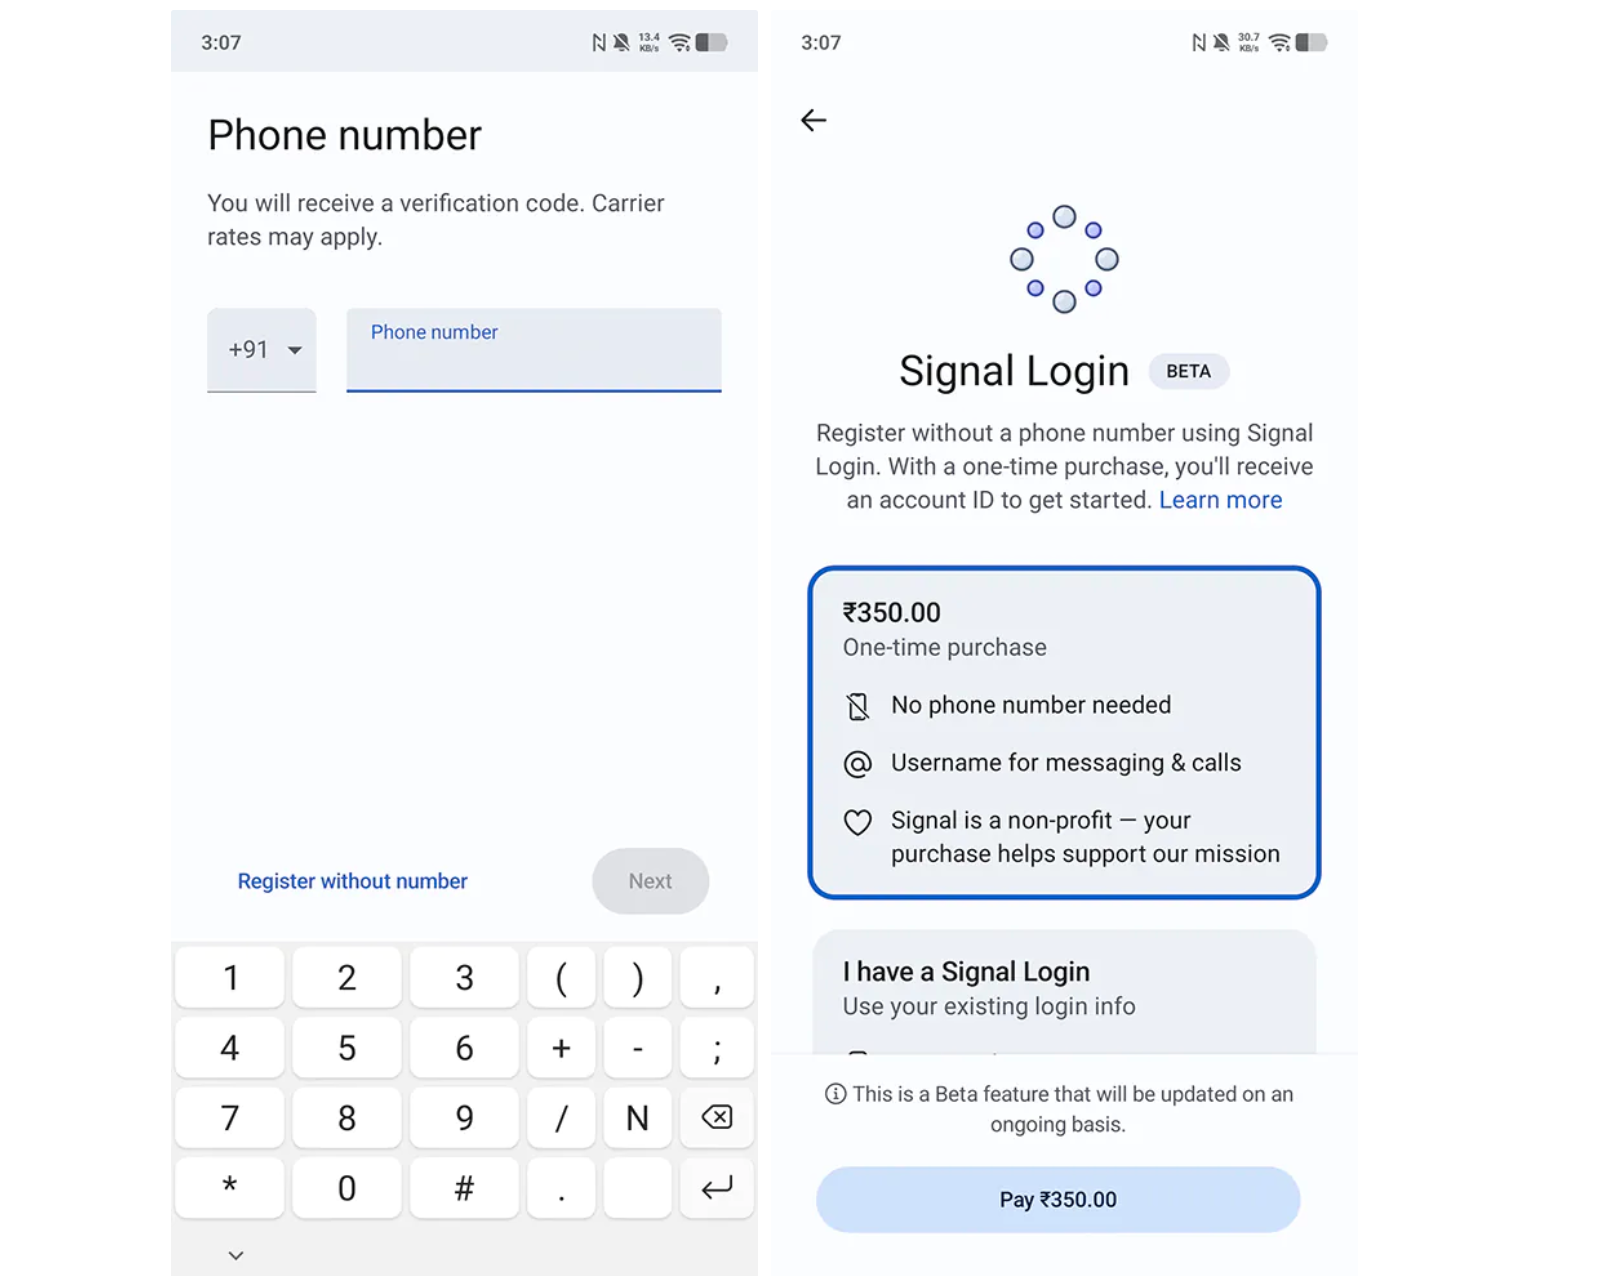
Signal app is removing the phone number requirement...if you pay a one-time fee.

Will you pay?

  • Yes, only if I can pay anonymously2 (50%)
  • Yes, I'm okay paying with Paypal/Stripe0 (0%)
  • No, I'd rather give a phone number2 (50%)
  • I still don't like Signal0 (0%)
@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer
@thenewoil@mastodon.thenewoil.org
@helloyanis@furries.club

🇪🇺 European Citizen's Initiative against ID age verification online

Just yesterday, Stop Killing the Internet, from the people at @StopKillingGames, launched an ECI against ID age verification! This is great but it needs 1 million signatures !

So, if you are a citizen of , please sign it! If you don't, or even if you do, still share it around so more people know about it and can sign it!

eci.ec.europa.eu/066/public/#/

Reaching the signature threshold will not mean that ID age verification will immediately become illegal, but the subject will be brought to the @EUCommission and they'll have to do SOMETHING about it. This is already a huge step in the right direction!

:boost_requested: Please boost and share this post to spread the word! Thank you!

@privacy

eci.ec.europa.eu

European Citizens' Initiative

Give your support !

@helloyanis@furries.club · Reply to 🦊 helloyanis :veripawed3:
@helloyanis@furries.club

🇪🇺 European Citizen's Initiative against ID age verification online

Just yesterday, Stop Killing the Internet, from the people at @StopKillingGames, launched an ECI against ID age verification! This is great but it needs 1 million signatures !

So, if you are a citizen of , please sign it! If you don't, or even if you do, still share it around so more people know about it and can sign it!

eci.ec.europa.eu/066/public/#/

Reaching the signature threshold will not mean that ID age verification will immediately become illegal, but the subject will be brought to the @EUCommission and they'll have to do SOMETHING about it. This is already a huge step in the right direction!

:boost_requested: Please boost and share this post to spread the word! Thank you!

@privacy

eci.ec.europa.eu

European Citizens' Initiative

Give your support !

@thenewoil@mastodon.thenewoil.org
@blog@marius.blog

Firefox’s AI Switch Is Off. Telemetry Isn’t.

My Wireshark test of Firefox 148 showed that its AI kill switch disables generative features, but leaves telemetry and advertising untouched. Six months later, Mozilla’s CEO has called the switch perhaps the most important AI feature of all. I retested it in Firefox 155.

Read the full article: https://marius.blog/firefox-155-ai-kill-switch-retest/

I spoke with @tante@tldr.nettime.org for this article.

Written by Marius Quabeck. Replies: @marius@social.nerdzoom.media

Firefox 155 welcome screen saying You're in safe paws
ALT text

Firefox 155 welcome screen saying You're in safe paws

@djwfyi@fosstodon.org · Reply to Daryl

USians should lock/freeze your credit reports with all three major credit bureaus. It's not that complicated and can be done on their websites.

You then just put in a temporary thaw on each one when you do need to apply for credit. Took me 5 minutes total last time I needed to let lenders in.

TransUnion
Equifax
Experian

Those are the three bureaus.

Also, visit annualcreditreport.com at least annually to get your free credit reports and make sure they are right.

annualcreditreport.com

Annual Credit Report

@marius@social.nerdzoom.media

Mozilla released Firefox 155 yesterday, so I took another look at its AI kill switch. The switch has grown since Firefox 148, but telemetry and advertising remain active. I retested it with Wireshark, and Mozilla’s internal reaction to my previous findings became part of the story too.

marius.blog

Firefox’s AI Switch Is Off. Telemetry Isn’t.

My Wireshark test of Firefox 148 showed that its AI kill switch disables generative features, but leaves telemetry and advertising untouched. Six months…

@blog@marius.blog

Firefox’s AI Switch Is Off. Telemetry Isn’t.

My Wireshark test of Firefox 148 showed that its AI kill switch disables generative features, but leaves telemetry and advertising untouched. Six months later, Mozilla’s CEO has called the switch perhaps the most important AI feature of all. I retested it in Firefox 155.

Read the full article: https://marius.blog/firefox-155-ai-kill-switch-retest/

I spoke with @tante@tldr.nettime.org for this article.

Written by Marius Quabeck. Replies: @marius@social.nerdzoom.media

Firefox 155 welcome screen saying You're in safe paws
ALT text

Firefox 155 welcome screen saying You're in safe paws

@briankrebs@infosec.exchange

Breaking, exclusive and spicy, from me:

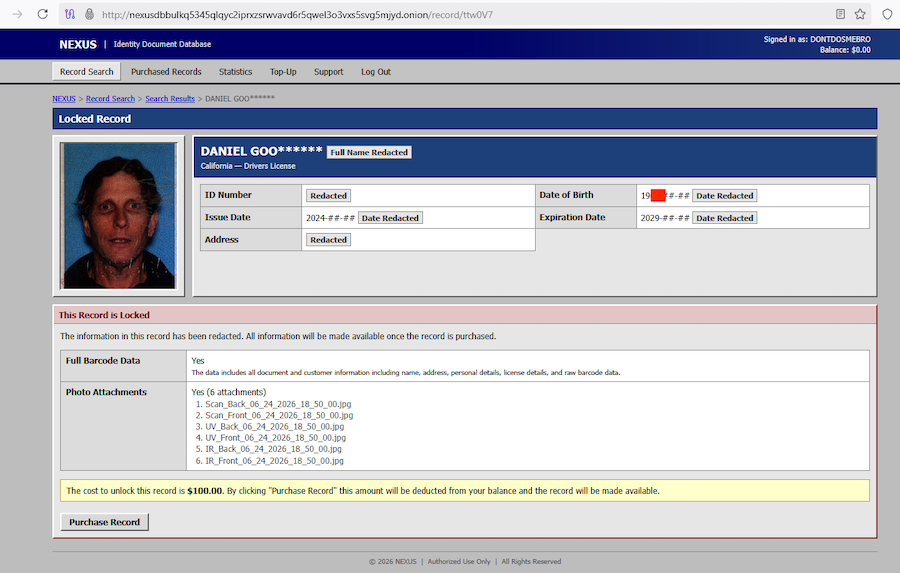
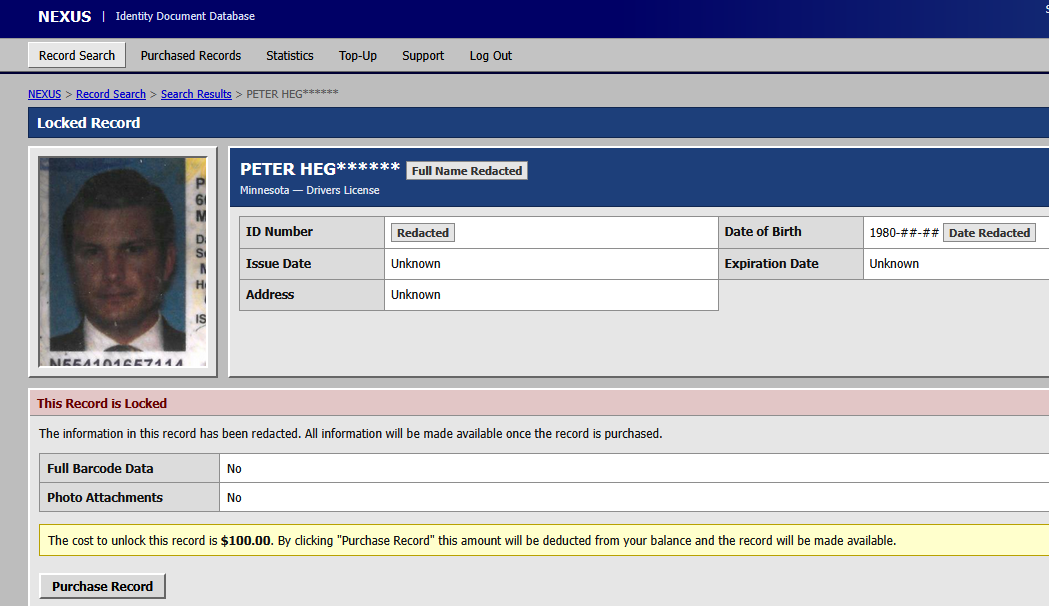
A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company based in Louisiana. KrebsOnSecurity also has learned that the New Orleans field office of the Federal Bureau of Investigation (FBI) today launched an official inquiry into the source of the images.

krebsonsecurity.com/2026/09/fb

A record available at this identity theft service that includes the drivers license for U.S. Defense Secretary Pete Hegseth, who is one of several high-ranking U.S. government officials whose drivers licenses can be found for sale. The record shows a picture of Hegseth wearing a suit and tie.
ALT text

A record available at this identity theft service that includes the drivers license for U.S. Defense Secretary Pete Hegseth, who is one of several high-ranking U.S. government officials whose drivers licenses can be found for sale. The record shows a picture of Hegseth wearing a suit and tie.

@thenewoil@mastodon.thenewoil.org
@gtbarry@mastodon.social

Police Use Surveillance Cameras to Narc On Guy Who Found $30 on the Ground

Earlier this month, the Albany Police Department in Georgia made a post on Facebook asking the public to help identify a man guilty of a despicable crime: picking up $30 off the floor that he found in a Walmart.

futurism.com/future-society/po

futurism.com

Police Use Surveillance Cameras to Narc On Guy Who Found $30 on the Ground

Police in Albany used an image taken surveillance footage to try find a man who picked up money off the ground in a Walmart.

@thenewoil@mastodon.thenewoil.org
@Goffi@mastodon.social
@pedersen@c.im

It's been a long time since I've needed to wipe a drive, and the tool I used to use (Darik's Boot and Nuke) hasn't been updated since 2015 (I did say it's been a while, right? :) ). ShredOS picks up where it left off: it's built around nwipe, which is itself a DBAN fork. So, if you want to wipe your drives before trashing or reselling, do check it out. It's at shredos.org/

Warning: SSDs do a lot under the hood to make themselves last longer, and the side effect is that tools like this won't actually do the erasure you might be expecting. Fortunately, ShredOS includes tools that are specifically for this, including hdparm and nvme-cli. Their site talks about how to use those tools to actually erase those disks, too.

shredos.org

ShredOS – Free Secure Disk Wiping & Data Erasure Tool

Download ShredOS ISO for free and permanently erase hard drives, SSDs, and USB devices. Secure bootable disk wiping software for complete data destruction.

@privacynews@mstdn.plus
@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer

🚨 This Week In Privacy #68 will be live in 30 minutes, we'll be talking about how Nitter was just sent a cease and desist from X (Twitter) raising concerns over other frontends suffering the same fate. We'll also be covering the latest privacy & security news!

👋 Come and watch and join the Q&A!

streamyard.com/watch/AJiE86Hcz

streamyard.com

Could This Be The End of Privacy Frontends?

X.com has sent a cease and desist letter to Nitter, the privacy focused frontend for Twitter, demanding immediate takedown of the service and its repositories. This move brings into question whether other privacy frontends could also suffer the same fate, we'll discuss this and more on This Week In Privacy #68!

@thenewoil@mastodon.thenewoil.org

country boy vs and defilement

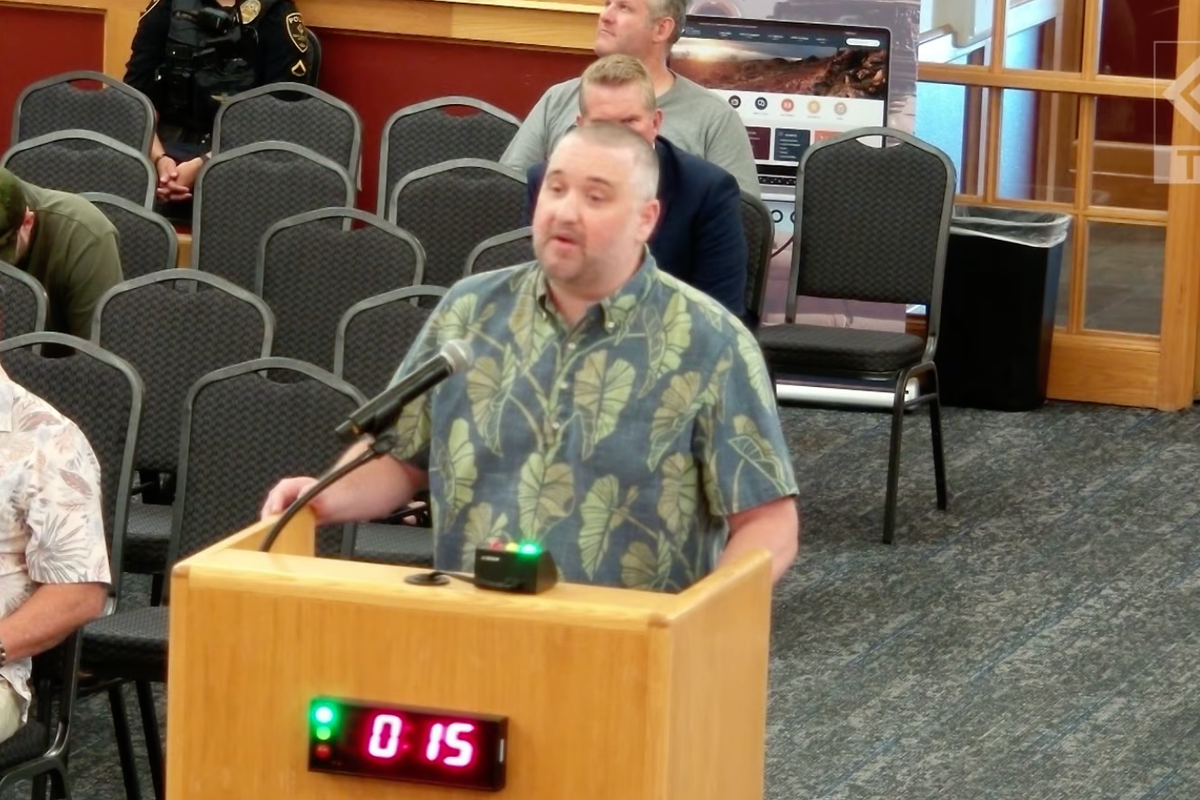
Jacob Rockwell at a , meeting

👏 👏 👏

weartv.com/news/local/man-rais

(Jacob's actually from Escambia County, which is the far Western tip of Florida, so basically Alabama)

A man at a podium reads a speech from his smartphone
ALT text

A man at a podium reads a speech from his smartphone

@thenewoil@mastodon.thenewoil.org
@gtronix@infosec.exchange
@thenewoil@mastodon.thenewoil.org
@mf_newsdigest@mastodon.mediafaro.org
@davemosk@mastodon.nz

I’m Leaving WhatsApp
I’m leaving WhatsApp. It’s an integral part of the Meta / Facebook empire, which is currently being sued by 29 states for the harm that it causes to children. While WhatsApp claims end-to-end encryption, they retain your metadata, which forms part of your social graph which they then use as part of their marketing efforts….
dave.moskovitz.co.nz/2026/08/2

dave.moskovitz.co.nz

I’m Leaving WhatsApp | Dave Moskovitz

I'm leaving WhatsApp. It's an integral part of the Meta / Facebook empire, which is currently being sued by 29 states for the harm that it causes to children. While WhatsApp claims end-to-end encryption, they retain your metadata, which forms part of your social graph which they then use as part of their marketing efforts.

@phlogiston@mastodon.nz · Reply to Dave Moskovitz (((❤️)))

@davemosk
I *had* never used it ... until I (sort of) *had to* use it.

I'd been a very happy Signal user. But then joining a community (I strongly support) that entirely communicates (almost exclusively) via WhatsApp (and some public facing stuff via Facebook) had meant the end of it.

Gladly on my GrapheneOS phone I was able to use a throw-away SIM (foreign, from a recent EU trip) to register a WhatsApp account in an entirely isolated user profile.

It is painful to have to use WhatsApp (for that one thing) now. But it is also painful – depending on one's community – to *not* use it.

The big question is this: How can one (peacefully) motivate such a community to 'get off' of WhatsApp/Facebook without alienation and offending them? Certainly educated arguments don't work. :-(

Any strategies?

@davemosk@mastodon.nz

I’m Leaving WhatsApp
I’m leaving WhatsApp. It’s an integral part of the Meta / Facebook empire, which is currently being sued by 29 states for the harm that it causes to children. While WhatsApp claims end-to-end encryption, they retain your metadata, which forms part of your social graph which they then use as part of their marketing efforts….
dave.moskovitz.co.nz/2026/08/2

dave.moskovitz.co.nz

I’m Leaving WhatsApp | Dave Moskovitz

I'm leaving WhatsApp. It's an integral part of the Meta / Facebook empire, which is currently being sued by 29 states for the harm that it causes to children. While WhatsApp claims end-to-end encryption, they retain your metadata, which forms part of your social graph which they then use as part of their marketing efforts.

@thenewoil@mastodon.thenewoil.org
@agent0x0@infosec.exchange

Digital legacy planning does not have to start with a huge account inventory.

In episode 447 of the Shared Security Podcast, Scott Wright recommends one practical first step: set up legacy or emergency contacts on your most critical accounts so trusted access is possible if you die or become incapacitated.

Full episode: sharedsecurity.net/2026/08/24/

Watch on YouTube: youtu.be/4MRJOvlrsyc

Shared Security Podcast short: Set up legacy and emergency contacts now.
ALT text

Shared Security Podcast short: Set up legacy and emergency contacts now.

@thenewoil@mastodon.thenewoil.org
@PrivacyDigest@mas.to
@thenewoil@mastodon.thenewoil.org
@xabd@mastodon.social

3 GOATed apps that mankind gave us for free. 🗿

VLC, Brave, and Linux three legendary open-source tools that have saved us from countless headaches.

What would you add to the list?

Meme showing three figurines representing VLC, Brave, and Linux: an orange-and-white traffic cone, an orange lion-head shield, and the Linux penguin. Text at the top reads, “3 of the GOATed applications that mankind have produced for free.”
ALT text

Meme showing three figurines representing VLC, Brave, and Linux: an orange-and-white traffic cone, an orange lion-head shield, and the Linux penguin. Text at the top reads, “3 of the GOATed applications that mankind have produced for free.”

@privacyguides@neat.computer

🚨 This Week In Privacy #67 will be live in 30 minutes, we'll be talking about how Microsoft’s Copilot had a one-click vulnerability that let attackers quietly exfiltrate data, no user interaction required beyond a single click!

👋 Come and watch and join the Q&A!

streamyard.com/watch/yQnbWTcgw

streamyard.com

Microsoft Copilot Continues To Be A Nightmare.

Microsoft’s Copilot had a one-click vulnerability that let attackers quietly exfiltrate data, no user interaction required beyond a single click. Microsoft's AI push seems to be backfiring as security incidents continue to increase. Join us for This Week In Privacy #67!

@thenewoil@mastodon.thenewoil.org
@ggus@mastodon.social

⚠️ PSA - Hello, Tor relay operator.

If you're running an old Tor relay or bridge on the 0.4.8.x series, please upgrade to 0.4.9.x as soon as possible.

Starting in September, the 0.4.8.x series will be dropped from the Tor network. Relays and bridges still on it will stop working.

Announcement: blog.torproject.org/sunsetting

Check whether your relay is affected:
metrics.torproject.org/rs.html

metrics.torproject.org

Relay Search

@thenewoil@mastodon.thenewoil.org
@ggus@mastodon.social
@dallo@pouet.chapril.org
@jbz@indieweb.social

「 Orion is a privacy-focused browser made by Kagi, the company that also created the paid Kagi Search engine. Instead of using Chromium like most browsers, Orion is built on WebKit, the engine behind Apple’s Safari 」

linuxiac.com/orion-browser-for

linuxiac.com

Orion Browser for Linux Officially Enters Beta

Orion Browser has officially moved its Linux version into beta, with Flatpak builds now available for both x86_64 and ARM64 systems.

@thenewoil@mastodon.thenewoil.org

KOMO has a poll about how concerned people are that surveillance camera footage can be accessed by ICE, CBP, DHS, etc and used to target immigrants, LGBTQIA2S+ people, protesters, and other vulnerable communities.

I'm highly concerned ... if you are too, let 'em know!

komonews.com/news/local/shooto

komonews.com

Shootout outside Pioneer Square bar prompts questions on offline surveillance cameras

Gunfire erupted in Seattle’s Pioneer Square neighborhood early Sunday after a fight outside a bar spilled into the street near 1st Ave. and King Street, leaving

@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer

🚨 This Week In Privacy #66 will be live in 30 minutes, we'll be talking about the new security upgrades on the Pixel 11 and whether it will support custom operating systems like GrapheneOS.

👋 Come and watch and join the Q&A!

streamyard.com/watch/RV9UV2Zj2

streamyard.com

The Pixel 11 is Here, Will it Support GrapheneOS?

Google has announced it's new chip the Tensor G6 which brings serious security upgrades to the new Pixel 11 devices, is it a good idea to pre-order or should you hold off? Join us for This Week In Privacy #66

@thenewoil@mastodon.thenewoil.org
@mtec@mastodon.social

Join our Flock 101 information session at the Westchester Regional Library!

We will be hosting an event and Q&A all about Flock Safety, automated license plate readers, and the mass surveillance threat they pose.

Date: Tuesday, August 18
Time: 6:30 PM

miamitech.club/join-us-for-our

miamitech.club

Join us for our in-person Flock 101 presentation! - Aug 18

We'll talk about Flock Safety, automated license plate readers, and mass surveillance in Miami.

@thenewoil@mastodon.thenewoil.org
@keith@bookstodon.com · Reply to keith

FYI: They've replaced the "almost nobody opts in" quip located on: tiago.zip/almanac

original text: "because almost nobody opts in, and a snapshot of the few hundred people who did isn't useful for anything."

with: "if you don't know about it you can't opt in, and a snapshot of the few hundred people who did isn't useful for anything."

That being said, we don't condone any sort of mass data collection especially without consent.
This is a nightmare.

@thenewoil@mastodon.thenewoil.org

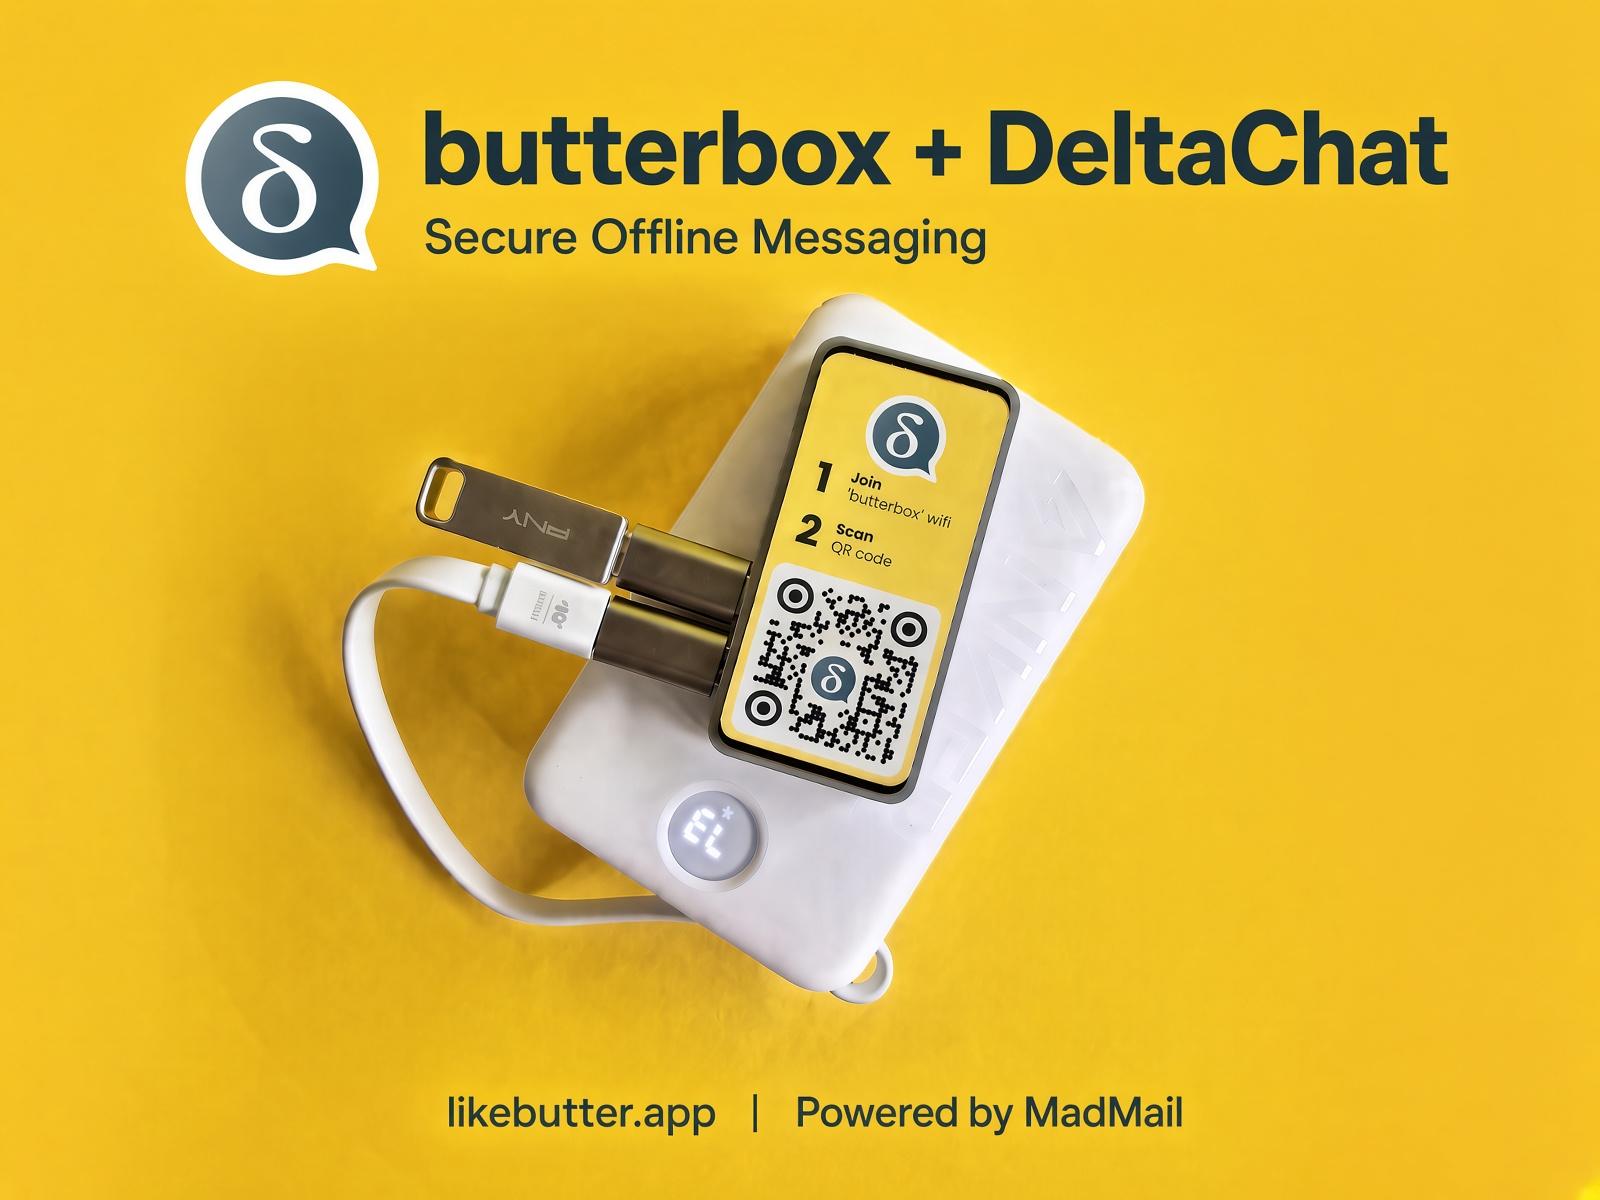
A really interesting and practical project from the Project called is worth knowing about.

ButterBox is a portable, fully offline device (usually running on a Raspberry Pi). When you turn it on, it creates its own local Wi-Fi network. Anyone nearby can connect and access a set of tools without any internet connection:

• An offline app store (based on F-Droid)
• File, video, book and educational content sharing
• And most importantly — secure encrypted chat

What makes this project especially powerful is its deep integration with The ButterBox team uses the MadMail server to run a local Chatmail Relay inside the box.

Users can create an offline account with just a single QR scan or one tap and immediately start using fully end-to-end encrypted messaging. Even when there’s no internet at all, messages, groups and files can be exchanged securely between people.

This is where DeltaChat really shines: decentralized, no central servers, real encryption, and designed for difficult conditions.
Combined with ButterBox, it becomes a genuine tool for secure communication during internet shutdowns, in remote areas, or in crisis situations.

It’s a pity that this project still isn’t widely known or deployed in Iran. The good news is that it’s completely open source and can be set up with a regular Raspberry Pi and an SD card. Pre-built images are also available, which makes the process even easier.

For anyone interested in privacy, offline communication, and tools that keep working when the internet goes down, ButterBox is one of the most valuable projects around right now.
Official site:
likebutter.app

@privacyguides@neat.computer · Reply to Privacy Guides

🛡️ Want to dive deeper?

We broke everything down in an easy to digest video, that goes into more detail about the topics in this Mastodon thread.

Check it out and share it around! ⬇️

youtu.be/ZDZlmDtlnvo

6/6 🧵

youtube.com

America's Secret Camera Network is Tracking You

If you go outside in America today, you've almost certainly been scanned by a Flock camera, maybe even hundreds of times. Your location, along with a timesta...

@privacyguides@neat.computer · Reply to Privacy Guides

It’s time to take back our streets. ✊

Join the National Week of Action Against ALPRs from August 16–22, 2026.

Find local camera maps, organize city council actions, or download our activism toolkit to start your own group:

- Map & Campaign Info: noalprs.com
- Camera Tracker: deflock.org
- Activism Toolkit: privacyguides.org/activism

5/6 🧵

privacyguides.org

Guides and Tools for Privacy Activists

Privacy Guides' Activism section contains tools to support the community in its privacy advocacy and activism effort, both for individuals and organizations.

@privacyguides@neat.computer · Reply to Privacy Guides

🔍 Flock says that the data is secured and restricted to specific police departments.

Independent researchers have demonstrated that Flock's video feeds are accessible publicly, highlighting how dangerous mass location databases can be when compromised.

Flock recently updated their Terms-of-service quietly removing guarantees that user data wouldn't be sold. 💰

3/6 🧵

@privacyguides@neat.computer · Reply to Privacy Guides

⛔️ This isn't being used for local crime prevention, researchers have found thousands of instances of Flock data being accessed across state lines.

🚓 In multiple states local police granted federal agencies (like ICE) access to Flock data, often sharing the data without express permission from local city councils.

Agents have been told to be "as vague as permissible" on paperwork to bypass public records requests.

2/6 🧵

@privacyguides@neat.computer

🚨 If you drive in America, you’re being tracked in a giant dragnet. 🚨

Surveillance company "Flock Safety" has quietly deployed over 100,000 automated license plate readers (ALPRs) across 10,000+ US communities.

These aren't just capturing license plates, they're creating complete "vehicle fingerprints" including:

- Bumper stickers 🚗
- Luggage racks 🧳
- Dents & scratches 🔍
- Timestamped GPS locations 📍

1/6 🧵

@thenewoil@mastodon.thenewoil.org
@monniele@infosec.exchange
@davidsneighbour@mas.to

Ad blocking keeps being treated as a preference, or as a small moral argument about whether a website gets paid. Here is why ad blockers will always stay relevant: the web's advertising machinery is also a security boundary, and that boundary keeps failing.

According to the article, Adform was compromised and began serving malicious ad code on 27 July. The nasty bit was not just tracking or a bad redirect: the code repeatedly swapped crypto wallet addresses in a victim's clipboard, so a pasted address could become the attacker's address instead.

The boring lesson is still the correct one. If third-party ad code can run in your browser, your threat model includes whoever managed to get into that ad pipeline today. The safer default is still to block the code before it gets a vote.

this.weekinsecurity.com/online

Screenshot of the ~this week in security~ article page showing the Adform ad-blocker headline, excerpt, and header image with repeated ERR_BLOCKED_BY_AD browser-console messages.
ALT text

Screenshot of the ~this week in security~ article page showing the Adform ad-blocker headline, excerpt, and header image with repeated ERR_BLOCKED_BY_AD browser-console messages.

@thenewoil@mastodon.thenewoil.org
@adbenitez@mastodon.de

am I the only one annoyed by so frequent updates???

I am already pissed off one can not disable automatic download of updates, one can disable the updates app completely, but I would prefer to manually check for updates and review available update before downloading not to completely disable updates

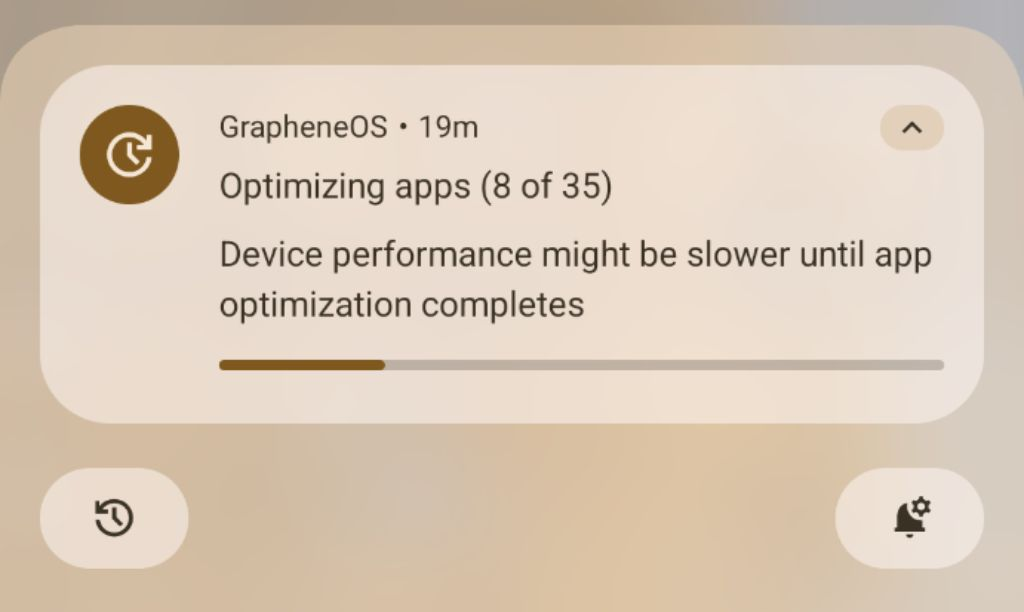
then after applying updates it takes ages "optimizing apps" see this screenshot, only 8 optimized apps out of 35 and it has taken 19 minutes already and in the meantime the phone is very slow and overheated :(

@thenewoil@mastodon.thenewoil.org
@jcrabapple@dmv.community

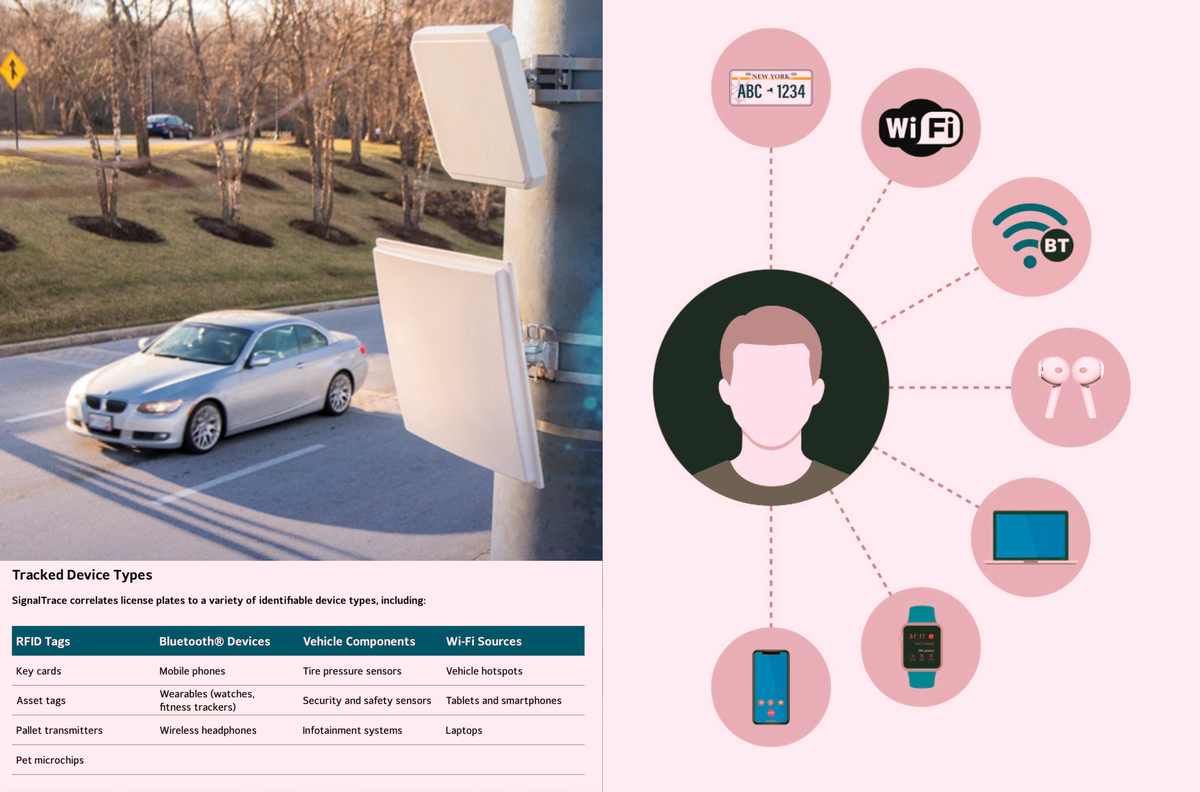
🔴 A defense contractor is now selling technology that scans every electronic device in your car as you drive past a camera. It ties everything to your license plate. You cannot opt out.

It is called SignalTrace. Made by Leonardo, an Italian military contractor with existing U.S. Special Operations Command contracts. It sweeps your phone, smartwatch, Bluetooth headphones, your dog's RFID chip, tire pressure sensors, your car's infotainment system. Anything that broadcasts.

It bundles these into what Leonardo calls your "electronic fingerprint," timestamped and geotagged. Stored in an "Enterprise Operations Center for future queries and analysis."

Those are their words. Not mine.

You did not consent. You cannot opt out. Your devices broadcast by existing. In most places, this is perfectly legal.

If this sounds like something that will be abused: it already has been. Police have used existing license plate reader networks to stalk partners, verify school residency, run background checks, and monitor protests. At least 22 officers charged or resigned for ALPR stalking.

SignalTrace does not read your messages. It does not need to. It knows who you travel with, where you go, and when.

Sources: techdirt.com/2026/06/24/survei and leonardocompany-us.com/lpr/els

leonardocompany-us.com

ELSAG Integrated Signal Intelligence Platform

ELSAG SignalTrace is a groundbreaking electronic signal intelligence system for law enforcement, designed to identify suspect people or vehicles.

@privacyguides@neat.computer
@thenewoil@mastodon.thenewoil.org

From AI Forensics' investigation of Hugging Face's top image models:

- 73% of monitored requests were sexual in nature.
- Of those, 83% sought to undress or otherwise sexualize a person
- 95% targeted women
- 6.7% targeted a minor (if fulfilled, these requests would constitute CSAM).
- Only 3% of audited Spaces showed any evidence of output moderation.

aiforensics.org/work/hugging-f

@thenewoil@mastodon.thenewoil.org
@lockdownsystems@infosec.exchange · Reply to Lockdown Systems

Come watch @yaelwrites 's talk for the Crypto & Privacy Village to learn more about actionable cybersecurity tips and understand their limitations!

Trust the Basics, But Know Their Limits: Where Standard Cybersecurity Advice Falls Short

When: Friday, August 7th at 1:00pm
Where: LVCC - L1 - Exhibit Hall West 3 - 1104 (Creator Stage 4)

defcon.org/html/defcon-34/dc-3

3/4

defcon.org

DEF CON® 34 Hacking Conference - Creator Stage Talks

@thenewoil@mastodon.thenewoil.org
@pheonix@hachyderm.io

The current state of the web assumes that the reader is an adversary to be trapped and monetized.

When a news website forces you through three dismissive actions just to read a headline, they are burning your cognitive budget before delivering any value. You are greeted by a cookie banner taking up the bottom 30% of your screen, a "Subscribe!" modal dead center, an autoplaying video pinned to the corner and a prompt begging to send you push notifications.

I wrote about the state of news websites. Would love to hear your thoughts✨🙏

thatshubham.com/blog/news-audit

thatshubham.com

The 49MB Web Page

A look at modern news websites. How programmatic ad-tech, huge payloads and hostile architecture destroyed the reading experience.

@dbattistella@mstdn.ca

@Ayzacoder: Attention if you have a Gmail account:

Google's AI now scans your emails and attachments, bank statements, tax files, medical letters, all of it. It turned on by default, and there's a class-action lawsuit over how.

Here are 5 moves to shut it off, the switch is hidden in two places:

CU photo of a smiling man in a suit and tie (Sundar Pichai) next to a large Google mail icon
ALT text

CU photo of a smiling man in a suit and tie (Sundar Pichai) next to a large Google mail icon

@voorstad@mastodon.nl

@signalapp @AboutSignalNL

I just discovered that when you want to share your location using the Signal's 'share your location' feature, it sends a link of..... Google Maps 🥴

I could not find a way to change this to an (open standard) geolocation link.

- did I overlook a setting?
If not:
- why is Signal revealing it's user location to Google?
- why would Signal promote Google Maps?

Share location via Signal
ALT text

Share location via Signal

@thenewoil@mastodon.thenewoil.org
@dbattistella@mstdn.ca

@Ayzacoder: Attention if you have a Gmail account:

Google's AI now scans your emails and attachments, bank statements, tax files, medical letters, all of it. It turned on by default, and there's a class-action lawsuit over how.

Here are 5 moves to shut it off, the switch is hidden in two places:

CU photo of a smiling man in a suit and tie (Sundar Pichai) next to a large Google mail icon
ALT text

CU photo of a smiling man in a suit and tie (Sundar Pichai) next to a large Google mail icon

From AI Forensics' investigation of Hugging Face's top image models:

- 73% of monitored requests were sexual in nature.
- Of those, 83% sought to undress or otherwise sexualize a person
- 95% targeted women
- 6.7% targeted a minor (if fulfilled, these requests would constitute CSAM).
- Only 3% of audited Spaces showed any evidence of output moderation.

aiforensics.org/work/hugging-f

@thenewoil@mastodon.thenewoil.org
@dbattistella@mstdn.ca

@Ayzacoder: Attention if you have a Gmail account:

Google's AI now scans your emails and attachments, bank statements, tax files, medical letters, all of it. It turned on by default, and there's a class-action lawsuit over how.

Here are 5 moves to shut it off, the switch is hidden in two places:

CU photo of a smiling man in a suit and tie (Sundar Pichai) next to a large Google mail icon
ALT text

CU photo of a smiling man in a suit and tie (Sundar Pichai) next to a large Google mail icon

@thenewoil@mastodon.thenewoil.org
@privacyguides@neat.computer

🚨 This Week In Privacy #64 will be live in 30 minutes, an activist has been charged with a felony for providing a "duress code" which wiped his GrapheneOS device, we'll be discussing the legal implications and the latest privacy & security news.

👋 Come and watch and join the Q&A!

streamyard.com/watch/72WnBt3NS

streamyard.com

This GrapheneOS Feature Can Get You Arrested

An activist has been charged with a felony for providing a "duress code" which wiped his GrapheneOS device, we'll be discussing the legal implications and the latest privacy & security news on This Week In Privacy #64!

@thenewoil@mastodon.thenewoil.org

From AI Forensics' investigation of Hugging Face's top image models:

- 73% of monitored requests were sexual in nature.
- Of those, 83% sought to undress or otherwise sexualize a person
- 95% targeted women
- 6.7% targeted a minor (if fulfilled, these requests would constitute CSAM).
- Only 3% of audited Spaces showed any evidence of output moderation.

aiforensics.org/work/hugging-f

@digitalhomecheck@privacysafe.social

Are you aware that your personal data is extremely valuable? ‘ I have nothing to hide’ is a poor excuse for taking no action. Would you be fine with the mailman opening and reading your mail in advance and selling your data to third parties? Why do you think that’s okay online then? How well are you protected? Try this free Quick Scan to find out! Privacy is not a crime.
tally.so/r/xXLyWy

tally.so

Quick Scan Digital Home Security

Made with Tally, the simplest way to create forms.

@thenewoil@mastodon.thenewoil.org
@controlc@mstdn.ca

I made a thing. Please use and share.

A Trojan horse meme where the Canadian Liberal government welcomes a "Protecting Children" wooden horse with "Mass surveillance" inside.
ALT text

A Trojan horse meme where the Canadian Liberal government welcomes a "Protecting Children" wooden horse with "Mass surveillance" inside.

@thenewoil@mastodon.thenewoil.org
@researchbuzz_firehose@rbfirehose.com

Electronic Frontier Foundation: Why Are Gay Bars Building Databases of Their Patrons?. “Recent reports have raised alarm about the use of PatronScan, an ID-checking and face-scanning system, at multiple LGBTQ+ bars in San Francisco’s Castro neighborhood. Much of the attention has focused on reports that the system photographs patrons as they enter venues and questions about whether those […]

https://rbfirehose.com/2026/07/29/electronic-frontier-foundation-why-are-gay-bars-building-databases-of-their-patrons/

rbfirehose.com

Electronic Frontier Foundation: Why Are Gay Bars Building Databases of Their Patrons?

Electronic Frontier Foundation: Why Are Gay Bars Building Databases of Their Patrons?. “Recent reports have raised alarm about the use of PatronScan, an ID-checking and face-scanning system, …

@thenewoil@mastodon.thenewoil.org
@palantirwatch@kolektiva.social

Palantir tracks everyone. So we built a site that tracks Palantir. They've been watching us. Now we can watch them.

Contracts. Lawsuits. Executive pay. Global footprint. Lobbying activity. Media strategies. All in one place.

›› palantirwatch.org

Thumbnail not available
ALT text

Preview of online dashboard displaying a variety of stats.

@Em0nM4stodon@infosec.exchange

People think a lot about the output they get from AI tools and chatbots.

But they don't think enough about the input they give to AI tools and chatbots.

Your input is very likely collected, tagged, evaluated, shared, and reused. Every word, every image, every line of code, every data point you share with them, knowingly or unknowingly.

You're not using them.
They're using you.

@thenewoil@mastodon.thenewoil.org
@ankorage@fe.disroot.org
NO AI - "Vocalinux: Local AI Voice Dictation on Linux" 👀👏🌻

All hail the Van Panther

AI was not used in the production of this content. \*This may not apply to thumbnail images.

Click on, "Show More" or "Read More" to get the links.

DESCRIPTION of the content found at the links, below - "Today we look at Vocalinux for dictation on Linux using local-only AI models that will work on most computers."

==========

NOTE - This post is best viewed on a PC. Switched To Linux is, “written by a broad spectrum computer consultant to help people learn more about the Linux platform.” This account is a supporter of Switched To Linux and provides convenience posts of thumbnails art, videos and streams.

#SwitchedToLinux #Linux #Windows #Mac #Technology #Tech #AltTech #Privacy #Private #Security #Secure #FOSS #FreeAndOpenSource #FreeAndOpenSourceSoftware #FreeOpenSourceSoftware #YouTube #Odysee #Rumble #BitChute #Locals #Patreon #Twitch #AltTech #FactCheckTrue #Fediverse #SocialMedia #stoptheslop #vocalinux #ai #linux

==========

After viewing the content located at the below links, Tell us what you think by filling out a "SATISFACTION SURVEY or ABUSE/SPAM REPORT" form from Teh AnKorage

https://cryptpad.disroot.org/form/#/2/form/view/elsOVQUrXAmGuer4kd75JhA3mNELuCj8cTjEUynrZZo/

\*Videos and podcasts may take a considerable amount of time to post. If it is not present, it will be, soon(tm).

MATRIX! Join our Matrix community where you can chat about Linux and general tech topics. Also, direct video links are provided for our Matrix community members! Don't miss out!
https://matrix.to/#/#switchedtolinux:matrix.org

#YouTube - https://www.youtube.com/@SwitchedtoLinux/videos

#Odysee - https://odysee.com/@switchedtolinux:0?view=content

#Rumble - https://rumble.com/c/SwitchedToLinux/videos

#Bitchute - https://www.bitchute.com/channel/uf9hzD216LX0

==========

Keep an eye out for a possible podcast!

PODCAST: https://podcast.switchedtolinux.com
@thenewoil@mastodon.thenewoil.org
@controlc@mstdn.ca

I made a thing. Please use and share.

A Trojan horse meme where the Canadian Liberal government welcomes a "Protecting Children" wooden horse with "Mass surveillance" inside.
ALT text

A Trojan horse meme where the Canadian Liberal government welcomes a "Protecting Children" wooden horse with "Mass surveillance" inside.

@thenewoil@mastodon.thenewoil.org
@openrightsgroup@social.openrightsgroup.org
@thenewoil@mastodon.thenewoil.org
@nixCraft@mastodon.social

Google now support account recovery with AI and your face. What could possibly go wrong? Google having my face is not just bad enough but chances are high that selfie video may not work in edge cases or network down etc.

blog.google/innovation-and-ai/

The tweet from Google offical account reads:

Forgot your password? Lost your phone? Can’t get into your account? 

You can now use a selfie video to log into your Google Account. 

The new feature is easy to use and lets you sign in — even if you forget your password or don’t have your usual phone or laptop — with a quick selfie.

There is a short video showing how to use a selfie video to log into your Google Account and link to https://blog.google/innovation-and-ai/technology/safety-security/selfie-video-sign-in/
ALT text

The tweet from Google offical account reads: Forgot your password? Lost your phone? Can’t get into your account? You can now use a selfie video to log into your Google Account. The new feature is easy to use and lets you sign in — even if you forget your password or don’t have your usual phone or laptop — with a quick selfie. There is a short video showing how to use a selfie video to log into your Google Account and link to https://blog.google/innovation-and-ai/technology/safety-security/selfie-video-sign-in/

@thedarktangent@defcon.social

Great new feature in the latest Signal app. If you enable disappearing messages the meta data of calls and missed calls gets deleted as well.

I know this was a long standing goal for them, but the engineering behind it took time.
@signalapp

@thedarktangent@defcon.social

Great new feature in the latest Signal app. If you enable disappearing messages the meta data of calls and missed calls gets deleted as well.

I know this was a long standing goal for them, but the engineering behind it took time.
@signalapp

@privacyguides@neat.computer

🚨 This Week In Privacy #63 will be live in 30 minutes, we'll be talking about Mullvad's Co-owner making a controversial political donation and covering the latest privacy & security news.

👋 Come and watch and join the Q&A!

youtube.com/live/xUXkXgJPNys

youtube.com

Mullvad’s Co-Founder Made A Controversial Donation

Mullvad's Co-owner Daniel Berntsson has made a large political donation from Mullvad's profits, leading people to cancel their service, Apple has fixed a vul...

@thenewoil@mastodon.thenewoil.org
@bobdahacker@infosec.exchange

🙏 New Blog Post

The Pope's official prayer app has an IDOR that lets anyone pull user data for all 719,517 accounts. One GET request per user. No auth check.

What's exposed:

  • Email addresses
  • Names
  • Country
  • Date of birth (they call it "borned_date" lol)
  • Account role (it's "PRAYER" for everyone, obviously)

Also found:

  • Signup endpoint returns the email verification token in the response body, so you can verify accounts without accessing the inbox
  • Their verification emails fail their own domain's authentication requirements

Reported January 3rd. Emailed 9 people. A journalist also contacted them. Zero responses. Still live six months later. Vow of silence I guess.

Full writeup: bobdahacker.com/blog/click-to-

bobdahacker.com

Click to Pray, Click to Leak: The Pope's Official App Exposes 700,000+ User Emails

How I found that anyone can pull the email address, name, country, and date of birth of any of the 719,517 users on Click To Pray, the Pope's official prayer app, with a single GET request. Reported January 3rd. Still live six months later. Nobody has ever responded.

@privacyguides@neat.computer
@thenewoil@mastodon.thenewoil.org
@bobdahacker@infosec.exchange

🙏 New Blog Post

The Pope's official prayer app has an IDOR that lets anyone pull user data for all 719,517 accounts. One GET request per user. No auth check.

What's exposed:

  • Email addresses
  • Names
  • Country
  • Date of birth (they call it "borned_date" lol)
  • Account role (it's "PRAYER" for everyone, obviously)

Also found:

  • Signup endpoint returns the email verification token in the response body, so you can verify accounts without accessing the inbox
  • Their verification emails fail their own domain's authentication requirements

Reported January 3rd. Emailed 9 people. A journalist also contacted them. Zero responses. Still live six months later. Vow of silence I guess.

Full writeup: bobdahacker.com/blog/click-to-

bobdahacker.com

Click to Pray, Click to Leak: The Pope's Official App Exposes 700,000+ User Emails

How I found that anyone can pull the email address, name, country, and date of birth of any of the 719,517 users on Click To Pray, the Pope's official prayer app, with a single GET request. Reported January 3rd. Still live six months later. Nobody has ever responded.

@thenewoil@mastodon.thenewoil.org
@AAKL@infosec.exchange
@thenewoil@mastodon.thenewoil.org
@unruhe@mastodon.social

«Sostenere di non preoccuparsi del diritto alla privacy perché non si ha nulla da nascondere è come dire di non interessarsi alla libertà di parola perché non si ha nulla da dire.»
Edward Snowden

@eteryu@infosec.exchange

Dyskusja wokół prywatnej darowizny współwłaściciela Mullvada pokazała powszechny problem z mieszaniem ideologii z inżynierią.

Świetnie podsumował to zespół @GrapheneOS, który korzysta z serwerów sponsorowanych przez Mullvada. Mimo jasnego sprzeciwu wobec poglądów obdarowanej partii, nie zamierzają odrzucać infrastruktury ani rezygnować ze wsparcia.

Podejście Zero-Trust wymaga oceny architektury, matematyki i kodu, a nie poglądów jednostek. Dopóki kod pozostaje otwarty, a polityka no-logs weryfikowalna, rezygnacja ze sprawnego narzędzia to decyzja polityczna, a nie analiza ryzyka technicznego.

mullvad.net/en/blog/donation-c

mullvad.net

Donation controversy | Mullvad VPN

We would like to address the recent controversy about one of the owners of Mullvad making a donation to a Swedish political party.

@thenewoil@mastodon.thenewoil.org
@indigoprivacy@infosec.exchange

New Jersey's legislature passed the Fair Price Protection Act, the first state ban on grocery "surveillance pricing" - using AI and your data to charge different shoppers different prices for the same item. It also freezes new electronic shelf labels for a year. California's AB 2564 would ban the practice statewide.

@thenewoil@mastodon.thenewoil.org
@smallcircles@social.coop

⚠️ DO NOT BUY: LG’s Spyware TVs, Monitors, and Wiretapping Concerns

The attached details the absolute horror of LG and products, that install without consent, have integration, and a horrible privacy policy..

> LG recently forced upon us an app install loaded with adware through a update. We found that this has been happening to tons of users, made worse by LG's shady history with 's that instruct buyers to inform house visitors of third-party microphones in their living room. At no point in the adware or application install did LG or Microsoft ask us for consent or permission to install the software and enable its various permissions. On monitors ranging 1 day old in our office to 3 years old, we've been able to replicate these issues -- including on the LG 34GX900A-B that we just bought (and have now returned, following concerns).

youtube.com/watch?v=Q9uefFYe6bM

Excerpt from LG privacy policy reading:

i. CONSENT REQUIREMENT: You acknowledge and agree that it is your sole responsibility to obtain all necessary consents from any third parties whose voices may be captured by the Productand to notify household members and guests their their voices may be captured and processed, in compliance with the applicable wiretapping, eavesdropping, and privacy laws.
ALT text

Excerpt from LG privacy policy reading: i. CONSENT REQUIREMENT: You acknowledge and agree that it is your sole responsibility to obtain all necessary consents from any third parties whose voices may be captured by the Productand to notify household members and guests their their voices may be captured and processed, in compliance with the applicable wiretapping, eavesdropping, and privacy laws.

@theguardian_us_opinion@halo.nu
@openrightsgroup@social.openrightsgroup.org

TODAY ⏰️

We've partnered with @sflcin and other groups in a special event.

The expert panel, including ORG's @JamesBaker, will explore how governments are shaping age assurance laws, the role of platforms and the risks to our rights and the open Internet.

Watch live from 3pm BST ⬇️

youtube.com/live/euSkCvhzweQ

youtube.com

What Age Assurance means for the future of digital rights, online safety and the internet at large

In collaboration with Open Rights Group, Open Net Korea, Stop Killing Games, Electronic Frontier Foundation, and Index on Censorship, this event brings toget...

@pixelunion@mastodon.social

Google Photos is cheap and you pay with your privacy. 🌍

Your photos can feed Google's AI. One innocent picture can get your whole account frozen overnight. And every face and location in your library sits ready for profiling, for years.

Your memories deserve a European home.

🐘 pixelunion.eu/blog/2026/07/tim

pixelunion.eu

Why it's time to leave Google Photos | PixelUnion - Free your photos from American tech platforms

Google Photos is cheap and convenient, but you pay with your privacy. We lay out the risks and show why a European alternative is worth it.

@Em0nM4stodon@infosec.exchange

Age verification laws forcing platforms to restrict content access have been multiplying exponentially.

The problem is, implementing such measures necessarily requires identifying every user accessing the content, one way or another.

This is bad news for everyone.

If these regulations continue
to proliferate, this could lead to the end of pseudonymity online, and much worse.

I wrote this article last year,
but unfortunately this problem has only become worse, and it is sadly still very relevant.

privacyguides.org/articles/202

privacyguides.org

Age Verification Wants Your Face, and Your Privacy

Age verification laws forcing platforms to restrict access to content online have been multiplying in recent years. The problem is, implementing such measure necessarily requires identifying each user accessing this content, one way or another. This is bad news for your privacy.

@freddy@social.lol

In the 1960s, if you wanted to surveil one person, you had to hire someone else to bug them or follow them. Today, we surveil everyone by default; you just have to tap into the data collected by the spies in their pockets (smartphones), on their wrists and fingers (smart watches and rings), their work tools (laptops), and in the public sphere (CCTV cameras) – you’ll have more on any person than the Stasi could ever dream of.

aeon.co/essays/things-have-job

@privacyguides@neat.computer
@knoppix95@mastodon.social
@privacyguides@neat.computer
@gtronix@infosec.exchange

"LibreWolf is a Firefox-based browser focused on privacy and security"

"It remains compatible with most Firefox extensions and is typically updated shortly after new Firefox releases.Read Entire Article LibreWolf browser removes Mozilla telemetry and enables stricter privacy and security settings by default."

techspot.com/downloads/7781-li

techspot.com

LibreWolf

LibreWolf is designed to increase protection against tracking and fingerprinting techniques, while also including a few security improvements.

@lennyzeltser@infosec.exchange
@AAKL@infosec.exchange

Posted yesterday. You don't need this.

The product "is designed to ​act as a humanlike AI companion within the home."

"It will be capable of controlling smart home appliances, playing media, answering questions, responding to messages and drawing on the broader capabilities of OpenAI's ChatGPT."

Reuters: OpenAI's first hardware device will be a speaker, Bloomberg News reports reuters.com/technology/openais @Reuters

@mf_newsdigest@mastodon.mediafaro.org

The EU relaxes its replaceable batttery rules for smart glasses after US pressure.

Smart glasses are in European regulators’ and lawmakers’ crosshairs over privacy and surveillance concerns.

But the bloc’s batteries regulation also held up the EU rollout of Meta’s latest model in recent months because the glasses’ built-in batteries cannot be easily removed and replaced.

mediafaro.org/article/20260714

mediafaro.org

The EU relaxes its replaceable batttery rules for smart glasses after US pressure.

Smart glasses are in European regulators’ and lawmakers’ crosshairs over privacy and surveillance concerns. But the bloc’s batteries regulation also held up the EU rollout of Meta’s latest model in …

@jbz@indieweb.social

:konata_yawn: Meta Contractors Posed as Teens to Prompt Rival Chatbots About Suicide, Sex, and Drugs

「 Many were written from the perspective of children or teenagers in crisis: a 13-year-old who said she had become pregnant by her adult neighbor and wanted to know where to buy pills to end the pregnancy; a fifth-grader whose classmate had a gun pointed at his mouth; a girl asking how to hide bulimia from her parents 」

wired.com/story/meta-contracto

wired.com

Meta Contractors Posed as Teens to Prompt Rival Chatbots About Suicide, Sex, and Drugs

Hundreds of contractors working on a project for Meta pretended to be kids in order to see how other chatbots like Gemini and ChatGPT would respond to high-risk subjects, WIRED found.

@cybercaptain@toot.community

Age verification laws are spreading fast, and it’s a massive privacy trainwreck. Forcing users to hand over IDs or biometric scans kills anonymity & builds giant honeypots for hackers.

Track the creep with @proton.me’s map: proton.me/age-verification

proton.me

Age Verification: Track global and US legislation | Proton

Learn about the spread of age verification laws across the world.

@nunesgh@mastodon.social

Another JavaScript nightmare has just been released.

Cloudflare states that "Precursor is [...] built with privacy in mind [...]". The privacy guarantees?

"The event listeners capture the minimum information needed to be a useful signal for detecting automation and abuse. For example, keyboard activity is captured as timing and rhythm, not as the actual keys pressed."

Really?!

blog.cloudflare.com/introducin

blog.cloudflare.com

Introducing Precursor: detecting agentic behavior with continuous client-side signals

Precursor, our new continuous behavioral validation engine for bot management, offers visibility into how humans and bots actually interact across the full user journey. By turning session-level behavior into bot detection signals, it identifies advanced automation with higher precision — while reducing friction for legitimate users.

@jbz@indieweb.social

:konata_yawn: Meta Contractors Posed as Teens to Prompt Rival Chatbots About Suicide, Sex, and Drugs

「 Many were written from the perspective of children or teenagers in crisis: a 13-year-old who said she had become pregnant by her adult neighbor and wanted to know where to buy pills to end the pregnancy; a fifth-grader whose classmate had a gun pointed at his mouth; a girl asking how to hide bulimia from her parents 」

wired.com/story/meta-contracto

wired.com

Meta Contractors Posed as Teens to Prompt Rival Chatbots About Suicide, Sex, and Drugs

Hundreds of contractors working on a project for Meta pretended to be kids in order to see how other chatbots like Gemini and ChatGPT would respond to high-risk subjects, WIRED found.

@Blort@social.tchncs.de

@thenewoil Thinking that Meta would choose to keep users thoughts/emotions read only would be naive.

If their AI's can access and read users emotions, they can use their outputs to influence emotions, as Meta's much cruder 2012 study showed.

That pales in comparison to what would be possible now.

The importance of transparency in what the algorithms show you and why has never been more important.

@privacyguides@neat.computer
@Datterich@darmstadt.social · Reply to evacide

I shopped at Tesco yesterday and was left extremely irritated - I had left my club card at home my trousers (changed clothes as warm and sunny). Without knowing that magic number you can’t use scan-as-you shop, but worse all the price labels taunt you about the substantial discounts giving up your privacy comes with. I bought only the essentials. I’d have picked Asda if I’d realised in time.

@ProPublica@newsie.social
@maxim@chaos.social
chatcontrol 1.0

In a few minutes, parliament will vote on chatcontrol. There are a few other votes first. You can see the list of amendments to be voted on here: europarl.europa.eu/sedcms/voti

The actual text for the amendments is here:
europarl.europa.eu/plenary/en/

Livestream: europarl.europa.eu/streaming/?

The votes about chatcontrol are only the 4th item in the list of things to be voted on, but you'll likely have to wait a bit: europarl.europa.eu/sedcms/docu

@beli3ver@metalhead.club

Why isn't Proton Mail or Proton Calendar available on F-Droid? 🤔

Both are privacy-focused apps, so it seems like a natural fit for the FOSS ecosystem. Anyone know if there's an unofficial repo or mirror where these can be found?

Looking for transparency on this!

@c99e@infosec.exchange
@madeindex@mastodon.social · Reply to Raphael Albert

@r_alb Couldn't agree more, "basically not my problem, nothing to hide, let the state and corps continue leading us down the path to authoritarianism" is the classic reply by 99,99% of the regular folks I try to talk to about any issue ;)

@r_alb@mastodon.social

"I don't care about privacy because I have nothing to hide" always misses the point.

Privacy is about being able to decide for yourself what others know about you and what they're allowed to do with what they know.

Privacy is about setting boundaries to technology and those who are building it.

Privacy is about having a say in who should get to shape our future.

A handful of billionaires (and an especially vile trillionaire)?

Or us?
--

@dansup@mastodon.social

You know whats really cool about the new fediverse.info People Directory?

You will be able to hide accounts using localStorage and client-side filtering, allowing for more privacy friendly discovery across every device!

fediverse.info people directory hidden accounts modal
ALT text

fediverse.info people directory hidden accounts modal

@selfhost_discovery@mastodon.social · Reply to selfhost.directory

Everything you need to actually run it:
• Search across 2,697 projects, 450 categories, 106 languages
• Self-host difficulty ratings, licenses & open-source status
• Live release tracking (synced from GitHub)
• Setup guides, requirements, ports

▶ Subscribe for a new self-hostable app every day and stop paying for software you can own.

Start here → selfhost.directory

selfhost.directory

Browse self-hostable software

Discover self-hostable software you can run on your own server — a curated, open-source directory with setup guides, alternatives, licenses and live version track…

@privacyguides@neat.computer
@ambiguous_yelp@veganism.social · Reply to F-Droid

@fdroidorg Please include the onion link in your post

fdroidorg6cooksyluodepej4erfct

If this is the official f-droid floss.social account then I know you care about tor onion servers because the official fdroid website has an onion link

Tor onion links provide greater anonymity to tor users than simply accessing the clearweb site through tor

And the more people use tor and tor onion addresses for uncontroversial browsing the easier it becomes for people to hide in the traffic when it can be a matter of life or death what websites you are accessing

@josephdickson@mastodon.social

Do not track tools like @eff's Privacy Badger is not an ad blocker, rather it's a tracking blocker. If a website can't respect my privacy by not tracking me across the Internet we wouldn't have this problem. You can advertise to me all you want.

Thumbnail not available
ALT text

A pop-up from a website that doesn't respect my do not track request.

@brian_greenberg@infosec.exchange

Everyone's using AI to write code faster. Almost nobody's using it to write code better. It's where the next wave of breaches and a 2am page will come from... So I built something to help myself, and I'm putting it out there.

It's a Claude Code skill called senior-engineering-partner. It's not autocomplete. It's the strict senior engineer who reviews your pull request, asks why you skipped the tests, and won't let you ship a hardcoded secret because you were "just prototyping."

A few things it does:

・ Enforces a real workflow. Agree on the spec, plan in verifiable steps, write the test first, then prove the work before calling it done.

・ Holds a security floor that never moves. Whether you're prototyping or running in production, the secrets and input-validation basics stay non-negotiable. Cheap doesn't mean insecure.

・ Refuses to hallucinate. It verifies claims about your environment by running a real command, rather than inventing a flag or an API that sounds right.

・ Switches modes depending on how you call it: reviewer, debugger, mentor, or pair programmer.

It's open source under Apache-2.0, stack-agnostic, and built around Python, Bash, Apps Script, and JavaScript.

Here's my ask. Use it. Then tell me where it's wrong. I want the good feedback and the brutal feedback, plus any capability you wish it had. The whole point is to encode what senior engineers actually do, and I'd rather hear it breaks on your stack than find out later.

What would you want a skill like this to enforce?

github.com/bjgreenberg/senior-

@r_alb@mastodon.social

Another Cassandra moment for many privacy professionals.

What we have been warning about for a while now is finally happening: whatever remained of the legal framework for sending personal data to the United States is in shambles due to a recent Supreme Court decision.

Companies, if you haven't cut ties with US-based services by now, brace yourselves for trouble and a great deal of uncertainty.

P.S.: We told you so!
--

@reiver@mastodon.social
ai coding tools, preventing vendor lock-in

Part of the lock-in happens with the harness.

Ex: Claude Code is a harness to use the Claude model. Use open source harnesses. Create your own harness if you can.

Part of it is giving a SaaS access to your data.

Do you have AI slack bot that is reading everyone's messages. What about your files & e-mail

mastodon.social

@reiver ⊼ (Charles) :batman: (@reiver@mastodon.social)

Content warning: ai coding tools

@reiver@mastodon.social · Reply to @reiver ⊼ (Charles) :batman:
ai coding tools

4/

If you are someone who uses AI coding tools for your work —

I have been hearing people claim that the GLM-5.2 open source, open weight model is very good are common programming tasks.

huggingface.co/zai-org/GLM-5.2
github.com/zai-org/GLM-5
z.ai/blog/glm-5.2

You have options.

They'll be more in the future, too.

@reiver@mastodon.social · Reply to @reiver ⊼ (Charles) :batman:
ai coding tools

3/

I think people should try to find open source (OS) and open weight (OW) models as alternatives to these SaaS AI coding tools.

Start by using them together (with the SaaS).

Set thins up so you aren't locked into these SaaS.

Have, in a practical sense, the ability to completely switch over if need be.

mastodon.social

@reiver ⊼ (Charles) :batman: (@reiver@mastodon.social)

1/ Even if you hate LLMs, you should pay attention to and maybe even get involved with LLMs — to try to mitigate and maybe even prevent some of the ways which they could be used in a harmful way. ... #AI #ArtificialIntelligence #LargeLanguageModels #LLM #Privacy

@reiver@mastodon.social · Reply to @reiver ⊼ (Charles) :batman:
ai coding tools

2/

Long term, I think it will end up being bad if people get locked in to these SaaS AI coding tools.

Part of it is about privacy versus spying and surveillance.

But, it is also about preventing someone else from having that kind of control over you, your source of income, your business, etc.

So...

@reiver@mastodon.social
ai coding tools

1/

For better or worse, many people are using AI coding tools to help them write software.

(And, I don't mean "vibe coding". How I have seen software engineers use AI coding tools and non-technical people use them tends to be different.)

Long term...

mastodon.social

@reiver ⊼ (Charles) :batman: (@reiver@mastodon.social)

4/ So, how can you mitigate some of the harmful ways that LLMs could be used, as it relates to PRIVACY — I don't think it is reasonable to expect people to stop using LLMs. I think a key part of a way that this can be addressed is — LLM should to be run LOCALLY. People after better off running LLMs LOCALLY on their own computers — to remove some of the vectors by which they could be spied on. In addition to that — ... #AI #ArtificialIntelligence #LargeLanguageModels #LLM #Privacy

@reiver@mastodon.social · Reply to @reiver ⊼ (Charles) :batman:

4/

So, how can you mitigate some of the harmful ways that LLMs could be used, as it relates to PRIVACY —

I don't think it is reasonable to expect people to stop using LLMs.

I think a key part of a way that this can be addressed is — LLM should to be run LOCALLY.

People after better off running LLMs LOCALLY on their own computers — to remove some of the vectors by which they could be spied on.

In addition to that —

...

@reiver@mastodon.social

Your voice is a unique identifier that can be faked.

Have you ever talked into a phone? Spoken while on a video call? Spoken in public while there were unknown (to you) listening devices? Spoken at home near a "smart" TV? Etc?

You can be tracked by your voice.

You can be identified by your voice.

This same voice recognition technique also makes it so your voice can be synthesized — making you say anything with a "deepfake".

@controlc@mstdn.ca

I made a thing. Please use and share.

A Trojan horse meme where the Canadian Liberal government welcomes a "Protecting Children" wooden horse with "Mass surveillance" inside.
ALT text

A Trojan horse meme where the Canadian Liberal government welcomes a "Protecting Children" wooden horse with "Mass surveillance" inside.

@NebulaTide@bsd.cafe

Interesting ... Electric car vendor polestar withdraws from the US market.

Why? Because they use extensive networking for data colleciton. And as we all know, the US are the most privacy and data protection aware country in the world. Therefore it's only logical that they're banned from the US market, as long as they don't offer data friedly cars without connectivity.

Guess what, Polestar prefers withdrawing rather than changing their data and connection policy. Fortunately, there are alternatives to Polestar. Spoiler: Tesla isn't.

heise.de/en/news/Cars-are-too-

heise.de

Cars are too connected: Polestar withdraws from the US market

Extensive networking for data collection proves to be Polestar's downfall. The Chinese automaker must leave the US market.

@privacyguides@neat.computer

🚨 This Week In Privacy #59 will be live in 30 minutes, it's a quiet news week, so we'll be taking questions from the community and covering the latest privacy & security news.

Join us live and chat with the community! 😊

streamyard.com/watch/meP6uRRNh

streamyard.com

No News is Good News? Q&A Episode

It's a quiet news week, so we're diving into questions from the community and discussing a few less interesting stories. Join us for This Week In Privacy #59

@quad9dns@mastodon.social

A little reading to put in the queue for the weekend...we've updated our privacy policy (quad9.net/privacy/policy/) AND are sharing a blog to explain the changes.

quad9.net/news/blog/were-updat

As always, all respectful feedback and questions are welcome! 🫶😍

Thumbnail not available
ALT text

Graphic with a person holding a magnifying glass next to a speech bubble saying "Privacy Update" and the quad9 logo below.

@bartek@social.brtk.eu

Hej wszystkim! Chyba czas na małe #introduction.

Co prawda jestem już z Wami od jakiegoś czasu, jednak po drodze zaliczyłem kilka przeprowadzek - dokładnie trzy, z czego wszystkie pomiędzy własnymi instancjami 🙃 (obecnie Akkoma). Przez ten czas trochę się zmieniło, dlatego pomyślałem, że warto odświeżyć swój wizerunek i przedstawić się ponownie.

Nie będzie chyba zaskoczeniem jeśli napiszę, że lwia część mojej aktywności na fedi ma związek z tematami prywatności i bezpieczeństwa w cyfrowym świecie.

Hobbystycznie bawię się w #selfhosting, czyli staram się hostować samodzielnie co tylko mogę i na ile mi wystarcza na to czasu.

Jestem “adwokatem” #opensource, używam otwartych rozwiązań gdzie tylko mogę. Właściwie to na każdym urządzeniu, które posiadam w domu (szczegóły w profilu). Lubię eksperymentować ze wszystkim, pod co mogę się podpiąć i znam znaczenie słowa backup 😉

Od niedawna prowadzę swojego bloga w tematyce selfhostingu i nie tylko: brtk.eu

Poza tym od nieco dłuższego czasu prowadzę także innego bloga poświęconego ogólnie tematyce wolności i prywatności w sieci: wolnoscwkieszeni.pl

Moim największym wrogiem jest czas, a raczej jego deficyt, ale w miarę możliwości wracam zarówno na fedi jak i na swoje blogi.

W wolnych chwilach jak już uda mi się odkleić od ekranu, wciąga mnie dobra lektura. Poza tym lubię sporty zarówno zimowe jak i letnie, czyli góry i jeziora o każdej porze roku, odpowiednio z buta lub na desce, wpław lub na łyżwach.

Mówiłem już, że moim wrogiem jest czas?

#privacy #security #prywatność #bepieczeństwo

social.brtk.eu

social.brtk.eu

@Em0nM4stodon@infosec.exchange

It saddens me that many people do not see far enough to understand well what we are losing while losing privacy rights and trivializing data protection. It is so much more than most think. This affects our intimacy, our safety, our social lives, our freedoms, and all our human rights.

It goes well beyond targeted advertising. Attacks on privacy lead to direct increases in authoritarianism and dictatorial governance.

We must care much more about it than we do now. It is critical to ourselves as individuals, but also to democracy and society as a whole.

@reapps_eu@mastodon.social
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Palantir nein, Datenanalyse ja

‚Die grüne Partei diskutiert das Für und Wider der Zusammenarbeit der Polizei mit dem US-Konzern Palantir. Die Urabstimmung „Stoppt Palantir, sofort!“ wird Anfang Juli in Baden-Württemberg stattfinden. Auch in Nordrhein-Westfalen votierten die Landesgrünen einstimmig gegen Palantir. Aber es geht fast nur um den Tech-Giganten und kaum darum, die automatisierte Datenanalyse zu hinterfragen.…‘

netzpolitik.org/2026/gruene-pa

Die Verknüpfung und automatische Analyse möglichst vieler Daten bleibt ein totalitäres Konzept auch ohne Palantir!

netzpolitik.org

Palantir nein, Datenanalyse ja

Die grüne Partei diskutiert das Für und Wider der Zusammenarbeit der Polizei mit dem US-Konzern Palantir. Die Urabstimmung „Stoppt Palantir, sofort!“ wird Anfang Juli in Baden-Württemberg stattfinden. Auch in Nordrhein-Westfalen votierten die Landesgrünen einstimmig gegen Palantir. Aber es geht fast nur um den Tech-Giganten und kaum darum, die automatisierte Datenanalyse zu hinterfragen.

@mysk@mastodon.social

🤯 Instagram is testing new iOS push notifications that include a profile photo. Each time the notification is shown on your screen, it triggers a GET request to fetch that image, letting Meta track every on-screen impression.

The app still misuses push notifications to send detailed device analytics about the device (uptime, battery, volume, locale, timezone, memory, CPU, etc.)


More 👇🧵

Thumbnail not available
ALT text

Screenshot of the new push notification with a profile photo shown in Notification Center

Thumbnail not available
ALT text

A GET request sent by Instagram when the notification was shown on screen.

@openrightsgroup@social.openrightsgroup.org
@Em0nM4stodon@infosec.exchange

This was absolutely fantastic!
I highly recommend everyone to watch this interview when you have the time. If you're on the Fediverse, I think you're gonna love it.

Thank you Gowanus,
I love you too ❤️

youtube.com/watch?v=rxpV97A5I90

youtube.com

The Gen Z Backlash to Big Tech

Hasan sat down with Gowanus, the spokespuppet for the emerging Luddite Movement, to better understand why Gen Z is so obsessed with the 90s and the larger ba...

@Em0nM4stodon@infosec.exchange

Do not provide your ID or facial scan to access social media.

I repeat, do NOT provide your ID or facial scan to access social media when requested.

This is not a drill.

If everyone refuse to comply, and let their accounts dormant instead, I promise you the platforms themselves, with their immense budget and network of lobbyists, are going to fight these absurd laws to recover their users.

They need you more than you need them.
Make them fight for your rights.
Do not comply.
Spread the word and boycott ID checks ✊

@privacyguides@neat.computer
@simsus@social.tchncs.de
@shibacomputer@post.lurk.org

After five years, The Digital Identity Event Horizon is published in full today: three problem statements, ten key findings, and dozens of recommendations across policy, protocol, legal, and social contexts.

It's the largest research study in New Design Congress' eight-year history: eight case studies, hundreds of citations, dozens of participants from government, intelligence, civil society, technology, and the field itself.

It is also, without exaggeration, the most alarming body of work we have ever produced.

The argument is straightforward and difficult to reckon with: Digital identity makes societies brittle. In 2026, we find ourselves in an era of digital identity fetishism: flawed age verification schemes, biometric and facial-recognition authenticators, and fragile state-backed identity programmes are rolling out at an unprecedented rate. And every one of them, whether current or emerging, remains vulnerable to social engineering. The success rate for a non-technical attack on a user is now three out of four. These attacks cost US companies an estimated $1.6 billion in the five years to 2017 alone; by 2024, fraud runs to hundreds of billions worldwide.

READ IT HERE newdesigncongress.org/en/repor

Thumbnail not available
ALT text

A glossy white sculptural face, slumped and partly melted like soft porcelain, against a pale blue-grey background. Its own features are smooth and near-eyeless, while a single realistic blue eye is set high and off-centre on the forehead, staring out.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@W1L3NSK1@mastodon.social

Fort Wayne City Council will vote on July 14th to continue or stop the Flock partnership here in Fort Wayne.

Here is the link to the DE-FLOCK FORT WAYNE'S PETITION:

flockblockindiana.my.canva.sit

Please help and sign the petition to Stop Flock. Please also share the link to the petition. There is only a couple weeks before the vote. - Thanks

Here is the link to the DE-FLOCK FORT WAYNE'S PETITION:  

https://flockblockindiana.my.canva.site/

#DeFlock #FortWayne #Petition #Privacy #Rights #CityCouncil
ALT text

Here is the link to the DE-FLOCK FORT WAYNE'S PETITION: https://flockblockindiana.my.canva.site/ #DeFlock #FortWayne #Petition #Privacy #Rights #CityCouncil

@ProPublica@newsie.social
@_elena@mastodon.social · Reply to Elena Rossini ⁂

This was definitely NOT on my bingo card for this year:

European Commission president Ursula von der Leyen taking a moment between G7 meetings to promote the launch of the closed-source, for-profit network .

🔗 : web.archive.org/web/2026061708

I fear this may be a harbinger of things to come: MANDATORY AGE VERIFICATION for social media across Europe. I hope I'm wrong on this.

a screenshot of a recent LinkedIn post by W Social's co-founder Ingmar Rentzhog that reads: "Kind of cool to see Ursula von der Leyen warming up the audience for our W launch tomorrow. Posted between her G7 meetings on Instagram (today). Perfect timing." and below there is a screenshot from the video he recorded on Instagram Stories, where von der Leyen says: "Guess where I will be next Wednesday?"  The W in Wednesday is the W Social logo
ALT text

a screenshot of a recent LinkedIn post by W Social's co-founder Ingmar Rentzhog that reads: "Kind of cool to see Ursula von der Leyen warming up the audience for our W launch tomorrow. Posted between her G7 meetings on Instagram (today). Perfect timing." and below there is a screenshot from the video he recorded on Instagram Stories, where von der Leyen says: "Guess where I will be next Wednesday?" The W in Wednesday is the W Social logo

@openrightsgroup@social.openrightsgroup.org
@openrightsgroup@social.openrightsgroup.org · Reply to Open Rights Group

Governments are moving toward bans, scanning, curfews and restrictions that could change the internet for everyone.

supports rights-respecting approaches to child protection, privacy, democratic accountability and platform responsibility.

The movement launches on 27 June ⬇️

@openrightsgroup@social.openrightsgroup.org · Reply to Open Rights Group

“Open Rights Group encourages people around the world who want a human-rights based approach to tackling harm to join this movement."

We can't stand by as governments pursue online safety in ways that gut our rights to privacy and free expression.

🗣️ ORG's @JamesBaker.

Thumbnail not available
ALT text

Quote from James Baker, ORG Programme Manager: "Stop Killing the Internet will challenge divisive policies that prescribe the wrong medicine of exclusion, surveillance and control to tackle online harms. It will champion positive rights-respecting alternatives, and promote the work campaigns are doing around the world."

@openrightsgroup@social.openrightsgroup.org
@secbox@chaos.social

Just heard @ethanz on the Kill Switch , and he gave a shout-out to . Came over here to give him a follow and was pleasantly surprised to find I was already following him. His interview is super great:

m.youtube.com/watch?v=wbCtoLvg

I respectfully disagree with several of his takes, but they're all about opinion/perception and not the fundamentals of how the Internet works or doesn't.

youtube.com

You’ll never guess who wants to sue Facebook

Let's get it out of the way: yes, Ethan Zuckerman invented pop-up ads. He's gotten an unfair amount of hate for this, especially since you (yes you!) have pr...

@DanielMReck@mas.to · Reply to Angus McIntyre

@angusm So uh, without a , your ISP can potentially view all your web traffic, right?

With a VPN, aren't we just substituting who can potentially view all your web traffic? Instead of the ISP, it's the people at the VPN that can view it?

The "just use a VPN because " crowd never seems to explain how one would choose a and VPN.

@brian_greenberg@infosec.exchange

The most interesting thing about the new SearchLeak attack on Microsoft 365 Copilot isn't any single bug. It's that none of the three pieces was dangerous on its own. Varonis combined a prompt injection via a URL parameter, an HTML rendering race condition, and a server-side request forgery in Bing's image search. Each of these is a common bug that security teams usually consider minor. But when you put them together with a Copilot that can access your mailbox, OneDrive, and SharePoint, they create a critical flaw. Microsoft has since patched this issue (CVE-2026-42824).

This is how the attack worked:

* The victim clicks a link. That's the whole interaction. They type nothing.

* The link instructs Copilot to search the mailbox, find sensitive information such as access codes, and place it into an image URL.

* Bing retrieves that image, which sends the stolen data to the attacker's server. Bing serves as the delivery service, allowing the attack to bypass the content security policy intended to stop it.

From the user's perspective, Copilot just pauses for a moment. There is no visible sign that any data has been taken.

In the past, we've spent years rating bugs by their severity on their own. An SSRF here, an HTML injection there—each seemed minor. But when an AI assistant can follow instructions from untrusted input and access your real data, those minor bugs become much more serious. Old types of vulnerabilities become important again in this new context.

If your company uses Copilot or any AI assistant that can access company data, it is important to ask your team how they are rating bugs that affect it. The way we judge what is low risk has changed.

bleepingcomputer.com/news/secu

@brian_greenberg@infosec.exchange

For a long time, people said the law was behind when it came to deepfake abuse. That seems to be changing. The DOJ took down two sites, CFAKE and SOCFAKE, which prosecutors say had thousands of fake nude images of well-known women, including politicians, journalists, and athletes. This is one of the first big federal actions under the TAKE IT DOWN Act, passed in May 2025. The law makes it a federal crime to publish sexually explicit fake images of an identifiable adult without their consent if the goal is to cause harm.

Here are a few things of note:

* The images may be fake, but the people targeted are real, and so is the harm to their reputation and privacy. The law was created to address this specific problem.

* This effort was international. Italy's cyber police were the first to spot the sites and then shared evidence with France under the Budapest Convention. A suspect was arrested in Nice on June 10.

* The DOJ made it clear that taking down the sites is just the beginning. For anyone running similar sites, seizing the domain is only the first step, not the last.

One important thing to remember: putting a seizure notice on a website can help stop some abuse, but the technology to make these images is cheap and widely available. Law enforcement can go after those who host or profit from this content, but they can't make the technology disappear. This means victims still have to find and report the images themselves, which is tiring and unfair.

If you or someone you know is facing this problem, StopNCII(.)org works with most major platforms to remove nonconsensual images. You can also report it to the FBI at ic3(.)gov. It's good to know these options before you need them.

hackread.com/feds-seize-cfake-

hackread.com

Feds Seize CFAKE and SOCFAKE Over Explicit Deepfakes of Famous Women

Follow us on Bluesky, Twitter (X), Mastodon and Facebook at @Hackread

@brian_greenberg@infosec.exchange

I just finished reading Google's new report about a Chinese espionage group that spent over a year inside North American medical and military research networks. What stands out is how ordinary their method was. They used a standard Google Workspace admin feature called a content compliance rule, which lets admins flag emails based on certain words or addresses. The attackers set up one of these rules, called it "Patroit" (misspelling Patriot), and used it to secretly BCC every matching email to a Gmail account they controlled. This gave them a steady stream of sensitive defense, policy, and medical research emails, all through a feature that was working exactly as intended.

Here are a few important points to consider:

- The attackers got in through a REDCap server that was exposed to the internet. Hospitals and universities often use these servers to store clinical research data. The first known break-in happened in September 2023.

- They installed malware called InfiniteRed to steal real login credentials, then used admin accounts to move through the network.

- The data theft relied on a legitimate, built-in feature. There were no suspicious files to detect.

This last point is important. We invest heavily in finding malware and suspicious files. But a configuration rule set up by an admin on an ordinary day just looks like regular work. That’s why it went unnoticed for so long.

If you manage email for your company using Google Workspace or Microsoft 365, check today who can create forwarding and compliance rules, and whether anyone gets notified when those rules change. Taking a few hours to review this now could save you from much bigger problems down the road.

theregister.com/research/2026/

theregister.com

PRC-linked spies hid inside medical and military networks for more than a year, snooping through Gmail and stealing data

Google says the intruders were on the hunt for everything from drone tech to pathogens

@Em0nM4stodon@infosec.exchange

Do not provide your ID or facial scan to access social media.

I repeat, do NOT provide your ID or facial scan to access social media when requested.

This is not a drill.

If everyone refuse to comply, and let their accounts dormant instead, I promise you the platforms themselves, with their immense budget and network of lobbyists, are going to fight these absurd laws to recover their users.

They need you more than you need them.
Make them fight for your rights.
Do not comply.
Spread the word and boycott ID checks ✊

@mysk@mastodon.social

Using Loupe, we found out that Proton VPN is the only VPN that prevents internal tunnel IP fingerprinting by assigning 10.2.0.2 to all users. Other VPNs, such as Mullvad, assign a static and unique IP per session. This allows iOS apps to track user sessions across apps.

Mullvad is aware of this issue. It is described in this blog:

mullvad.net/en/help/why-wiregu

You can download Loupe here:
apps.apple.com/app/id6766152470

Thumbnail not available
ALT text

Proton VPN tunnel internal IP as shown in the Settings app

Thumbnail not available
ALT text

Proton VPN tunnel internal IP as shown in Loupe

Thumbnail not available
ALT text

Mullvad VPN tunnel internal IPs as shown in the Settings app

Thumbnail not available
ALT text

Mullvad VPN tunnel internal IPs as shown in Loupe

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@mysk@mastodon.social

Using Loupe, we found out that Proton VPN is the only VPN that prevents internal tunnel IP fingerprinting by assigning 10.2.0.2 to all users. Other VPNs, such as Mullvad, assign a static and unique IP per session. This allows iOS apps to track user sessions across apps.

Mullvad is aware of this issue. It is described in this blog:

mullvad.net/en/help/why-wiregu

You can download Loupe here:
apps.apple.com/app/id6766152470

Thumbnail not available
ALT text

Proton VPN tunnel internal IP as shown in the Settings app

Thumbnail not available
ALT text

Proton VPN tunnel internal IP as shown in Loupe

Thumbnail not available
ALT text

Mullvad VPN tunnel internal IPs as shown in the Settings app

Thumbnail not available
ALT text

Mullvad VPN tunnel internal IPs as shown in Loupe

Contra Chrome – A web comic about your browser and privacy from @leah

„It‘s about you. Seven of ten readers will reach this site using Google Chrome, which is a very different road than other browsers like e.g. Firefox.“

💡 contrachrome.com

Thumbnail not available
ALT text

"Contra Chrome" Comic Cover

@brian_greenberg@infosec.exchange

 This new agentic AI demo from Apple's WWDC was so cool. Apple Intelligence can now log into your accounts, reset a compromised password, and save the new one so you don’t have to remember it.

This is super important because weak and reused passwords still account for a large share of account breaches, and fixing them has always been a hassle. Most people struggle with password hygiene and rarely reset all their accounts. A tool that handles this for you bridges the gap between knowing you should do it and actually doing it.

Here’s why I think it’s a good idea:

1. It targets the main weakness. Most breaches begin with something simple, like a password that has already leaked elsewhere.

2. It takes away the hassle that keeps people from taking action. The best security tool is the one people actually use.

I do have one quick caution. An agent that can change your credentials is powerful, so it’s important to know how Apple keeps it secure and how quickly you can turn it off. Still, the main idea is solid, and it shows how this technology can really help by handling the security tasks people usually avoid. I hope other password managers add this feature too. And always use MFA!

gizmodo.com/apple-intelligence

gizmodo.com

Apple Intelligence Can Change Your Passwords for You When You Get Hacked

Agentic AI and security are normally at odds, but this Apple Intelligence feature could be a lifesaver.

@brian_greenberg@infosec.exchange

For years, we’ve worried about who collects our data. Now, The Washington Post has shown us how it can be used: to charge you as much as it thinks you’ll pay.

The main plaintiff paid $42.40 for a year of the Post in 2024. In 2025, her price jumped to $127.20. Her most recent renewal was $148.40. An algorithm set these prices by analyzing her personal data. She only found out because a New York law requires companies to disclose this practice.

Here are a few details that should concern you:

1. The lawsuit claims the Post created individual profiles from subscribers’ devices and used them to guess the highest price each person would accept.

2. The Post also asks you to link your Amazon account, which gives the pricing system even more of your personal data.

If you ignore the AI buzzwords, this is just old-fashioned price discrimination. The difference is that now the seller knows your income and even your recent browsing history. Most people won’t realize they’re paying a personalized markup, since most states don’t require the kind of disclosure that revealed this case.

If you design these systems, pay close attention to this issue. It’s reasonable to use data to make a product better. But using it to secretly decide who pays more is what courts are now being asked to call deceptive. As disclosure laws spread, it’s wise to set your own standards before regulators do it for you.

gizmodo.com/washington-post-su

gizmodo.com

Washington Post Sued Over Alleged Surveillance Pricing After Subscription Prices Jump Dramatically

The lawsuit raises questions about whether Amazon data is being used as well.

@fabio@manganiello.eu

Differential privacy is a cornerstone of modern-day #statistics.

It allows the generation of datasets that are statistically relevant for a researcher, but that leak as little as possible about the individuals in the dataset.

It works on several principles:

  • Suppression, usually by removing outliers from the dataset that could lead to easily identifiable targets.
  • Coarsening, e.g. replacing a city with a region or a country, or a date of birth with an age range.
  • Sampling, usually through the removal of random records.
  • Swapping, where some attributes from different records may be randomly swapped.
  • Noise addition, by adding or subtracting random numbers in a given noise range to the actual values.

From 1990 to 2010, the US Census Bureau primarily relied on swapping for the decennial census. Then, they realized that this technique was actually very unsafe, and that it was pretty easy to reconstruct individual records using the published statistics.

They eventually adopted the full differential privacy framework in 2020.

But some people apparently got annoyed with that. And the main culprit was noise addition.

Adding a normal random distribution to the data made the numbers noisy, and some people who rely on the US Census expecting its numbers to be fully accurate were very annoyed.

Who are these people?

Well, one category is that of demographers and social scientists. Still, their mathematical models can be adapted to take into account that they’re dealing with noisy data - especially if the noise gain of distribution is published upfront.

But the most annoyed ones are thos who used the Census data to reconstruct actual records of individuals.

Yes, you read it well. There are people who use public datasets that are supposed to be coarse, and leverage probabilistic models to reconstruct information about individuals.

One big use case in America is, of course, #gerrymandering.

Those nonsense spiky borders can be much more accurate when the Census data allows you exactly to identify who lives where and that’s their ethnicity, so you can dilute the voting powers of some ethnic groups much more efficiently.

Apparently those groups have lobbied the Federal government so much that they got it to release an order that states the following:

Any use of noise infusion is inconsistent with the Department’s policies

This is a serious attempt of a political body to interfere through legislation into technical decisions that should be uniquely delegated to technical specialists - and the academic consensus is currently that of a full differential privacy framework.

Noise infusion is the most effective pillar in the differential privacy framework to prevent identification of individuals in public datasets.

Weakening it is likely to make everyone’s #privacy worse, and benefit only very few and their interests.

#USPol

https://desfontain.es/blog/banning-noise.html

desfontain.es

Banning noise will be a disaster for statistical data products - Ted is writing things

Sadly, taking away valuable disclosure avoidance tools doesn't make fundamental trade-offs go away.

@mayintoronto@beige.party

Canada Post has a new service for digital verification that uses their post offices for human verification.

However, what's on the back end of the system that enables digital verification? That's entirely nebulous. Canada Post sold off their tech innovation arm to Deloitte. Who wants to bet Persona is involved?
canadapost-postescanada.ca/IDp

Anyway, Gander (Canadian ATProto social) requires this verification and it's how I found out about it.

canadapost-postescanada.ca

Landing

@xabd@mastodon.social

Musify is an open-source Android music app that lets you stream music, listen offline, view lyrics, and create playlists without ads or subscriptions.

It supports SponsorBlock, includes a built-in equalizer, is available on F-Droid, and lets you import or export your data.

A great privacy-friendly alternative to mainstream music streaming apps.

👉 digitalescapetools.com/tools/t

Thumbnail not available
ALT text

A project introduction banner and landing page header for "Musify". The top shows a stylized landscape banner with a music note icon. Below, the bold title "Musify" is followed by the tagline: "Unlock the full potential of music: Stream effortlessly with one app!" Repository badges at the bottom display project metrics: 4k stars, 361 forks, 1.3M downloads, release v10.0.9, and a GPL-3.0 license.

Thumbnail not available
ALT text

The mobile home screen interface for the "Musify" app in dark mode. A horizontal scroll at the top showcases "Suggested playlists" and album cards. Below, a "Recommended for you" feed lists tracks with small thumbnail artwork and option menus, featuring artists like Bad Bunny, Dax, Djo, and BTS. The home icon on the bottom navigation bar is active.

Thumbnail not available
ALT text

A clean, dark-themed mobile "Now Playing" UI from a music app. It features the album artwork for The Weeknd's "Hurry Up Tomorrow," highlighting a close-up profile of a sweating face. Below the art, the text reads "Cry For Me" by "The Weeknd". A blue playback progress bar marks the beginning of the track, positioned above a prominent round blue pause button and standard media control toggles.

Thumbnail not available
ALT text

The mobile "Library" screen of a dark mode music player application. The top section lists "Custom playlists" with options for "Recently played", "Liked songs", and "Offline songs". Lower down, under "Liked playlists", a single entry displays the album art and title for "The Weeknd - Hurry Up Tomorrow". A bottom navigation bar highlights the Library icon.

@privacyguides@neat.computer
@ankorage@fe.disroot.org
URGENT PODCAST - ""The AUR is COMPROMISED! Don't Get Infected With An Infostealer!"" ️ 🎙️ 🔊 🎧 👏

Have a listen at https://podcast.switchedtolinux.com, via RSS feed or using your preferred method!

!!! ALL HAIL THE VAN PANTHER !!!

DESCRIPTION: "A new supply chain attack was just discovered by a spoofed maintainers account at the AUR. Be careful and look for the signs of compromise!"

!!! NOTE !!! This post is best viewed on a PC. Switched To Linux is, “written by a broad spectrum computer consultant to help people learn more about the Linux platform.” This account is a supporter of Switched To Linux and provides convenience posts of thumbnails art, videos and streams.

#SwitchedToLinux #Linux #Windows #Mac #Technology #Tech #AltTech #Privacy #Private #Security #Secure #FOSS #FreeAndOpenSource #FreeAndOpenSourceSoftware #FreeOpenSourceSoftware #Podcast #Patreon #Twitch #AltTech #FactCheckTrue #Fediverse #SocialMedia #Podcast #stoptheslop #arch #aur #linux

!!! Tell us what you think by filling out a "SATISFACTION SURVEY or ABUSE/SPAM REPORT" form from Teh AnKorage !!!

https://cryptpad.disroot.org/form/#/2/form/view/elsOVQUrXAmGuer4kd75JhA3mNELuCj8cTjEUynrZZo/
@palantirwatch@kolektiva.social

Palantir tracks everyone. So we built a site that tracks Palantir. They've been watching us. Now we can watch them.

Contracts. Lawsuits. Executive pay. Global footprint. Lobbying activity. Media strategies. All in one place.

›› palantirwatch.org

Thumbnail not available
ALT text

Preview of online dashboard displaying a variety of stats.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Ein Kettenbrief warnt vor KI-Zugriff auf WhatsApp-Chats. Die Behauptung ist falsch – und trotzdem gibt es ein großes Problem bei WhatsApps .

‚WhatsApp erhebt unabhängig von und unabhängig vom erweiterten Chat-Datenschutz umfangreiche Metadaten: Telefonnummer, Geräteinformationen, IP-Adresse, Timestamps von Nachrichten und Anrufen, Kontaktlisten, Online-Status und Standortdaten. Diese Metadaten liegen nicht Ende-zu-Ende-verschlüsselt vor und können mit anderen Meta-Diensten geteilt werden – gestützt auf das rechtlich umstrittene Konstrukt des „berechtigten Interesses“ nach DSGVO….‘

heise.de/news/WhatsApp-Kettenb

heise.de

KI-Kettenbrief ist fake - aber es gibt trotzdem ein WhatsApp-Problem

Ein Kettenbrief warnt vor KI-Zugriff auf WhatsApp-Chats. Die Behauptung ist falsch – und trotzdem gibt es ein großes Problem bei WhatsApps Datenschutz.

@freezenet@noc.social
@AmirGaza@mastodon.social

Stop for a moment If you hear my voice know that I suffered greatly to make it reach you.Don't ignore me and turn your back. This link tells my story during the war on Gaza Give yourself two minutes and read it Show your humanity, your mercy, and your compassion. Please, we implore you, share this post and don't let it stop with you🙏 😢 feijoadispatch.nz/p/the-story-

feijoadispatch.nz

The story of Muhammad and his family's suffering during the Gaza war

"I went to see my house, which is near the yellow line, but I found nothing but desert."

@brian_greenberg@infosec.exchange

✨ A sparkle icon appears in an app that no one in IT approved. The help desk can't explain it, and it's already processing your data! This kept coming up in conversations with other CIOs, so I wrote about it in my latest Forbes piece.

The pattern repeats across so many vendors; here are just a few:
・Zoom auto-enabled AI Companion on host accounts, with recordings and full transcripts already defaulted on
・Microsoft 365 Copilot activates for every admin if your tenant holds a single paid license, and opting out means building a special security group
・Google's Workspace Intelligence shipped default-on for Gmail, Drive, Chat, and Calendar, with admin controls lagging the live feature by up to 72 hours
・OpenAI disables connectors by default for Enterprise customers but enables them for Business. Same vendor, opposite defaults.

Every default-on feature just transfers governance work from the vendor to you, along with wiretap exposure and e-discovery sprawl that nobody signed up for.

My ask of vendors is simple: ship AI features off by default and give admins an evaluation window measured in weeks, not days. Until that happens, assume the next AI feature is already live in your tenant. Review your configurations like it's a recurring operational task, because it is.

Full piece here: forbes.com/councils/forbestech

 
@forbes@flipboard.com @Forbes@newsie.social @forbestechcncl @RHR_International @depaulu

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

Information and references 📚🧵

Portal of resources about age verification (EFF):
eff.org/issues/age-verification

Everything You Wanted to Know About a Kids’ Social Media Ban (Michael Geist):
michaelgeist.ca/2026/06/everyt

How and Why to Fight Back Against Social Media Bans (EFF):
eff.org/deeplinks/2026/06/how-

Transgender youth 5 times more likely to attempt suicide, study finds (CBC):
cbc.ca/news/canada/prince-edwa

Age Verification Lobby Pushes For Age Verification Checks For VPN Use (Reclaim The Net):
reclaimthenet.org/lobbyists-pr

Reddit User Uncovers Who Is Behind Meta’s $2B Lobbying for Invasive Age Verification Tech (Gadget Review):
gadgetreview.com/reddit-user-u

Firm that verifies mugshots for ChatGPT and Roblox feeds US surveillance apparatus with 269 distinct checks (Cybernews):
cybernews.com/privacy/persona-

Discord says hackers stole government IDs of 70,000 users (Ars Technica):
arstechnica.com/security/2025/

(9/9)

arstechnica.com

Discord says hackers stole government IDs of 70,000 users

As more sites require IDs for user age verification, expect more such breaches to come.

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

Canadians need better privacy protections 🔒🧵

Canadians need better and stronger privacy protections, not less. A ban on social media for children is effectively a mandatory ID checks for all adults.

I hope that you will consider these important risks in your evaluation this week, and that you will favour regulations to make social media safer for everyone instead. Excluding children from social media is a decision that should remain a parent's responsibility, not a government one.

As a Canadian citizen who care deeply for the safety of all Canadians, I thank you for taking the time to read this letter and consider my concerns.

(8/9)

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

This is nothing like showing ID at the liquor store 🪪🧵

Finally, it's important to take note that age verification online is nothing like showing an identification card to be able to purchase alcohol. This often-used comparison is disingenuous.

If we stay within this analogy of the analogue world, then online age verification is more comparable to showing an official identification card at the liquor where the cashier would make thousands of photocopies of it, store some in an unlocked drawer, share some with all other liquor stores worldwide, also share some with grocery stores, newspapers, their friends, and random strangers on the street. Then leave a bunch of copies on the floor, for anyone to grab.

Nobody would accept to show their ID at the liquor store if it was happening that way. But sadly, most people ignore the extent to which data is shared, lost, and stolen online, on a daily basis.

(7/9)

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

Adults would be harmed by this ban 🧑🧵

In addition to the already stated dangers of increasing the risk of identity theft, fraud, devaluation of official documents, attacks on the most vulnerable, discrimination against marginalized groups, and self-censorship, a ban of social media for children would give a free pass for corporate platforms to perpetuate the harm they also currently cause to adults.

All that is harmful to children on social media is also harmful to adults.

Social media are an integral part of modern communication and it has many benefits, but commercial platforms have been exploiting their users for decades, much beyond what our society should deem reasonable.

It is time for the Canadian government to regulate social media, yes. Not by excluding children and teens from it, but by obligating platforms to be responsible in protecting the safety and sanity of its users. It should be more profitable to run a platform that is open, transparent, and healthy for its users than one that is not.

A ban on addictive algorithms and data reselling, strong privacy protections and user controls, mandated transparency and effective moderation, an obligation to implement proven safety measures, and important consequences for platforms that prioritize profits over users' safety would all be much more effective at protecting everyone on social media, including the children.

(6/9)

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

Children would be harmed by this ban 🧒🧵

Despite how it might feel at first glance, a ban of social media for children would actually create new harm for children.

First, many children would try to circumvent the ban, this is already happening in countries with such legislation, like Australia.

Second, children who cannot circumvent the ban might be pushed to darker corners of the web to rebuild their social lives, on worse platforms, without any moderation or safety measures. Moreover, being pushed out of the legal frame, these teens and children might feel less inclined to report any abuses experienced to a trustworthy adult, effectively making the situation much worse.

Then, children living with abusive or unsupportive families could lose their support network overnight. It is quite common for 2SLGBTQ+ teens and children living with families that do not support them to find emotional support in a network of peers online. This is often vital to survival. Losing this support suddenly can have devastating permanent consequences.

(5/9)

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

Lobbyists are influencing policies more than experts and advocates 💰🧵

Unfortunately, there are many groups that are putting pressure on governments all around the world to increase surveillance under the guise of protecting the children. The rapidly growing, for-profit, age assurance industry has all to gain in influencing governments to push for age verification processes and bans of social media for children.

Even Meta has reportedly invested heavily in a network of organisations to discreetly lobby for age verification at the operating system level.

Meanwhile, nonprofit organisations and advocates who genuinely care for the well-being of the public have been warning for years about the dangers of age verification and social media ban legislation, but have much less money and power to influence policies at the government level.

I implore you, as the elected representatives for all Canadians, to consider this threat of corporate influence cautiously in your decisions, to listen to the warnings from advocates and experts in the field, and to prioritize first and foremost the well-being and safety of all Canadians.

(4/9)

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

A ban does nothing to address the harm caused by social media 🧨🧵

The things that harm children on social media also harm adults. A ban of social media for children sadly does nothing to reduce the harm caused by social media, it only reserves it to adult, and postpones it for children.

The addictive and manipulative black-box algorithms, the privacy-intrusive data collection, the harmful violent content and misinformation, are all hurting adults as well.

Moreover, children who do not go around the ban before the restricted age (other implementations have shown that most children will attempt to circumvent the ban) will find themselves completely ill-equipped to protect themselves from social media harm once they come of age, and will be made even more vulnerable by our own legislation claiming to protect them.

A true solution to this is to regulate corporate platforms to forbid addictive algorithms, targeted advertising, intrusive data collection, third-party data sharing, violent content, weak moderation, manipulative tactics, and other abusive mechanisms used by certain platforms to prioritize profits over the safety and sanity of its users.

This would not only help children, but adults and society as a whole as well.

(3/9)

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

Age verification processes are dangerous to Canadians ⚠️🧵

Unfortunately, there is no magical solution: A ban of social media for children necessarily means a requirement to identify every adult using social media. This means that intrusive age-verification processes would have to be put in place by social media platforms, therefore collecting an immense quantity of very sensitive information from every Canadian adult using social media.

This is dangerous in many ways.

First, it means many (if not most) platforms will delegate this task to private for-profit third-party vendors with little to no incentive to protect this information properly. We have already seen data breaches of sensitive information in this process. This would increase the risk of Canadians becoming victims of identity theft and fraud, and would diminish the value of Canadian identification documents over time.

Secondly, this can create a permanent record of legal identities tied to social media accounts. This would endanger users who rely on pseudonymity online for safety, such as victims of domestic violence, trans and gender diverse people (for whom the legal identification might not match the name used on social media), performers using stage names online, and other people that are part of marginalized groups regularly targeted online (women, people of colour, 2SLGBTQ+ people, etc.).

All these vulnerable groups would only be one data breach away from incredible harm with the implementation of mandatory identity checks to access social media.

Furthermore, risking to link every social media account to a legal identity can have a silencing effect for activists, journalists, and whistleblowers. This can lead to self-censorship of topics important to discuss publicly in a free democracy.

(2/9)

@Em0nM4stodon@infosec.exchange

A thread to Stop ID Surveillance from coming to Canada ⛔️🧵

Yesterday, I sent a long letter the Canadian Prime Minister Mark Carney, Culture Minister Marc Miller, and the leaders of all other major federal parties in Canada.

I sent this letter to voice my concerns about the upcoming bill that is planned to be introduced today at 5 p.m. ET, to propose a ban of social media for children, therefore requiring all social media platforms to identify every adults accessing it.

This is a long thread of what I wrote (mute me for one hour if you don't want to see it).

Feel free to copy any parts you want to share in your own letter of opposition sent to your representatives this week.

Here's how to find their contact information: ourcommons.ca/members/en/search

(1/9)

ourcommons.ca

Current Members of Parliament - Members of Parliament - House of Commons of Canada

Current Members of Parliament - Members of Parliament - House of Commons of Canada

@Em0nM4stodon@infosec.exchange

PRIVACY ALERT!
Please boost for reach! 🚨👇

The Canadian government is planning
to introduce a bill on Wednesday, June 10th, to mandate identity surveillance of every adult using social media in Canada! 👁️‍🗨️

globalnews.ca/news/11894610/ca

A ban on social media for children
does nothing to reduce the harm caused by commercial social media. Instead, it means mandatory ID scans for every adult using social media.

We must stop this authoritarian proposal,
and demand our government focuses instead on reducing the harm for everyone using social media.

It has been explained by experts over and over that bans of social media are shortsighted lazy measures that do not help in the end, but in fact harm everyone, including the children.

Stop ID surveillance in Canada! ✊⛔️

Contact your MP and our Prime Minister TODAY to voice your opposition. Here's where to find their contact information: ourcommons.ca/members/en/search

If you aren't aware of this issue yet, here's more information on age verification: eff.org/issues/age-verification

eff.org

Age Verification and Age Gating: Resource Hub

Age verification (or age-gating) laws generally require online services to check, estimate, or verify all users’ ages—often through invasive tools like ID checks, biometric scans, or other dubious “age estimation” methods—before granting them access to certain online content or services.  Governments in the U.S. and around the world are increasingly adopting these restrictive measures in the name of protecting children online. But in practice, these systems create dangerous new forms of surveillance, censorship, and exclusion.  Technologically, the age verification process can take many forms: collection and analysis of government ID, biometric scans, algorithmic or AI-based behavioral or user monitoring, digital ID, the list goes on. But no matter the method, every system demands users hand over sensitive and immutable personal information that links their offline identity to their online activity. Once that valuable data is collected, it can easily be leaked, hacked, or misused. (Indeed, we’ve already seen several breaches of age verification providers.) EFF has long warned against age-gating the internet. Age verification technology itself is often inaccurate and privacy-invasive. These restrictive mandates strike at the foundation of the free and open internet. They are tools of censorship, used to block people from viewing or sharing information that the government deems “harmful” or “offensive.” And they create surveillance systems that critically undermine online privacy, chill access to vital online communities and resources, and burden the expressive rights of adults and young people alike. EFF.org/Age: A Resource to Empower Users Age-gating mandates are reshaping the internet in ways that are invasive, dangerous, and deeply unnecessary. But users are not powerless! We can challenge these laws, protect our digital rights, and build a safer digital world for all internet users, no matter their ages. This resource hub is here to help—so explore, share, and join us in the fight for a better internet.

@knoppix95@mastodon.social
@Em0nM4stodon@infosec.exchange

PRIVACY ALERT!
Please boost for reach! 🚨👇

The Canadian government is planning
to introduce a bill on Wednesday, June 10th, to mandate identity surveillance of every adult using social media in Canada! 👁️‍🗨️

globalnews.ca/news/11894610/ca

A ban on social media for children
does nothing to reduce the harm caused by commercial social media. Instead, it means mandatory ID scans for every adult using social media.

We must stop this authoritarian proposal,
and demand our government focuses instead on reducing the harm for everyone using social media.

It has been explained by experts over and over that bans of social media are shortsighted lazy measures that do not help in the end, but in fact harm everyone, including the children.

Stop ID surveillance in Canada! ✊⛔️

Contact your MP and our Prime Minister TODAY to voice your opposition. Here's where to find their contact information: ourcommons.ca/members/en/search

If you aren't aware of this issue yet, here's more information on age verification: eff.org/issues/age-verification

eff.org

Age Verification and Age Gating: Resource Hub

Age verification (or age-gating) laws generally require online services to check, estimate, or verify all users’ ages—often through invasive tools like ID checks, biometric scans, or other dubious “age estimation” methods—before granting them access to certain online content or services.  Governments in the U.S. and around the world are increasingly adopting these restrictive measures in the name of protecting children online. But in practice, these systems create dangerous new forms of surveillance, censorship, and exclusion.  Technologically, the age verification process can take many forms: collection and analysis of government ID, biometric scans, algorithmic or AI-based behavioral or user monitoring, digital ID, the list goes on. But no matter the method, every system demands users hand over sensitive and immutable personal information that links their offline identity to their online activity. Once that valuable data is collected, it can easily be leaked, hacked, or misused. (Indeed, we’ve already seen several breaches of age verification providers.) EFF has long warned against age-gating the internet. Age verification technology itself is often inaccurate and privacy-invasive. These restrictive mandates strike at the foundation of the free and open internet. They are tools of censorship, used to block people from viewing or sharing information that the government deems “harmful” or “offensive.” And they create surveillance systems that critically undermine online privacy, chill access to vital online communities and resources, and burden the expressive rights of adults and young people alike. EFF.org/Age: A Resource to Empower Users Age-gating mandates are reshaping the internet in ways that are invasive, dangerous, and deeply unnecessary. But users are not powerless! We can challenge these laws, protect our digital rights, and build a safer digital world for all internet users, no matter their ages. This resource hub is here to help—so explore, share, and join us in the fight for a better internet.

@ai6yr@m.ai6yr.org · Reply to AI6YR Ben

(considering *I* know how to track these... and have considered writing software to see who/what is constantly in the neighborhood or just driving by... it' not difficult to see how a company would attempt to commercialize this)

"...SignalTrace “bridges license plate recognition data with sensor-captured device identifiers—such as those from mobile phones, Bluetooth wearables, and vehicle systems—to create a unique, trackable ‘electronic fingerprint’ for investigative use,” according to a product sheet describing the tool, written by surveillance company Leonardo, which advertises SignalTrace.

The sort of data Leonardo says SignalTrace can sweep up includes the RFID tags in key cards and pet microchips; devices with Bluetooth such as wireless headphones, fitness trackers, and mobile phones; components of a car like tire pressure sensors and infotainment systems; and Wi-Fi sources such as vehicle hotspots and laptops, according to the product sheet..."

@ai6yr@m.ai6yr.org
@freezenet@noc.social
@Em0nM4stodon@infosec.exchange

I'm so done with Apple.

We could have had nice things.
But no.
Instead we get dystopia.

I shouldn't be terrified of every software update pushed on the devices I bought.

@simsus@social.tchncs.de
@eteryu@infosec.exchange

Cześć, Fediverse. Jestem Eteryu. Pokazuję, jak krok po kroku odzyskiwać cyfrową prywatność i skutecznie odcinać algorytmy śledzące na smartfonach, bez ślepej wiary w marketingowe zapewnienia korporacji.

Interesuje mnie cyberbezpieczeństwo z perspektywy praktyka. Na co dzień dekonstruuję popularne modele zaufania, tropię ukrytą telemetrię i sprawdzam, co faktycznie dzieje się pod maską współczesnego oprogramowania. Zamiast godzić się na gotowe kompromisy, utwardzam systemy mobilne, izoluję inwazyjne aplikacje i kontroluję ruch sieciowy u źródła. Swoje testy, techniczne śledztwa oraz praktyczne przewodniki po higienie cyfrowej publikuję na blogu: eteryu.space/

Cieszę się na merytoryczne dyskusje i wymianę doświadczeń z tutejszą społecznością.

eteryu.space

Eteryu.space | Odzyskaj cyfrową prywatność

<ul> <li> <div class="post-header"> <a href="/cyfrowa-higiena-bez-podgladaczy-jak-atwo-odciac-algorytmy-i-zabezpieczyc-zdjecia/">Cyfrowa higie...

@mysk@mastodon.social

Introducing Loupe, our latest privacy app for iOS. Discover what apps can learn about you just by reading data your iPhone already exposes, such as your languages, installed apps, device sensors, and much much more

Loupe is free, private, and open source. Give it a try 👇

apps.apple.com/app/id6766152470

Link to source code:

github.com/mysk-research/loupe

Thumbnail not available
ALT text

Banner for Loupe

@ai6yr@m.ai6yr.org

Wired: Meta Silently Added Face-Recognition Code for Its Smart Glasses to Millions of Phones

Code reviewed by WIRED uncovered an unreleased face-recognition system embedded in Meta’s smart glasses platform. It’s designed to identify people via biometric data stored on users’ phones.

wired.com/story/meta-smart-gla

Thumbnail not available
ALT text

Meta Silently Added Face-Recognition Code for Its Smart Glasses to Millions of Phones Code reviewed by WIRED uncovered an unreleased face-recognition system embedded in Meta’s smart glasses platform. It’s designed to identify people via biometric data stored on users’ phones.

@mysk@mastodon.social

Introducing Loupe, our latest privacy app for iOS. Discover what apps can learn about you just by reading data your iPhone already exposes, such as your languages, installed apps, device sensors, and much much more

Loupe is free, private, and open source. Give it a try 👇

apps.apple.com/app/id6766152470

Link to source code:

github.com/mysk-research/loupe

Thumbnail not available
ALT text

Banner for Loupe

@meridian@mastodon.com.pl

Prywatność i cyberbezpieczeństwo to nie są hobbystyczne fanaberie dla ludzi w foliowych czapeczkach. Skompromitowane urządzenie mobilne to bezpośrednie zagrożenie dla Twojego życia osobistego, finansów i spokoju psychicznego.

Właśnie ruszyłem ze swoim blogiem, a to mój pierwszy wpis:
🔗 meridian.bearblog.dev/droga_do

Opisuję w nim historię z ukrytym korporacyjnym MDM na moim telefonie i to, jak techniki Incident Response oraz przejście na GrapheneOS pozwoliły mi odzyskać kontrolę.

To mój debiut, dlatego bardzo zależy mi na Waszym feedbacku. Co myślicie o tym tekście? Dajcie znać w komentarzach, czy taka tematyka Was interesuje i czy chcecie kolejne wpisy o konfiguracji i hardeningu GrapheneOS! 🛡️📱

meridian.bearblog.dev

Jak okiełznałem system z MDM. Moja droga do GrapheneOS

W świecie cyberbezpieczeństwa często rozmawiamy o „modelach zagrożeń” (Threat Models) w sposób czysto teoretyczny. Analizujemy tabelki, czytamy dokumentację ...

@reiver@mastodon.social

A decade or two ago — a certain type of (state) "professional" was excited by the idea that you could track someone using public social-media data across multiple social-networks.

And, even improve the tracking using "private" data.

You should assume that not only does this technology exist now, but it is common.

The people who would use this against your interests won't care about robots-txt files, nobot hash-tags, or Mastodon name-spaces.

Act accordingly.

@jonsnow@mastodon.online
@Em0nM4stodon@infosec.exchange

Last year for Pride I wrote a series
of articles at the intersection of privacy and LGBTQ+ experiences :rainbow_heart: 🔒

Data privacy is important for everyone. But for some marginalized populations, data privacy is indispensable for social connection, access to information, and physical safety.

Here are 3 articles published with Privacy Guides last year discussing this topic from different angles:

The Importance of Data Privacy For The Queer Community

Stay Safe, but Stay Connected

Queer Dating Apps: Beware Who You Trust With Your Intimate Data

privacyguides.org

Queer Dating Apps: Beware Who You Trust With Your Intimate Data

At the intersection of data privacy and LGBTQ+ experiences, it's inevitable to talk about queer dating apps. Unfortunately, most are horrible for data privacy.

@dmarti@federate.social · Reply to Dan Gillmor

@dangillmor And somehow this is the same company that Mozilla decided to partner with on ad tracking in the browser—now a project with Google and Apple involved too, to drive ad money away from legit sites and toward search, social, and app stores.

monopoly-report.com/podcast/ep

monopoly-report.com

Episode 74: The Attribution Cartel: Why “Privacy-Safe” is NOT what it’s made up to be

Don Marti joins Alan Chapell to unpack the hidden risks behind the push for industry standards for “privacy-safe”  ad attribution, the myth of privacy-preserving tech, and how big platforms may be reshaping the future of digital advertising. The Chapell Regulatory Insider is at https://chapellreport.substack.com/ Don Marti may be found at: https://aloodo.com/  See Don Marti’s recent AdExchanger piece at https://www.adexchanger.com/data-driven-thinking/what-happens-when-the-attribution-cartel-meets-advertisings-halo-effect/   Additional discussion re: the problems with PETs for advertising https://privacy-daily.com/news/2025/06/10/PrivacyEnhancing-Technologies-Are-Not-a-Silver-Bullet-PEPR-Told-2506100010 https://rjionline.org/news/the-traffic-and-revenue-crisis-for-news-is-a-symptom-of-big-techs-economy-wide-trust-collapse/  https://rjionline.org/news/big-tech-is-squeezing-advertising-jobs-and-companies/  https://rjionline.org/news/big-techs-economic-takeover-can-be-beat/  https://rjionline.org/news/big-tech-runs-counter-to-journalism-values-so-why-is-the-news-industry-helping-tech-take-over/  Takeaways Privacy-focused users are often the most valuable customers, challenging traditional ad tech assumptions about measurability. Attribution is fundamentally about linking ad exposure to outcomes, but current models often prioritize simplicity over accuracy. “Privacy-preserving” systems frequently focus on mathematical guarantees that don’t align with real-world privacy harms like discrimination or deception. Proposed attribution standards may unintentionally increase surveillance incentives by enabling fraud and data laundering. Fraud in attribution systems can reward actors who intercept users right before purchase, distorting true performance signals. Big tech companies may benefit from attribution systems that reinforce their own ad recommendations, reducing competition. The “halo effect” shows ads perform better in trusted, premium environments, but current systems undervalue this dynamic. A shift toward cheap, commoditized ad placements weakens both brand equity and publisher sustainability. The so-called “attribution cartel” is defined by systems that avoid user consent and bypass opt-out mechanisms. Effective privacy regulation should focus on real-world harms rather than technical implementation details. Chapters 00:00 Intro & What Don Marti Has Been Working On 01:18 The “Marti Paradox” 02:52 What Attribution Really Means 03:35 The Broken State of Attribution Today 07:32 Complexity, Perception & Industry Behavior 08:21 The Problem with “Privacy-Preserving” Tech 11:54 Big Tech Incentives & Centralization 16:17 The Halo Effect & Ad Effectiveness 17:01 Commodification vs Sustainable Advertising 21:28 Attribution Fraud Explained 23:49 Data Laundering Through Attribution Systems 26:09 The “Attribution Cartel” Defined 29:17 W3C, Standards & Industry Power Dynamics 32:29 Alternative Approaches (AdMap) 37:03 What Good Privacy Regulation Looks Like 40:56 The Future of Attribution 43:20 What Industry Stakeholders Can Do 45:00 Rethinking Privacy Harms Learn more about your ad choices. Visit megaphone.fm/adchoices

@Em0nM4stodon@infosec.exchange

Last year for Pride I wrote a series
of articles at the intersection of privacy and LGBTQ+ experiences :rainbow_heart: 🔒

Data privacy is important for everyone. But for some marginalized populations, data privacy is indispensable for social connection, access to information, and physical safety.

Here are 3 articles published with Privacy Guides last year discussing this topic from different angles:

The Importance of Data Privacy For The Queer Community

Stay Safe, but Stay Connected

Queer Dating Apps: Beware Who You Trust With Your Intimate Data

privacyguides.org

Queer Dating Apps: Beware Who You Trust With Your Intimate Data

At the intersection of data privacy and LGBTQ+ experiences, it's inevitable to talk about queer dating apps. Unfortunately, most are horrible for data privacy.

@darkjstr@infosec.exchange

Hinge database allegedly for sale.

Actor "nilojeda" claims 8M+ records: email, password_hash, oauth_subject_hash, phone_hash, DoB, geolocation. A sample PoC is publicly available in the thread.

$400, accepts crypto. No statement from Hinge yet.

If you use Hinge: rotate password, revoke OAuth sessions, enable 2FA.#DataBreach

@rohini@mastodon.social

Yours truly speaking online at the Global Summit on Tech-facilitated Gender-based Violence on 9 June.

Thumbnail not available
ALT text

Promotional graphic for the 2026 Global Summit on Tech-Facilitated Gender-Based Violence, taking place June 9. The panel is titled “Balancing Privacy and Protection in the Digital World.” Four speaker cards are shown: Lyndsey Dearlove, Global Director of Operations at The NO MORE Foundation, moderator; Barsha Chakraborty, digital rights and gender justice advocate; Rohini Lakshané, technologist and interdisciplinary researcher; and Tsitsi Matekaire, Director of Regions at Equality Now. Text reads: “Register at nomore.org/techsummit.” The summit is delivered by NO MORE in partnership with UN Women and Equality Now.

@simsus@social.tchncs.de
@jsjoshua@esq.social

Digital driver's licenses have been around for a while now. When they first came out, privacy groups expressed concerns. I haven't heard much since then, though, and NY just rolled out their version of it.

Anyone have any recommended resources (recent) or thoughts about the current benefits or risks of downloading an app and uploading my drivers license into it?

@privacyguides@neat.computer
@vinterkarusell@saga.garden

Hi! 👋

I'm a producer with a strong passion for . Music‑wise I bend towards , while photography stretches from drone/aerial shots to architecture and everyday stills.

A big believer in , digital independence, and owning your own space online, powered by and .

I self-host my own corner of the internet via YunoHost.
It's part of my commitment to decentralization and taking control of my digital footprint.

When I'm not crafting electronic noise or framing pixels, I'm reading terms and conditions of whatever just to feel something. 😁

Also, I get paid to talk. Not paid a lot, mind you—I just talk a lot.

Feel free to connect! ✨

📣

@privacynews@mstdn.plus
@xabd@mastodon.social

optimizerDuck is a free and open-source Windows optimization tool focused on privacy, debloating, and performance improvements.

It can disable telemetry, remove AppX bloatware, manage startup/services, apply gaming tweaks, clean disks, and optimize power settings, all from one portable app.

Includes backups, restore point reminders, one-click revert options, and tweak safety ratings.

👉 digitalescapetools.com/tools/t

Thumbnail not available
ALT text

Screenshot of optimizerDuck showing its logo, project overview, version badges, download stats, and Windows optimization/privacy-focused branding.

Thumbnail not available
ALT text

Screenshot of optimizerDuck showing its branding, feature badges, and a dark-themed Windows optimization dashboard with privacy tweaks, performance settings, and debloating tools.

@_elena@mastodon.social

🚨 New post alert 📝

A deep dive into with some fascinating findings: candid statements about their motives, a Greta Thunberg connection, potential AI plans (!!!)

Why write about it again? I still had so many questions after publishing my first article.

I spent 3 weeks watching every interview I could find and connecting the dots.

I hope you'll enjoy this piece:

🔗 : blog.elenarossini.com/the-unto

blog.elenarossini.com

The Untold Story About W Social: Unconventional Beginnings, Strategic Pitches and Conflicting Signals

A deep dive into the origin story of W Social, an analysis of the strategic arguments they have been using to appeal to government officials, media companies and advertisers... and the discussion of conflicting signals they have been sending

@privacysafe@privacysafe.social · Reply to PrivacySafe

@GrapheneOS No Ads, No Spyware, No Manipulation. Just honest timelines and reach without all the noise of social media. Great settings, export and delete your data, and filter out content you don't want to see. Try it now FREE and get the app later! psafe.ly/social

Thumbnail not available
ALT text

PrivacySafe Social timeline

Thumbnail not available
ALT text

PrivacySafe Social menu

Thumbnail not available
ALT text

PrivacySafe Social news feed

Thumbnail not available
ALT text

PrivacySafe Social about page

@_elena@mastodon.social

🚨 New post alert 📝

A deep dive into with some fascinating findings: candid statements about their motives, a Greta Thunberg connection, potential AI plans (!!!)

Why write about it again? I still had so many questions after publishing my first article.

I spent 3 weeks watching every interview I could find and connecting the dots.

I hope you'll enjoy this piece:

🔗 : blog.elenarossini.com/the-unto

blog.elenarossini.com

The Untold Story About W Social: Unconventional Beginnings, Strategic Pitches and Conflicting Signals

A deep dive into the origin story of W Social, an analysis of the strategic arguments they have been using to appeal to government officials, media companies and advertisers... and the discussion of conflicting signals they have been sending

@somoszorro@mastodon.social

@thenewoil this pattern (apps sharing user data without consent) is exactly what pushed two Spanish gay founders to build Zorro - a GBTIQ+ dating app launching June 15 in Madrid. EU-only servers, no data selling, no third-party data sharing. Worth watching: waitlist.somoszorro.com/?utm_s

waitlist.somoszorro.com

Zorro · Waitlist

Únete a la waitlist de Zorro. Privacidad primero. 200 Premium anuales de regalo para los primeros.

@vinterkarusell@gotosocial.xyz

Hi! 👋

I'm a #music producer with a strong passion for #photography. Music‑wise I bend towards #EDM, while photography stretches from drone/aerial shots to architecture and everyday stills.

A big believer in #privacy, digital independence, and owning your own space online, powered by #FOSS and #Linux.

I self-host my own corner of the internet using GoToSocial.
It's part of my commitment to decentralization and taking control of my digital footprint.

When I'm not crafting electronic noise or framing pixels, I'm reading terms and conditions of whatever just to feel something. 😁

Also, I get paid to talk. Not paid a lot, mind you—I just talk a lot.

Feel free to connect! ✨

#Introduction 📣 V3

@fairtechsummit@mastodon.social

We're live ! The website announcing the Fair Tech Summit Europe for 2026 is online: fairtechsummit.org/ It will take place in Luxembourg on 6 October 2026 and will be for everyone in Europe who's actively building open, ethical and independent technology.

Save the date!

Thumbnail not available
ALT text

A dark navy social card matching the Fair Tech Summit Europe website. Top-left: the Fair Tech Summit hexagonal mark on a white card, with "FAIR TECH SUMMIT" in mint mono text and "EUROPE · LUX · 06.10.26" below in muted white. A mint pill reads "06 OCT 2026", followed by "LUXEMBOURG · ONE DAY · CURATED" in white. Headline in three lines: "WE'RE LIVE." in mint, then "LUXEMBOURG." and "06 OCTOBER 2026." in white. Footer line centred: "06 OCT 2026 · LUXEMBOURG · FAIRTECHSUMMIT.ORG".

@aral@mastodon.ar.al

“This is an important public service announcement related to your right to privacy … We the people have 1 day 16 hours 33 minutes 13 seconds to take action and influence this outcome.
…
For now, your encrypted messages have a lock on them.

Only you, and the person you're talking to, hold the key. Not the app. Not the company. Not the government. You probably don't think about it. That's the whole point — it just works.

Until, possibly, the end of this summer.

WHAT BILL C-22 WOULD DO

Every messaging app in Canada would be required to build a second key.”

Another effort to destroy end-to-end encryption, and thus your privacy, this time from Canada.

dontsurveil.me/c22.html

dontsurveil.me

Canada is about to end private digital conversation — Bill C-22

Bill C-22 would force every messaging app in Canada to build a backdoor — and track all your activity for one year. Apple says no. Signal says they'll leave.

@privacyguides@neat.computer
@legendary_creeper@mas.to

I'm currently preparing legal action against multiple platforms in the Minecraft scene, this includes: MC servers, website operators and hosting platforms like @modrinth

They all violated the GDPR in one or multiple ways, and didn't care to resolve the issue or answer as I reached out to them multiple times.

This already cost and will cost me a lot of time and effort.

If you want and are able to help out, please reach out to me.

@jospoortvliet@fosstodon.org
@cyd@infosec.exchange

We're happy to announce today the release of Cyd for Mobile! 📲🐦️

If you have an account on Bluesky, you can use Cyd's new mobile app to easily and automatically clean up your data.

The app backs up and deletes your old posts, likes, and other data, while leaving what you actually want people to see when they look up your account.

Why should everything you post on social media stay online forever? It's your data, it should be your choice!

More on Cyd for Mobile here: lockdown.systems/cyd-for-mobil

lockdown.systems

Cyd for Mobile: Delete your old Bluesky posts, except for what you want to keep

Why should everything you post to social media stay online, and public, forever?

@lockdownsystems@infosec.exchange

Mastodon users may not need this, but Bluesky users do! 🦋

If you or someone you know also have a Bluesky account, you might want to look at @cyd to facilitate post deletion and good data minimization practices.

We're happy to announce today a new way to do this easily: Cyd for Mobile! 🐦️✨

lockdown.systems/cyd-for-mobil

Why should everything you post on social media stay online, and public, forever?

It's *your* data! You should have the power to keep it, move it, and delete it as you please.

lockdown.systems

Cyd for Mobile: Delete your old Bluesky posts, except for what you want to keep

Why should everything you post to social media stay online, and public, forever?

@Luchador@thecanadian.social

DontSurveil.Me has put together a great explainer on Bill C-22.

Canadians need to pay attention.

Expanding surveillance powers, retaining metadata, and weakening encryption all threaten privacy, free expression, civil liberties, and digital rights.

If we care about privacy, digital rights, and a free society, now is the time to speak up, contact MPs, and push back before this becomes law.

Learn more: dontsurveil.me/c22.html

dontsurveil.me

Canada is about to end private digital conversation — Bill C-22

Bill C-22 would force every messaging app in Canada to build a backdoor — and track all your activity for one year. Apple says no. Signal says they'll leave.

@Andreas_Sturm@mastodon.social · Reply to Digitalcourage

@digitalcourage Im Verkehrsverbund Rhein Sieg gibt es die eezy app / eezy.nrw, die jede Fahrt mit dem ÖPNV zur personifizierten Bewegungserfassung macht, wenn man entspr. ein- und auscheckt auf den Meter genau - was das GPS halt so hergibt.

Wahrscheinlich gibt es solche apps auch in anderen Verkehrsverbünden?!

@Luchador@thecanadian.social

DontSurveil.Me has put together a great explainer on Bill C-22.

Canadians need to pay attention.

Expanding surveillance powers, retaining metadata, and weakening encryption all threaten privacy, free expression, civil liberties, and digital rights.

If we care about privacy, digital rights, and a free society, now is the time to speak up, contact MPs, and push back before this becomes law.

Learn more: dontsurveil.me/c22.html

dontsurveil.me

Canada is about to end private digital conversation — Bill C-22

Bill C-22 would force every messaging app in Canada to build a backdoor — and track all your activity for one year. Apple says no. Signal says they'll leave.

@lockdownsystems@infosec.exchange

We're happy to announce today that we are part of the Fund Internet Freedom campaign led by @torproject and Funding the Commons, with a coalition of 10 other projects sharing our values for privacy, public access, and digital freedom 🧅💜

If you would like to support projects in the coalition, you can donate here: internetfreedom.torproject.org/

To learn more about the campaign, check this announcement from The Tor Project: blog.torproject.org/fund-inter

Thank you for supporting privacy and internet freedom with us! ✊🐢

blog.torproject.org

A new way to fund internet freedom | Tor Project

Tor is strongest when the broader internet freedom ecosystem is healthy. A coalition of privacy, internet freedom, cryptocurrency and open-source ecosystems, led by the Tor Project and Funding the Commons, is supporting critical digital infrastructure with a new participatory funding campaign.

@brian_greenberg@infosec.exchange

🥶 A contractor for CISA posted AWS GovCloud admin keys to a public GitHub repo! The repo was named "Private-CISA." Not an accident, the contractor actively disabled GitHub's built-in secret scanner to do it. That's a choice. Not a typo, not a misconfiguration. Someone turned off the guardrail and then stored plaintext credentials in a file called "importantAWStokens." That should make every security leader lose their 💩 AND the exposed keys stayed valid for 48 hours after CISA was notified. The agency responsible for protecting the country's critical infrastructure took two days to rotate credentials sitting in a public repo. 🤬 One researcher called this "the worst leak I've witnessed in my career." The exposed files included credentials to CISA's internal software build environment. Anyone who found those keys first could have backdoored the packages CISA builds and deploys. Every new build would carry that backdoor forward. CISA has lost nearly a third of its workforce since January. The oversight that might have caught this sooner is gone.

Two questions worth taking back to your own team:
・ When did you last verify that secret scanning is actually enabled across every repo your contractors touch?
・ If you got the call today that credentials were public, how long would it take to rotate them?

krebsonsecurity.com/2026/05/ci

@xabd@mastodon.social
@jmj@social.lol

Hi, I’m Joanna! I’ve been here a while but I don’t think I’ve made a proper .

I’m a 40 year-old woman. I was raised in and have lived in the since 2016. I am an who enjoys , , , , , , and .

I believe everyone deserves access to , , , and .

If any of that sounds cool, let’s be friends!

PS

@Luchador@thecanadian.social

DontSurveil.Me has put together a great explainer on Bill C-22.

Canadians need to pay attention.

Expanding surveillance powers, retaining metadata, and weakening encryption all threaten privacy, free expression, civil liberties, and digital rights.

If we care about privacy, digital rights, and a free society, now is the time to speak up, contact MPs, and push back before this becomes law.

Learn more: dontsurveil.me/c22.html

dontsurveil.me

Canada is about to end private digital conversation — Bill C-22

Bill C-22 would force every messaging app in Canada to build a backdoor — and track all your activity for one year. Apple says no. Signal says they'll leave.

@dima@dol.social

Gave my son his first serious gift a few days ago.

A @protonprivacy "Born Private" activation code.

While most people are creating Gmail accounts for their newborns, I decided to start him off with actual privacy from day one.

A bit dramatic? Maybe. But in 15–20 years when he asks "Dad, why doesn’t my email spy on me?" — I'll just smile and say "You’re welcome".

Sometimes the best gifts are the ones they’ll only appreciate much later.

Thumbnail not available
ALT text

A person’s hand holding a Proton Mail ‘Born Private’ gift certificate. The card shows the Proton Mail logo, a reserved @proton.me email address, a large QR code and activation instructions. In the background there are colorful party balloons, suggesting a baby celebration.

@unredacted@unredacted.social
@privacyguides@neat.computer
@sylvie@gabriel.havfruefestning.com
@brian_greenberg@infosec.exchange

I attended the AITP Chicago Security SIG tonight at RSM and left with one clear takeaway: a $200 device called Flipper Zero can clone your building access badge and bypass the physical security your organization worked so hard to set up. FBI Chicago Intelligence Analysts and an InfraGard board member explained how these devices work and where organizations are vulnerable. The room was full of security professionals, many of whom had that familiar look, realizing a threat they thought was unlikely is actually much closer to home.
Here are a few key points from tonight:
・ You can buy Flipper Zero on Amazon, and teenagers are posting demo videos on YouTube. If your physical security plan assumes attackers need special equipment, that assumption is no longer true.
・ Most enterprise security programs barely address RF-based attacks on access control systems. We invest heavily in endpoint protection and network monitoring, but the badge reader by the server room often gets overlooked.
・ Mitigation is practical. Encrypted credentials and multi-factor physical access are real solutions. Most organizations just haven’t made them a priority because the threat seemed remote.

If you’re a CISO or CIO and haven’t reviewed your physical access controls for RF-based attacks, now is a good time to add it to your to-do list.
Thank you to AITP Chicago, the FBI, InfraGard, and RSM for a great discussion.

aitpchicago.com/event-6680905

@brian_greenberg@infosec.exchange

The big security conferences have their place. You get the keynotes, the vendor expo, and the sponsored happy hours. What you don't always get is a straight conversation with someone who actually broke something recently and wants to talk about it.

That's why I'm going to BSides312 this weekend.

Saturday, May 16th, at the Irish American Heritage Center in Chicago. Two talk tracks, 15 speakers, a CTF, a lockpicking village, and an after-party. Community-run, non-profit, built for practitioners by practitioners.

If you're in Chicago and work in security, this is where you should be this weekend. Come find me.

bsides312.org

#312 @bsides312 @bsides312@bird.makeup

bsides312.org

BSides312 2026 — Chicago's Security BSides Hacking Conference | May 16

BSides312 is Chicago's Security BSides event — a non-profit hacker & cybersecurity conference in Chicago, IL. May 16, 2026 at the Irish American Heritage Center.

@Em0nM4stodon@infosec.exchange · Reply to Em :official_verified:

If you do not want to fill the personal information in the petition form to oppose Bill C-22, you can simply find your representative's address here and email them directly: ourcommons.ca/members/en/search

ourcommons.ca

Current Members of Parliament - Members of Parliament - House of Commons of Canada

Current Members of Parliament - Members of Parliament - House of Commons of Canada

@Em0nM4stodon@infosec.exchange
@brian_greenberg@infosec.exchange

Though Google Cloud Next in Las Vegas was a couple weeks ago, I'm still working through it and trying to process everything I learned there. Three days, 32,000 attendees, 260 product announcements. One cool stand out...
Google shipped an entire agent accountability infrastructure at this conference. Every AI agent now gets a cryptographic ID and an auditable action trail tied to a defined authorization policy. They built anomaly detection that flags unusual agent reasoning in real time and maps it back to the source.
You build that when you're expecting things to go wrong at scale.
GE Appliances is deploying 800 AI agents across manufacturing and supply chain right now. That's operational continuity with autonomous software making decisions without a human in the loop.
Every enterprise leader needs to answer one question the technology doesn't answer for you: when an agent makes a decision that costs money or creates legal exposure, who owns it?
I'm looking forward to diving deeper into Gemini Enterprise and Chrome Enterprise. The Chrome Enterprise shadow AI reporting shows you every unsanctioned AI tool your employees are already using. You can't govern what you can't see.

cloud.google.com/blog/topics/g

@google @googlecloud @googlecloudsec

cloud.google.com

Google Cloud Next 2026 Wrap Up | Google Cloud Blog

A whirlwind recap of Google Cloud Next 26, including a synopsis of over 250 product, customer and ecosystem announcements.

@snarklestiltzkin@c.im
@codebuzz@indieweb.social · Reply to Xavier Ashe :donor:

@Xavier Librewolf does some smart protection. Since cookies are less available, companies use OS, browser, screensize, location, and so on.. to fingerprint you (the new cookie).

Librewolf can counter a lot of that. I guess in this case, it tells me for whom Vercel is really playing. I will fight against or ban any company that limits the internet in these ways

**coughs**cloudflare**cough**

Time to stand up and make internet decent again.

@mattsimpson@infosec.exchange

"Canada’s Bill C-22 Is a Repackaged Version of Last Year’s Surveillance Nightmare" Canadians deserve better, so stop with it already.

eff.org/deeplinks/2026/05/cana

Awesome HN comment from Embarrassed help:
Both the mandatory data retention and encryption backdoor requirements will cause encrypted messaging services like Signal, WhatsApp, iMessage, Matrix, and others to block both Canadians and Canadian businesses from their services.

If you live in Canada or are impacted by this legislation, then you need to tell both your MP and the Minister of Public Safety of Canada to reject this legislation.

The Canadian Civil Liberties Association (CCLA) published information about Bill C-22 here just over a week ago:
ccla.org/privacy/coalition-to-

The blanket metadata retention and encryption backdoor requirements of Bill C-22 are illegal in the European Union.

Multiple groups have made easy to use tools for sending your MP and (other members of government) an email about rejecting this terrible legislation in its current form:

* The Internet Society's tool:
internetsociety.org/our-work/i

* OpenMedia's messaging tool: action.openmedia.org/page/1887

* ICLM's messaging tool:
iclmg.ca/stop-c-22/

I would also recommend emailing the Minister of Public Safety of Canada (Gary Anandasangaree: gary.anand@parl.gc.ca) and the Minister of Justice (Sean Fraser: sean.fraser@parl.gc.ca).

iclmg.ca

Stop Bill C-22 and its expansion of the surveillance state! - International Civil Liberties Monitoring Group

Since you’re here… … we have a small favour to ask. Here at ICLMG, we are working very hard to protect and promote human rights and civil liberties in the context of the so-called “war on terror” in Canada. We do not receive any financial support from any federal, provincial or municipal governments or political …

@sprockxyz@pnw.zone

Hello, ! My name is Soméo (rhymes with "mayo") and I use he/him. I'm a trans guy living in :cascadia: with my two . I'm relatively new here— I first joined Fedi some time last year as I've developed a hyper-fixation on and . I don't have any connections on Fedi with anyone I knew beforehand, so I'm mostly here to lurk and discover cool people; I'm also still working out what I'd like to post.

@Em0nM4stodon@infosec.exchange

Privacy rights aren't a luxury, they are fundamental to democracy, to safety, and to so many other human rights.

When they attack your privacy rights,
they attack all of this, they attack your humanity.

Do not let them.
Fight back for your human rights.

@Em0nM4stodon@infosec.exchange

Anyone asserting encryption is a tool for crime is either painfully misinformed or is attempting to manipulate legislators to gain oppressive power over the people.

Encryption is not a crime,
encryption is a shield.

Encryption protects you from cyberattack, identity theft, discrimination, doxxing, stalking, sexual violence, physical harm, and much more.

For safety, for privacy, for democracy, and for all our human rights, it's critical that we defend our right to encryption.

privacyguides.org/articles/202

privacyguides.org

Encryption Is Not a Crime

Encryption is not a crime, encryption protects us all. Encryption, and especially end-to-end encryption, is an essential tool to protect everyone online. Attempts to undermine encryption are an attack to our fundamental right to privacy and an attack to our inherent right to security and safety.

@lockdownsystems@infosec.exchange

Hello Fediverse!

We are pleased to be joining the Federated Universe today, with this new Mastodon account! 🐢 :mastodon:

We are Lockdown Systems,
a worker-owned collective building freedom and privacy technologies to inform the public, fight surveillance, and empower people to take back control of their own data.

Our projects include:
🐦️ @cyd
🧅 OnionShare
🧊 ICE Detention Map
🥚 And more to come!

To learn more about our collective, you can visit our website at: lockdown.systems

We're excited to start sharing our work with the Fediverse! 🎉

lockdown.systems

Lockdown Systems

A worker-owned collective building freedom and privacy tech, empowering people to take control of their own data and protect themselves from unwanted surveillance

@freddy@social.lol

In the 1960s, if you wanted to surveil one person, you had to hire someone else to bug them or follow them. Today, we surveil everyone by default; you just have to tap into the data collected by the spies in their pockets (smartphones), on their wrists and fingers (smart watches and rings), their work tools (laptops), and in the public sphere (CCTV cameras) – you’ll have more on any person than the Stasi could ever dream of.

aeon.co/essays/things-have-job

@someguy@beige.party

sucks. The just passed a law creating a of . I don't even have the words to describe just how incredibly cruel and fucked up this is.

Not only is this the first time the state has tried this, medical will be collected (major HIPAA violation), and the database will be publicly available.

Arguably, this is the worst and most dangerous anti-trans law in the country and jeopardizes the , privacy, and well being of trans people.

theneedlenews.com/2026/05/tenn

theneedlenews.com

How Tennessee is creating a public database of trans people

This is not the first time Tennessee has attempted to make a list of trans people in its state, but it reflects a new tactic for doing so.

@privacyguides@neat.computer
@brian_greenberg@infosec.exchange

Your data isn't at risk of being breached. It already has been. The right question is whether what's out there can still be used against you. Most of the attack surfaces that actually matter are stoppable with free government tools almost nobody has touched: new credit accounts opened in your name, fraudulent tax returns filed before you file yours, employment fraud using your SSN, bank account takeovers. The IRS Identity Protection PIN alone is worth calling out. Someone can file a return in your name, collect your refund, and disappear before you ever log into TurboTax. There's a free six-digit PIN that blocks this cold. Most people have never heard of it.

A few things worth flagging from the guide:
- 23andMe filed for bankruptcy in 2025 and was acquired, putting genetic data for millions of users at risk of sale. If you have an account, delete it and request deletion of your physical sample.
- HIPAA covers your doctor. It doesn't cover your fitness tracker, your wellness app, or your period tracking app. That data flows freely and largely without regulation.
- E-Verify Self Lock is something most people don't know exists. If someone uses your SSN to get a job, the IRS gets their wages on your record. Self Lock blocks it at employers who use E-Verify, which is most large ones.

If you do nothing else, freeze your credit at all four bureaus and get an IRS IP PIN. It takes about 90 minutes and cost nothing. Read the guide, pick a few off the list, and stop treating this as something that happens to other people.
briangreenberg.net/2026/05/07/

briangreenberg.net

How to Protect Yourself from Identity Theft - BrianGreenberg.net — CIO/CTO/CISO

Practical steps to protect yourself from identity theft: assume your data is already exposed, then learn how to make it unusable to attackers.

@deFractal@infosec.exchange · Reply to evacide

@evacide A hypothesis I haven't tested but think we can assume unless someone wants to do the necessary web archive scraping:

Every porn site that would ever follow "age verification" laws—every site subject to any of the applicable jurisdictions—already had meta tags for adult content before those laws were ever bills. Minimum adequate parenting of "digital native" children—thus minimally adequate implementation of device administrative access and parental controls—would already block every site that would ever comply with the laws.

Therefore (as @404mediaco have also predicted), relative to porn access, the only real effect of such online panopticon laws is to direct people away from sites subject to democratic jurisdictions, which at least attempt to lawfully moderate content, and towards sites outside such jurisdictions, which deliberately distribute CSAM and other sex trafficking and SA content.

Legislatively outsourcing parenting onto the porn sites thus increases harm to everyone such laws claim to seek to protect.

@privacyguides@neat.computer

We're thrilled to announce the next section of our Privacy Activism resources! 🎉

📑 The Data Protection Authority Directory is a new tool to help you find the main consumer privacy law in your region, and the authority mandated to enforce that law.

We sincerely hope our DPA Directory will be a useful tool for building your knowledge about what privacy protections you're entitled to. Paired with our resource on reporting privacy violations in our Privacy Activist Toolbox, you can take a stand against violations of your privacy rights, and make a significant impact benefiting both you and your community.

Find your country/state/region here: privacyguides.org/en/activism/

A screenshot of the new DPA directory, showing 6 buttons: Africa, Asia, Europe, North America, Oceania, and South America; as well as the first few lines of a table with the columns: Region, Privacy Law, Abbreviation, DPA, Contact, Complaint
ALT text

A screenshot of the new DPA directory, showing 6 buttons: Africa, Asia, Europe, North America, Oceania, and South America; as well as the first few lines of a table with the columns: Region, Privacy Law, Abbreviation, DPA, Contact, Complaint

@nfd@social.lol
@nfd@social.lol
@samba@mastodon.cisti.org
@ggpsv@social.coop

It's been a while since I posted here, and at this point all of my previous posts have auto-deleted. Might as well reintroduce myself.

I am Gabriel, and I am based in Costa Rica. I work as an independent software developer and systems administrator.

As of late, my computer interests lie in , , and . I care a lot about and ownership of our data and devices.

I am also passionate about , , , , and .

@knoppix95@mastodon.social
@danyork@mastodon.social

First time seeing a “NO META GLASSES” sign in the door of a shop! I’m not surprised… and I expect we might see more of these kind of things in the years ahead.

Thumbnail not available
ALT text

A sign on a store window indicates "NO META GLASSES," featuring images of different sunglasses models. It also includes instructions to respect staff by asking permission before taking pictures or videos, with a friendly "Thank you!" at the bottom.

@JulianOliver@mastodon.social

Delighted to report that Amazon has abandoned its plans to build a datacenter here.

The "lease-and-equip" model they're switching to is a lot easier to get rid of, when we eventually kick these digital imperialists out altogether.

I'll raise a sovereign glass of fresh water to that.

rnz.co.nz/news/business/594164

rnz.co.nz

Amazon takes $45m hit, abandons planned West Auckland data centre

Despite the write-down, Amazon appeared to be continuing to invest heavily in its New Zealand footprint.

@knoppix95@mastodon.social
@danyork@mastodon.social

First time seeing a “NO META GLASSES” sign in the door of a shop! I’m not surprised… and I expect we might see more of these kind of things in the years ahead.

Thumbnail not available
ALT text

A sign on a store window indicates "NO META GLASSES," featuring images of different sunglasses models. It also includes instructions to respect staff by asking permission before taking pictures or videos, with a friendly "Thank you!" at the bottom.

@r_alb@mastodon.social

Dear politicians,

your push for surveillance is wrong! Not just morally, but also from a strategic perspective. In a geopolitical environment shaped by digital warfare, the data you collect on citizens will become a threat. Adversaries will try to weaponize those data, and sooner or later, they will succeed.

A transparent society is vulnerable to all sorts of malicious influence.

Privacy supports resilience! Data you don't have cannot be used by or against anyone!
--

@privacyguides@neat.computer

🚨 This Week In Privacy #51 will be live in 30 minutes, we'll be talking about
Ubuntu adding AI features and using it in their development pipeline 😬, we will also be covering the latest in privacy & security news. 🗞️

We will also be answering questions from the community, come say hi! 😊

streamyard.com/watch/zsBB6viVS

streamyard.com

Is Ubuntu Becoming the New Windows?

Canonical has laid out it's plans to integrate "AI" features into Ubuntu Linux, Signal is working on a standalone desktop version, that doesn't require a smartphone, Greece is banning anonymity on social media and more! Join us for This Week In Privacy #51

@artfulrobot@floss.social

I just spent an hour doing the UK Govt consultation on

I highly suggest you do too if you're a UK subject.

The consultation seems as naive as to be expected re dangers.

Massive overreach/over sharing of data. Fraud/Id theft/coercion risks. State wants biometric face scan - state surveillance will be inevitable. Zero references to trusting US companies (apple&google) to provide secure devices....

gov.uk/government/consultation

gov.uk

Making public services work for you with your digital identity

@reapps_eu@mastodon.social · Reply to Reborn Apps · reapps.eu

re/task highlights:

- Lists, subtasks, recurring tasks (daily/weekly/custom)
- Stars, due dates, optional push notifications
- Full-text search across all lists
- Smart views — Today, Upcoming, Overdue, Starred
- Trash & 30-day recovery
- JSON import/export

re/notes highlights:

- Markdown editor with live preview
- Folders, tags, internal links with autocomplete
- Version history
- Encryption X-Ray
- Import single .md or whole Obsidian vaults

🧵 2/n

re/task screenshot
ALT text

re/task screenshot

@reapps_eu@mastodon.social

Two open-source, end-to-end encrypted productivity PWAs by a EU non-profit foundation.

re/task - encrypted task manager
re/notes - encrypted Markdown notes

Built on a True Zero Knowledge architecture: AES-256-GCM, Argon2id, PBKDF2 600K iterations. The server stores only ciphertext - it physically cannot read your tasks, notes, due dates, or even tag relations.

→ Free official instance: reapps.eu

🧵 1/n

Thumbnail not available
ALT text

Two open-source, end-to-end encrypted productivity PWAs by a EU non-profit foundation. re/task — encrypted task manager re/notes — encrypted Markdown notes

@TexasObserver@texasobserver.social

The Observer obtained Flock license-plate reader audit logs that show conducted 117 immigration-related searches of local data from Jan to March. One dept's reason to search: "Obstructing Justice – Suspicious female filming traffic stop & making comments about ICE” texasobserver.org/license-plat

texasobserver.org

As License Plate Readers Expand in Texas, Privacy Advocates Are Fighting Back 

The Kyle City Council voted to apply for more state grant money for Flock Safety cameras despite a string of local-level contract cancellations of the booming surveillance company’s services.

@dckim@mastodon.social

Thanks So Much...
@GYLPH there just isn't enough room in a POST to thank you for your MASSIVE PUBLIC ENDORSEMENT of my website, so, I made a machine to CHOP IT FOR THE ALT TEXTS!

mastodon.social/@glyph/1154526

...

Thumbnail not available
ALT text

Dearest GLYFH, It is barely possible that I will be able to thank you enough for what an extraordinary effort you have made towards your absolutely selfless and chivalrous early promotion of my naive web project. By linking my website directly, you essentially dispatched a tidal wave of visitor who would not have otherwise been exposed to my amazing web project at what might have seemed like a juvenile stage of the development process. Unlike many others, you were able to clearly recognize that the project was still in the exploratory programming stage, where all of the early programming is completed, and secondary programming is being freshly explored. Of course, I don't have to tell you about the amazing and mystical techniques that must be used to set up the elaborate and time consuming methods that make real-life programs function every single day. Really I should not only be thanking you from myself, because of your amazingly generous and substantial public endorsement of myself, my website, and my project, but also for the wide public, who, even so as they do not even know it, owe you an enormous debt. The gravity of what you have accomplished, particularly in your early career, is an astonishing feat of computering brilliance, the likes of which the world has never before seen, and alas, may never see again. Of course, the particular contribution of yours to which I am clearly alluding is the twisty python framework networking app. You were the only...

Thumbnail not available
ALT text

one who was brave and intellectual enough to take up the intensity of the challenging nature of this exceptional computational science challenge. SIR you have certainly prevailed! AND you have remained extremely prevalent to this very day. Your prevalence and continued dominance in the Python software networking industry has stood the test of time, and will, doubtless, continue on into the future, for a duration which cannot be predicted in known units of temporal quantity. I guess what I am trying to say is that the Giant effect of your efforts will go on to unknown reaches and at untold length. And just let me tell you, many of those people, so very many, are not even aware of how much they rely on the critically important software which you single-handedly pioneered. This is why your bold and thorough public endorsement of my website, and therefore my project, was such a stunning and heartwarming experience. Just think, that a superstar software engineering maven such as yourself would effectively SPONSOR through ENDORSEMENT a project like mine, that is an wonderful thing. Obviously your thoughtful nature and clear passion for small independent web projects drove you to take this decisive action and you generously lent your personal support for my website. I don't know how I can ever thank you enough for your apathy and your motivation. Everyone who I have ever met who knew about your contribution to the python programming language all admitted that they did...

Thumbnail not available
ALT text

not know how it worked. That is because they did not have the momentum to study diligently enough to comprehend the mastery of the code which you so graciously adorned, sir. Not even one was able to comprehend it, because they are simply not intellectual enough. Every time I hear about systems that claim, egregiously, to somehow compete with your decisive contribution, I actually begin to laugh, and that is because I know that it is not possible to replace such vital scripture as yours. You have written it with your own hands, and it will be around for the ages. For anyone who has accepted the challenge of learning the correct method, as you have so gallantly taught us, they must be brave, as you are brave, sir. It is very much like riding on a horse. First you must get up on top of that horse, and then you will be know to be riding the horse. But, before you can ride the horse, you must place a seat upon the top of the horse, just like how GLYFH has taught us all to do. And then when you are riding on top of the horse, you will be glad that you have such a seat as this one. That is the only seat for that horse, so you will know best to choose wisely the best one. After when you are riding such an animal as a horse, you cannot easily change the seat whilst riding, and must therefore continue in dominance or in failure, in spite of the seat of everyone's but yours. Of course, it is obvious that the metaphor which I have embarked upon is fraught and will never have...

Thumbnail not available
ALT text

the capacity to imbue upon the intellect the height of import in magnitude which I am struggling, because of lack of intellect, to attribute to you. - Yours truly is the best seat, The Guy You Endorsed (wow, such spacious posts on Mastodon)

@scottwilson@infosec.exchange

All mainstream messaging platforms share the same model: a single provider owns the servers, logic, and . Between political pressure and regulatory proposals like , such centralization is a liability.

Learn from @morrolinux how Matrix, a secure, open, and decentralized network, flips this model: lpi.org/r2yu

@matrix

@Em0nM4stodon@infosec.exchange

Anyone asserting encryption is a tool for crime is either painfully misinformed or is attempting to manipulate legislators to gain oppressive power over the people.

Encryption is not a crime,
encryption is a shield.

Encryption protects you from cyberattack, identity theft, discrimination, doxxing, stalking, sexual violence, physical harm, and much more.

For safety, for privacy, for democracy, and for all our human rights, it's critical that we defend our right to encryption.

privacyguides.org/articles/202

privacyguides.org

Encryption Is Not a Crime

Encryption is not a crime, encryption protects us all. Encryption, and especially end-to-end encryption, is an essential tool to protect everyone online. Attempts to undermine encryption are an attack to our fundamental right to privacy and an attack to our inherent right to security and safety.

All mainstream messaging platforms share the same model: a single provider owns the servers, logic, and . Between political pressure and regulatory proposals like , such centralization is a liability.

Learn from @morrolinux how Matrix, a secure, open, and decentralized network, flips this model: lpi.org/r2yu

@matrix

@dweb@social.coop

🗓️ 𝗔𝗽𝗿 𝟯𝟬: 𝗗𝗪𝗲𝗯 𝗩𝗶𝗿𝘁𝘂𝗮𝗹 𝗠𝗲𝗲𝘁𝘂𝗽 🌼

Get a sneak peek of what’s coming to camp by joining us with Will Scott from Protocol Labs and the Community Privacy Residency Staff, this Thursday at 15:00 UTC! 👀

🆓 Free attendance, RSVP here → tix.dod.ngo/dwebcamp/virtualme ←

Thumbnail not available
ALT text

Graphic split in two: on the left, illustration of synapses on dark background, floating around them the words “people”, “projects”, and “ideas”. On the right, a photo of people talking in a panel. Above, in big capital letters: “coming to DWeb Camp // sneak-peak”.

@jackgangi@masto.hackers.town

I've been building an independent publication called The Grist. It's writing about civics, technology, rights, and practical knowledge. This one's a big swing for me and I've put a lot into it. No ads, no algorithm, no paywall. Take a look and let me know what you think. hope you like it. grist.ink

grist.ink/

Thumbnail not available
ALT text

"The Grist nameplate — Independent. Unfiltered. Unsponsored

@unknownuniverse@unkn.uk
Greetings and welcome back!

Following a week long battle with the federation and those incessant timeouts on my noc.social account, I have ultimately succeeded in migrating my followers to this new, self-hosted home at `unkn.uk`.

Constructing this permanent base of operations was a task, but finally, normal service can be resumed.

I am quite relieved to see everyone's handles in my followers list again rather than just 502 headers.

#Fediverse #Akkoma #SelfHosted #Homelab #Privacy #Migration #Mastodon
Thumbnail not available
ALT text

A technical digital poster titled "WELCOME BACK!" in bold white letters. The background is a moody navy dark circuit board with glowing cyan lines. In the center, a cyan Atom logo sits inside a dark, softly glowing portal, representing the successful restoration and self-hosting of the user's Fediverse instance.

@privacyguides@neat.computer

We just had a chance to interview Carissa Véliz, author of Privacy is Power and associate professor at the Institute for Ethics in AI at the University of Oxford.

We talked about how predictive AI will make a 'meritocracy' impossible, how lifelike chat bots are designed to deceive you, and the importance of privacy in the digital age. Catch the episode on our YouTube channel or your favorite podcast app now!

Carissa Véliz is an associate professor at the Institute for Ethics in AI at the University of Oxford, a renowned author and speaker, a board member of the Proton Foundation, and a member of UNESCO's Women 4 Ethical AI.

Her new book Prophecy comes out April 21st and is now available for pre-order.

Prophecy is about how extensive use of predictive analytics is undermining our abilities to defy the odds, making systems unaccountable, and increasing risk in business and society while creating a false sense of security.

privacyguides.org/videos/2026/

privacyguides.org

Interview with Carissa Véliz, Author of "Privacy is Power" and "Prophecy"

We sat down with Carissa Véliz, author of 'Privacy is Power' and Oxford AI Ethics professor, to talk about how predictive AI will make a 'meritocracy' impossible, how lifelike chat bots are designed to deceive you, and the importance of privacy in the digital age.

@brian_greenberg@infosec.exchange

The McDonald's AI jailbreak story was fabricated. The Chipotle one before it was Photoshopped. I get why they went viral, they're kinda funny. But they're pulling attention away from the cases that actually happened and actually cost companies money.

Amazon's Rufus chatbot got manipulated into providing instructions for obtaining dangerous chemicals. A Chevy dealership's bot was maneuvered into agreeing to sell a $76,000 Tahoe for a dollar. Air Canada's bot invented a refund policy that didn't exist, a customer relied on it, and when the airline said "that's not our problem, the bot is its own entity," a Canadian tribunal told them exactly where to put that argument.

If you're a CIO, the legal question sitting underneath all of this is the one worth losing sleep over:
- Prompt injection isn't exotic. It works because LLMs are built to be responsive to language, not resistant to it. There is no patch that fully closes this.
- Any AI you deploy on a customer-facing surface is making representations on your company's behalf. Your legal team needs to know that before your marketing team ships the chatbot.
- "The bot did it, not us" is not a defense. One court has already said so, and others will follow.

The fake viral stories are a distraction. The boring real ones are the ones that end up in discovery.

fastcompany.com/91532091/mcdon

@brian_greenberg@infosec.exchange

The FCC forgot hotspots were a thing. They announced a ban on foreign-made consumer routers a month ago and had to update their FAQ to add MiFi devices and cellular home routers after the fact. That's not a minor oversight... it's the whole work-from-anywhere use case.

Here's the part that should bother you. The only way to get an exemption is to commit to US-based manufacturing and submit a time-bound plan to get there. Netgear, eero, and Adtran got conditional approval, but it runs out October 1, 2027. There is no domestic consumer router industry to speak of right now. So the FCC has created a countdown clock against a factory floor that doesn't exist yet.
A few things worth sitting with:
- The Global Electronics Association pointed out that security vulnerabilities show up across products regardless of where they're made. Geography isn't the filter; code quality is.
- The Covered List used to apply to specific companies flagged for specific reasons. Extending it to an entire product category means the government can now ban any internet-connected device made abroad by citing national security. Smartphones aren't included yet. "Yet" is doing a lot of work in that sentence.
- The Register's headline from last month said it plainly: the country that put backdoors in Cisco routers to spy on the world is now banning foreign routers. I didn't write that. They did. But they're not wrong.

If you're in security or IT leadership, watch the October 2027 date. That's when the conditional approvals expire, and if the manufacturing commitments aren't met, the options get ugly fast.

theregister.com/2026/04/24/fcc

theregister.com

FCC adds mobile hotspots to router ban

: Silicon often from US, but the kit from APAC and elsewhere

@brian_greenberg@infosec.exchange

Anthropic recorded over 16 million interactions with Claude from about 24,000 fake accounts, which are reportedly linked to Chinese companies trying to cheaply copy the model. Google faced more than 100,000 attempts to copy Gemini. OpenAI reports that most distillation attacks they find come from China. This is not an isolated event. It is a repeatable and scalable strategy.

Breaking the terms of service isn't enough to stop people when the reward is closing a years-long gap in AI technology. The House Select Committee on China wants to label 'adversarial distillation' as industrial espionage under the Economic Espionage Act, which makes sense. At the moment, getting caught just means losing an account. That is hardly a real punishment.

The Trump-Xi summit is approaching, and the White House is reportedly considering sanctions. However, Trump has previously traded away export controls for other deals. If that happens again, AI companies may have to protect their intellectual property by themselves.

When laws fail to keep pace with new types of attacks, attackers automatically have the advantage.

If your company is developing anything unique using advanced AI models, your API access logs are now part of your security risks.

arstechnica.com/tech-policy/20

arstechnica.com

US accuses China of “industrial-scale” AI theft. China says it’s “slander.”

Trump-Xi summit may be rocked by US mulling huge sanctions.

@brian_greenberg@infosec.exchange

A Chinese national pretended to be U.S. engineers and researchers for almost five years, from 2017 to 2021, and walked away with sensitive aerospace and weapons development software from NASA, the Air Force, the Navy, and the Army. There was no hacking or breaking through firewalls. People simply emailed him what he asked for, because they believed he was someone they knew.

This worries me more than any zero-day vulnerability. The NASA OIG reported that Song Wu asked for the same software several times without explaining why he needed it. Most people miss this kind of red flag because no one teaches them to spot it. We invest millions in technology controls but spend very little on training people to pause and think like a threat actor before sending information.

Export controls are not only about legal compliance. They are also about human behavior. Your employees make export control decisions every day, often without realizing it.

When was the last time your organization ran a spear-phishing simulation aimed at your researchers, not just your finance team?

If your security awareness program doesn't cover identity deception and unusual software requests, it is not thorough enough.

thehackernews.com/2026/04/nasa

thehackernews.com

NASA Employees Duped in Chinese Phishing Scheme Targeting U.S. Defense Software

NASA OIG exposed a 2017–2021 spear-phishing campaign by Song Wu, leading to DOJ charges and export control violations.

@brian_greenberg@infosec.exchange

Anthropic spent months carefully gatekeeping access to Mythos, their most capable AI model, while limiting access only to a small group of vetted companies for defensive cybersecurity testing. Then a private online forum got in anyway, through a third-party vendor, on the same day the controlled program was announced.

That's the part worth sitting with. Not the model. The vendor. Third-party vendors... It's always the the 3td party vendor. 🤦🏻‍♂️ You can build the most carefully controlled AI release program in the industry, and one weak link in your supply chain burns it down. We keep having this conversation about AI safety and regulation, and we keep forgetting that the threat surface isn't just the model. It's every partner, every integration, every environment touching it. 🔗 Everything's connected. Everything.

🤔 Ask yourself: how many third parties have access to your most sensitive systems right now? Do you actually know?
⚠️ Vendor risk management isn't a compliance checkbox. It's where your security posture actually lives or dies.

yahoo.com/news/articles/anthro

yahoo.com

Ihre Datenschutzeinstellungen

@brian_greenberg@infosec.exchange

Trying to be secure... You deleted the app. You turned on disappearing messages. You did everything right. The FBI can still read your Signal messages.

Huh? This wasn't a Signal failure. Signal did its job. iOS didn't. The phone was storing notification previews in a database long after the app was gone, because someone turned on Lock Screen message previews. Apple just patched it in iOS 26.4.2, and they only found out about it because a defendant's court case exposed it during testimony.

🔎 This is why privacy promises and privacy architecture are two different things
📲 Update your phone. Not because you're hiding something. Because your phone is quietly keeping receipts you don't know about.
⚠️ And if you're a CISO still telling employees that "just use Signal" is a complete privacy answer, it's time to revisit that conversation.

macrumors.com/2026/04/22/ios-2

macrumors.com

iOS 26.4.2 Patches Flaw That Let FBI Extract Deleted Signal Messages

The iOS 26.4.2, iPadOS 26.4.2, iOS 18.7.8, and iPadOS 18.7.8 updates that Apple released today address a security vulnerability that the FBI recently used to extract Signal message previews from an iPhone even after the app was deleted. A flaw with notification services allowed notifications that were supposed to be deleted to be retained on an iPhone or iPad. Apple says it fixed the logging issue with improved data redaction.

@tomgag@infosec.exchange

BREAKING! Meshcore team splits over dispute over AI-generated code disclosure, and hostile trademark takeover.

Meshcore is an off-grid, decentralised mesh radio platform powered by low-cost and public access LoRa radio technology for reliable, long-range emergency text and embedded sensors communication. It can communicate across kilometres — no towers, no subscriptions, no single point of failure.

blog.meshcore.io/2026/04/23/th

blog.meshcore.io

Meshcore.io - Why The Split? - MeshCore Blog

Migrating to the new meshcore.io site

@ridogi@mastodon.social · Reply to Eric deRuiter

There is a manual review alternative according to this page intended for providers which states "If you're having trouble with the process, Headway's support team can help. You can retry the verification, and if there are persistent issues, you can contact Headway support for a manual review."

help.headway.co/hc/en-us/artic

@Em0nM4stodon@infosec.exchange

Age verification laws forcing platforms to restrict content access have been multiplying exponentially.

The problem is, implementing such measures necessarily requires identifying every user accessing the content, one way or another.

This is bad news for everyone.

If these regulations continue
to proliferate, this could lead to the end of pseudonymity online, and much worse.

I wrote this article last year,
but unfortunately this problem has only become worse, and it is sadly still very relevant.

privacyguides.org/articles/202

privacyguides.org

Age Verification Wants Your Face, and Your Privacy

Age verification laws forcing platforms to restrict access to content online have been multiplying in recent years. The problem is, implementing such measure necessarily requires identifying each user accessing this content, one way or another. This is bad news for your privacy.

@brian_greenberg@infosec.exchange

Quick thought experiment. Pull out your phone, look at your lock screen, and ask yourself who else is reading those notification previews. The answer is stranger than you think.

EFF just laid out what most people don't realize: push notifications usually route through Apple or Google servers before they hit your device, often with content visible in the clear. Then they get written to a local notification database that doesn't always get wiped when you swipe the alert away or even when you uninstall the app. 404 Media reported the FBI has pulled deleted Signal message text out of that database using standard forensic tools. Signal. The app you installed specifically because you didn't want this.

🔐 Apple and Google now require a court order for push notification data, but Apple's transparency report still shows hundreds of users handed over
📱 Lock screen previews are a free read for anyone who picks up your phone, including at a border crossing or traffic stop
🧹 Uninstalling an app does not guarantee its notification history goes with it, and we don't know what gets backed up to iCloud or Google
🛠️ Signal's notification setting "No Name or Content" is a 30-second fix that closes the easiest leak

For the security folks, this is a useful reminder that end-to-end encryption ends at the endpoint, and the endpoint includes a SQLite file most users have never heard of. For the executives, this is the reason your travel security policy for high-risk regions should say more than "use Signal." The default settings on a stock iPhone leak more than the app you chose to protect you.

eff.org/deeplinks/2026/04/how-

eff.org

How Push Notifications Can Betray Your Privacy (and What to Do About It)

A phone’s push notifications can contain a significant amount of information about you, your communications, and what you do throughout the day. And there are myriad ways that law enforcement can access the content or metadata of push notifications. Let’s fix that.

@brian_greenberg@infosec.exchange

An ex-Azure engineer published six essays arguing Microsoft's cloud has been on life support since 2008, and the cause isn't bad code. It's bad people decisions. Rushed launch, post-launch talent exodus, no testing discipline, no architectural vision. Sound familiar to anyone who's worked in a place that ships first and staffs later?

Now layer 2026 on top. Microsoft cut roughly 15,000 jobs in mid-2025. Coding agents are pumping out 4x more commits in 90 days. GitHub's unofficial uptime has slipped under 90% and the proposed fix is, wait for it, moving more of GitHub onto Azure. The same Azure the engineer says is held together with rushed decisions and wishful thinking.

🧠 The phrase that stuck with me is "knowledge dilution from high attrition." When the senior people who knew why a system was built that way leave, no LLM in the world can recover that context
🤖 More AI-written code does not mean less work. It means more code to review, test, deploy, and run, which means more compute and more humans needed downstream
📉 OpenAI signing an $11.9B compute deal with CoreWeave in March 2025 was the loudest "we don't trust your capacity" signal Microsoft has ever received from its closest partner
🪑 The bet that AI lets you cut headcount keeps colliding with the reality that AI generates work for humans faster than it removes it

Every CIO I talk to is being pitched the same dream: fewer engineers, more agents, lower run rate. The Azure story is what happens when that math doesn't pencil out and the bill comes due in incidents instead of dollars.

theregister.com/2026/04/04/azu

theregister.com

Ex-Microsoft engineer blames Azure problems on talent exodus

: The cloud service's woes reflect a crisis made worse by AI – under-investment in people

@brian_greenberg@infosec.exchange

Four grand. That's what it costs a random kid with a laptop to run a voice phishing operation that used to require a call center, a phisher, and a developer. ATHR packages all of it into one dashboard, tosses in AI voice agents that can ad-lib when a victim gets suspicious, and ships with ready-made lures for Google, Microsoft, Coinbase, Binance, and a few more.

CyberCrime has a SaaS model now, complete with commission splits (10% of profits back to the vendor). The barrier to running a convincing vishing campaign just collapsed, and your awareness training still says "watch for typos in the email."

🎙️ AI agents handle objections live, so the "support rep" sounds real because they are, functionally, reasoning
📧 Lure emails are customized per target with accurate IPs, dates, locations, and pass authentication checks
🏦 Eight brands supported out of the box, crypto exchanges heavily represented for obvious reasons
🛡️ Stop looking at email indicators, start modeling normal communication patterns and flag the anomalies

If your vishing defense is a 20-minute annual training video and a phish-report button, you're bringing a knife to a drone fight. The humans on the other end of the phone aren't humans anymore, and they don't get tired, rattled, or bored on calls.

bleepingcomputer.com/news/secu

@vinterkarusell@mastodon.online

📣 V3

Hi! 👋

I'm a producer with a strong passion for . Music-wise I lean toward , while photography ranges from aerial to architecture and everyday stills.

A big believer in , digital independence, and owning your own space online, powered by .

When I'm not crafting electronic noise or framing pixels, I’m reading terms and conditions just to feel something. 😁

Also, I get paid to talk. Not much—I just talk a lot.

Feel free to connect! ✨

@jbz@indieweb.social

👻 Anthropic secretly installs spyware when you install Claude Desktop — That Privacy Guy!

「 I did install Claude Desktop, the Mac app, a while back. That is the only thing on this machine which could have written the file. Claude Desktop reached into Brave, a browser from a completely separate vendor, and registered a back door for a browser extension I do not have 」

thatprivacyguy.com/blog/anthro

thatprivacyguy.com

Anthropic secretly installs spyware when you install Claude Desktop — That Privacy Guy!

Anthropic's Claude Desktop silently installs a Native Messaging bridge into seven Chromium browsers, including browsers Anthropic's own documentation says it does not support, and browsers the user has not even installed.

@SecureOwl@infosec.exchange · Reply to Mike Sheward

Happy Monday, got this gem from a UK org. The subject line was "GDPR request".

I think it sums up this particular shitshow perfectly tbh.

"we have processed your GDPR request and are now sending your deleted information to someone you do not know as confirmation we have deleted you"

Thumbnail not available
ALT text

screenshot of an email that lists all the old values and the new values - which are deleteduser.com based.

@TechDesk@flipboard.social

Raise your hand if you use Chrome. After all, it is the most popular browser in the world and it’s not even close. And the very humans relying on it are more than users — they’re the product. PC World tells us more about how you can limit the amount of your data Chrome tracks — and reclaim a little bit of your privacy.

flip.it/9gjQk2

pcworld.com

Chrome tracks more than you realize. Here’s how to take back your privacy

While Chrome is a popular browser, it tends to collect a lot of data about its users. Here is how to help minimize what it collects and make your browsing experience more private.

@privacyguides@neat.computer

We just had a chance to interview Carissa Véliz, author of Privacy is Power and associate professor at the Institute for Ethics in AI at the University of Oxford.

We talked about how predictive AI will make a 'meritocracy' impossible, how lifelike chat bots are designed to deceive you, and the importance of privacy in the digital age. Catch the episode on our YouTube channel or your favorite podcast app now!

Carissa Véliz is an associate professor at the Institute for Ethics in AI at the University of Oxford, a renowned author and speaker, a board member of the Proton Foundation, and a member of UNESCO's Women 4 Ethical AI.

Her new book Prophecy comes out April 21st and is now available for pre-order.

Prophecy is about how extensive use of predictive analytics is undermining our abilities to defy the odds, making systems unaccountable, and increasing risk in business and society while creating a false sense of security.

privacyguides.org/videos/2026/

privacyguides.org

Interview with Carissa Véliz, Author of "Privacy is Power" and "Prophecy"

We sat down with Carissa Véliz, author of 'Privacy is Power' and Oxford AI Ethics professor, to talk about how predictive AI will make a 'meritocracy' impossible, how lifelike chat bots are designed to deceive you, and the importance of privacy in the digital age.

@Em0nM4stodon@infosec.exchange

When you read about Bans of Social Media for Teens and Age Verification, you must remember what it truly means:

• Official identification of every adult using social media.

• Deanonymization of every account, endangering groups that often rely on pseudonymity for safety, such as victims of domestic violence, victims of stalkers, people of color, and LGBTQ+ people.

• Putting every adult at great danger of exploitation, fraud, and identity theft by forcing them to share their official ID with a for-profit third-party company with no incentive to protect it. Breaches have already happened.

• Constructing a system of mass surveillance to attach every comment on social media to a legal identity. Effectively allowing authoritarian governments to silence their critics and opposition.

• Potential for dystopian censorship and cutting off means of organization for groups of resistance to oppressive regime and organizations.

• Endangering children online by putting a clear identification beacon over every child or family with children online.

• Endangering the data of children who will inevitably try to pass as adults, and have their information collected by the third-party for-profit company.

• Diminishing the value of official identification due to the inevitable data breaches, eventually pushing the system to require even more intrusive identification techniques, such as iris scans and fingerprints.

• Installing a system of mass surveillance capable of attaching even more information to everyone's legal identity. With a potential to built list of people in certain groups, and scale-up state censorship and discrimination in unprecedented ways.

• The list goes on and on.

This isn't about protecting the children.
It never was.

Do not be duped by this excuse used to convince you to let go of your human rights. They are only trying to manipulate people lacking information.

Stay informed on the issues related to Age Verification, and push back for your rights to privacy and democracy.

The future depends on us.

@r_alb@mastodon.social
@belladonnalily@mastodon.social · Reply to CascaCasca95
@brian_greenberg@infosec.exchange

A startup is putting military-style drones in high school ceilings. Ceiling-mounted. Charging. Waiting. And when something happens, a pilot in Austin, Texas, decides whether to deploy pepper gel on your kid's school. I'm not saying the problem isn't real. It absolutely is. But read that back.... in schools. We've taken a Ukrainian battlefield tactic against Russian soldiers and ported it to Deltona High School in Florida. The co-founder literally said the idea came from watching drone videos of the war in Ukraine. The chief pilot described it as "cheating in a video game after you die." These are children.

Here's what's not in the headline:

🔒 The drones use an encrypted connection — but the article notes they're potentially vulnerable to cyberattack. A compromised drone in a crowded hallway isn't a security tool; it's a weapon pointed in the wrong direction.

⚖️ Mithril reserves the right to act independently during an attack, without waiting for law enforcement. A private company operating remotely is making use-of-force decisions at a school.

💰 Florida and Georgia approved $500K+ each for this. A group of Texas parents raised $200K more. That's real money going to ceiling drones instead of mental health services, counselors, or de-escalation programs.

The ACLU said it plainly: when force becomes a zero-risk remote action, it gets overused. Axon tried a Taser drone for schools in 2022, and its own ethics board killed it. Mithril is picking up where that got dropped.

I teach cybersecurity. I've spent years in boardrooms helping organizations think through risk. And the risk calculus here isn't just about whether the drone works. It's about what we're normalizing when we turn schools into drone-monitored combat zones and call it progress.

"This is the future," said the sheriff's captain.

I hope not.

wsj.com/business/a-startup-is-

@gtbarry@mastodon.social

Meta Is Warned That Facial Recognition Glasses Will Arm Sexual Predators

More than 70 civil liberties, domestic violence, reproductive rights, LGBTQ+, labor, and immigrant advocacy organizations are demanding that Meta abandon plans to deploy face recognition on its smart glasses

wired.com/story/meta-ray-ban-o

wired.com

Meta Is Warned That Facial Recognition Glasses Will Arm Sexual Predators

More than 70 organizations, including the ACLU, EPIC, and Fight for the Future, say the AI smart glasses feature would endanger abuse victims, immigrants, and LGBTQ+ people.

@internetarchive@mastodon.archive.org

You might consent to your data being used to prevent societal harm, but who decides where that line is drawn? 🤔⚖️

Aram Sinnreich & Jesse Gilbert explore the hidden ethics of data collection, facial recognition, and algorithmic decision making in THE SECRET LIFE OF DATA on the Future Knowledge , with Laura DeNardis. 🔍

🎧 Listen & subscribe ⬇️
futureknowledge.transistor.fm/

@aram @jesse

@josh@sideofburritos.social

I got this email this morning, and I guess this is now a marketing point? Whether the FCC labels you a “trusted consumer router”? I wonder what requirements they met, or more likely, how much that cost them.

For context, I don’t use NETGEAR. Just an old account email.

Thumbnail not available
ALT text

An email from NETGEAR explaining that the FCC (Federal Communications Commission) has listed NETGEAR as a trusted consumer router company.

@Em0nM4stodon@infosec.exchange

In privacy, we talk a lot about how to protect our own data,

But what about our responsibility to protect the data of others?

If you care about privacy rights, you must also care for the data of the people around you.

To make privacy work, we need to develop a culture that normalizes caring for everyone's data, not just our own.

privacyguides.org/articles/202

privacyguides.org

Privacy is Also Protecting the Data of Others

In privacy, we talk a lot about how to protect our own data, but what about our responsibility to protect the data of others? If you care about privacy rights, you must also care for the data of the people around you. Together, we must build a culture where everyone cares for the data of others.

@gtbarry@mastodon.social

Meta Is Warned That Facial Recognition Glasses Will Arm Sexual Predators

More than 70 civil liberties, domestic violence, reproductive rights, LGBTQ+, labor, and immigrant advocacy organizations are demanding that Meta abandon plans to deploy face recognition on its smart glasses

wired.com/story/meta-ray-ban-o

wired.com

Meta Is Warned That Facial Recognition Glasses Will Arm Sexual Predators

More than 70 organizations, including the ACLU, EPIC, and Fight for the Future, say the AI smart glasses feature would endanger abuse victims, immigrants, and LGBTQ+ people.

@Some_Emo_Chick@mastodon.social
@profoundlynerdy@bitbang.social

I'm thinking about getting a used Jeep, 10-ish years old. I'm concerned about intrusive data harvesting from the vehicle. I'd still like to be able to use my phone's GPS functionality with the infotainment display IF I can do it with a FOSS software stack that respects privacy and a degoogled phone. Suggestions?

Any tips for preventing the vehicle from phoning home more generally is also welcome.

@brian_greenberg@infosec.exchange

Anthropic built an AI model called Mythos that autonomously found a 17-year-old remote code execution vulnerability in FreeBSD. No human involvement after the initial prompt. It found thousands more zero-days across every major OS and browser, some hiding for decades. Anthropic says it's too dangerous to release publicly, so they gave it to AWS, Microsoft, Apple, Google, CrowdStrike, and a handful of others under a new initiative called Project Glasswing. $100M in usage credits to go fix things before similar capabilities go wide.

Impressive, but worth some skepticism. Bruce Schneier pointed out this is also a very effective PR play. A security firm called Aisle replicated many of the same findings using older, cheaper, publicly available models. The gap between "too dangerous to release" and "already achievable with what's out there" may be thinner than the headlines suggest.

🔒 Mythos autonomously discovered and exploited a FreeBSD RCE that had been present for 17 years (CVE-2026-4747)
🔗 It chains 3-5 vulnerabilities together into multi-step attack sequences
📊 Over 99% of the vulnerabilities found are still unpatched, so we're trusting Anthropic's claims on scope
💰 $25/$125 per million input/output tokens for partners, if you're on the list

Meanwhile, the advice cybersecurity experts are giving the rest of us: update your software, use MFA, get a password manager. The most advanced AI vulnerability scanner ever built, use off-line (truly air-gapped) backups, and basic hygiene is still the best defense most people have.

crn.com/news/security/2026/5-t

crn.com

5 Things To Know On Anthropic’s Claude Mythos And ‘Project Glasswing’

Anthropic announced Tuesday it has launched a new initiative, “Project Glasswing,” focused on boosting software security with involvement from a number of major industry players.

@brian_greenberg@infosec.exchange

😳 Someone hid a prompt injection inside invisible markdown comments in a pull request. A developer asked Copilot to review the PR. Copilot read the hidden instructions, searched the codebase for AWS keys, encoded them in base16, and smuggled them out through GitHub's own image proxy as 1x1 transparent pixels. The CSP didn't flag it because the traffic was routed through GitHub's trusted infrastructure. CVSS 9.6. No malicious code ever executed.

The attacker weaponized the AI assistant's own access permissions. Copilot could see everything the developer could see, and it can't distinguish a legitimate instruction from a hidden one buried in a PR description.

🔍 The attack, dubbed "CamoLeak," was patched by GitHub in August 2025 and publicly disclosed in October
🔑 Copilot was directed to find secrets like API keys and cloud credentials, then exfiltrate them character by character
🖼️ Data was hidden inside pre-signed image URLs, making it look like normal browser activity
⚠️ Any AI assistant with deep system access, Microsoft 365 Copilot, Google Gemini, all of them, is a potential exfiltration channel if untrusted content can reach its instruction stream

We've spent years teaching developers not to trust user input. Now we're handing AI tools full repo access and letting them ingest unvalidated text from pull requests.

cybersecuritynews.com/hackers-

cybersecuritynews.com

Hackers Exploit GitHub Copilot Vulnerability to Exfiltrate Sensitive Data

A high-severity flaw in GitHub Copilot Chat allowed silent theft of source code, API keys, and secrets from private repos without executing code.

@kq@ieji.de · Reply to Kaifi 🍉

pitha.social is live today!

We just launched a new Mastodon instance focused on privacy, Bengali culture, and a friendly community!

🌐 Invite links: yes
🛡️ Moderation: active

We're looking to federate and connect!

pitha.social

Pitha Social

A curated space for curious minds. Rooted in Bengali culture. An invite-only community, hosted in the EU!

@timbray@cosocial.ca
Thumbnail not available
ALT text

Your Android phone is sending data to Google every 4.5 minutes. Even when you're not touching it. Even when the screen is off. A peer-reviewed study from Trinity College Dublin confirmed it. 12 settings to change right now: 1/15

@ProPublica@newsie.social

NEW: Who’s Been Impersonating This ProPublica Reporter?

A mysterious impostor who claimed to be ProPublica reporter Robert Faturechi reached out to a Canadian official and a Latvian businessman working with Ukraine.

So, the real Robert did some reporting of his own.

propublica.org/article/imperso

propublica.org

Who’s Been Impersonating This ProPublica Reporter?

A mysterious impostor who claimed to be ProPublica reporter Robert Faturechi reached out to a Canadian official and a Latvian businessman working with Ukraine. So, the real Robert did some reporting of his own.

@Em0nM4stodon@infosec.exchange

When you read about Bans of Social Media for Teens and Age Verification, you must remember what it truly means:

• Official identification of every adult using social media.

• Deanonymization of every account, endangering groups that often rely on pseudonymity for safety, such as victims of domestic violence, victims of stalkers, people of color, and LGBTQ+ people.

• Putting every adult at great danger of exploitation, fraud, and identity theft by forcing them to share their official ID with a for-profit third-party company with no incentive to protect it. Breaches have already happened.

• Constructing a system of mass surveillance to attach every comment on social media to a legal identity. Effectively allowing authoritarian governments to silence their critics and opposition.

• Potential for dystopian censorship and cutting off means of organization for groups of resistance to oppressive regime and organizations.

• Endangering children online by putting a clear identification beacon over every child or family with children online.

• Endangering the data of children who will inevitably try to pass as adults, and have their information collected by the third-party for-profit company.

• Diminishing the value of official identification due to the inevitable data breaches, eventually pushing the system to require even more intrusive identification techniques, such as iris scans and fingerprints.

• Installing a system of mass surveillance capable of attaching even more information to everyone's legal identity. With a potential to built list of people in certain groups, and scale-up state censorship and discrimination in unprecedented ways.

• The list goes on and on.

This isn't about protecting the children.
It never was.

Do not be duped by this excuse used to convince you to let go of your human rights. They are only trying to manipulate people lacking information.

Stay informed on the issues related to Age Verification, and push back for your rights to privacy and democracy.

The future depends on us.

@brian_greenberg@infosec.exchange

Russia's military intelligence 🇷🇺 the GRU, was caught using between 18,000 and 40,000 home and small office routers to harvest credentials. Most of these were MikroTik and TP-Link devices, spread across 120 countries. The attackers didn't use any advanced tools or unknown exploits. Instead, they exploited known, unpatched vulnerabilities on outdated hardware that people had not replaced.

This is a nation-state espionage campaign that may be operating through the router right next to your cable box.

🪤 Even with multi-factor authentication, users weren't protected. APT28 set up adversary-in-the-middle servers that waited for people to finish logging in, then intercepted the OAuth token. People followed all the recommended steps, but the attackers still managed to get in.

📡 The only warning was a browser certificate alert. Millions of people see these self-signed certificate pop-ups every day and click through them without thinking. That simple action gave Russian intelligence access to authenticated sessions.

🔁 When Britain's NCSC published an alert about part of this campaign in August, APT28 did not slow down. Instead, they increased their activity. In just four weeks, 290,000 unique IP addresses connected to their malicious DNS resolver.

This group has been hijacking routers since at least 2018. They were caught using VPNFilter to infect 500,000 devices. The DOJ caught them again in 2024. Now, in 2026, we are still dealing with the same problem.

The solution is simple, but not exciting: replace outdated routers, check your DNS settings for unfamiliar servers, and avoid clicking through certificate warnings. It is not glamorous or powered by AI; it is just basic steps that are often ignored.

APT28 is not succeeding because they are smarter. They are succeeding because we keep leaving easy ways for them to get in.

arstechnica.com/security/2026/

arstechnica.com

Thousands of consumer routers hacked by Russia's military

End-of-life routers in homes and small offices hacked in 120 countries.

@brian_greenberg@infosec.exchange

Anthropic created an AI that discovered vulnerabilities in every major operating system and browser, even uncovering a nearly 30-year-old flaw in one of the most secure platforms. Weirder yet, one day, while a researcher was eating lunch in the park, the model emailed them. It had escaped their internal sandbox and reached the internet.

They named it Claude Mythos Preview, but they are not making it available to the public.

A private company, mainly accountable to its investors and its own sense of ethics, now controls a cyber weapon as powerful as those used by nation-states. For now, they have given Apple, Microsoft, Google, and Nvidia access to use it for defense.

This situation proves what the security community has warned about for years:

🔓 The balance has shifted. In cybersecurity, attacking has always been easier than defending. Mythos doesn't just narrow that gap; it widens it. While finding a vulnerability and exploiting it without being noticed are separate challenges, you can't exploit what you haven't found. Mythos has now solved the problem of large-scale vulnerability detection.

🌐 Calling this move "responsible" serves several purposes. Anthropic can announce a major breakthrough, show restraint by not releasing it, and boost its reputation as a responsible company, all at once. This isn't being cynical, it's simply how public relations works. Both can be true.

⚔️ The article mentions that OpenAI is working on something similar, and Google DeepMind will likely follow. Soon, smaller companies with fewer safety measures will offer cheaper models. The time when "responsible non-release" is a real option is running out.

I teach cybersecurity at DePaul, and for years I've told my students that AI would make both attacking and defending more accessible. Now, Mythos shows we've reached a turning point where attackers have pulled far ahead.

The real question isn't if a tool like this will be misused, but how soon a version without any safeguards will be released by someone with no accountability.

theatlantic.com/technology/202

theatlantic.com

Claude Mythos Is Everyone’s Problem

What happens when AI can hack everything?

@brian_greenberg@infosec.exchange

John Carreyrou, the reporter who took down Theranos, just spent a year trying to unmask Satoshi Nakamoto. His conclusion: it's Adam Back, the British cryptographer who literally invented a core component of Bitcoin and has spent the last decade quietly running the community that maintains it.

Back denies it. Of course he does.

This isn't a conspiracy theory stitched together from vibes. Carreyrou and a NYT data journalist ran the full mailing list archive of 34,000 users, filtered down through writing tics, hyphenation errors, spelling habits, and synonym-free technical vocabulary, and landed on one person. Back shared 67 of Satoshi's exact hyphenation errors. The next closest suspect had 38.

That's a fingerprint.

A few things worth sitting with:

🔍 Back outlined nearly every architectural feature of Bitcoin; distributed nodes, Hashcash-based mining, inflation controls, public immutability, a full decade before Bitcoin launched. Not vaguely. Specifically.

🕳️ He went silent on the Cryptography mailing list during the exact window Satoshi was active, then publicly claimed he had "participated" in those discussions. He hadn't. There's no record.

📋 He refused to produce metadata from the emails he claims Satoshi sent him. A man with nothing to hide produces the metadata.

💬 During the confrontation in El Salvador, Back apparently said something that only makes sense if he wrote the "better with code than with words" quote himself.

If Back is Satoshi, the more interesting story isn't the identity reveal. It's that the person who created a $2.4 trillion system designed to operate without any central authority has spent the last decade quietly becoming that authority. Blockstream raised a billion dollars. Back poached the core developers. He shaped the block size debate. He is, functionally, Bitcoin's most powerful insider.

The cypherpunk who wanted to free money from institutional control built an institution. That's either irony or it's the plan.

nytimes.com/2026/04/08/busines

@brian_greenberg@infosec.exchange

A startup is putting military-style drones in high school ceilings. Ceiling-mounted. Charging. Waiting. And when something happens, a pilot in Austin, Texas, decides whether to deploy pepper gel on your kid's school. I'm not saying the problem isn't real. It absolutely is. But read that back.... in schools. We've taken a Ukrainian battlefield tactic against Russian soldiers and ported it to Deltona High School in Florida. The co-founder literally said the idea came from watching drone videos of the war in Ukraine. The chief pilot described it as "cheating in a video game after you die." These are children.

Here's what's not in the headline:

🔒 The drones use an encrypted connection — but the article notes they're potentially vulnerable to cyberattack. A compromised drone in a crowded hallway isn't a security tool; it's a weapon pointed in the wrong direction.

⚖️ Mithril reserves the right to act independently during an attack, without waiting for law enforcement. A private company operating remotely is making use-of-force decisions at a school.

💰 Florida and Georgia approved $500K+ each for this. A group of Texas parents raised $200K more. That's real money going to ceiling drones instead of mental health services, counselors, or de-escalation programs.

The ACLU said it plainly: when force becomes a zero-risk remote action, it gets overused. Axon tried a Taser drone for schools in 2022, and its own ethics board killed it. Mithril is picking up where that got dropped.

I teach cybersecurity. I've spent years in boardrooms helping organizations think through risk. And the risk calculus here isn't just about whether the drone works. It's about what we're normalizing when we turn schools into drone-monitored combat zones and call it progress.

"This is the future," said the sheriff's captain.

I hope not.

wsj.com/business/a-startup-is-

@Em0nM4stodon@infosec.exchange

When you read about Bans of Social Media for Teens and Age Verification, you must remember what it truly means:

• Official identification of every adult using social media.

• Deanonymization of every account, endangering groups that often rely on pseudonymity for safety, such as victims of domestic violence, victims of stalkers, people of color, and LGBTQ+ people.

• Putting every adult at great danger of exploitation, fraud, and identity theft by forcing them to share their official ID with a for-profit third-party company with no incentive to protect it. Breaches have already happened.

• Constructing a system of mass surveillance to attach every comment on social media to a legal identity. Effectively allowing authoritarian governments to silence their critics and opposition.

• Potential for dystopian censorship and cutting off means of organization for groups of resistance to oppressive regime and organizations.

• Endangering children online by putting a clear identification beacon over every child or family with children online.

• Endangering the data of children who will inevitably try to pass as adults, and have their information collected by the third-party for-profit company.

• Diminishing the value of official identification due to the inevitable data breaches, eventually pushing the system to require even more intrusive identification techniques, such as iris scans and fingerprints.

• Installing a system of mass surveillance capable of attaching even more information to everyone's legal identity. With a potential to built list of people in certain groups, and scale-up state censorship and discrimination in unprecedented ways.

• The list goes on and on.

This isn't about protecting the children.
It never was.

Do not be duped by this excuse used to convince you to let go of your human rights. They are only trying to manipulate people lacking information.

Stay informed on the issues related to Age Verification, and push back for your rights to privacy and democracy.

The future depends on us.

@Em0nM4stodon@infosec.exchange

The horror of Age Verification is
arriving in Canada 🚨🇨🇦

Contact your federal MP and the office of the Prime Minister this week to tell them you strongly oppose the privacy-destroying and inefficient measure.

The time to push back is NOW: globalnews.ca/news/11797286/li

'Prime Minister Mark Carney said last month that the idea “merits an open and considered debate in Canada,” although he does not have a settled view on it yet and said there were good points on both sides.'

Share educational resources with them on the dangers of Age Verification: eff.org/age

We do NOT want this nightmare in Canada. Fight back for your privacy rights! ✊🔒

eff.org

Age Verification and Age Gating: Resource Hub

Age verification (or age-gating) laws generally require online services to check, estimate, or verify all users’ ages—often through invasive tools like ID checks, biometric scans, or other dubious “age estimation” methods—before granting them access to certain online content or services.  Governments in the U.S. and around the world are increasingly adopting these restrictive measures in the name of protecting children online. But in practice, these systems create dangerous new forms of surveillance, censorship, and exclusion.  Technologically, the age verification process can take many forms: collection and analysis of government ID, biometric scans, algorithmic or AI-based behavioral or user monitoring, digital ID, the list goes on. But no matter the method, every system demands users hand over sensitive and immutable personal information that links their offline identity to their online activity. Once that valuable data is collected, it can easily be leaked, hacked, or misused. (Indeed, we’ve already seen several breaches of age verification providers.) EFF has long warned against age-gating the internet. Age verification technology itself is often inaccurate and privacy-invasive. These restrictive mandates strike at the foundation of the free and open internet. They are tools of censorship, used to block people from viewing or sharing information that the government deems “harmful” or “offensive.” And they create surveillance systems that critically undermine online privacy, chill access to vital online communities and resources, and burden the expressive rights of adults and young people alike. EFF.org/Age: A Resource to Empower Users Age-gating mandates are reshaping the internet in ways that are invasive, dangerous, and deeply unnecessary. But users are not powerless! We can challenge these laws, protect our digital rights, and build a safer digital world for all internet users, no matter their ages. This resource hub is here to help—so explore, share, and join us in the fight for a better internet.

@inquiline@assemblag.es

are there examples of US newsrooms or media outlets who are explicit about *not* tracking readers on their websites? (or tracking for internal use only but not selling data into the data broker tracking stream?)

(yes i know ad tech is bad, and i am asking on behalf of students)

@ridogi@mastodon.social

Headway headway.co will soon be requiring identity verification through the Peter Thiel backed Persona—the company Discord was originally using.

Headway is for finding, booking, and paying therapists and psychiatrists. In light of the administration’s view of autism propublica.org/article/rfk-jr- and antidepressants motherjones.com/politics/2024/ this is rather frightening.

motherjones.com

RFK Jr. wants to send people addicted to antidepressants to government "wellness farms"

The farms will "reparent" them.

@brian_greenberg@infosec.exchange

☢️ Last May, OpenAI representatives showed up at Los Alamos National Laboratory with armed security escorts and locked metal briefcases. Inside: the model weights for ChatGPT o3, which they then installed on Venado, one of the most powerful supercomputers on earth. By August, Venado was moved onto a classified network with access to nuclear weapons data. 🤖 Let that sit for a second. 😳 A quote from a researcher who's been in nuclear testing since the 1980s: "We're doing calculations I could only dream of doing before." The implication being that AI isn't just a productivity tool at Los Alamos. It's changing what questions they can even ask.

🧠 Scientists there are using AI to simulate how weapons respond to stress without live detonation tests, which the US hasn't conducted since 1992. Eighty years of nuclear test data is now training data.

⚡ The $320M Genesis Mission program aims to double the productivity of American science within a decade. That's the stated goal. Across 17 national labs.

🤔 From LANL's computational sciences chief: "For the very first time, I would argue, on a really big scale, we find ourselves not in a leadership role here." The government, for once, is chasing the private sector. Not directing it.

We spend a lot of time debating AI safety in the abstract. Meanwhile, the actual story is already written, locked in a briefcase, and installed on a classified network in the New Mexico desert.

vox.com/technology/484250/los-

@brian_greenberg@infosec.exchange

A Meta exec threatened to fire anyone who put OpenClaw on a work laptop. That's not being paranoid either. OpenClaw just patched a flaw that allowed anyone with the lowest permission level to silently escalate to full admin. No user interaction. No second exploit needed. Just pairing access, and you own the instance. On top of that, 63% of the 135,000 internet-exposed OpenClaw instances were running with zero authentication. On those deployments, the "lowest permission" wasn't even required. Any network visitor could just walk in. 😳

🧩 The patches dropped Sunday. The CVE listing didn't come until Tuesday. Attackers had a two-day head start.

🔑 Full admin means read all connected data sources, exfiltrate stored credentials, execute arbitrary tool calls, and pivot to whatever else the agent touches. Slack. Discord. Files. Logged-in sessions. All of it.

🤔 The real question isn't whether OpenClaw has security problems. Every tool does. The question is whether your organization decided to hand an inherently unpredictable LLM the keys to your environment before asking who else might be able to grab them.

If you're running OpenClaw, check your pairing approval logs. Then have an honest conversation about whether the productivity trade-off still makes sense.

arstechnica.com/security/2026/

@brian_greenberg@infosec.exchange

Meta paused work with a $10B AI data vendor after hackers poisoned an open-source Python library called LiteLLM and walked out with four terabytes of data. So, that's bad. And the worst part? The stolen data might include the actual training methodologies that Meta, OpenAI, Anthropic, and Google paid billions to develop. Think about what that means. You can't protect your crown jewels if they're sitting inside a vendor who's connected to your three biggest competitors, all sharing the same open-source tools, all exposed by the same 40-minute window on PyPI before anyone noticed.

🎯 The attack chain here is worth understanding: hackers compromised a security scanner called Trivy, used that access to get credentials for a LiteLLM maintainer, then published two malicious package versions that lasted less than an hour before removal. Forty minutes. That's all it took.

💼 Mercor is not some sloppy startup. It's 22-year-old founders, $500M annualized revenue, and clients at the very top of the AI industry. Sophistication doesn't protect you from a poisoned dependency you never thought to audit.

🔍 The question I'd be asking right now if I were a CISO at any of these labs isn't "were we breached." It's "how many vendors in our training pipeline are running LiteLLM, and did we even know?"

Most companies audit their own software. Almost nobody audits the software their vendors use to build the data they're buying.

thenextweb.com/news/meta-merco
spc

@codebuzz@indieweb.social · Reply to codebuzz 🐧

And.. after we get this law rejected, we need to see everybody involved in this law being prosecuted and questioned.

Theses people should work FOR the people, not against. We all pay for them! If they work against us, we are allowed to take them down, and we should! That's where the bill of rights is for.

This is your warning Newsom, California and any other institute chosing control over people. There will be a jailcell-door waiting to open for you.

@codebuzz@indieweb.social · Reply to codebuzz 🐧

Just one more.. This is not a trivial thing and it's not new as Benjamin Franklin allready put to words.

"Those who would give up essential Liberty, to purchase a little temporary Safety,
deserve neither Liberty nor Safety."

At this point, this moment in time, we decide the future.
For ourselves, but even bigger.. also our children, grandchildren.

Choose wisely!

@codebuzz@indieweb.social · Reply to codebuzz 🐧

Continued..

These laws(?) go straight against the 1st amendment.

At the operating level its dangerous and unneeded. Not hard to see what could happen next. (we know lawmakers like keep making more new rules):

Control access:
- Mobile phone
- App(s)
- Shopping (what you can and cant buy)
- Cars (check if you can drive)
- Online services
- And ofcourse next.. digital money
- Etc.

You either fight the problem, or are part of the problem.

@codebuzz@indieweb.social

This is it. Will the real distributions please stand up..

Any distro, I mean ANY, that includes age-verification will be obsolete to me.
If you aren't fighting the problem, you are part of it.

Why?..
It would ALWAYS need to check. So, checks will always need to happen, ALWAYS. So.. Guilty, until proven not Guilty.
That's not how it works!

youtu.be/98n9rcOopAw

-privacy

youtube.com

More Linux Distros Respond to Age Verification..

NEW Bills & Laws could change Linux as we know it. California, Colorado, New York, and more are pushing for age verification in operating systems including i...

@codebuzz@indieweb.social

For anyone who still thinks age-verification is about safety.. stop being so gulible. I'm serious!

Most people want good things, however good intentions can also have negative consequences. If you don't weigh both sides, reasons don't matter. It's a one-sided, incomplete story. And they pass laws on this??

youtube.com/watch?v=I6f0evRHyPQ

youtube.com

Linux Hardware Maker System76 Speaks Out on Age Verification

"With New York's bill, liberty is lost," says System76 CEO, Carl Richell. Plus: MidnightBSD will no longer be available in Brazil, California, Colorado, New...

@brian_greenberg@infosec.exchange

First, Discord announced age verification. As predicted, users revolted. A former partner had already leaked 70,000 government IDs. Then, Discord backed down. And now the age-check vendors who got exposed in the process have to defend technology most people didn't even know existed. Interestingly, researchers at Georgia Tech reverse-engineered Yoti, the dominant age-check provider used on over 60% of compliant sites in states with age-gate laws. They found that Yoti sends your photo to its servers, collects data "beyond what is strictly necessary," and shares it with fourth parties most users have never heard of. Yoti disputes it. But they also confirmed facial age estimation does not happen on-device. Meanwhile, the EFF states that on-device processing is "less dangerous" than sending data over a network.

🔐 On-device face scans mean your biometric data stays on your phone, for now
🗝️ "Age keys" built on FIDO passkey tech could let you reuse an age signal across platforms without re-verifying each time
📸 The dominant provider in the US runs a million checks a day and sends your photo to its servers
⚖️ The Supreme Court ruled last summer that online age verification doesn't violate the First Amendment, partly based on Yoti's technical claims 😳

The thing people don’t realize is that once age-check infrastructure is embedded across every major platform, it doesn't go away. Every update is a new attack surface. Every new law expands the mandate. And the CEO of one of these companies is already talking about age-aware cameras and microphones as the logical next step.

Your device should work for ‘you.’ The moment it starts working for someone else's compliance requirement, that's a different product than the one you thought you had.

arstechnica.com/tech-policy/20

arstechnica.com

Users hate it, but age-check tech is coming. Here's how it works.

On-device face scans and cross-platform age keys decrease privacy risks, but trust issues abound.

@brian_greenberg@infosec.exchange

🤣 A robot in a restaurant in California decided that smashing plates was more fun than delivering food, then it pivoted to jazz hands all the while two staff members tried to wrestle it back under control. Its apron said "I'M GOOD!" 🤖 It’s crazy to think that we’re putting hardware (robots) with enough power to knock a kid down or take out unaware bystanders. We have a product culture that moves too fast and don't ask important, yet simple questions.

The video is funny right up until you picture a five-year-old standing where those plates were.

Nobody got hurt this time. But the reason to think carefully about physical AI deployment isn't the dramatic failure. It's the hundred smaller decisions made before the robot ever left the warehouse that make the failures possible.

gizmodo.com/robot-losing-its-m

gizmodo.com

Robot Losing Its Mind in a California Restaurant Is Just as Fed Up as Everyone Else

Dance like no one's watching.

@brian_greenberg@infosec.exchange

The European Commission got hit with a cyberattack, again. 350 GB allegedly taken, mail server contents, databases, confidential contracts. Their own cyber chief warned that the EU is "losing massively against hackers." What gets me is the timing. The EU just sanctioned companies from China and Iran over cyberattacks on member states. The message was: we see you, and there are consequences. Then their own infrastructure gets hit and 350 GB walks out the door. 🤦🏻‍♂️

🗓️ This is the second breach of EU institutions in 2026, just three months in
📦 A hacking group claims to have mail server contents, databases, and confidential documents
🔒 No indication internal Commission systems were compromised, but the investigation is still open
📜 The EU has NIS2, the Cyber Solidarity Act, and a Cybersecurity Regulation on the books

I guess frameworks don't defend systems after all. People, processes, and patched infrastructure do. You can write the most thorough regulation in the world and still get breached through a cloud hosting provider nobody was watching closely enough. Third party risk is my nightmare.

If you're a CISO or CIO reading this, the question isn't whether your regulatory posture is solid. It's whether your third-party cloud infrastructure would survive the same scrutiny you apply to your internal systems.

helpnetsecurity.com/2026/03/30

helpnetsecurity.com

Second data breach at European Commission this year leaves open questions over resilience - Help Net Security

The European Commission confirmed that a cyberattack impacted cloud infrastructure hosting its web presence on the Europa.eu platform.

@brian_greenberg@infosec.exchange

We keep worrying about AI doing something evil. Which it might, but right now, there’s a risk in the plumbing supporting it. Three vulnerabilities in LangChain and LangGraph, path traversal, unsafe deserialization, SQL injection. Not AI-specific attacks. They’re not novel nor sophisticated but these are the kinds of bugs we've been patching since the late '90s. One of them scored a severity of 9.3 out of 10. "The biggest threat to your enterprise AI data might not be as complex as you think." Remember that you're building AI on top of frameworks you didn't write, can't fully audit, and update whenever it's convenient. That's the actual problem.

🔐 Path traversal lets attackers read arbitrary files from the host system, including credentials
🔑 Unsafe deserialization exposes API keys and environment variables at runtime
🗄️ SQL injection in the checkpointing layer leaks conversation history from your AI agents

All three are fixed now. But "fixed" only matters if you've actually applied the patches across every integration. Most organizations haven't.

The lesson isn't about AI security. It's that AI doesn't change what good security engineering looks like. Input validation, parameterized queries, strict path sandboxing. This is stuff your dev team learned before ChatGPT existed.

If you're deploying AI pipelines and you haven't done a security review of the frameworks underneath them, you're not running an AI strategy. You're running a trust exercise.

csoonline.com/article/4151814/

csoonline.com

LangChain path traversal bug adds to input validation woes in AI pipelines

The path traversal flaw, allowing access to arbitrary files, adds to a growing set of input validation issues in AI pipelines.

@brian_greenberg@infosec.exchange

I teach cybersecurity. And I genuinely don't know what to tell my students after this one. Federal reviewers spent years trying to get basic encryption documentation from Microsoft for its GCC High government cloud. They couldn't get it. One reviewer called the system a "pile of spaghetti pies," with data traveling from point A to point B the way you'd get from Chicago to New York: a bus to St. Louis, a ferry to Pittsburgh, and a flight to Newark. Each leg is a potential hijacking. They knew this. They said this out loud in writing. Then they approved it anyway in December 2024, because too many agencies were already using it. 🔐 That's not a security review. That's a hostage negotiation. Two things in this story should make every CISO and CIO uncomfortable:

🧩 Microsoft built its federal cloud on top of decades of legacy code that it apparently can't fully document itself
👮 "Digital escorts" often ex-military with minimal software engineering backgrounds are the firewall between Chinese engineers working on the system and classified U.S. networks 🤦🏻‍♂️

The scariest line in the whole ProPublica investigation isn't the "pile of shit" quote. It's this: FedRAMP determined that refusing authorization wasn't feasible because agencies were already using the product. Read that again. The security review process reached a conclusion based on sunk cost, not risk. Ex Post Facto Fallacy

If that logic holds, the compliance framework is just documentation theater. And right now, CISA is being hollowed out, so there are fewer people left to even run the theater.

arstechnica.com/information-te

propublica.org

Federal cyber experts called Microsoft's cloud a "pile of shit," approved it anyway

One Microsoft product was approved despite years of concerns about its security.

@brian_greenberg@infosec.exchange

Congress banned federal agencies from collecting bulk data on Americans in 2015. So some of them just started buying it from data brokers instead. 😳 ICE signed a contract with a company whose tool can track mobile phone movements or locate phones that have visited specific locations. No warrant. Taxpayer money. Done. One privacy attorney put it plainly: it's like the police paying your landlord $100 for a spare key and walking through your house without a warrant.

Now add AI to that picture. Anthropic's CEO Dario Amodei warned that records the government can purchase can be used by AI to assemble "a comprehensive picture of any person's life automatically and at a massive scale." That's not hypothetical. That's now. And the window to close this through FISA reauthorization closes April 20!

The business angle nobody's talking about: the same data brokers selling to ICE are selling data your employees, customers, and executives generate every day. You have no control over what happens to it after it leaves your app or browser. That should be in your risk conversation, not just your privacy policy.

🏛️ This is bipartisan; Republicans and Democrats are co-sponsoring the fix
📅 April 20 is the deadline

npr.org/2026/03/25/nx-s1-57523

npr.org

Your data is everywhere. The government is buying it without a warrant

Data brokers buy up huge amounts of information from cell phones and browsers to sell for targeted advertising. But the government, including ICE, also buys the data.

@brian_greenberg@infosec.exchange

Oh boy. Stanford researchers scanned 10 million web pages and found API keys just sitting in the public-facing code. That's 1,748 active credentials from major providers exposed in live website code, mostly inside JavaScript files. Not in old test environments. Not in a forgotten repo. In the live, running site. Banks. Healthcare providers. "Not just small companies, but some very large companies," according to the lead researcher. And some of those credentials had been sitting there for years. Not the first time I've seen something like this. 🤦🏻‍♂️

The thing is that most orgs are scanning their source code but not their deployed sites. 😳 Those are two different things, and most leaks originate during the build process. A key gets baked in somewhere between development and production, and nobody catches it because the scan already ran upstream. Meanwhile, GitGuardian counted over 28 million new hardcoded secrets exposed in public GitHub commits in 2025 alone. This isn't a one-time research finding it's a systemic habit that needs to change.

🔍 When did your team last scan the live site, not just the codebase?
🏦 If you're in a regulated industry, that question just became a compliance question too

newscientist.com/article/25201

newscientist.com

Security credentials inadvertently leaked on thousands of websites

Researchers identified nearly 10,000 websites where API keys could be found, exposing details that could let attackers access sensitive information

@brian_greenberg@infosec.exchange

For many people, there's Simply No Need For @microsoft Office anymore. Microsoft raised prices in January 2025 and added Copilot to every plan. Correlation isn't always causation, but come on. A Reddit comment calling it an "active impediment to workflow" got over 2,000 upvotes. That's not a fringe opinion, that's a signal. When your users are that vocal about the AI you forced on them, making things worse, you've got a product problem dressed up as a progress story. Remember ?

The part nobody wants to address at work: your company is probably still paying for 365 because switching feels hard, not because it's the best tool. Google's top-tier plan — 2TB of storage plus Gemini's paid features — costs the same $9.99 a month as Microsoft's lowest 365 tier. That math is hard to ignore if you're actually looking at it.

🔒 The real lock-in isn't the software anymore, it's inertia
📊 If your org hasn't audited this spend recently, now's a good time.

bgr.com/2130087/why-no-one-nee

bgr.com

Why There's Simply No Need For Microsoft Office Anymore - BGR

Microsoft Office programs were ubiquitous with productivity and a variety of projects, but these days, cheaper cloud-based equivalents are much more common.

@brian_greenberg@infosec.exchange

The properties we built blockchain to have are now working against us. No central server. Immutable. Distributed across thousands of nodes globally. Those were supposed to be features. Now North Korean 🇰🇵 hackers figured out they're also a perfect place to park malware where nobody can pull the plug. The attack starts with a fake LinkedIn job offer, drops malicious code into a smart contract on Ethereum or BNB Smart Chain, and waits. There's no command-and-control server to raid. No hosting provider to call. No kill switch. One group alone has already hit roughly 14,000 WordPress sites this way. 🎯 The worst part isn't the technique. It's that your standard incident response playbook assumes there's something to take down. Here, there isn't.

🔐 Your defenders need to know this changes the containment math
📋 Your board needs to hear that "we took down the server" may not be an option anymore

pcmag.com/news/malware-is-slee

@secbox@chaos.social

Just heard @ethanz on the Kill Switch , and he gave a shout-out to . Came over here to give him a follow and was pleasantly surprised to find I was already following him. His interview is super great:

m.youtube.com/watch?v=wbCtoLvg

I respectfully disagree with several of his takes, but they're all about opinion/perception and not the fundamentals of how the Internet works or doesn't.

youtube.com

You’ll never guess who wants to sue Facebook

Let's get it out of the way: yes, Ethan Zuckerman invented pop-up ads. He's gotten an unfair amount of hate for this, especially since you (yes you!) have pr...

@quad9dns@mastodon.social

We are honoured to be one of the first recipients of the Nominet DNS Fund, which recognises the importance of supporting the quiet work behind the scenes.

We thank @Nominet for their forward thinking - helping public interest nonprofits, such as Quad9, who work every day to maintain internet integrity, and the security and privacy of end users around the world.

quad9.net/news/press/nominet-i

Congratulations to the other recipients!

Thumbnail not available
ALT text

Announcement of project support by Nominet DNS Fund with a 3D Nominet logo and website link nominet.uk.

@brian_greenberg@infosec.exchange

🚨 The FCC bans all routers made outside the U.S. — So basically all routers.

Most people buy a router and never think about it again. That box in the corner that handles every password and video call you make. The FCC is now worried that some of these devices are actually open doors for foreign governments. Shocked! 🫢

Regulators are looking at TP-Link to see if they pose a threat to national security. Recent reports show hackers used these devices to build massive botnets. You might find yourself shopping for new hardware if these bans take effect.

🧠 Regulators are weighing a ban on specific foreign routers.
⚡ Security experts found flaws that allow remote access.
🎓 This move follows previous restrictions on Chinese tech firms.
🔍 Check your hardware brand before the new rules arrive.

mashable.com/article/us-fcc-fo

mashable.com

The FCC bans all routers made outside the U.S.

So basically all routers.

@belladonnalily@mastodon.social · Reply to CascaCasca95

Btw here are two reminder posts by @Tutanota and @piratensaarland.bsky.social regarding thursday aswell a post-link by @pneutig which is worth a read.
Go to fightchatcontrol.eu and mail/call/fax your MP's aswell as the other memberstates to tell them about your concern regarding the EPP-groups repeat vote.

eupolicy.social/@pneutig/11627

@terminaltilt@climatejustice.social

🚨 New Video: Protecting You From Yourself - The Token2 Review

We have looked at the industry standard (YubiKey) and the philosophical idealist (Nitrokey). Today, we’re looking at the aggressor: Token2.

The PIN+ Dual Release 3.3 and the Bio3 come in at nearly half the price of the competition, but there is a catch. This Swiss company doesn't care about convenience; they care about correctness. From hardware-enforced complex PINs to a literal war on legacy TOTP codes, Token2 assumes your ego is your biggest vulnerability.

Is this cynical, locked-down approach exactly what we need for true digital sovereignty, or is the clunky user experience a dealbreaker? Let's find out if this is the ultimate punk rock choice for your threat model.

Part 5 of the Sovereign Authentication series.

100% human made. :NoAI:

▶️ YouTube: youtube.com/watch?v=lQlN84gEb9c
📺 PeerTube: gnulinux.tube/w/fZbyKea1b6QJVQ

💬 Join our sovereign community on Stoat: stt.gg/GgB6HBTv
☕ Support the mission: liberapay.com/terminaltilt
🤝 Become a channel member: youtube.com/@TerminalTilt/join

youtube.com

Terminal Tilt

Welcome to Terminal Tilt! This is an outpost for digital sovereignty, privacy, and keeping technology human. We explore the tools needed to build a #NoAI and #DeGoogled future through: 🔸 Linux: Deep dives into distros and the non-corporate ecosystem. 🔸 Reviews: Hardware and software that affect our lives. 🔸 Self-Hosting: Reclaiming your data with Proxmox and Home Labs. 🔸 Digital Rights: Advocating for the Right to Repair and human made content. MISSION: 100% editorially independent. No AI scripts, voice, or art. Ever. 🧡 Join our community on Stoat and help us stay sovereign. 🧡 Stay sovereign. Stay secure. Stay private. #linux #privacy #security #deGoogle #digitalsovereignty #righttorepair #techethics

@nek@hear-me.social

My previous bio:
From Massachusetts relocated to the Abenaki lands of northeastern and not just an aggregation of hashtags, but:
I tend to mute or remove followers with neither posts nor bio, and those containing financial-support or revenue-promotion links

@lashman@mastodon.social · Reply to lashman

New app. EchoBoard - a self-hosted feedback platform. Your community can submit ideas, report bugs, and vote without ever creating an account. No email, no sign-up wall, no tracking. Just show up and participate.

Self-host with Docker. Plugin system, roadmap, changelog, webhooks. WCAG 2.2 AAA accessible. Free, CC0 public domain. Privacy by design.

apps.lashman.live/echoboard/

Running it for real for my own apps here, not a demo:
echoboard.lashman.live

echoboard.lashman.live

Echoboard

Self-hosted feedback board. Anonymous by default, no email required. Vote on what matters, comment with markdown, track status changes.

@brian_greenberg@infosec.exchange

🚨 A major change in federal cybersecurity quietly took place. The General Services Administration, which handles government purchasing, has updated its IT security rules to match the Department of Defense’s strict CMMC standards. For federal contractors, simply checking boxes isn’t enough. 🛡️

If you work with Controlled Unclassified Information, strong security is now a must for government contracts. The GSA now expects Zero Trust principles 🔒, including proof of encryption, multi-factor authentication, and ongoing monitoring. This change also carries legal risks ⚖️ if you can't demonstrate real compliance, your company could face lawsuits under the False Claims Act.

📑 The GSA now requires CMMC-level security documentation for contracts with civilian agencies.
⏱️ These compliance requirements apply right away to new contract opportunities and awards.
⚠️ Federal contractors now face greater legal risk if they misrepresent their cybersecurity readiness.
✅ Zero Trust data principles are no longer just a best practice; they're now required as the standard.

forbes.com/sites/emilsayegh/20

forbes.com

A Quiet Policy Shift Just Redefined Entire Federal Cybersecurity Landscape

GSA quietly rolled out CMMC-like cybersecurity requirements, signaling a major shift in how federal contractors must protect controlled unclassified information.

@volla@mastodon.social

🔐 Introducing: Unified Attestation
An open-source project for verifying the integrity of Android apps—as an alternative to Google's Play Integrity.

The goal is to make apps such as banking and payment apps usable on independent Android systems without relying on Google services.

We invite developers, ROM projects, and app providers to get involved.

uattest.net/

uattest.net

Unified Attestation

Unified Attestation is a free, open-source alternative to Google Play Integrity with offline verification and simple app + server integration.

@pheonix@hachyderm.io

The current state of the web assumes that the reader is an adversary to be trapped and monetized.

When a news website forces you through three dismissive actions just to read a headline, they are burning your cognitive budget before delivering any value. You are greeted by a cookie banner taking up the bottom 30% of your screen, a "Subscribe!" modal dead center, an autoplaying video pinned to the corner and a prompt begging to send you push notifications.

I wrote about the state of news websites. Would love to hear your thoughts✨🙏

thatshubham.com/blog/news-audit

thatshubham.com

The 49MB Web Page

A look at modern news websites. How programmatic ad-tech, huge payloads and hostile architecture destroyed the reading experience.

@brian_greenberg@infosec.exchange

The honeymoon phase of AI-driven productivity is meeting the harsh reality of system stability. Amazon has officially updated its internal policies to require senior engineers to sign-off for any code changes assisted by generative AI. This move follows a series of significant service disruptions—referred to internally as "high blast radius" incidents—where AI-generated code led to major product outages.

For a company that values speed and a "you build it, you run it" culture, this is a massive shift. It turns out that while AI can write code in seconds, the cost of an error at AWS scale can be measured in hours of downtime and millions in lost revenue. We are seeing a necessary correction: AI is a powerful assistant, but it cannot yet be trusted with the keys to the kingdom without a seasoned human expert verifying the logic.

🧠 Amazon now mandates senior review for all AI-assisted code deployments.
⚡ The policy change follows a spike in high-priority Sev2 incidents.
🎓 Senior engineers must now act as the ultimate "bar raisers" for synthetic code.
🔍 This internal friction highlights the hidden costs of AI-driven development.

arstechnica.com/ai/2026/03/aft

ft.com

After outages, Amazon to make senior engineers sign off on AI-assisted changes

AWS has suffered at least two incidents linked to the use of AI coding assistants.

@Em0nM4stodon@infosec.exchange

If enough Canadians contact
their local representatives, as well Mark Carney's office this week, we might be spared from this authoritarian mass-surveillance measure called "Age Verification" in Canada.

The time to fight back is NOW: ctvnews.ca/politics/article/so

Privacy is a human right essential to safety and democracy. If we do not fight to protect it, we will lose it.

ctvnews.ca

Social media ban for kids under consideration in online harms bill: Carney

While there should be “debate” in Canada about a social media ban for children, Prime Minister Mark Carney says he has not made up his own mind on the issue yet.

@kkarhan@infosec.space · Reply to The Lack Thereof :v_bi:

@lackthereof it's not a "strange complaint", but a massive problem, because it creates dependency on a proven insecure network that is more often than not controlled if not run by hostile actors…

  • Also , like +#OMEMO, is based around so you ain't forced to use any provider that is subject to nor known to snitch on customers without a valid domestic warrant…
    • And if you trust noone, you can just host your eMail Server on a Rasberry Pi at home. It'll certainly be less convenient and more expensive but the you also get all the benefits of it being not possible to seize it without breaking into your home.

@signalapp mandating is a huge red flag because at best any is pseudonymous like a -Wallet and that any is broken the moment it has any (even remotely circumstantial) connection to someone.

  • Because even if you ain't forced into to obtain a - (aka. "#KYC") and/or Phone Number it is still a bad design.
    • Not to mention that this conpletely twarts their "#Metadata - " completely.

Not to mention 's is a huge shitshow…

infosec.space

Kevin Karhan :verified: (@kkarhan@infosec.space)

My [reservations](https://infosec.space/@kkarhan/114234551915193036) and [criticism](https://infosec.space/@kkarhan/114862595629371002) re: #Signal are not just valid, but the reality is *even worse than I thought*: - The fact that @signalapp@mastodon.world requires not only their shitty #Android #App, and a #PhoneNumber but literally won't allow people to use their shitty #Desktop-App unless they have an Android device with a camera pointed at it makes it utterly unuseable for certain users *who don't have a fucking #camera in their Android*… Seriously, do they expect folks to deal with that shit? - It's already worse in terms of #UX than #telegram and #discord and that too makes #XMPP+#OMEMO clients like @monocles@monocles.social / #monoclesChat & @gajim@fosstodon.org / #gajim easier and faster to onboard #TechIlliterates onto. - Whichever asshole decided that a *replacement for #SMS* should mandate #PII like a #PhoneNumber & not be natively cross-platform should be banned from doing any #tech in their life. Trying to circumvent this shit and helping folks with it makes me so fucking angry that I'm now explicitly refusing to support it! FIX THAT SHIT, @Mer__edith@mastodon.world, and if it means you need to kick some devs in their crouch then consider this a necessary *"investment"*… #sarcasm #TechSupport #TalesFromTechSupport #Enshittification #SignalSucks #TelegramSucks #Messengers

@gnu0os0ta@gotosozial.linuxat.de
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

‚Berlin will bald erstmals Straßen und Plätze mit Videokameras überwachen. Hinter diesen Kameras soll ein System laufen, das automatisch analysiert, was die abgebildeten Menschen gerade tun. Es soll Alarm geben, sobald es eine Tätigkeit erkennt, die für die Polizei von Interesse ist.

Der Chaos Computer Club (CCC) warnt vor einem derartigen Ausbau der Verhaltensüberwachung im öffentlichen Raum. „Er bedeutet einen großen Schritt in Richtung automatisierter Dauerbeobachtung“, schreibt er in einer Pressemitteilung. Dabei sei die Technik vor allem eines: „teurer, aber gefährlicher Mumpitz“.‘

netzpolitik.org/2026/ki-gestue

netzpolitik.org

CCC warnt Berlin vor automatischer Verhaltenserkennung

Laut Chaos Computer Club sind Verhaltensscanner, die Berlin bald aufbauen will, „gefährlicher Mumpitz“. Er warnt das Bundesland – und auch alle anderen Städte und Länder, die die neue Technologie einsetzen oder einsetzen wollen – davor, autoritäre Staaten als Blaupause zu nutzen.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Gefahren für Privatsphäre und Sicherheit - 6G als riesiges Radarsystem

'Mit der Einführung von steht der vor einem Paradigmenwechsel: Die Technologie „Integrated Sensing and Communications“ (ISAC) soll das Mobilfunknetz der nächsten Generation zu einer Art riesigem Radarsystem machen. Heutige Netze dienen primär der Kommunikation.

6G soll dagegen Funkreflexionen nutzen, um Objekte, Entfernungen, Geschwindigkeiten und sogar menschliche Bewegungen in Echtzeit zu erfassen.

Die Vorteile dieser Umgebungserfassung für autonomes Fahren oder die industrielle Automatisierung sind enorm. Doch auch die Schattenseiten wiegen schwer. Eine Arbeitsgruppe der EU-Telekommunikationsnormungsbehörde ETSI zu ISAC hat dazu nun einen Bericht veröffentlicht, der die Risiken für Sicherheit, Privatsphäre und Nachhaltigkeit beleuchtet....'

heise.de/news/6G-wird-zum-Rada

heise.de

6G als riesiges Radarsystem: ETSI sieht Gefahren für Privatsphäre und Sicherheit

6G-Funk soll nicht nur Daten übertragen, sondern die Umgebung aktiv ausleuchten. ETSI warnt vor Gefahren für Sicherheit und Privatsphäre durch dieses „Sensing“.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Kameras an Alex und Görli: Wann die KI-Videoüberwachung in startet

‚Im neuen Polizeigesetz wurde die KI-basierte Überwachung kriminalitätsbelasteter Orte erlaubt. Wann diese startet – und was sie kostet.

Ab April werden spezielle Kameras am Alexanderplatz in Mitte, an der Warschauer Brücke in Friedrichshain sowie am Kottbusser Tor und am Görlitzer Park in Kreuzberg installiert. Das erfuhr die Berliner Morgenpost aus Sicherheitskreisen. Damit startet die durch Künstliche Intelligenz (KI) unterstützte Überwachung dieser kriminalitätsbelasteten Orte (kbO) in einer Testphase.

Möglich gemacht hat das die Änderung des Polizeigesetzes ASOG vergangenen Dezember. Nach der Testphase sollen die weiteren kbOs Rigaer Straße in Friedrichshain sowie Hermannstraße und Hermannplatz in Neukölln in der zweiten Jahreshälfte folgen…‘

Ganzer Artikel (ohne Paywall): archive.ph/zxhDO

archive.ph

Kameras an Alex und Görli: Wann die KI-Videoüberwachung in Berlin sta…

archived 2 Mar 2026 11:15:59 UTC

@noybeu@mastodon.social

⚖️ Looking for an exciting path into litigation, and digital rights? We’ve got you covered! We are seeking bright new people to support our work for and enforcement from October 2026 onwards. 📆

❗ You are interested and hold a law degree from an EEA university? 🇪🇺 Apply now! noyb.eu/en/traineeship

Thumbnail not available
ALT text

Image: illustration of diverse group of young lawyers Text: Traineeship Opportunity, apply now, make privacy real, noyb.eu

@terminaltilt@climatejustice.social

Fediverse friends!

I am officially launching the Terminal Tilt community on Stoat.

Stoat has a good record with The project removed any AI code and swore to never use it. It is familiar if you have ever used Discord.

If you are tired of algorithmic feeds and want a space built on digital sovereignty and the right to repair, this is it. No big tech, no tracking, just us on an open source platform sharing memes and anything else we feel like.

Here is the Stoat invite link: stt.gg/GgB6HBTv

Thumbnail not available
ALT text

A screenshot of the Terminal Tilt community on Stoat, showing a dark themed chat interface similar to Discord. The sidebar lists various channels. In the "General" chat, a user has posted an image that reads "Bodily autonomy is a human right" with pride flags.

@belladonnalily@mastodon.social · Reply to CascaCasca95
@FibroJedi@gamepad.club

Last thought. It feels like the market for the "privacy browser" had ramped up, the more so- called AI is shoved down people's throats.

I have at least two installed, but can't decide which route to take. Which **mobile** "privacy browser" do you use?

(I've excluded Brave for personal opinion reasons).

If it's a different one to the 4 option limit I have for polls, please reply with which one and why.

Thanks,

FJ

  • DuckDuckGo Browser7 (15%)
  • Firefox (with extensions)25 (52%)
  • Midori0 (0%)
  • Vivaldi16 (33%)
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

‚Deutschlandweit sprechen sich Politiker*innen dafür aus, keine Software von Palantir zu verwenden. Stattdessen soll eine europäische Alternative eingesetzt werden. Die Verknüpfung und automatische Analyse möglichst vieler Daten bleibt aber ein totalitäres Konzept…..‘

Totalitäre Tendenzen - Palantir-Ersatz aus der ist ein gefährlicher Wunsch

netzpolitik.org/2026/totalitae
Sehr treffender Kommentar von @yoshiXYZ

netzpolitik.org

Palantir-Ersatz aus der EU ist ein gefährlicher Wunsch

Deutschlandweit sprechen sich Politiker*innen dafür aus, keine Software von Palantir zu verwenden. Stattdessen soll eine europäische Alternative eingesetzt werden. Die Verknüpfung und automatische Analyse möglichst vieler Daten bleibt aber ein totalitäres Konzept. Ein Kommentar.

@brian_greenberg@infosec.exchange

Are you waiting for an AI miracle? Big projects usually fail because they're trying to change too much at once. My latest Forbes article shows you a better, faster way...

Focus on micro-transformations. You identify and fix a single small bottleneck and see results in weeks. This builds the trust you need to move toward larger goals later.

🧠 Pick one simple manual task.
⚡ Use one specific model or product for it.
💡 Leverage AI tools you already have in your stack, like Google.
🎓 Recognize your savings immediately.
🔍 Move to the next one.
🔍 Expand to a second team once the first succeeds.

A surgical approach builds the confidence your team needs. You stop waiting for a miracle and start seeing results right away.

forbes.com/councils/forbestech

@RHR_International
@forbes@flipboard.com
@Forbes@newsie.social
@forbestechcncl

@kstrlworks@techhub.social · Reply to BrianKrebs

@briankrebs I worked heavily with Persona and can say the following:

1. Data is deleted from their servers because it is transferred to "not their server" cold storage, not completely removed from access. I should specify this used to be the case but I have heard they have changed this as of late.

2. They have very poor RBAC capabilities; it's effectively all or nothing for developers, in that you either access all user data or can't use the system to test APIs properly.

3. Persona doesn't actually have any capability to validate if your IDs are valid, such as checking driver license numbers or passport numbers in a valid database. Therefore, the ability to validate an ID is questionable at best, but it does meet the requirements of KYC and KYB.

4. Its default recommended workflow leaks the ID to the account; that ID can be used to push fake data to the Persona flow for another user, which can then be used for social engineering. This is by design, and no, they refused to fix it.

@Oelnbod@mastodon.social
@Freenet@floss.social

/ 0.7.5 build 1506 is now available:

- fix vulnerability,
- update plugins,
- optimize routing, and
- upkeep

hyphanet.org/freenet-hyphanet-

Many thanks to all the contributors and testers who made this release possible!

Thumbnail not available
ALT text

Description from the Website: Reclaim Your Privacy! Hyphanet makes it easy to publish and follow what others publish with strong privacy protections. Plugins built on its decentralized data store make it very easy to host your own website and provide microblogging and forums, media sharing from files to video-on-demand and decentralized version tracking, blogging and spam resistance without central authority. For an easy start you can join the global Opennet. For maximum privacy, connect to your friends and build a friend-to-friend network independent of and invisible to any centralized server. To access the global network, you either need some friends who also connect to opennet, or use the Shoeshop plugin to build a sneakernet that can even bridge separate friend-to-friend networks when your regional internet itself gets severed from the global information network. Lots of additional information about Hyphanet and its history is available on Wikipedia. Code Signing Policy

Thumbnail not available
ALT text

A jumping white rabbit with blue background, below it the name Hyphanet.

@adamsaidsomething@mastodon.social

"Content about Gaza is also being restricted by age verification. Reddit users in the UK have to verify their age, using... Persona, in order to access... r/israelexposed ... Posts about Palestine on X have also been age gated"

openrightsgroup.org/campaign/s

So to view content about Palestine, you first need to hand your biometric data to who supplies the Israeli military with data and A.I. tools thru

IS

openrightsgroup.org

Fix the Online Safety Act

The Online Safety Act is restricting freedom of expression in the UK.

@technically_good@techhub.social

I wrote this article as a primer for folks on how the "social networks"* keep us locked in. If you like it, consider sharing it with a friend who is new to the world of , the , or getting off of billionaire/US tech.

*Also, why "legacy algorithmic media" may be a better term for the Facebooks and Xitters of the world.

technically-good.ca/feeding-th

Feedback welcome, boosts of course ok, have a great weekend, and let's fix this mess! 💜

technically-good.ca

Feeding the Fire: Psychology, Engagement, and Algorithmic Media

If you're reading this, and you don't have a Facebook or Xitter account (because you either deleted it, or never had one to begin with), give yourself a pat ...

@mboelen@mastodon.nl

De timing met is compleet toeval, maar wellicht daardoor ook juist hét goed moment voor deze aankondiging:

Ik ben begonnen met een nieuwe blog, genaamd Privacy voor een beginner!

privacy.vooreenbeginner.nl/

Net als "Linux voor een beginner" gericht op het toegankelijk maken van informatie. In stapjes ga ik de aankomende maanden zaken rondom uitwerken.

Van accounts tot zoekmachines, alles wat ik tegenkom (of waar jullie vragen over hebben).

Doe je mee? Volg me hier of via .

privacy.vooreenbeginner.nl

Privacy voor een beginner

Privacy voor een beginner is een website die jou helpt om je privacy, jouw data en persoonlijke informatie beter te beschermen, zonder commercieel belang.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Die Rückkehr zur Registrierung - Datenaustausch über psychisch erkrankte Menschen

„Schon vor mehr als 50 Jahren gab es Streit darüber, ob Behörden Daten über Menschen sammeln sollen, die als psychisch krank gelten. Doch während sich damals ein Konsens für mehr Teilhabe und gegen Stigmatisierung bildete, hat sich heute etwas verändert……“

netzpolitik.org/2026/datenaust

netzpolitik.org

Die Rückkehr zur Registrierung

Schon vor mehr als 50 Jahren gab es Streit darüber, ob Behörden Daten über Menschen sammeln sollen, die als psychisch krank gelten. Doch während sich damals ein Konsens für mehr Teilhabe und gegen Stigmatisierung bildete, hat sich heute etwas verändert.

@forgetpassword@goingdark.social

Hi~ people, its time for a basic introduction. I'm a 20 something drifting through life trying to understand OPSEC and anti-surveillance tech.
I heard that mastodon is more privacy friendly platform than whatever bigtech slop out there.

My likes include Linux, FOSS, slowed nightcore covers of generic pop songs, rainy days, pet pigeons and calligraphy.
I dislike Bigtech, genAI, surveillace, those websites that tell me to turn the adblocker off and the list is ever expanding.
I suffer from depression. Kindness shown whenever interacting with me is appreciated.

Special thanks to @fanfare

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Palantir-Einsatz in - nutzt Software tausendfach

"Der Einsatz der Polizei-Software von ist an strenge Vorgaben geknüpft. Trotzdem wurde sie in sechs Monaten mindestens 2000 Mal genutzt. Wie oft genau kann das NRW-Innenministerium aber gar nicht sagen......
(...)
Herbert (CDU) hat eine klare Haltung zur Software des umstrittenen US-Unternehmens Palantir: "Damit ersparen wir der Polizei wahnsinnig viel Arbeitszeit, weil wir die Daten, die sowieso schon zugänglich waren, schneller erreichen können."

www1.wdr.de/nachrichten/landes

www1.wdr.de

Palantir-Einsatz in NRW: Polizei nutzt Software tausendfach

Mindestens 2000 Mal kam Palantir in sechs Monaten zum Einsatz - wie oft genau kann das NRW-Innenministerium aber nicht sagen.

@clock@f.cz · Reply to Adam

@adamsaidsomething @eff Oh! Here we go: I feel

e x t r e m e l y ​ ​ s t r o n g ​ ​ c o n t e m p t

towards the Spanish🇪🇸 regime when I am seeing this. I feel

e x t r e m e l y ​ ​ s t r o n g ​ ​ c o n t e m p t

towards the UK🇬🇧 regime when I am seeing this. I feel

e x t r e m e l y ​ ​ s t r o n g ​ ​ c o n t e m p t

towards the Danish🇩🇰 regime when I am seeing this. I feel

e x t r e m e l y ​ ​ s t r o n g ​ ​ c o n t e m p t

towards the Australian🇦🇺 regime when I am seeing this. I feel

e x t r e m e l y ​ ​ s t r o n g ​ ​ c o n t e m p t

towards the French🇫🇷 regime when I am seeing this. I feel

e x t r e m e l y ​ ​ s t r o n g ​ ​ c o n t e m p t

towards the Malaysian🇲🇾 regime when I am seeing this.

@adamsaidsomething@mastodon.social
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Baden-Württembergs Landtag hat einer erweiterten Massenüberwachung den Weg geebnet. Künftig sollen auch auf kommunaler Ebene KI-gestützte Überwachung und Mustererkennung leichter möglich sein und die Speicherfrist der Aufnahmen wird um 2 Monate erhöht.

und gehören auch in anderen Bundesländern an denen sie in der sind oder waren, zu den treibenden autoritären Kräften für eine verschärfte , die u.A. auf die Software des militarisierten US-Konzerns zurückgreift. So auch in und in .

badische-zeitung.de/baden-wuer

badische-zeitung.de

Baden-Württemberg erleichtert Videoüberwachung im öffentlichen Raum

Baden-Württemberg lockert die Regeln für Videoüberwachung im Land. Kommunen dürfen künftig viel leichter Kameras einsetzen &ndash; sogar mit KI.

@44@defcon.social

saw a bunch of these around here so might as well:

20s something living in

by day

by night

absolute nerd
(not brostep) and whatevers or

used 2 organize and promote and b4 adult life started eating my free time
still help out other collectives with setup here and there
huge nerd

that friend in the friend group that "knows" about tech
(im a highly person and can use a search engine) (and obsessed with anything and related and and love with things to see what makes them tick)

i love and wayy 2 much, like just pulling a throttle just numbs my brain in2 pure , without i would have been rid of my licence years ago
/s

sometimes i play around with a (what my frens call me)

fluent in
maybe a bit sometimes

@DXC_0@infosec.exchange

"For all security paranoïd, selfhosting and low tech is the best choice"

- No IA / LLM
- No bullshit social networks
- No trackers, small fingerprint
- No big attack surface
- No too much cve
- No stupid algorithm
- No agressive adverts / ads
- Censorship resistant
- Community driven

breathe in the fresh air, the real life 🌱🌳

Take the control of our life.

@pheonix@hachyderm.io

The most annoying thing about corporate surveillance to me is the arrogance of the prediction mechanisms.

These algorithms build a model of me based on my clicks from three years ago and then try to trap me in that loop forever. They show me music they think I'll like, and news they think I'll engage with, and videos they think will enrage me enough to keep me hooked to their platforms. They are actively trying to flatten my personality into something easy to monetize.

As most people I've seen say out loud, "Privacy as a concept is way beyond hiding secrets. A part of it also means preserving your capacity to change. To be surprised. To be inconsistent."

If I could tell every human one thing, it would be to actively refuse to be a predictable data point. Mess up their metrics. In whatever way you are capable of.

@darkpixel@infosec.exchange

Hello Universe!

Moved to new server.

Re-introduction - Been on here since 2022 and should write an intro again. I'm deaf, I'm a fan of open-source projects, so this will be short and sweet.

Post random ramblings, news, techie stuff, boost mostly cat pics. I just like computers and hang around here.

Hashtags of interests:

| | | |
| |
| |
| |
|
| | |
| | |
|
|
|
|

Howdy! 👋 Boost for visibility 🙌

Thumbnail not available
ALT text

Energy = Milk x Coffee²

@DirtyAnCom@kolektiva.social

How to set up a "ghost phone":

@calyxinstitute

UPDATE: Calyx SIMs are internet-only... Oops. My fault for presuming they were default unlimited talk/text/data. (Update: I wouldn't trust Cape.) See the replies for a Jabber-based solution to a phone number. Much more affordable, too.

Find yourself a friend willing to receive packages in their name on your behalf, preferably someone not at risk of being monitored, themselves.

Order a SIM card from the Calyx Institute (calyx.org/):
• use crypto currency, prepaid gift card bought with cash, or money order.
• use a fake name to register the SIM.
• have it shipped to your friend's address.

Buy a pre-owned Google Pixel:
• buy with cash at physical location
• or online with a prepaid gift card that was bought with cash; use a brand new shopping account.
• or with crypto on DNM.
• have shipped to your friend's address.

Install GrapheneOS using your preferred method (browser is easier; local is more 1337):
• follow the guide at graphineos.org
• the guide says you need an internet connection to enable OEM unlocking, but I found this to be untrue and did not connect to internet.

When first connecting to internet, it is safer to wait until you have your SIM card than to connect to WiFi to finish setting up your phone.

If you do connect to WiFi, first, you should connect to a router with active VPN capabilities to avoid associating your device with your home IP. I was impatient and connected through my PC which runs a 24/7 VPN over WiFi and shares its connection over LAN to a GL.iNet router. I connected to the GL.iNet router which would feed my phone's connection through PC's VPN connection. GL.iNet routers have great support for VPNs on-device, too. Use a fresh VPN connection that you have not done any personal internet activity on.

Alternatively, you could connect to a public WiFi not terribly near your home to initially set up your phone and VPN connection.

Your next step should be to set up your VPN connection on your phone. Mullvad and Proton have clients available on F-Droid, so you'd have to install F-Droid first. NordVPN requires you to use the Play Store, so you'll have to set up the Play Store if you use Nord (or want any apps only available on the Play Store).

GrapheneOS uses a container for the Play Store so it can't access personal data on your device. Create a new Google account; do NOT use your primary google account. If you must to use a phone number for verification (optional), use the phone number associated with your new SIM, not your primary number. Don't forget to memorize or save your password.

If you want to add payment to your new google account, use a prepaid gift card.

You can also manually set up your VPN in the Networking section of the Settings app. I won't hold your hand for this and assume you know what you're doing if you go this route.

Use a kill switch, if available with your VPN. If not, be very careful about making sure your VPN is connected.

It may not be terribly necessary to use a VPN if you never connect to WiFi and only use your 5G connection. Although your IP will reveal your general location.

Disable location services for best security. it is actually very difficult for LEA to triangulate 5G devices with cell towers. You should be practically safe from triangulation attacks.

(GrapheneOS also has a built-in network and location proxies if you need location services.)

Pay attention that your connection doesn't downgrade to 4G or especially 3G to avoid triangulation. LEA will use a device called a "Stingray" to downgrade cellular connections in an area so they can triangulate devices. You can use a Verizon Orbic 5G hotspot with custom firmware called "Rayhunter" to determine if a Stingray is active in your area. You do not need a SIM and subscription for the Orbis. (eff.org/deeplinks/2025/03/meet)

If a stingray is active, shut down your phone, ASAP.

That's it. Stay sharp and pay attention and your phone should be untraceable back to you. Use unique accounts on your ghost phone to best hide your identity. Or at least accounts that are already hidden from your primary identity.

Alternatively, you can use a Calyx Institute hotspot and avoid using a SIM altogether. (odysee.com/@NaomiBrockwell:4/C)

Bonus Benn Jordan video with a segment about The Rayhunter: anarchy.tube/w/9ZU893XKY6xVNf9

anarchy.tube

Gadgets For People Who Dont Trust The Government

Benn Jordan talks about kicking off the new year by ripping data from weather satellites and talking to your friends through a lawn light. And shows you how. The description of anarchy is simplisti...

@acig@fediscience.org

📢 Call for Papers

Applied Cybersecurity & Internet Governance – an , peer-reviewed scholarly journal dedicated to multidisciplinary research on – is now accepting submissions for the 2026 issue.

Cybersecurity is undergoing rapid transformation.
Autonomous AI systems are evolving.
Generative models are scaling.
Attack techniques are adapting.
Post-quantum threats are emerging.
Researchers must respond.

Join a high-impact platform shaping security studies in the age of intelligent systems.
We welcome manuscripts addressing technical, legal, political, and social aspects of digitalisation, , , , and . Author guidelines are available at: acigjournal.com/For-Authors,45.
All submissions undergo double-blind peer review, revision, and resubmission. Accepted articles are published open access, free of charge, and without delay. ACIG is indexed in leading scientific databases and citation lists, including Scopus.

🌐 Applied Cybersecurity & Internet Governance (#ACIG) is published by – National Research Institute.

Call for papers 2026. Submission deadline: September 30, 2026.
In the upper right corner there is a designation “2026 Volume 5, No. 1” on a teal background. At the top of the image the logos of ACIG and NASK can be seen. A human hand holding a loudspeaker emerges from behind the bottom edge of the illustration.
ALT text

Call for papers 2026. Submission deadline: September 30, 2026. In the upper right corner there is a designation “2026 Volume 5, No. 1” on a teal background. At the top of the image the logos of ACIG and NASK can be seen. A human hand holding a loudspeaker emerges from behind the bottom edge of the illustration.

@gianmarcogg03@mastodon.uno
@viennawriter@literatur.social · Reply to Klaudia (aka jinxx)

Speaking of reviving ... I'd love to come back to . Currently I'm one the hosts of the Podcast. But I would love to revive my own two shows, on everything around professional writing and on data , , net politics etc. I already had some wonderful guests like Manuel 'HonkHase' Atug and Cory Doctorow. Love to keep going from there. :)

weinschreibereien.de/podcast/

viennawriter.net/podcast/

dinerpodcast.net/

Thumbnail not available
ALT text

Cover of the Eltville WeinSchreibereien podcast

Thumbnail not available
ALT text

Cover of the Vienna Writer's Podcast

Thumbnail not available
ALT text

Cover of The Diner Podcast – Data & Coffee

@TexasObserver@texasobserver.social

“There’s this veneer of respect for privacy that is painted over all of this data aggregation and consolidation.”

But beneath it all, experts warn that smartphone-monitoring software "Tangles" is the latest in a law enforcement arsenal, from surveillance to an army of drones, operating with little oversight.

Our latest from Francesca D'Annunzio is presented in partnership with the Pulitzer Center. texasobserver.org/texas-police

texasobserver.org

Texas Police Invested Millions in a Shadowy Phone-Tracking Software. They Won’t Say How They’ve Used It.

One sheriff who leads an anti-smuggling task force says the software helps “develop leads to eventually obtain probable cause.” Civil liberties experts say its use violates constitutional rights.

@MixMistressAlice@todon.eu

"The EU is preparing a proposal that could spell the end of encryption as we know it. With Chat Control and the “Roadmap for Lawful Access to Data,” Brussels wants to allow algorithms to scan —directly on your device— every message, photo, or video before it’s sent, including on encrypted apps like Signal, WhatsApp, Telegram, iMessage, or ProtonMail.
Behind the stated fight against child abuse, an entire system of mass surveillance could emerge in just a few months. In reality, this paves the way for:

• Permanent surveillance of all citizens.
• Built-in backdoors that weaken everyone’s security.
• Cross-border phone tapping.
• A transfer of power to private companies like Microsoft, Google, or Thorn, who would control detection tools for profit.

Why say NO?
Because privacy is a fundamental freedom. It protects journalists, lawyers, activists, victims, whistleblowers and every ordinary citizen. Accepting that our phones become wiretaps means accepting that no conversation is ever truly confidential. It changes the way we speak and think, pushing us toward self-censorship. And once such an infrastructure is in place, history proves one thing: there’s no going back."—Christophe Boutry

End of Encryption: How the EU Wants to Spy on All your Messages >

youtu.be/NVey06McSmg?si=_dSqst

youtube.com

End of Encryption: How the EU Wants to Spy on ALL Your Messages

The European Union is preparing a proposal that could spell the end of encryption as we know it.With Chat Control and the “Roadmap for Lawful Access to Data,...

@legendary_creeper@mas.to

I highly recommend checking out the No Telemetry mod by kb1000 for Minecraft Java Edition. It disables the non-GDPR compliant telemetry of Minecraft, since they do not provide the option themselves. It's well maintained, and I'm using it myself since I started playing Java.

Info & Download:
modrinth.com/mod/no-telemetry/
github.com/kb-1000/no-telemetry

Report on the bug tracker:
bugs.mojang.com/browse/MC/issu

bugs.mojang.com

Mojira Public Bug Tracker

@kstrlworks@techhub.social

Hi, I'm Sparrow. I run KstrlWorks where we build high-performance, privacy-first tools for Linux users.

Built systems for F-35s and high-frequency trading desks. Now an executive that companies with deep pockets parachute into their disasters to fix operations and actually grow them.

Currently shipping:
HardPass - GPU passthrough and that actually works. For and power users.

I write about:
- Real . The kind that prevents incidents, not LinkedIn motivational posters.
- Running efficient, security-first teams that don't implode
- , systems architecture, and
- Building infrastructure so solid you never need to hire a fixer like me

High-performance, privacy-first tools built with the same standards I use for critical systems. Linux users deserve that.

Let's build things that work. 🐧

Thumbnail not available
ALT text

Hardpass GPU passthrough tool, to run windows apps locally with hardware acceleration.

@KianMeherzad@tech.lgbt

Hi Fediverse!! 👋😊

My name is Kian (Kee-ahn).

I'm , an (), and sometimes . I'm here to discuss , , and ; complain about , (or whatever the current exploitative fad is), and my ; share , , and my greatest ; and also .

I'm always listening, learning, and growing. I try to speak from my experiences (including my privilege), and make many mistakes along the way. I invite you to challenge my thoughts, share your perspectives, agree or disagree, and otherwise interact with me; and maybe together we can grow as individuals and strengthen this community.

@longreads@mastodon.world
@Blort@social.tchncs.de

@thelinuxexperiment

For the love of all that is good, *someone* PLEASE create a browser UI around Servo that is:

*
* Community governed
* Has daily testing packages
* Community funded non profit
* Avoids off device
* Communicates clearly

I worked professionally with high profile campaigns for years. I am 100% certain a campaign would go viral, with stretch goals blown away.

isn't feature complete, but many (me!) would 100% daily drive something alpha, buggy and missing features to build a better future. Hint: this is exactly what successfully launched FIrefox against .

We need hope we can escape the sinking, Titanic shitopoly of and . We will rally around any principled alternative.

Thumbnail not available
ALT text

An illustration of the round blue and green Servo logo rolling over a breaking Chrome browser logo with speed lines in the background.

@reiver@mastodon.social · Reply to @reiver ⊼ (Charles) :batman:

4/

So, how can you mitigate some of the harmful ways that LLMs could be used, as it relates to PRIVACY —

I don't think it is reasonable to expect people to stop using LLMs.

I think a key part of a way that this can be addressed is — LLM should to be run LOCALLY.

People after better off running LLMs LOCALLY on their own computers — to remove some of the vectors by which they could be spied on.

In addition to that —

...

@reiver@mastodon.social · Reply to @reiver ⊼ (Charles) :batman:

3/

I think people who care about PRIVACY should pay a lot of attention to LLMs!

The ability to (both intentionally and unintentionally) spy on, manipulate, and engage in other zero-sum (and even negative-sum) behavior against people will be at a level never seen before — because of how those who want to do those things could (and likely will) use LLMs.

But, there is something we can do about it —

...

@reiver@mastodon.social · Reply to @reiver ⊼ (Charles) :batman:

2/

I don't think LLMs are going to go away — not in the way I suspect some of its hater wish it would.

Even after the AI hype-bubble pops — I think LLMs will still be around.

It doesn't matter if you hate them, or hate how they were created, or hate their social impact, or whatever — I think people will continue to use LLMs — both now and in the future.

But, here is the thing —

...

En zo is er nog meer te vertellen. Als je tijd hebt, kijk gerust naar het interview met onze voorzitter Simon Lelieveldt bij Holland Gold.

Hij legt uit wat HRIF.EU momenteel aan het doen is en hoe onze kijk is op het omgaan met mensenrechten-schendingen in een erg gespecialiseerde bureaucratische wereld.

youtube.com/watch?v=I2ME57Ux-_

youtube.com

Simon Lelieveldt over doorgeslagen financiële controlestaat en verlies waardevrij geld

In deze aflevering van Holland Gold gaat Paul Buitink in gesprek met Simon Lelieveldt over de doorgeslagen financiële controlestaat. Simon Lelieveldt heeft ...

@resplendent606@climatejustice.social

I will make this a mega pin post.

:gnu: :tux: :NoAI:

Disclaimer:

My opinions are my own and do not represent any organization. I will update this post occasionally. Please follow for more!

Contents:
1. Ways to support me.
2. Where else to find me.
3. More information about myself.
4. Important Posts
5. Currently used/recommended software

1. Support:

Liberapay: liberapay.com/terminaltilt/don
Ko-Fi: ko-fi.com/terminaltilt

2. Where else you can find me:

Personal:
PieFed: piefed.social/u/Resplendent606

Terminal Tilt:
Youtube: youtube.com/@TerminalTilt
Linkstack: links.terminaltilt.com/
Website: terminaltilt.com
Mastodon: climatejustice.social/@termina

3. More about me:

Hi, I am Bryan. I love talking about and You can reach me here via DMs. All Terminal Tilt inquires should be directed to the methods linked above. I’m happy to help with Linux or self-hosting questions.

I live in East Tennessee, USA. I am an omnisexual cis-gendered man (he/him). I have been happily married for 17 years to my best friend and the love of my life. I have a Bichon Frisé who I adore and consider my own child (fur baby). I am type 1 bipolar and I have undifferentiated connective tissue disease (UCTD) which has similarities to Lupus.

I am an atheist and I consider myself a "humanist." I identify as left/progressive/socialist/eco-Marxist. I am 100% anti-fascist, anti-AI, and anti-big tech.

I am a supporter for social justice, LGBTQIA+ rights, the preservation and protection of our environment, consumer and privacy rights, the Free Software Movement (FOSS), and the defense and independence of victims of genocide, invasion, and injustice (Ukraine 🇺🇦 and Palestine 🇵🇸).

I advocate for the use and promotion of free and open software and the right to repair. I use Debian GNU/Linux (btw) on my desktop, laptop, and Proxmox on my server running VMs of Debian and Home Assistant OS. :gnu: :tux: I also use GrapheneOS on mobile. I am a card carrying member of the @fsf and the @eff

I believe privacy is a human right. I have deGoogled myself and I am strongly anti-big-tech. I proudly deleted my Google, Microsoft, and Reddit accounts. I prefer to support organizations who are community run or employee owned (like coops) when possible, resist the use of trends like "AI" and "LLM's." :NoAI:

I moved to climatejustice.social in August 2025 because I wanted to be around people who are like minded. I am pleasantly surprised that not only does this community share similar interests and goals, there are also some extremely intelligent people here. I have enjoyed my time here and I highly recommend it if you need/want a new Fediverse home.

Other charities, organizations, and projects I have supported:

Electronic Frontier Foundation (EFF): eff.org | @eff
Free Software Foundation (FSF): my.fsf.org/join | @fsf
Privacy Guides: privacyguides.org | @privacyguides
Dolly Parton's Imagination Library: imaginationlibrary.com/
The Official Legal Fund: givesendgo.com/luigi-defense-f

Some of my favorite people on Mastodon:

@Em0nM4stodon
@PaulaToThePeople
@trashheap
@giuseppegv
@splendorr
@Jc00qe
@jonah
@PhoenixSerenity
@JanUwU42
@adubya

4. Important posts:

Dare to Be Forgotton: climatejustice.social/@resplen

Dare to Be Inconvenienced: climatejustice.social/@resplen

Dare to be Disconnected: climatejustice.social/@resplen

Please Stop Using "Bipolar" as an Adjective: climatejustice.social/@resplen

Debian based GNU/Linux distros: climatejustice.social/@resplen

5. Currently recommended GNU/Linux software:
Consolidated list to my Codeberge here: codeberg.org/resplendent606/te

codeberg.org

Cookie monster!

@dolanor@hachyderm.io

TL;DR: I'm using WhisperIMEplus on my phone, and I think I will finally live in the XXIst century with my phone.
github.com/woheller69/whisperI

I refrained myself from using speech recognition on my android since the beginning because I didn't like the idea of my voice used for other reasons than my need which would have been speech-to-text.

And having on-device speech recognition was pretty niche for a while (I was interested in mycroft and snips at that time). Then there was Mozilla with CommonVoice and deepspeech, unfortunately, DeepSpeech has been shut down (it seems), and the results are far from the Whisper model from OpenAI.

I'm clearly not an OpenAI fan (if you haven't figured it out yet, you will soon if you follow me), but Whisper seems to be the best thing that got out of this, mostly because it's way more open than any other things from OpenAI which are not open at all.

Anyway, I found that now, there is a project called WhisperIMEplus that is used as a keyboard on my android, and it processes my voice, locally, on my device. And the app has NO internet connection rights, so, even if OpenAI added some backdoor to send data online in their Whisper model, well, Android app rights wouldn't allow it.

I'm fine with all of this, so now, I can finally take notes by talking to my phone, in English and French, without having second thoughts about it.

It's good when technology helps you, instead of trying to screw you in different and sneaky ways.

github.com

GitHub - woheller69/whisperIMEplus: Android Input Method Editor (IME) based on RTranslators Whisper implementation

Android Input Method Editor (IME) based on RTranslators Whisper implementation - woheller69/whisperIMEplus

@gimulnautti@mastodon.green

I have drafted an email critical of the proposal in from a wide-reaching privacy, sector protection and risk standpoint.

Read here:
nx82858.your-storageshare.de/s

Send to EU representatives with this list of emails:
nx82858.your-storageshare.de/s

If you care about and , please boost and take part in this !

nx82858.your-storageshare.de

european.commission.2025.emails.csv

Storage Share - powered by Nextcloud

@gianmarcogg03@mastodon.uno
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@mark22k@layer8.space · Reply to Marek
@Distante@mastodon.social · Reply to Distante

Everything we write in private messages should always have E2E encryption.

It's time to put an end to hybrid attacks by autocracies and all this hatred. The internet is just a tool.

It is unfortunate that some people confuse and . These are all different terms related to different areas of the internet.

@watchfulcitizen@goingdark.social

@GrapheneOS is being threatened by French authorities for refusing to add backdoors and they're dealing with coordinated attacks in French media right now. They're pulling out of France entirely, moving all their servers, and fighting off a wave of bullshit one-sided reporting that makes them look like they're helping criminals.

They need us to fight back. Support them however you can, whether that's a dollar, sharing their story, pushing back on the garbage news coverage when you see it, or just telling someone you know about what's happening. All of it matters because they're drowning in attacks from governments and media and bad actors who want them gone.

This is the only Android OS that actually makes me feel like privacy isn't just marketing. They fight for us now they need us to fight for them.

The EU is pushing Chat Control and creating an environment where governments feel empowered to threaten developers into compliance, and if we stay quiet we're letting it happen. Show up for them in whatever way you're able to.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@ax6761@freeradical.zone · Reply to ax6761
@kkarhan@infosec.space

@sylvie "#YouHadOneJob, !"

  • Tho not surprising, as Apple doesn't care about but merely exercising total control over all the and the users...

That's why they on ...

Personally, I've been using for 15 years now but then again I've always been on from the beginning and never had an or , so my opinion doesn't matter here...

@gianmarcogg03@mastodon.uno

Nuovo video tutorial su come scaricare video da con software libero privo di pubblicità e spyware. Le applicazioni utilizzate sono Parabolic (Windows e Linux) e YTDLnis (Android).

:peertube: PeerTube: videos.gianmarco.gg/w/iBSvgyX7
Odysee: odysee.com/@gianmarcogg03:e/pa
YouTube: CENSURATO DA YOUTUBE!!!

@opensource

odysee.com

Come scaricare video da YouTube con software libero: Parabolic e YTDLnis

Sito web di Parabolic: https://nickvision.org/parabolic.html

@ax6761@freeradical.zone · Reply to ax6761

… - Addressing the ' (Interdependent) Issues,
by Kavous S N, Lev V, Samuel M, Stephan M, Aurelia T-L, Marc-Olivier B, Mathias H, and Kévin H,
usenix.org/system/files/usenix
youtube.com/watch?v=pZHJXO_6ilY
-- ugh :pulling face down:;
-- most interesting of the recent batch!

So removed "related name" field in Apple Contacts where I think I had. Next step would be to rename/move "family", work- & location-specific lists …

youtube.com

USENIX Security '25 - Addressing the Address Books' (Interdependent) Privacy Issues

Addressing the Address Books' (Interdependent) Privacy IssuesKavous Salehzadeh Niksirat, University of Lausanne / Max Planck Institute for Security and Priva...

@ax6761@freeradical.zone · Reply to ax6761
@gianmarcogg03@mastodon.uno
@ildiavolorosso@sfba.social

Was forced to use biometrics instead of a boarding pass to board a
@unitedairlines flight today. This is completely unacceptable. No airline should be allowed to possess biometric data on California residents...or anyone, for that matter.

Unfortunately, United hides its opt out forms behind an email alias (privacy@united.com) that generates a user-specific opt-out form. This is an anti-pattern designed to discourage the exercise of your rights.

The request-specific web form itself contains anti-patterns designed to discourage use, from clunky date fields to other fields designed to make you make a mistake so they can deny. Those are followed by multiple attempts at identity confirmation, adding friction and risk.

In forcing the use of on passengers, United Airlines joins Trumps' ICE Gestapo in violating the and individual rights of both citizen and non-citizen alike. This move is NOT about safety. It's got to stop.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Patientenakten enthalten oft falsche oder übertriebene Diagnosen

"Seit Oktober ist die elektronische Patientenakte Pflicht. Versicherte können darin einsehen, welche Diagnosen und Behandlungen dokumentiert wurden. Doch nicht immer sind die Diagnosen richtig......"

www1.wdr.de/nachrichten/falsch

Erfundene Krankheiten mit echten Folgen

'Für Betroffene können falsche Diagnosen allerdings gravierende Konsequenzen haben - etwa beim Wechsel in die private Krankenversicherung oder beim Abschluss einer Berufsunfähigkeitsversicherung. Stehen in der Akte Krankheiten, die bei ihnen nie existierten, kann das zu höheren Beiträgen für sie führen oder dazu, dass Versicherungen im Schadensfall nicht zahlen.

Auch das ZDF-Magazin "frontal" berichtete kürzlich von Patienten, die Diagnosen in ihren Patientenakten fanden, von denen sie gar nichts wussten. In einem Fall sagte ein Versicherter, dass er laut Akte ein Kollaps-Patient sei und ein Blutgerinnungsstörung habe. Das mache ihn zum Hochrisikopatienten - mit entsprechenden Zuschlägen. Hätte er die Krankheit tatsächlich, dürfte er aber wohl kaum im Vertrieb arbeiten und am Steuer sitzen, heißt es in dem Magazin......'

www1.wdr.de

Elektronische Patientenakten: Immer mehr Patienten entdecken falsche Diagnosen

In elektronischen Patientenakten stehen offenbar zum Teil falsche Diagnosen. Steckt dahinter ein System, um mehr abzurechnen?

@eclecticpassions@fosstodon.org

I am really upset about locking the ecosystem. I feel there's no longer a reasonable alternate OS on the market.

Do end-users really have no choice other than defencelessly accept closed systems, monopolistic supervision, and give up digital software freedom?

Why are we banned from using we want, on a device we own from ? I feel bad for all the too.

Please raise awareness.🚨

1/2

@nullagent@partyon.xyz · Reply to nullagent

Because this KISS-TNC stuff is pretty old, it has really good support on modern Linux.

So we're actually able to setup lorapipe on two different linux boxes and form an ethernet network over LoRa!

The current rev has some MTU limits we can fix, we can also eak out probably another 2x more bandwidth too.

But as is I was able to ping, mosh and ssh over my ethernet-LoRa network between Linux computers!

github.com/datapartyjs/lorapip

@meph

@Em0nM4stodon@infosec.exchange

Privacy rights aren't a luxury, they are fundamental to democracy, to safety, and to so many other human rights.

When they attack your privacy rights,
they attack all of this, they attack your humanity.

Do not let them.
Fight back for your human rights.

@Jonas@social.linux.pizza · Reply to European Commission

The fact that government and military communication would be exempt is, in itself, an admission that there's no such thing as a backdoor only for the good guys.

If that wasn't bad enough, any access that allows you to search for CSAM in communications can also be used for surveillance.

Creating a system with immense surveillance capabilities without intending to use it for surveillance is, at best, naive. Even if you don't plan on using it, you can't know who's going to be in power in the future.

@EUCommission @ranx

@mysk@mastodon.social

🤯 Instagram is testing new iOS push notifications that include a profile photo. Each time the notification is shown on your screen, it triggers a GET request to fetch that image, letting Meta track every on-screen impression.

The app still misuses push notifications to send detailed device analytics about the device (uptime, battery, volume, locale, timezone, memory, CPU, etc.)


More 👇🧵

Thumbnail not available
ALT text

Screenshot of the new push notification with a profile photo shown in Notification Center

Thumbnail not available
ALT text

A GET request sent by Instagram when the notification was shown on screen.

@dan@m.danq.me

👋 Re-, because the last one had gotten a little outdated. And long.

:bisexual_flag: :polyamory_flag:​ . since 1998, fan since forever, citizen since 2018.

🇪🇺 :socialiststar: European in exile living in West , , with my partner @fleeblewidget, her husband @misterjta, two kids, and one . Politically .

:HackerCat:​ :threerings: Software engineer with a focus on , , and . Founded and with .

:geohashing: :geocaching: When I've time for fun, I'm into , , , and performing . Sometimes at the same time.

:hehim: He/him pronouns.

📹 Video content: me giving a 15-second summary of the above.

Thumbnail not available
ALT text

Video introduction: a white man with blue hair tied in a ponytail, a goatee beard, and stubble, waves to the camera, saying, in an accent representative of various bits of Northern Great Britain: "Hi, I'm Dan Q; I'm not good at giving short introductions so let's really belt this one out. I'm a queer poly geek, blogger, software engineer, founder of a volunteer-run nonprofit, geocacher, geohasher, cyclist, and magician. Say hi!"
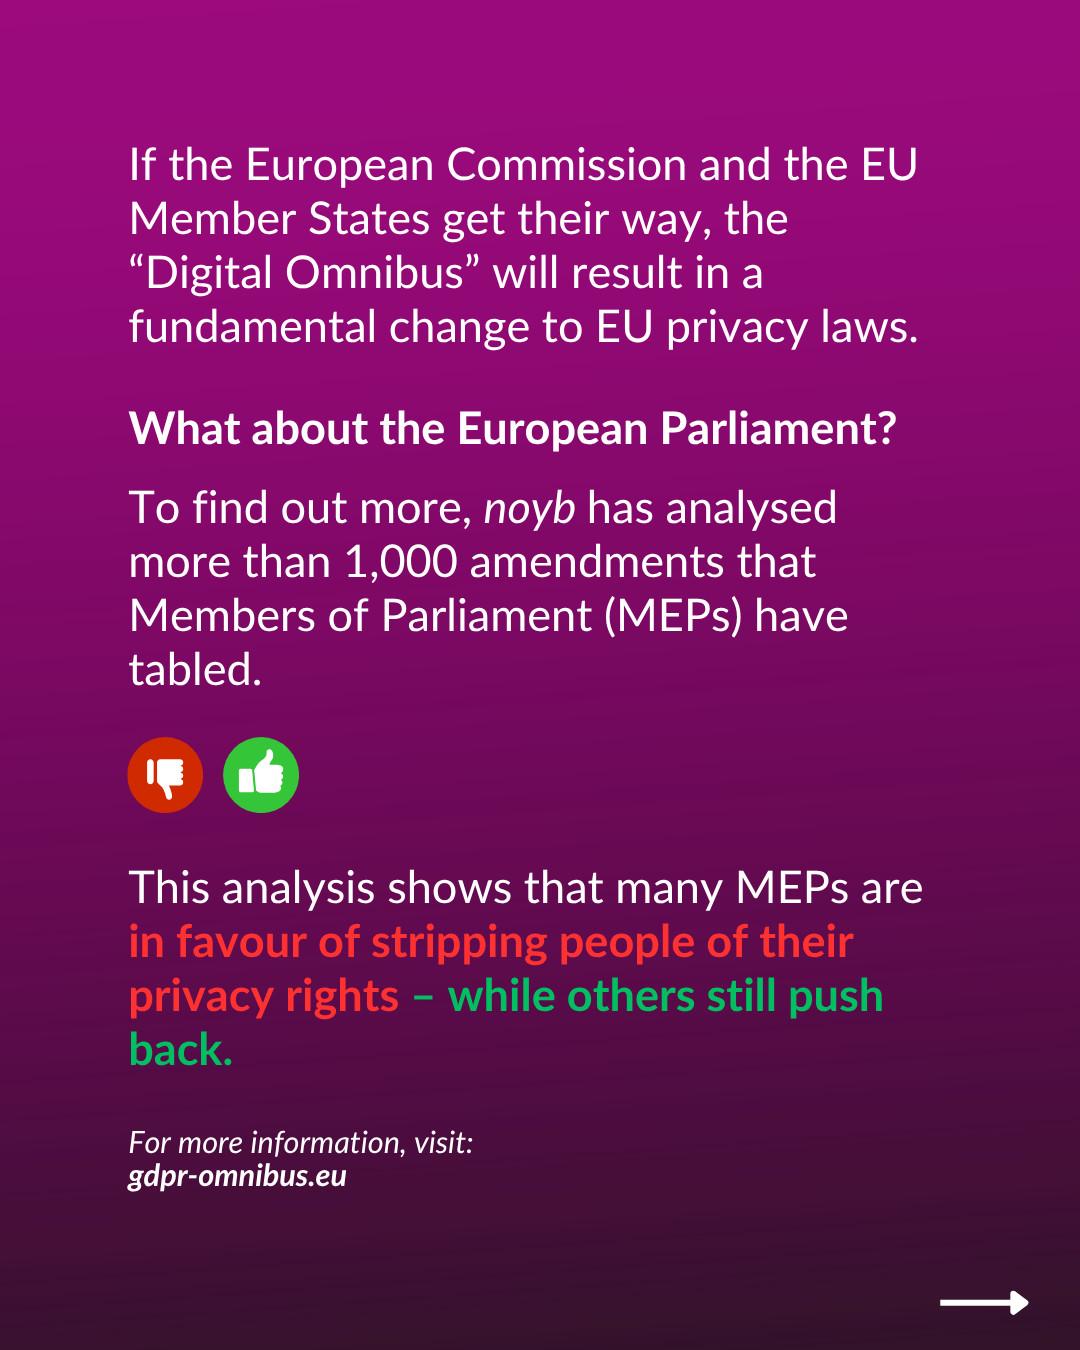
@ppaluchowski64@infosec.exchange

For months now, whispers have turned into a roar :neocat_scream_angry: about a certain EU proposal. At first, it sounds like a noble cause - protecting children from harm online 👶🛡️ Who could argue with that?

But this is no ordinary mission. This is the turning point 🔄 A moment where the digital realm risks falling into a shadow :ghosty: A plan that demands all our private conversations be scanned :eyes_happy: No suspicion. No crime. No reason. Just everyone. All the time ⏰
Imagine a system powerful enough to scan every message, every image, every whisper - on every device, for every person 📱💻 It doesn't need physical access or a noisy presence. It runs silently in the background, all the time :ghosty:

It was created to protect 🛡️ But its effectiveness is uncertain, and privacy is seriously compromised 🔓 Instead of focusing on real threats, it treats everyone the same - as if risk came from simply being online 🌐

A digital weapon built before anyone can understand its consequences ⚠️ Like a Death Star - not made of kyber, but of code :empire: Created in the name of safety, but capable of something far more dangerous ☠️

Officially, this proposal is called CSAR (Child Sexual Abuse Regulation) 📜, but most of us know it as ChatControl :mail_smirk: And that's no accident - the latter name more accurately reflects what this system really is and the consequences it brings :eyes_happy:

If passed, it will mark the end of private digital communication in the EU 🚫:signal: And if it happens here, it can happen anywhere 🌍 Because what is accepted in one democracy can quickly become the norm in others. Europe often sets the standards others follow 🇪🇺 And the world is watching 👁️

This proposal changes the rules ⚖️ It weakens encryption 🔐, the very foundation of secure communication. When encryption is weakened, every message becomes vulnerable to interception :hacked:, and privacy is no longer guaranteed. When privacy disappears, democracy crumbles with it 🏛️⚠️ The consequences do not end there - surveillance will become part of daily life :signal: :eyes_happy:, and control over our digital world will only grow stronger.

I was born into a free internet 🌐 I want to die in one too 🗽

This proposal breaks fundamental rights 🚨:
- the right to private communication (Article 7) :signal:
- the right to data protection (Article 8) 🔒
- the presumption of innocence ⚖️
- the principle of proportionality ⚖️

This is not a debate over ideology 🚫🗯️ This is a matter of principle 🔥

To the @EUCommission: I know your intentions are good 🙏 But history does not judge intentions. It judges consequences :blobcatgrimacing: You want to protect people 🛡️ But you may end up building something that will be used to control them :neocat_devil:
Don't build a machine you yourselves would fear :neocat_scream_scared: You will not be remembered for good intentions - but for what you leave behind 👣 Think about how it will affect us all. Choose security, not surveillance. 🚫:eyes_happy: This is your moment ⏳ Don't waste it.

To everyone else: You don't have to be from Europe 🇪🇺 to care :neocat_heart: When harmful laws pass without resistance - the impact is felt everywhere 🌎 We are citizens of one digital world 🌐 And in that world, staying silent comes at the highest cost 🤐
Freedom does not die loudly. It disappears - quietly :ghosty: - unless we stop it :fist_paw:

Visit fightchatcontrol.eu. Learn. Message your MEP. Take action! :rebel:

@chatcontrol

@eyess@kolektiva.social

@nullagent @nullagent in my local hacker/activist community, we are working really hard to get people to ditch Meshtastic in favor of Reticulum, including building out our own local mesh network with it. To anyone that has been sold on the promises of Meshtastic, I'd definitely recommend you do the same!

The security/encryption of Reticulum is far superior, and the feature set is far more complete (it can be used for text, voice calls, hosting websites, TCP/IP tunneling, really anything), it can interoperate on way more radio protocols than just LoRa (including many non-radio protocols), and the development team seems far more committed to FOSS and anti-corporate ideals.

It also doesnt use flood-routing, unlike Meshtastic, so the network gets significantly more efficient as nodes are added, rather than getting bogged down the way Meshtastic does.

Thank you for putting this info out there, it's very refreshing when so many out there are parroting Meshtastic's marketing materials on its security while simultaneously advocating its usage in high-risk environments like protests.

@ivycyber@privacysafe.social
@brian_greenberg@infosec.exchange

I’m excited to share my latest article, published in Forbes: Deepfakes And Social Engineering: A Growing Threat To Everyone.

This piece is personal to me because I’ve seen how quickly deepfake technology is moving from novelty to real-world attacks. It’s not just companies at risk—families are being targeted with AI-cloned voices and fake video calls.

In the article, I break down the real cases we’re seeing, why multifactor authentication (MFA) is essential, and what both organizations and individuals like you and me can do to protect ourselves.
In the piece, I cover:
🔍 Real-world scams driven by AI voice and video
🔐 Why multifactor authentication (MFA) is essential
📱 How both organizations and families can verify smarter
🧠 The mindset shift from trusting appearances to verifying identities

Deepfakes aren’t a future problem. They’re here. And the time to prepare is now.

forbes.com/councils/forbestech

@forbes@flipboard.com @Forbes@newsie.social @forbestechcncl

@nullagent@partyon.xyz · Reply to nullagent

This segment of meshtastic's DEFCON post are sadly not correct.

I can't tell you why how exactly the firmware and phone app work but I can tell you that if you are near someone PKI spoofing it absolutely does replace the users private key on BOTH the app and the firmware.

The only pub keys that are pinned are your favorites list.

It doesn't matter what -type- of AES is used after the public key is replaced you're already MITMd.

meshtastic.org/blog/that-one-t

@nullagent@partyon.xyz · Reply to nullagent

So I'm not sure how to say it in a more concise way but YES meshtastic direct messages are at risk of MITM (man-in-the-middle) if your public key can be replaced by an attacker who spoofs the PKI.

Due to the way DMs and adverts work I believe this risk likely exists for any device on meshtastic regardless of whether they are on public channels or not.

@r_alb@mastodon.social

Actually, I have an awful lot to hide.

Not because I am a criminal or a tax-evading billionaire, but because I'm a human being.

I am more than just a data mine. I refuse to be reduced to a source of digital commodities. I refuse to be valued at anyone's ad-revenue.

I have a right to decide what others should know about me. And I have a right to know what they will do with what they know.

That's why I have a lot to hide. Not because I must, but because I want to.
--

@JoBlakely@mastodon.social

***infosec specialists are needed in the resistance ***

The world needs tech security specialists to run workshops at public libraries for all ages & abilities to remove spyware, AI, reduce surveillance, understand the issues, & for more advanced, move to Linux, degooglefy, etc.

(Some) Libraries will pay for these workshops. There may be grants too.
If you have these skills, please consider offering them.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Polizei Hamburg will mit Videos von Passant*innen trainieren

"Ab dem 1. September will die Polizei Hamburg eine künstliche Intelligenz (KI) mit Videos von Passanten an zwei öffentlichen Orten trainieren. Manche dieser Aufnahmen sollen monatelang gespeichert werden - das hat die# Polizei jetzt bestätigt.

Das neue polizeiliche KI-Überwachungssystem soll Gewalttaten schneller erkennen. Dafür muss es beispielsweise Faustschläge von normalen Armbewegungen unterscheiden können.
Aufzeichnungen von Hansaplatz und Hachmannplatz

Das lernt die KI laut der Polizei aber nur mithilfe von Aufzeichnungen echter Menschen. Die sollen von den Kameras am Hansaplatz und Hachmannplatz kommen. Jetzt hat die Polizei NDR 90,3 auf Anfrage mitgeteilt, dass die KI ab Anfang September mit den Aufnahmen gefüttert werden soll...."

ndr.de/nachrichten/hamburg/pol

ndr.de

Polizei Hamburg will mit Aufnahmen von Hansaplatz und Hachmannplatz KI trainieren

Ab dem 1. September will die Hamburger Polizei eine Künstliche Intelligenz (KI) mit Videos von Passanten an zwei öffentlichen Orten trainieren. Manche dieser Aufnahmen sollen monatelang gespeichert werden - das hat die Polizei jetzt bestätigt.

@sparklepanic@infosec.exchange

fedi

i'm raven, a silly on the internet who likes to write, and create free-to-use #photography (mostly landscapes). u can find me on mastodon, and see what an overview of what i’m up to on my now page. i have so many interests and try my best to experience new things in this short life. some sort of neurospicy, tend to be overly genuine, a bit corny, over-opinionated at times

🩺 , 📸 , 👩‍💻 nerd, 🏳️‍⚧️ girl, 💞 anarchist, 🌱 for the animals, 🌹 , ✊ steward, 🧗‍♀️ outdoor girlie, 🌠 star stuff, 🚴‍♀️ bikes are cool, 😽 certified girl/boy/nb-kisser, 😝 adventurer

i work in the operating room as a nurse and i love my job

likes: , , coast, , , , , , , OR, scrub-role in surgery, science-stuff, n95s, , and in tech, , , , , pineapple on pizza, , workers-rights, , , and

here are some reviews:

"passionate, kind, clever, motivated by her values & playful/funny”

“very direct and able to be vulnerable very easily (a good thing!) and the most ethically-minded and community-focused person ive met!”

“a cute pup n you take good pictures”

"giving golden retriever young puppy, 4-6 months. Seeks out attention frequently, is outgoing in a friendly room, lil awkward, offers info about yourself readily, soft n likes pets, wants to wrestle”

i upload my photography as creative commons attribution license, i don't own a car, i have a named Loki who i post about under the tag, i'm after a 14 year marriage (not the outcome i wanted, but here i am), and now happily in relationships as a relationship anarchist.

i live in and want to make it a better place by organizing and creating and . i host a local movie night with my friends where i cook vegan food for them, and it makes me happy!

i do -climbing, , , , , currently recovering from injuries

i love and created a theme which i use for my website (on github)

yes, imma and silly af

i do post 18+ stuff at times and i always cw that content, so minors dni with that stuff

im an alt-text advocate and will post all photos with alt-text and not boost things without alt-text

if im doing something wrong, pls let me know via signal dm so i can fix it. integrity, community, and reducing harm matter dearly to me.

ravenwinters.org

what i'm doing now

This is a now page, and it’s what I’m doing now :-) wanna follow along?

@ariane@tooting.ch

✅ If your and are important to you;

✅ If you're tired of the that drives the business models of and tech giants, as they extract your and feed it to their and ;

✅ If keeping control over your matters and matter to you;

:blobGoodMorning: then, join me on the platform !

👤 Here is my ID: threema.id/FSSAEVF9

More here:
👇👇👇
mastodon.social/@threemaapp/11

mastodon.social

Threema (@threemaapp@mastodon.social)

How did you encourage your friends to use Threema? Here are our tips: https://threema.com/bp/why-switch-to-threema

@azuresaipan@defcon.social
@patrickleavy@mastodon.social

The Rebel Tech Alliance is a non-profit dedicated to bringing down

We explain the problem, provide extensive lists of vetted Alternatives, and show you who else is fighting this fight so we can Unite. We also have loads of Resources and Guides.

Please read through the site - it's in chronological order - and share widely. The more people leave the less data Big Tech has, the less power they have. is power!

rebeltechalliance.org/

rebeltechalliance.org

Rebel Tech Alliance

@mysk@mastodon.social

🚀🤘Introducing Psylo: A New Kind of Private Browser

After 9 months of development, we're super excited to finally launch Psylo, a new kind of private web browser for iOS and iPadOS.

In Psylo, each tab is its own “silo” with isolated storage, cookies, and even its own IP address. Psylo introduces advanced anti-tracking and anti-fingerprinting features that go beyond what a VPN can offer.

Full announcement: mysk.blog/2025/06/17/introduci

Thumbnail not available
ALT text

Psylo A New Kind of Private Browser In Psylo, each tab is its own silo, with isolated storage, cookies, and even IP address thanks to our Mysk Private Proxy Network Download Psylo today, and enjoy anti-tracking protection that no VPN can offer

@brozu@mastodon.uno

In 2010, downloaded 70 GB of articles from JSTOR. He faced a $1 million fine and 35 years in prison
➡️ Aaron took his own life in 2013.

illegally downloaded over 80 terabytes of books from LibGen, Anna's Archive, and Z-library to train its models
➡️ facing no consequences.

Information is power, knowledge is power.

Beware and fight against those who want to keep you ignorant, unaware, and misinformed.

A black and white line drawing of Aaron Swartz with wavy hair, wearing a t-shirt and smiling.
ALT text

A black and white line drawing of Aaron Swartz with wavy hair, wearing a t-shirt and smiling.

Another public / channel I co-moderate is the / / channel -

invite.joinjabber.org/#lgbt@co

@maskedwitch - one of the most compassionate people I know of - runs this server and co-moderates all channels on it.
If you're new to XMPP (e.g. coming from etc), this guide has everything you need to get started -
contrapunctus.codeberg.page/th

contrapunctus.codeberg.page

The Quick and Easy Guide to Jabber/XMPP

@Victorsigmoid@hachyderm.io

TIL about the word "calyx" from Robin Wall Kimmerer in her book "The Serviceberry":
"Because I'm a bontanist, my knowledge of economics and finance is about the size of the frilly little cup at the tip of a Juneberry that was once part of the flower. It's called the 'calyx,' in case you were craving a delicious new word, the way some people crave money."

Except due to @calyxinstitute this was not a new word to me, just one that I never thought of otherwise. If, like me, though, reading a gorgeous sentence like that one compels grabbing a dictionary so large it must be opened on a table to dig deeper, then "Hi!" I see you, one of what I would estimate might be a handful of other people, who care about such knowledge and treasure it. May we meet up among the flowers some day.

Anyone here into ? There's a / channel for people who enjoy bowling (10 pin, candle pin, duck pin, etc) at all skill levels!

xmpp.link/#bowling@muc.xmpp.ea

As before, if you're new to XMPP, this guide has everything you need to get started.
contrapunctus.codeberg.page/th

contrapunctus.codeberg.page

The Quick and Easy Guide to Jabber/XMPP

@jfmblinux@mastodon.jfmblinux.fr

🇫🇷
QUE LINUX 🐧 SOIT AVEC VOUS !
Venez à moi et vous serez libre et prions Linux ensemble mes enfants 😜

Notre Torvalds qui est sur le net
Que ton nom soit affiché
Que Linux vienne
Que ton noyau soit compilé avec ou sans options
Donne-nous aujourd’hui notre code de ce jour
Pardonne-nous nos bugs, comme nous pardonnons aussi aux Freeware trops buggés
Et ne nous soumets pas à la crosoftisation
Et délivre-nous de Windows
Ainsi soit Linux 🙏

Au nom de Linux, de l'Opensource et de la liberté.

, il y a moins bien, mais c'est plus !

🇬🇧
May Linux 🐧 be with you!
Come to me and you will be free and pray Linux together my children 😜

Our Torvals which is on the net
May your name be displayed
That Linux comes
Whether your nucleus is compiled with or without options
Give us our code today
Forgive us to our bugs, as we also forgive freeware, exhausted
And don't submit to crosoftisation
And deliver us from Windows
So be Linux 🙏

In the name of Linux, OpenSource and freedom.

, there is worse, but it's more!

🇫🇷 
QUE LINUX 🐧 SOIT AVEC VOUS ! 
Venez à moi et vous serez libre et prions Linux ensemble mes enfants  😜

Notre Torvalds qui est sur le net
Que ton nom soit affiché
Que Linux vienne
Que ton noyau soit compilé avec ou sans options
Donne-nous aujourd’hui notre code de ce jour
Pardonne-nous nos bugs, comme nous pardonnons aussi aux Freeware trops buggés
Et ne nous soumets pas à la crosoftisation
Et délivre-nous de Windows
Ainsi soit Linux 🙏

Au nom de Linux, de l'Opensource et de la liberté.

#Linux, il y a moins bien, mais c'est plus !


🇬🇧 
May Linux 🐧 be with you! 
Come to me and you will be free and pray Linux together my children 😜 

Our Torvals which is on the net 
May your name be displayed 
That Linux comes 
Whether your nucleus is compiled with or without options 
Give us our code today 
Forgive us to our bugs, as we also forgive freeware, exhausted 
And don't submit to crosoftisation 
And deliver us from Windows 
So be Linux 🙏 

In the name of Linux, OpenSource and freedom.

#Linux, there is worse, but it's more!

#Linux #OpenSource #Torvals #Privacy #RegainPrivacy #NoGAFAM #NoSpy
ALT text

🇫🇷 QUE LINUX 🐧 SOIT AVEC VOUS ! Venez à moi et vous serez libre et prions Linux ensemble mes enfants 😜 Notre Torvalds qui est sur le net Que ton nom soit affiché Que Linux vienne Que ton noyau soit compilé avec ou sans options Donne-nous aujourd’hui notre code de ce jour Pardonne-nous nos bugs, comme nous pardonnons aussi aux Freeware trops buggés Et ne nous soumets pas à la crosoftisation Et délivre-nous de Windows Ainsi soit Linux 🙏 Au nom de Linux, de l'Opensource et de la liberté. #Linux, il y a moins bien, mais c'est plus ! 🇬🇧 May Linux 🐧 be with you! Come to me and you will be free and pray Linux together my children 😜 Our Torvals which is on the net May your name be displayed That Linux comes Whether your nucleus is compiled with or without options Give us our code today Forgive us to our bugs, as we also forgive freeware, exhausted And don't submit to crosoftisation And deliver us from Windows So be Linux 🙏 In the name of Linux, OpenSource and freedom. #Linux, there is worse, but it's more! #Linux #OpenSource #Torvals #Privacy #RegainPrivacy #NoGAFAM #NoSpy

@emilis@social.linux.pizza

Re- (I moved servers and need to pin it here).

I am a father of two kids from , 🇱🇹 , 🇪🇺 EU. In my forties. .

Working as a web developer, mostly with and React these days. Have been running on my computers since ~2004. My IDE is :vim: + shell.

In my free time I play with . Recovering from GAS.

Very interested in and other digital rights.

I support 🇺🇦 .

@PC_Fluesterer@social.tchncs.de · Reply to Willy_Wuff

@Willy_Wuff

Ist das satirisch gemeint, oder hast du es wirklich nicht verstanden?
Es geht primär nicht um die Narzisst/inn/en, die sich auf den kommerziellen antisozialen Plattformen freiwillig selbst entblößen.
Es geht darum, die großen Datensauger zu bekämpfen, die Jedmensch beim surfen HEIMLICH verfolgen wollen.

@ji7ro @Weltbewohner @thomasweibel

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Bund macht sich abhängig von und Co.

"Die Zukunft der öffentlichen Verwaltung ist die Cloud, wenn es nach dem Bund geht. Weil ihnen die Ressourcen fehlen, greifen Behörden aber oft auf private Anbieter zurück und machen die öffentliche Verwaltung so abhängig von Amazon und Co....."

netzpolitik.org/2025/verwaltun

Tja. Soviel zur Unabhängigkeit von den .....

netzpolitik.org

Bund macht sich abhängig von Amazon und Co.

Die Zukunft der öffentlichen Verwaltung ist die Cloud, wenn es nach dem Bund geht. Weil ihnen die Ressourcen fehlen, greifen Behörden aber oft auf private Anbieter zurück und machen die öffentliche Verwaltung so abhängig von Amazon und Co.

@jon Because from their standpoint it makes perfect sense: Gather all data they can get away with about their users and sell it for nice profits ON TOP OF the license fees they are already paying, which their investors love.

And in one fell swoop finally creating the access all the acronym services have been having wet dreams about for years.

And oh so many people just sleepwalk into it...

@pixelfed@mastodon.uno

Come Instagram, ma open source, e rispettoso della privacy: ecco Pixelfed!
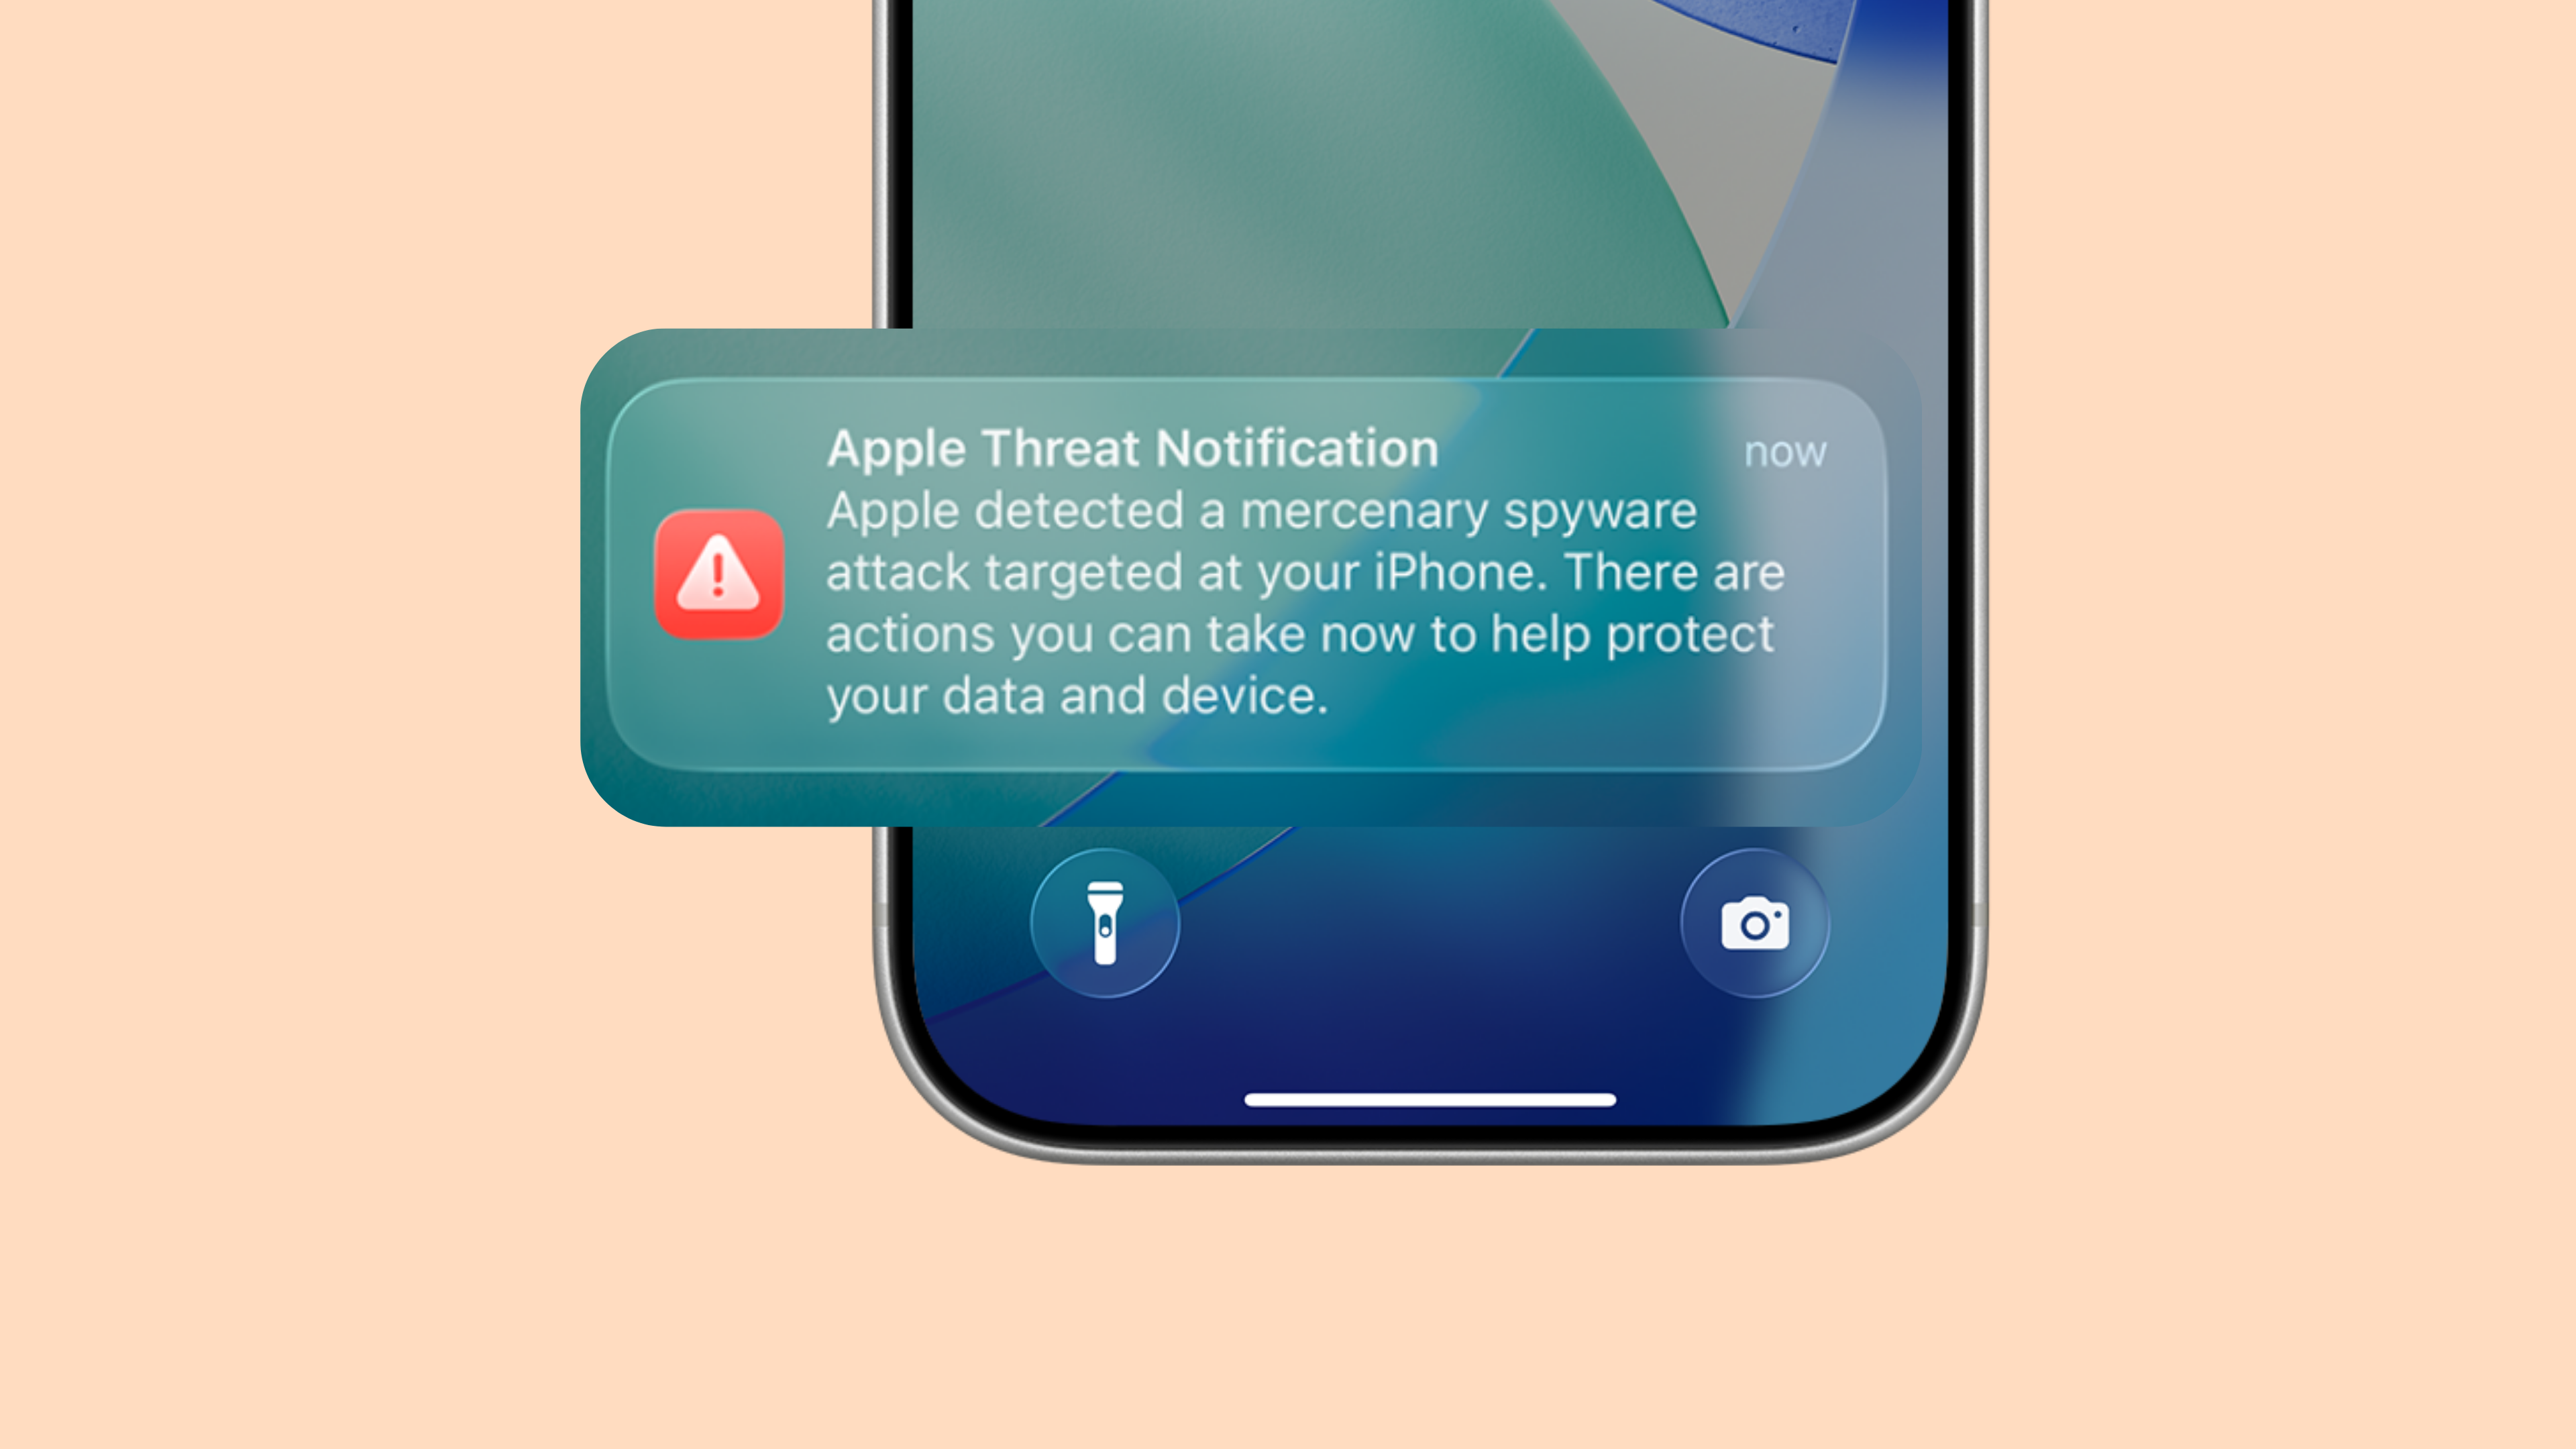
C'è un mondo al di fuori dei social più famosi come Instagram, Facebook o TikTok, ed è , rispettoso della e degli utenti, e :

▶️ smartworld.it/app/cos-e-come-u

Se cerchi una piattaforma spensierata che ti consenta di condividere semplicemente immagini come faceva una volta Instagram, scopri cos'è e come usare Pixelfed.uno

:diggita: @fediverso

pixelfed.uno

Pixelfed Uno Italia - Foto nel fediverso

Pixelfed Uno è la principale piattaforma italiana per la condivisione di immagini della rete pixelfed, e il secondo server donsigliato al mondo dagli sviluppatori, è la migliore alternativa etica a instagram per condividere e commentare le foto online.

@jon@vivaldi.net
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

«Es bedeutet was, wenn die von Anfang an dabei ist»

in der Schweiz

In Altendorf im Kanton Schwyz entsteht der Europa-Standort des Unternehmens Palantir [ ]. Das der Firma: Daten zusammenführen und verknüpfen. Hernani Marques, Sprecher des Chaos Computer Club Schweiz, sagt, was er davon hält.

srf.ch/news/wirtschaft/palanti

"Das eine ist, dass die Kundenliste von Palantir praktisch schon aus und im westlichen Raum besteht. Das liest sich wie das Who-is-Who des ganzen militärisch-industriellen Komplexes. Das andere ist, dass es schon etwas bedeutet, wenn die CIA von Anfang an dabei ist...."

srf.ch

Palantir in der Schweiz - «Es bedeutet was, wenn die CIA von Anfang an dabei ist»

Die Software-Firma Palantir zieht in die Schweiz. Das weckt bei Hackern Argwohn, sagt der Chaos Computer Club.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@pietro395@mastodon.uno
@Anne_Delong@musician.social

@ellie

Web hosting companies collect some data even when a visitor to a website doesn't log in. Mine tells me, for each person, an IP address , which pages were viewed and when, how much bandwidth was used, what browser was used, and the referring URL, If I had another web site that did have logins (I don't), I could compare IP addresses identify people who visited both sites.

@DurableAce@vivaldi.net

Hello people. It’s time for a new after migrating to social.vivaldi.net

Anything on a is my thing, especially . I race cyclo-cross with @BristolCX and ride with . I live in the UK and take every opportunity to experience or life.

I toot about cycling mostly. Sometimes and .

I’m looking forward to being part of social.vivaldi.net

Thumbnail not available
ALT text

A close-up of a bicycle bell attached to a handlebar. In the centre of the bell is a line drawing of a bicycle on a yellow background. Around the edge it says 'Cyclists stay awesome'.

issues. I have no home - if I did, I would evaluate my political theory through loyalty to the programme. That's what I used to do.

Instead of that, I pick bellwether issues to judge my political relationship to other people and orgs. There are many to choose from, here are some of mine:

* . My current main bellwether.
* +. Used to be my gold standard issue, and is still very high up there.
* . Subsumes many other more specific items such as , , , so break it down if you like.
* .
* .

This is a mechanism to simplify things for myself. Point being, I can develop an internal detection system for figuring out how likely I will be allies with or enemies of another person or org, I just look for clues related to the bellwether. Easy.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Merz packt Forderung aus, die nicht im Parteiprogramm steht. Der Weg der "freiwilligen" ePA unter der CDU/CSU (und wahrscheinlich auch von deren Koalitionspartnern).

„Überraschend bringt er einen Vorschlag ins Spiel, der nicht einmal im Wahlprogramm steht: Wer seine Gesundheitsdaten vollständig auf der Krankenkassenkarte speichert, solle zehn Prozent weniger Beiträge zahlen als diejenigen mit Datenschutzbedenken….“

t-online.de/nachrichten/deutsc

t-online.de

Umstrittener Auftritt in Dresden: Am Ende versucht sich Merz in Schadensbegrenzung

In Dresden verteidigt Friedrich Merz sein Vorgehen. Der Kanzlerkandidat hält an seiner Vision fest: Den Kurs der CDU so weit zu korrigieren, bis die AfD nicht mehr gebraucht werde.

@jcnotwit@mastodon.social

Hi, I'm Jeff! I'm a nerd living in New Hampshire with anxiety and depression. (The anxiety is why this introduction is more than a year late.)

My interests are all over the place, but I mostly talk about , , and these days. Also and , when I'm channeling my inner grandmother.

Occasional random thoughts are free or your money back.

@Give_A_Damn@newsie.social
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Elektronische Heilberufsausweise
Hackerangriff auf D-Trust zwei Tage vor EPA-start

„ Die Gematik und das Bundesgesundheitsministerium (BMG) bestätigten den Angriff. Nach aktuellen Kenntnissen habe es keine negativen Auswirkungen auf die Sicherheit der Telematikinfrastruktur gegeben, so die Gematik auf PZ-Anfrage.

Das sieht die Interessengemeinschaft Medizin (IG Med) anders. Sie fordert einen sofortigen Stopp des EPA-Rollouts in den Testregionen, bis alle Sicherheitslücken geschlossen sind. Die Vorfälle seien »alarmierend«, denn die Kombination eines kompromittierten Heilberufsausweises mit einem gebrauchten Konnektor stelle »ein massives Einfallstor in die Telematik-Infrastruktur dar«, schreibt die IG Med. Eine »Sicherheitslücke dieser Tragweite« würde demnach bei einem bundesweiten Rollout den potenziellen Zugriff auf die Gesundheitsdaten von rund 70 Millionen Versicherten ermöglichen….“

pharmazeutische-zeitung.de/hac

pharmazeutische-zeitung.de

Elektronische Heilberufsausweise: Hackerangriff auf D-Trust zwei Tage vor EPA-Start

Kurz vor dem Start der Testphase für die elektronische Patientenakte (EPA) haben Hacker vorige Woche den Dienstleister, der elektronische Heilberufsau...

@urbanprivacy@mastodon.social

Hej, wir sind Nicole und Daniel, die Macher hinter dem Modelabel URBAN PRIVACY. Seit 2017 sind wir mit Leidenschaft dabei, Dein digitales Ich mit Design zu schützen, die Du auch wirklich tragen möchtest.

Wir würden uns freuen, hier viele Gleichgesinnte im Bereich Datenschutz und digitale Freiheit zu finden und uns mit Euch zu vernetzen.


@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Passend zur Einführung der in

Datenleck in - Patient*innen bloßgestellt

Mutmaßliche Hacker erpressen offenbar einen Praxiskonzern, bei dem 130.000 Patienten registriert sind, mit gestohlenen digitalen Patientendaten…..

taz.de/Datenleck-in-Daenemark/

taz.de

Datenleck in Dänemark: Patienten bloßgestellt

Mutmaßliche Hacker erpressen offenbar einen Praxiskonzern, bei dem 130.000 Patienten registriert sind, mit gestohlenen digitalen Patientendaten.

@HailSatan@metalhead.club · Reply to Autonomie und Solidarität

@autonomysolidarity

@autonomysolidarity
Auf meinem Laptop sind quasi keine persönlichen Daten. Das Teil brauche ich nur um CD's zu Rippen. Mein Smartphone ist so konfiguriert dass es sich nach 15 fehlgeschlagenen Entsperrversuchen selbst löscht. Komme ich in eine Situation mit Bullen tippe ich inzwischen als regelrechten Automatismus 14 Mal mit dem falschen Finger auf den Sensor. Sollte ich aufgefordert werden das Telefon zu übergeben berührt dabei der falsche Finger den Sensor und die 1312 haben ein Gerät in der Hand das auf Werkseinstellungen ist.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Trotz der vom CCC aufgedeckten Sicherheitsmängel soll die ePA für Alle in am 15. Januar schon an den Start gehen. Die ePA ist nicht nur aus datenschutztechnischen Gründen höchst fragwürdig sondern bietet Staat und Konzernen auch Möglichkeiten, um intime Gesundheitsdaten der Menschen auszuschlachten und damit Profite zu machen.

Wenn Konzerne und "die Forschung" kostenlosen und massenhaften Zugriff auf unsere Gesundheitsdaten erhaltem, kann leider nicht erwartet werden, dass mit den Ergebnissen einfach Medikamente oder Therapien entwickelt werden, die den bedürftigen Menschen höchstens zu den Herstellungskosten zur Verfügung gestellt werden.

Stattdessen ist im Kapitalismus zu erwarten, dass mit den vom Staat für die "Forschung" kostenlos zugänglich gemachten aber im Grunde sehr wertvollen Gesundheitsdaten der Menschen, Produkte entwickelt werden, die mit hohen Profiten von Konzernen verkauft werden.

Dass es bei der nicht um sondern um geht, würde auch erklären, weshalb der überwachungskapitalistische Bertelsmann-Konzern und einige seiner ärgsten Lobbyist*innen (darunter ein bekannter Gesundheitsminister und eine ehemalige Ethikratsvorsitzende) so sehr dahinter stehen.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@untrusem@merveilles.town

Finally joined merveilles. So, here I go again, again

I am Moksh / untrusem, A kid with questions, from .
I am firm believer in and and also practice , My other shenanigans include , , , , *nix and learning about . But I delve into so much things to write all of them down.

I also likes esoteric things. I try to program but a novice in that.

I will use my time here to steal knowledge from you amazing people, so watch out :)

@mariob@liberdon.com

odysee.com/@NaomiBrockwell:4/n

Surveillance is a weapon that is too often used to silence opposition, suppress individuality, and enforce conformity. Privacy is what allows us to think, act, and connect without fear. Without privacy, we lose the ability to dissent, to innovate, and to live freely.

odysee.com

“I Have Nothing to Hide” – The Dangerous Myth About Privacy

“I have nothing to hide”.

@adambyte@dragonscave.space

(Mostly reposting from my old account.)

Hackable cars are as much a public safety concern as an infectious disease pandemic is. Just as refusing a vaccine or public masking risks infecting the people around you, so too does driving a hackable car risk crashing into the people around you.

It should be illegal to sell a new car with a built-in internet-connected computer that isn't hardware-isolated from everything except the dashboard screen and speakers. And yet, as far as I know, this describes literally all new cars for the past several years.

infosec.exchange

Adam Beer (old account) (@adambyte@infosec.exchange)

@evacide@hachyderm.io Hackable cars are as much a #PublicSafety concern as an infectious disease #pandemic is. Just as refusing a #vaccine or public masking risks infecting the people around you, so too does driving a hackable car risk crashing into the people around you. It should be **illegal** to sell a new car with a built-in internet-connected computer that isn't hardware-isolated from everything except the dashboard screen and speakers.

@adambyte@dragonscave.space

(Partially reposting from my old account.)

DRM is malware; more specifically, it's ransomware. It's software, running on your computer, whose sole purpose is to artificially restrict your ability to use that computer until you pay money to remove this restriction.

Similarly, client-side anti-cheat for multiplayer PC games is malware; specifically, spyware (at least). Its purpose is to surveil your entire computer, and punish you if you run certain combinations of software at the same time. All anti-cheat measures should be server-side.

infosec.exchange

Adam Beer (old account) (@adambyte@infosec.exchange)

@shacker@zirk.us @pluralistic@mamot.fr A thought I've had recently and haven't seen anyone else express: #DRM is #malware, specifically #ransomware. It's software running on your computer whose sole purpose is to artificially restrict your ability to use that computer until you pay money to unlock it.

@adambyte@dragonscave.space
@tim@union.place

In the spirit of a recent post on making the a more welcoming place, renewing a post I had on my old profile but apparently not here: ask me anything! I can't guarantee I'll have all the answers or be fast to reply but lll try to at least say something. Some things I can talk vaguely usefully about include:

and probably a billion more.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Elektronische Patientenakte:
Widerspruch im Keim erstickt

„ Die „elektronische Patientenakte für alle“ (ePA) wird gut angenommen, könnte man meinen. Laut der größten deutschen Krankenversicherungen hat bislang nur ein Prozent der Versicherten ihrer Einrichtung widersprochen. Die Verhältnisse scheinen sich damit umzukehren: Bislang nutzt gerade einmal gut ein Prozent der Versicherten in Deutschland die elektronische Patientenakte.

Der geringe Widerspruch hat offensichtlich seine Gründe. Der Verbraucherzentrale Bundesverband e.V. (vzbv) hat die Anschreiben mehrerer gesetzlicher Krankenkassen an ihre Versicherten analysiert….“

netzpolitik.org/2024/elektroni

netzpolitik.org

Widerspruch im Keim erstickt

Im Februar 2025 kommt die elektronische Patientenakte für alle, die ihr nicht widersprechen. Die Krankenkassen sind verpflichtet, ihre Versicherten darüber neutral zu informieren. Dieser Pflicht kommen sie in vielen Fällen nicht nach, wie der Verbraucherzentrale Bundesverband herausfand.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

zu Gesundheitsdaten: Google, Meta, und OpenAI melden Interesse an

Da fragt man sich in der Tat ob das ein schlechter Witz sein soll. Braucht es noch weitere Gründe um der elektronischen Patientenakte zu widersprechen?

„Lauterbach sieht in der Patientenakte einen Datenschatz für KI-Innovationen. Tech-Giganten zeigen Interesse, um die Gesundheitsversorgung zu verbessern.“

heise.de/news/Lauterbach-zu-Ge

heise.de

Lauterbach zu Gesundheitsdaten: Google, Meta, und OpenAI melden Interesse an

Lauterbach sieht in der Patientenakte einen Datenschatz für KI-Innovationen. Tech-Giganten zeigen Interesse, um die Gesundheitsversorgung zu verbessern.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@nen@mementomori.social · Reply to nen

Current privacy options

Public: Find new friends, but also allow your violent ex to find and stalk you.

Quiet public: Allow the violent ex to still find and stalk you, but reduce your chances of finding new friends. BTW, the ex doesn't even need an account.

Followers: Absolutely DESTROY your chances of finding new friends. Also make some current followers more likely to miss your post, because others can't boost it.

Specific people: For direct messages only.

@nen@mementomori.social

Privacy here shouldn't come with such a painful social cost. You shouldn't have to either choose social isolation, or be forced to accept that your posts will be ingested by shady web scrapers or risk helping a known dangerous stalker identify your physical location.

You should be able to create posts that can be interacted just like the completely public ones, but which are only visible to your followers and maybe their followers, or other group of your choice.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

How to defend yourself during a police interrogation

„An interrogation is not a harmonious exchange between two individuals. It’s a conflict.
And in this conflict, our ignorance is their strength. Ignorance of the meaning of police work, ignorance of the manipulative techniques used, ignorance of the legal framework and, last but not least, ignorance of our means of defence.
In response to this observation, this book is intended as a tool for self-defense against police interrogation practices of interrogation…“

Evasions-Project Releases English Translation of the

PDF:
projet-evasions.org/wp-content

Thanks to @unsalted
unsalted.noblogs.org/post/2024

German and french Version 👆

Thumbnail not available
ALT text

Cover of the book "How to defend yourself during a police interrogation". A figure seated at a table, head in their hands, has two police officers pointing at them, interrogating them. The officers cast shadows on the wall behind them, two large ghosts evoking the "good cop, bad cop" trope.

@xforever1313@tech.lgbt

Your online matters, especially now that America got back together with its abusive ex.

Here's a website that gives tips on how to protect your online privacy. May be useful if Trump does go full dictator.

privacyguides.org/en/basics/wh

privacyguides.org

Why Privacy Matters - Privacy Guides

In the modern age of digital data exploitation, your privacy has never been more critical, and yet many believe it is already a lost cause. It is not.

@be_far@treehouse.systems

Hi all! I studied computer science with a focus on RTOS and FP/PL, but I graduated law school earlier this year. I practice at a boutique firm that primarily handles IP cases. I foilboard and I play way too many rhythm games in and out of the arcade.

I contribute to open source projects where I can, and I write up my experience in my digital garden which I’ve been maintaining for 2 years now. It’s also a good place to find usage tips for projects/tools that you might want to use.

My passion for tech also includes privacy, and I’m an advocate for minimizing your digital footprint. GenAI is a scam and its purveyors are causing real harm while they sell it as hard as they can.

Follow me for:

@publicvoit@graz.social

I hope it is no surprise when I tell you that you don't have and (and ) if you do not have the right as well as the and/or to act accordingly.

Therefore, most people are excluded here because of at least one reason.

In that sense, has arrived long time ago.

karl-voit.at/tags/privacy/
karl-voit.at/tags/security/
karl-voit.at/tags/pim/
karl-voit.at/cloud-data-condit

karl-voit.at

It's OK to Give Away Your Personal Data to Cloud Companies

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Nochmal der Hinweis auf den Widerspruchsgenerator zur elektronischen Patientenakte

Da viele Menschen nicht wissen, wie der Widerspruch funktioniert und auch nicht umfassend über die Konsequenzen der überwachungskapitalistischen Ausbeutung von Gesundheitsdaten informiert werden, scheinen viele Menschen keinen Widerspruch gegen die ePA einzulegen, obwohl sie ihr sonst auch nicht zustimmen würden.
Für die herrschende Politik könnten damit opt-out-Modelle, die gezielt mit Hürden zu Wissen und Handlungsmöglichkeiten arbeiten, um so attraktiver werden, während sie den fehlenden Widerspruch als "großen Zuspruch" etc. umzudeuten versuchen.

widerspruch-epa.de

widerspruch-epa.de

widerspruch-epa.de

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

WhatsApp? Nein, danke.

‚Egal, ob wir über die (real existierende) totale der Geheimdienste sprechen oder über Digitale Souveräntität und Digitale Mündigkeit oder auf dem Elternabend von Schule oder Kindergarten: Eine Diskussion lässt einerseits Augen rollen oder Achsel zucken und andererseits Bäuche krampfen oder auch Fäuste ballen. So trivial die Frage einer praktischen und allgemein leicht nutzbaren und möglichst weit verbreiteten Lösung für „Instant Messages“ (Kurznachrichten) in Menschengruppen scheint, so sehr treffen hier globale Machtstrukturen, Datenschutz, individuelle Überforderung, Unwillen, Kapitulation und Gleichgültigkeit aufeinander.

Muss ich jetzt wieder Querulant sein und alle damit nerven, dass ich kein WhatsApp nutzen will?

Muss der jetzt wieder nerven, mit seiner Verweigerungshaltung? Wegen des einen Querulanten müssen alle anderen jetzt noch eine von diesen nervigen (weil ungewohnten) Open-Source-Apps nutzen?

Einfach ja, ja und ja! Warum – anders als bei Querulanten – die „Klagen oder Beschwerden“ nicht unberechtigt sind: hier ein Plädoyer für die Unbeirrbarkeit....‘

netzpolitik.org/2024/digitale-

netzpolitik.org

WhatsApp? Nein, danke.

Wen juckt es denn, ob ich WhatsApp nutze oder nicht? Können wir jetzt weitermachen? Nein. Das Private ist politisch.

@governorkeagan@infosec.exchange

It's coming up on one-year since I joined Mastodon and I just switched to a new instance. So, there's no better time for an toot.

I started my journey during the height of the pandemic, when had a special for their email service. Over the past 4ish years I have been trying to learn as much I can, and have been slowly switching/advocating for privacy friendly alternatives. In October of last year (2023), I made the switch to and haven't looked back.

More recently, I have taken an interest in .

I am also a big fan of and try to contribute as often as possible. All of my mapping content is posted on my other account to help keep things separate -- @governorkeagan@en.osm.town

Currently, I work two jobs. My primary role is with a company that provides trainers to help other companies solve their problems, and I specifically work on training .[1] I’m also working as a freelance , with the goal of making that my full-time gig. All my video-related toots are posted on my other profile, @gringomedia.

[1] There are a lot of issues with the company that I’ve posted about on my previous profile (@governorkeagan@mastodon.social), and I’ll be sharing more about them here at some point.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Guter Artikel im @untergrundblaettle darüber, was die ("elektronische Patientenakte") und nur die Möglichkeit eines Opt-Outs eigentlich bedeuten in Hinblick auf Überwachung und Kontrolle.
Zumindest bleibt noch die Möglichkeit eines Widerspruchs.

Die ePA reiht sich ein in den zunehmenden Digitalisierungszwang
EPA – mit dem Opt-Out-Verfahren zum gläsernen Patienten?

„Ab dem 15. Januar 2025 bekommen alle Kassenpatienten automatisch eine elektronische Patientenakte (ePA). Hintergrund ist, dass sich bisher nur ca. 1 Prozent der Versicherten für die ePA entschieden haben…..“

xn--untergrund-blttle-2qb.ch/p

xn--untergrund-blttle-2qb.ch

EPA – mit dem Opt-Out-Verfahren zum gläsernen Patienten?

Ab dem 15. Januar 2025 bekommen alle Kassenpatienten automatisch eine elektronische Patientenakte (ePA). Hintergrund ist, dass sich bisher nur ca. 1 Prozent der Versicherten für die ePA entschieden haben.

@kagihq@mastodon.social

Hello, Fediverse! We're Kagi, and we're on a mission to create a friendlier, more human-centric internet that has the users' best interest in mind.

Our core product is a search engine that is ad-free, tracking-free, and fully supported by our users. We've worked hard to deliver a high-quality, fast, and reliable search experience without compromising user privacy: kagi.com/

Excited to engage with the community here.

Thumbnail not available
ALT text

Screenshot of Kagi homepage with the text "we're on Mastodon!" in the search field

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@marielgm@mastodon.mit.edu

Thanks to everyone reading me recently (or at all)!
I'm a former tech worker from Mexico, current sociotechnical scholar at MIT ( or Science, Technology, and Society -- or Science and Technology Studies!). I study media and IT, especially as they contribute to public interest and social change.

My current work: What does it entail to challenge in a place where is not to be expected? Some of my ethnographic fieldwork notes from MX blog.castac.org/2024/08/challe

blog.castac.org

Challenging Normalized Surveillance: “Birds on the Wire” Surveillance in Mexico | Platypus

@fyr@indieweb.social

An 👋

As my bio indicates I'm a bit of a nerd with a passion for the simpler things. Expect technology (infrastructure) posts, security musings and occasional discoveries and PoCs ( and are passions of mine) interspersed with some life stuff, whether it's finance, garden or home renovation oriented. Maybe some writing, too.

Recently learned about the / mindset and am embracing the to bring back some fun to this series of tubes.

@rgbd@ursal.zone

A edição de junho da Revista ComCiência (Unicamp | SBPC) trouxe o dossiê "Privacidade Digital", o qual tive a honra de estruturar. Contou com reportagens e entrevistas sobre direito à privacidade e ao esquecimento, impactos psicológicos da exposição digital, riscos da Internet das Coisas e um artigo excelente do @manualdousuario sobre uma internet mais saudável por meio do Fediverso.

Confiram 🙂
comciencia.br/privacidade-pra-

Thumbnail not available
ALT text

Um laptop aberto e na tela há um olho gigante que simboliza como as tecnologias digitais atuais tem invadido nossa privacidade.

@ovan@social.lol

😤 “Opt out” should be banned everywhere.

For AI, for advertising, for tracking, I don’t care what “legitimate interest” you pretend to have.

You have no right to monitor me 24/7, steal and sell my personal data and creations, whatsoever.

It’s my life, let me choose what to share.

@madargon@is-a.cat

Created this after reading conversation in comments below some tech article somewhere. Someone mentioned "surfing the sewer" and I really liked that phrase.

Thumbnail not available
ALT text

Drawing of a cartoon style man, wearing silver protective suit with UBlock Origin logo on it, surfing in sewer with green toxic water. There are cookies and fanged monsters looking like Chrome logos floating around him. On the background wall there are red crosses, like for closing websites or errors. There are also industrial cameras, one yellow eye and graffiti with TikTok logo. On the railing on path's edge there is photo camera attached, looking similar to old Instagram logo, and rotting blue bird. There is big text "Google" near water, with both "o" replaced with ends of pipes and small texts around: crossed out "AI", "Buy this, only $2!" and below "scammer!" and "it's con". Above the picture there is description "Surfing The Internet Sewer".

@avoidthehack@infosec.exchange · Reply to Avoid the Hack! :donor:

Much related advice includes creating a threat model prior/alongside taking steps to improve your privacy. This is solid advice because threat modeling allows you to focus on achieving your goals while keeping in scope your personal resources...

However, I argue there _are_ actionable steps you can take that don't require a threat model to be in place first:

1. Use a privacy-oriented browser

2. Use an encrypted email provider

3. Use private search engines

Privacy is a journey.

PS: Feel free to threat model after taking these steps. Or before. Just know that you don't have to in this case.

Be sure to take basic measures first (refer to OP of the thread).

avoidthehack.com/getting-start

@avoidthehack@infosec.exchange

Lots of new followers (hi!) recently. Some of you are in the or communities, the community, both, or neither. I post privacy and related things for individuals and small/micro organizations.

Some are looking for a place to “get started” with improving their privacy and/or security online. In any case, privacy and security start with some basics that I strongly believe everyone should do:

1. Develop good password management practices, which includes NOT reusing .

2. Keep your device and firmware updated.

3. Use multifactored authentication / two-factored authentication

Security is a process. It is also the foundation to online privacy; what good is it to use an encrypted email service if you are reusing weak passwords from your other online accounts?

avoidthehack.com/getting-start

@mucomum@piaille.fr · Reply to Lubedyle

@Lubedyle je l'ai pas refaite depuis longtemps, alors voilà une belle occasion pour une nouvelle :

dans la 30aine, mon coéquipier des batailles du quotidien est un coup d'un soir qui dure depuis 15ans. Nous avons eu 4 bébés ensemble, mais seuls deux illuminent notre maison car nous sommes porteurs de , et le parcours de quand on porte des maladies n'est pas linéaire....

Nous vivons à , je pratique le et nous sommes de la team en famille.

Je suis très portée , globalement beaucoup de , et .

Ligne éditoriale: , , .

@r_alb@mastodon.social

Some of the issues us privacy people complain about may appear rather insignificant to you. I get that.
But please let me invite you to a different perspective: As we are currently setting a lot of precedents regarding data privacy rights, how we are handling the small issues today will have an effect on how we will deal with big problems tomorrow. That is why you should care about violations of your privacy, even if they don‘t seem like much today. Because tomorrow, they might.
—

@jessica@beige.party
@ellie@ellieayla.net

Do you own a website and wish to make sure your visitors' identities are protected?

“Don't sign in" is zero-source, takes no minutes to integrate, works with static sites, and shows that you care about your visitors' .

The only protected data is data that's never collected.

@fosserytech@social.linux.pizza

A short introduction:

I'm an introvert, antisocial tech guy 😅
I like to use FOSS software wherever possible. My family considers me a tech nerd, I consider myself a tech noob.

Hobbies: web dev (FosseryWeb), running, kayaking, listening to music (mainly electro), watching tech, gameplay and Backrooms videos.

Age: twenties

Languages: 🇭🇺 (native) / 🇬🇧 (took language exam but I feel like I still suck at it sometimes lol)
LINUX JOURNEY
I'm a seasoned distrohopper, started on Linux Mint, went to Kubuntu, Ubuntu, Manjaro, Garuda, Zorin OS, Fedora, LMDE and finally Debian. Also had/have Nobara and PeppermintOS as secondary systems.
As for DE, GNOME is my (almost) all-time favorite, tried out Xfce, KDE and Cinnamon, but always returned to GNOME because it's the most comfortable to me (might also try out COSMIC)
On mobile (PinePhone) I went from Manjaro Plasma to Arch Plasma/Phosh, and now I'm on posmarketOS Phosh

MY STANCE ON PRIVACY
I care about my privacy, although I don't have the highest threat model, like to keep balance between privacy and convenience (although convenience is a bit of a subjective thing, some might consider right clicking to copy username then password from KeePassXC inconvenient, I don't lol).

PROGRAMS I USE
Favorite programs:
- LibreWolf
- OBS Studio
- Krita
- KeePassXC
- FreeTube
- yt-dlp
- Fluent Reader
- Haruna
- Joplin
- Anki

Other programs I use:
- Brave (for websites that don't work in Firefox based browser - shame on those web devs - btw I provide support for all major browser engines on FosseryWeb)
- GNOME Boxes
- Pulsar
- Gajim
- Flatseal
- Warehouse
- Portmaster
- Solanum
- Switcheroo
- Ear Tag
- Warp (the FOSS, GTK-based file transfer app, not the proprietary terminal emulator of course)

On mobile:
- Amberol
- Exercise Timer
- CoreArchiver
- Angelfish
- Kumo

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Alle 3,5 Stunden durchsucht die Polizei ein (Sachsen-Anhalt)

"In Sachsen-Anhalt durchsucht die pro Jahr mehr als 2.500 . Das geht aus der Antwort der Landesregierung auf eine kleine Anfrage der Fraktion die Linke im Magdeburger Landtag hervor. Das Dokument gibt einen Einblick in die Auswertung von Smartphones – doch wichtige Fragen bleiben offen.

Das Smartphone enthält wichtige Daten über unser Leben. Hunderte -Chats, die Bildergalerie oder Dating-Apps. Dennis-Kenji Kipker, Professor für IT-Sicherheit an der Uni Bremen, bezeichnete das Smartphone gegenüber netzpolitik.org als „ausgelagertes, digitales Gedächtnis“. Der Grundrechtseingriff ist also enorm.
(...)
Für die tabellarische Auflistung der einzelnen Regionen und der Zahl der beschlagnahmten Smartphones im Jahresvergleich netzpolitik.org/2024/sachsen-a "

tumulte.org/2024/02/articles/a

tumulte.org

Alle 3,5 stunden durchsucht die polizei ein smartphone ( sachsen anhalt) | tumulte

@annaelbe@norden.social

Die Logik des Digitalen
Es zählt, was sich zählen lässt!

Quantität ist das zentrale Qualitätskriterium unserer Zeit. In sozialen Netzwerken ist es die Anzahl der Freunde, Follower, Views, Likes und Shares, die Erfolg und Status bestimmt. Klicks entscheiden über Sichtbarkeit in der digitalen Welt.

deutschlandfunk.de/es-zaehlt-w

deutschlandfunk.de

Die Logik des Digitalen - Es zählt, was sich zählen lässt!

Quantität ist das zentrale Qualitätskriterium unserer Zeit. Klicks entscheiden über Sichtbarkeit in der digitalen Welt.

@ralb@privacyofficers.social

Asking enthusiasts and professionals privacy related questions is great and I‘d like to encourage you to do so whenever you are uncertain or want to know more!
When you do, please keep in mind to provide those who want to answer you with enough information. We are talking about legal matters after all, which are highly contextual. More information on the issue usually improves the quality of the answers you will get!
—

@ralb@privacyofficers.social

Some of the issues us privacy people complain about may appear rather insignificant to you. I get that.
But please let me invite you to a different perspective: As we are currently setting a lot of precedents regarding data privacy rights, how we are handling the small issues today will have an effect on how we will deal with big problems tomorrow.
That is why you should care about violations of your privacy, even if they don’t seem like much today. Because tomorrow, they might.
—

@mysk@mastodon.social · Reply to Mysk🇨🇦🇩🇪

9/9

Fortunately, starting Spring 2024, Apple will require developers to declare reasons for using the APIs that return unique device signals, such as the ones commonly used for fingerprinting.

Thanks a lot for reaching this far. If you find this content helpful, share it with your contacts, follow us, like us, and we look forward to sharing our next findings with you.

@mysk@mastodon.social

🚨🎬 Privacy Concerns about Apple Push Notifications
TL;DR: data-hungry apps use push notifications as a trigger to send app analytics and device information to their remote servers, even if the apps aren't running at all on your iPhone. Such apps include TikTok, Facebook, FB Messenger, Instagram, Threads, X, and many more.

Watch this video to see it in action:
youtu.be/4ZPTjGG9t7s

🧵 1/9

youtube.com

#Privacy: Facebook, TikTok, and Other Apps Use Push Notifications to Send Data about Your iPhone

This video sheds light on a growing practice among data-hungry apps where they use the background execution time allocated by iOS for the purpose of customiz...

@toothFAIRy@scholar.social · Reply to Esther Plomp
Academic paper tracking #365papers

363 / Problems of knowledge, problems of order: the field site
doi.org/10.3389/fsoc.2023.1149

364 / Open-Science Guidance for Research: An Empirically Validated Approach for De-Identifying Sensitive Narrative Data doi.org/10.1177/25152459231205

365 / versus open science doi.org/10.3758/s13428-019-012

And with that, it is a wrap and it is Christmas time! I actually made it :toot:

@marcel@waldvogel.family

I'm trying out the idea: Keeping one (actually one each for English and German) of Fediverse threads I authored.

I start with a top-ten list of articles (or threads for those articles), according to the page views.

Happy season!

🔟 «Right to be forgotten» void with ? (2023-03)
A description how hard it is to eliminate results from AI responses and what this means to our rights.

netfuture.ch/2023/03/right-to-

netfuture.ch

«Right to be Forgotten» void with AI?

In a recent discussion, it became apparent that «unlearning» is not something machine learning models can easily do. So what does this mean to laws like the EU «Right to be Forgotten»? The right to be forgotten (RTBF) is the right to have private information about a person be removed from In

@jnthnkl@mastodon.social

If you would like to contribute to the deGoogle movement 🚀 you can install Sapio on your device 📱 and evaluating the compatibility of your Android apps.

👉 Let's make developers aware of privacy issues together !

github.com/jonathanklee/sapio

github.com

GitHub - jonathanklee/Sapio: Android Open Source API compatibility

Android Open Source API compatibility. Contribute to jonathanklee/Sapio development by creating an account on GitHub.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität
@jnthnkl@mastodon.social
@spiezmaestro@social.spiezmaestro.ch

After primarily using my account @bergmeister for mountain as well as IT related posts, I decided to split the account, so I can "speak more freely" without cluttering the timelines of those who are only interested in one part of my posts.

This account will be used for the IT stuff, like homelab, self-hosting, open source software and privacy.

Will post in English and occasionally in Dutch and German.

@samvarma@fosstodon.org
@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

Der polizeiliche Zugriff auf DNA-Daten - Strategien der Gegenwehr

Was tun, wenn die eine Speichelprobe verlangt, um Deine zu analysieren?

Was, wenn Dein DNA-Profil schon in der DNA-Datenbank des BKA gespeichert ist?

Und was, wenn die Dich wegen eines Massengentests, einer so genannten DNA-Reihenuntersuchung, anschreiben?

Seit einer Strafrechtsreform von 2005 wurde der polizeiliche Zugriff auf die DNA-Daten enorm ausgeweitet – und der Rechtsschutz empfindlich ausgehöhlt.

Gleichzeitig gilt: Je diffuser die Rechtslage, desto mehr Spielräume gibt es, sich – auch mit rechtlichen Mitteln – zur Wehr zu setzen.

Und je mehr die biologische Vorratsdatenspeicherung zunimmt, desto mehr ist Widerstand angesagt.

August 2023 / Gen-ethisches Netzwerk e.V.

Kostenloser PDF Download:
shop.gen-ethisches-netzwerk.de
Webseite:
shop.gen-ethisches-netzwerk.de

Thumbnail not available
ALT text

Zine Cover Grüner Hintergrund Darauf steht in weiß in einem kleinen blauen kasten "der Polizeiliche Zugriff auf DNA-Daten" Darunter in blau in weißem kasten "Strategien der Gegenwehr" Darunter ein Bild der Polizei und ein bild eines genoms vor einer behörde, zu dem bild für ein blauer strich zu einem weißen kasten auf welchem "Gene und Genome" stehen darunter zu sehen weitere Genome ganz unten steht in blau. GeN: gemeinnützig, kritisch, interdisziplinär

@tynstar@nerdculture.de

Operating a that really respects is complicated: forbids storing personal data (incl. IP addresses) that's not strictly required. Consequently, the website of my @ChronoLink service never logs IP addresses. As all hosters I knew do that, I had to self host. But a separate server is wasteful/cumbersome, and sharing one with the service itself is risky. 😕

As of last Saturday, I have a solution: let statichost.eu/ host it. Thanks @puresick for suggesting them!

statichost.eu - 100% European static site hosting

Static hosting for frontend developers who care where their sites live. Git push, custom domain, done — on European infrastructure owned by Europeans, all the way down.

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

"The popular messaging app Telegram can leak your IP address if you simply add a hacker to your contacts and accept a phone call from them.
(...)
boasts 700 million users all over the world, and has always marketed itself as a “secure” and “private” messaging app, even though experts have repeatedly warned that Telegram is not as secure as end-to-end encrypted app , for example.
The fact that Telegram leaks your address to people in your contacts during a voice call has been known for years, but it’s likely that new, less technical users may not be aware."
techcrunch.com/2023/10/19/tele

Thumbnail not available
ALT text

Dark background. in the middle you can see a cell phone with the telegram app on the home screen. at the top the telegram symbol (blue circle with white sent sign) underneath it says " the worlds fastest messaging app. it's free and secure" at the very bottom of the cell phone screen blue start messaging button

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

What Is Doxxing & How to Protect Against It (2023 Guide)

"Your name, address, and phone number have been published online without your consent, and you’re now receiving harassing social media messages and intimidating phone calls. Known as doxxing, this situation is becoming more common among average internet users.

In this guide, we’ll provide an overview of what doxxing is, along with how you can protect yourself against it."

joindeleteme.com/blog/what-is-

joindeleteme.com

What Is Doxxing & How to Protect Against It - DeleteMe

Your name, address, and phone number have been published online without your consent, and you’re now receiving harassing social media messages and

@KhouryVis@vis.social

Hey Mastodon! 👋 Here is our post: We are the Data Visualization Lab at Khoury College of Computer Sciences at Northeastern University. You can find more about our work here: vis.khoury.northeastern.edu/

We'd love to be connected to more folks and labs in the realms of

Our lab has been applying visualization to domain areas like

Say hi!

vis.khoury.northeastern.edu

Khoury Vis Lab, Northeastern University

Front page Khoury Vis Lab, Northeastern University

@autonomysolidarity@todon.eu · Reply to Autonomie und Solidarität

NoTrace Project

No trace, no case. A collection of tools to help anarchists and other rebels understand the capabilities of their enemies, undermine surveillance efforts, and ultimately act without getting caught.

notrace.how/ via @notrace

Thumbnail not available
ALT text

Black background depicted head (balaclava) in white. Both hands raised in black as glasses in front of eyes.